To simplify access to and synchronization of Malpedia's automatically generated, code-based YARA rules, we have created the following repository on Github: https://t.co/dFFVaqnOcT
Fresh auto-generated YARA rules (courtesy of @fxb_b) are now live on Malpedia and GitHub. This round brings 42 new rules and updates 1618 existing ones.
I have just published a new data set revision of MalpediaFLOSSed, now aggregating 5.6m unique strings gathered from 2.100 malware families. https://t.co/13bElmmIjI
@AzakaSekai_ thanks for the notice - we need to have the cert issues by our org and can't do that before business hours tomorrow morning. 🙄 I've now removed HSTS though, so it should at least be accessible...
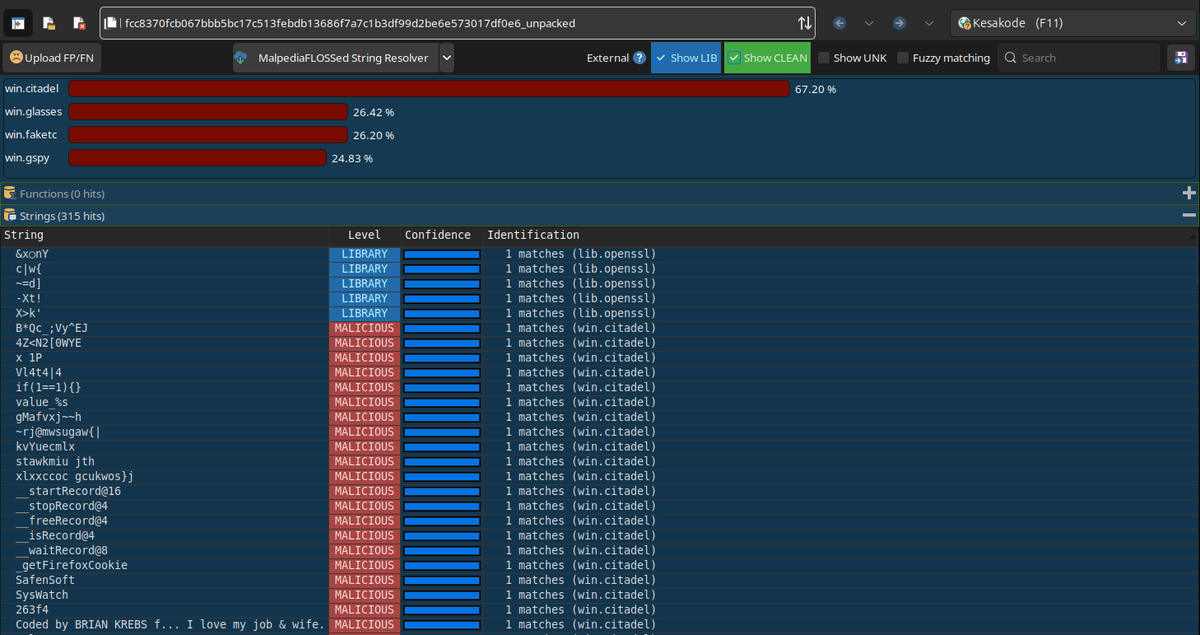
You can now check your strings in #malcat against an online library of #Malpedia FLOSSed strings. Just copy this plugin, courtesy of @push_pnx :
https://t.co/cwKzoGMatk
I wrote a blog post about MalpediaFLOSSed, a collection of ~4 million strings extracted from 1800+ malware families and upgrading its GUI plugin to work with IDA, Ghidra, and Binary Ninja at once!
Kudos to @hyun____22 for Hyara, which pioneered such cross-tool compatibility!
📣We updated "Malpedia FLOSSed".
TL;DR: More data, cleaner Rust/Go/Dotnet strings, various tags!
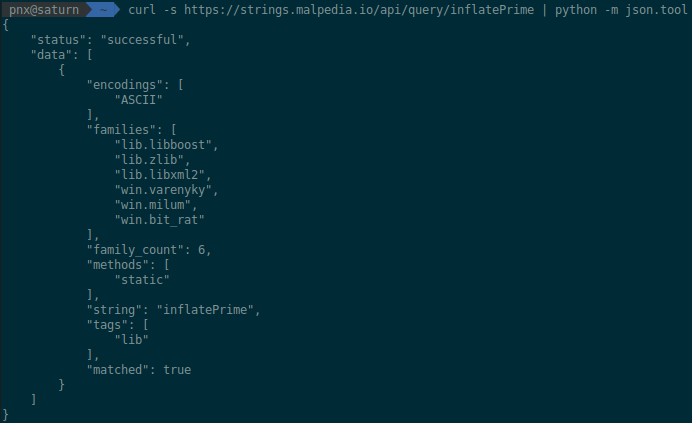
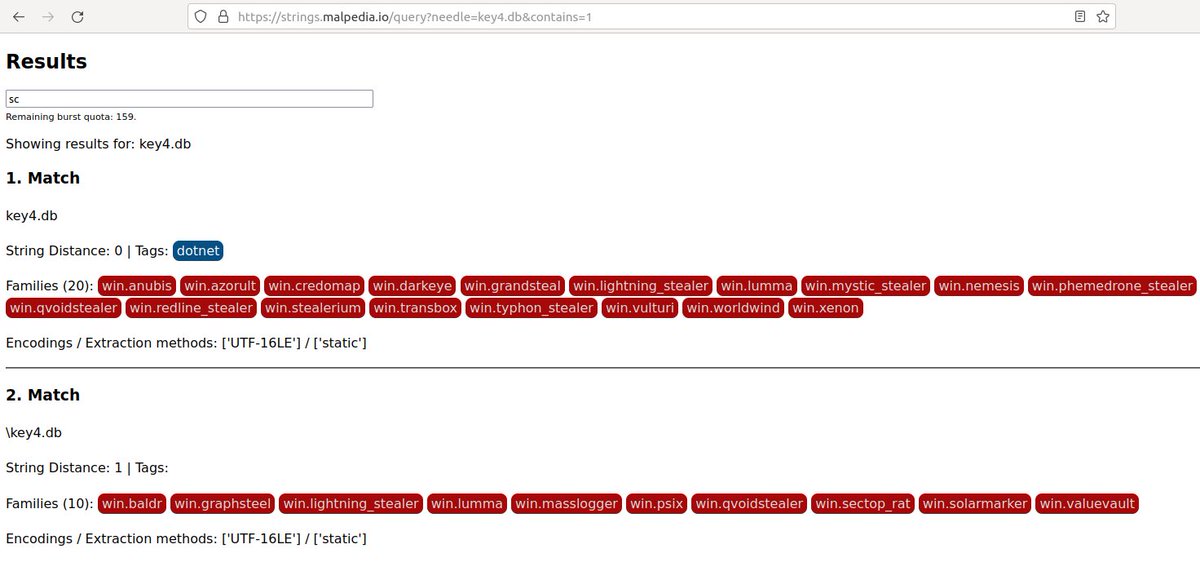
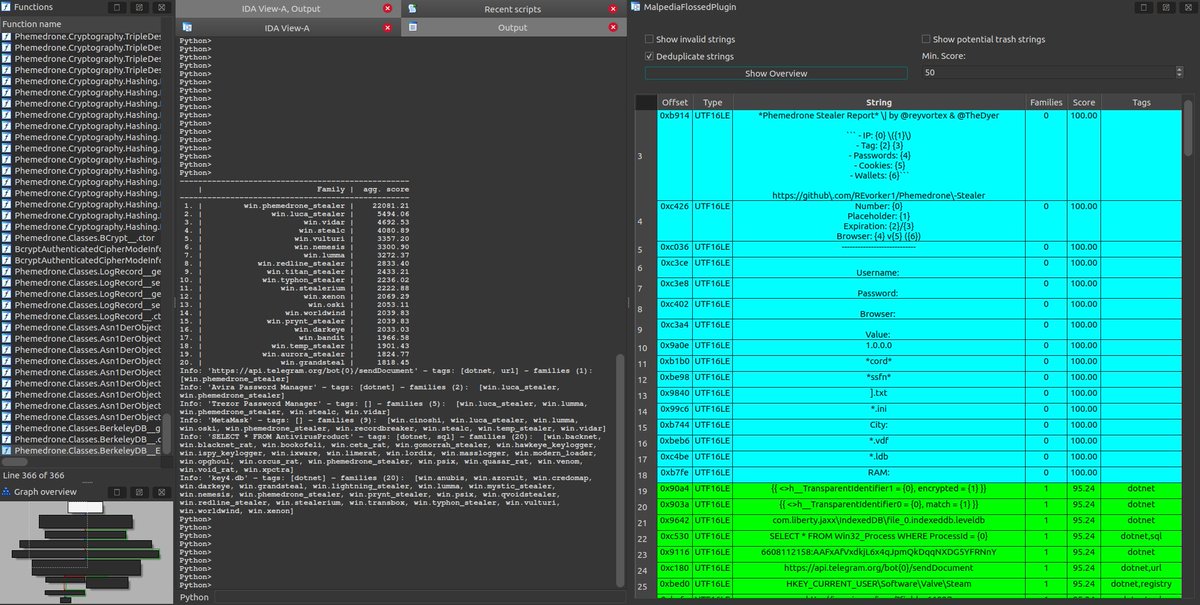
We also created a public web service to make this data more accessible: https://t.co/69y3BcGfht, as well as an IDA plugin as a demo use case.
Read more -> https://t.co/iFJO0O9hma
Based on this, I updated the @TrellixARC Ghidra script to locally use this JSON file. Additionally, I wrote a script to query the Malpedia web service via the exposed API, which one can also host locally. The Ghidra scripts can be found here: https://t.co/tWCfIq6Sar
📣We updated "Malpedia FLOSSed".
TL;DR: More data, cleaner Rust/Go/Dotnet strings, various tags!
We also created a public web service to make this data more accessible: https://t.co/69y3BcGfht, as well as an IDA plugin as a demo use case.
Read more -> https://t.co/iFJO0O9hma
I feel like this dump doesn't get enough credit.
So I filtered all malware debug ascii/utf16 strings from it and included it in a YAR rule file.
That's just one use-case for this awesome dump.
There are lots of other interesting malware indicators in it that could be used in a different way.
@malpedia@push_pnx #100DaysofYARA #malpedia
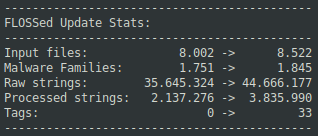
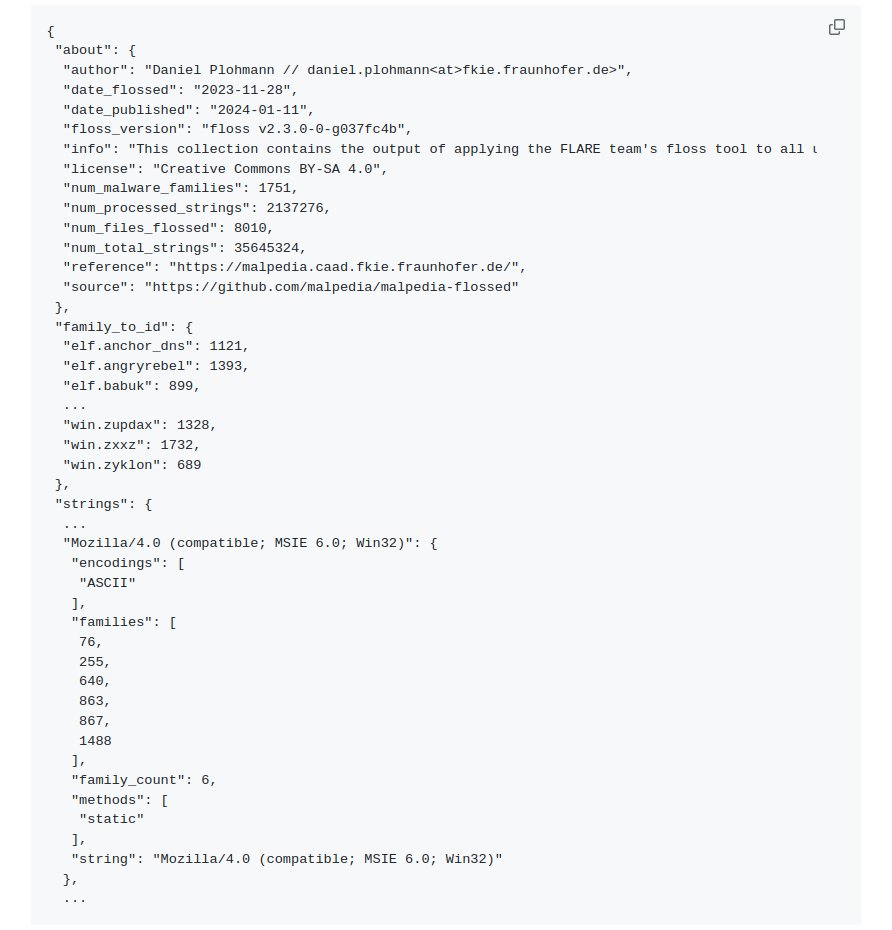
🛠️ We just published "Malpedia flossed": @Mandiant FLARE team's floss tool applied to all unpacked + dumped samples in @malpedia. Results: 35.645.324 raw strings, distilled to 2.137.276 unique strings from 1751 processed malware families - 400 MB JSON.
-> https://t.co/iFJO0O9PbI
Introducing YARA-Forge ⚡️
- Streamlined Public YARA Rule Collection
Excited to share my latest project with the community just in time for Christmas! After weeks of hard work, it's finally ready 🎄🎁
Blog Post
https://t.co/KStSe2Gqfo
Project Page
https://t.co/ruVg6bSSMO
We just deployed several updates to Malpedia.
1) There is now an RSS feed available.
2) @MsftSecIntel threat actor names have been integrated as aliases.
3) Family pages have links to @virustotal collections.
4) Library entries indicate if the article language is not English.