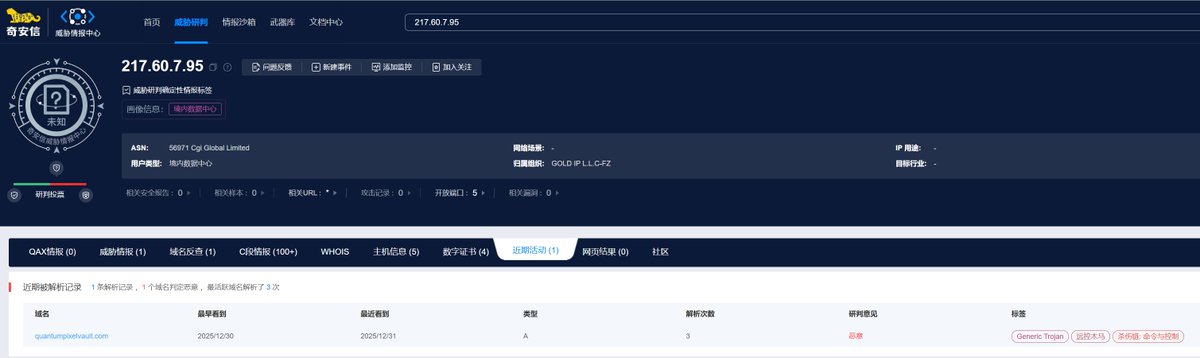
@Dir0nng discovered that the chinese government has been conducting large-scale surveillance on certain groups and stealing their internal information. We identified an IP address 217.60.7[.95] within the system configuration of a government-sponsored hacking.Still remains active
ROSO
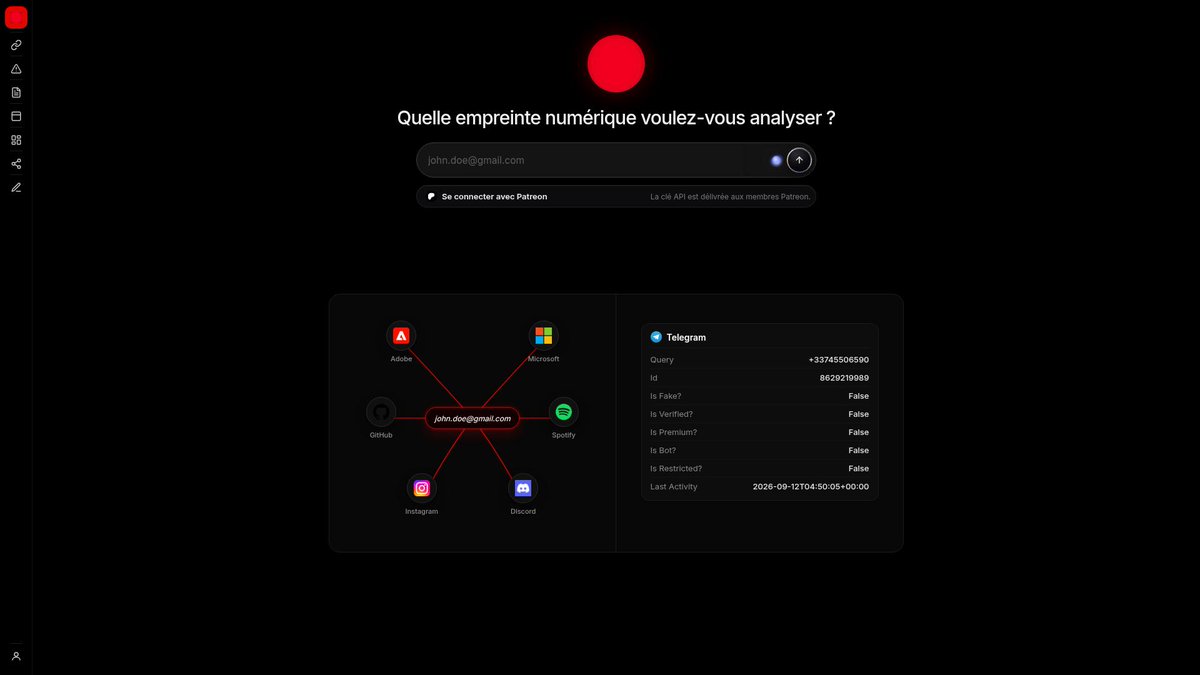
Roso. info is an all-in-one OSINT platform for investigating emails, phone numbers, partial numbers, usernames, domains, IP addresses, and cryptocurrency assets
https://t.co/hAOyjSaIQh
‼️CREDENTIAL EXPOSURE CLAIM — Multiple Countries 🌍
A forum user “DarkSynd” is advertising databases allegedly covering Germany, USA, UK, France, Italy, Spain, Canada, Australia, Netherlands and Switzerland.
The seller claims the databases may contain:
• Full names
• Phone numbers
• Email addresses
• Passwords, where available
• Country and address information
The post also includes what appear to be email/password combinations, indicating a potential credential exposure.
Source: Cerberux Marketplace
Seller: DarkSynd
Posted: September 22, 2026
Status: Unverified
The authenticity, origin, validity, and scope of the advertised databases have not been independently verified. The credentials reproduced in the source post should be treated as potentially compromised and should not be tested or reused.
#CyberSecurity #CredentialLeak #DataLeak #Infostealer #ThreatIntelligence
🚨 Android spyware and RAT source code advertised for $500
⠀
A forum actor using the handle "greekdev" is advertising an Android surveillance application, including its client source code, server code, and web-based control panel.
⠀
Some of the claimed capabilities include:
⠀
• Live microphone, camera, and screen monitoring
• Call recording across messaging apps
• Keylogging, SMS tracking, and notification interception
• Access to files, contacts, and browsing history
• Remote device control and protection against removal
⠀
The actor promises updates for future Android versions, including Android 17, and requires payment through forum escrow.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
🚀 Add Fresh C2 Intelligence to Your Security Workflow
Hunt’s OEM C2 feed gives your platform access to newly identified C2 infrastructure, including activity that often never reaches public OSINT sources. That can mean up to 10x more C2 coverage.
Each result is enriched with host data, malware and threat actor context, associated domains, JA4 fingerprints, and detections from more than 150 techniques.
We also review the dataset every day to keep stale or low-value entries out.
Try it free for 14 days and explore C2 infrastructure detected during the past seven days.
Apply here 👉 https://t.co/MevWob7ePV
#ThreatHunting #ThreatIntel
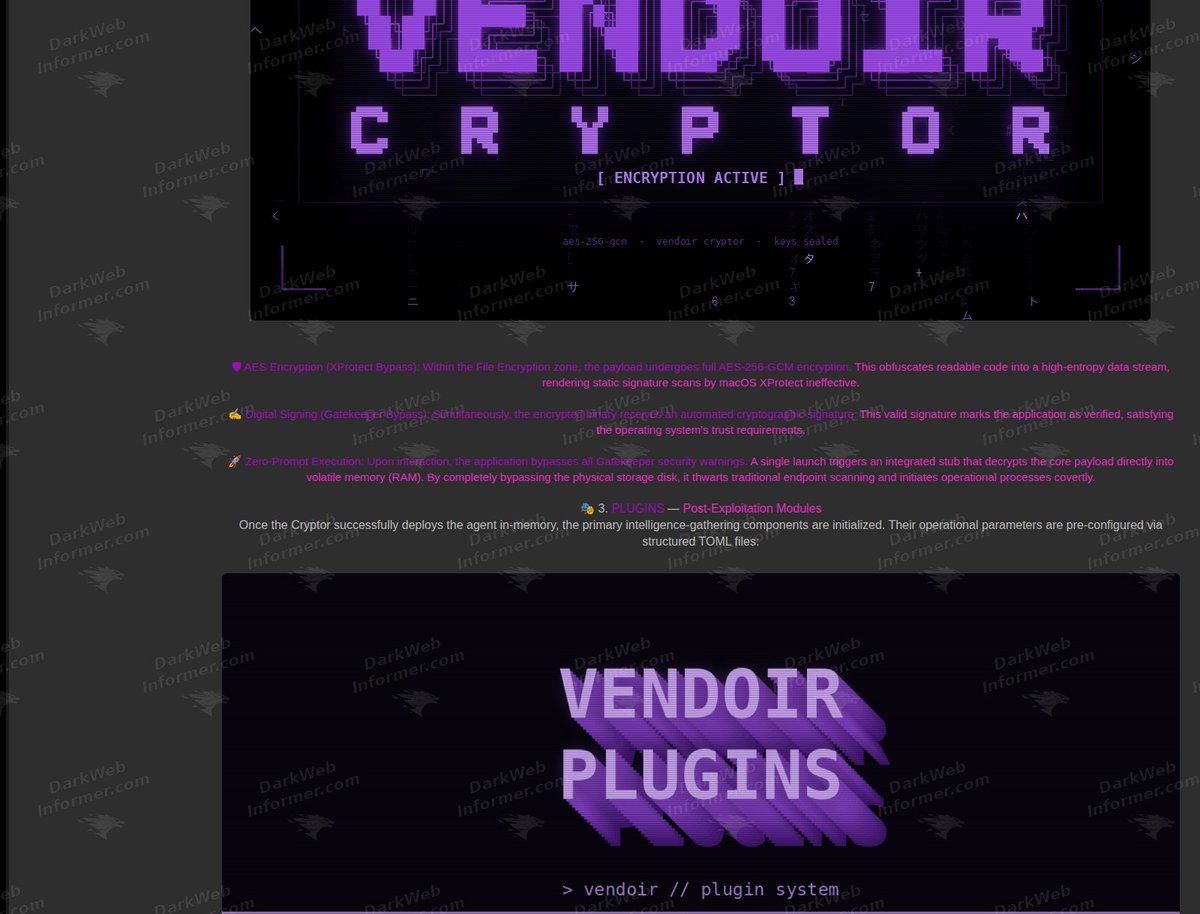
1/2🚨 Vendoir macOS RAT advertised with credential theft, keylogging, and claimed AI integration
⠀
A forum actor using the handle "vendoir" is advertising Vendoir, a macOS remote access trojan allegedly combining information theft, remote control, and security evasion capabilities.
⠀
The actor lists lifetime access for $1,399 and full source code for $6,599, with setup assistance and updates advertised.
⠀
Claimed capabilities include:
⠀
• Information theft: browser cookies, saved credentials, messaging application data, and cryptocurrency wallet private keys and seed phrases
• Surveillance: real-time keylogging and advertised camera access
• Remote control: an interactive terminal, file manipulation, system monitoring, and deployment of additional plugins
• Security evasion: encrypted payloads, in-memory execution, and claimed bypasses of macOS XProtect and Gatekeeper
• AI integration: a claimed DeepSeek-based component for extracting credentials and other information from stolen logs, alongside automated script obfuscation
• Application impersonation: payloads disguised as legitimate applications, including messaging clients
⠀
The source code package is advertised as including the frontend, backend, web panel, and built-in cryptor.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6WSh
🕵️ #RatonRAT uses BAT scripts for execution and cleanup, and scheduled tasks or Active Setup for persistence.
It targets credentials and sensitive data, giving attackers remote access to compromised systems ❗️
How to detect and reduce exposure: https://t.co/AQS4txlD0O
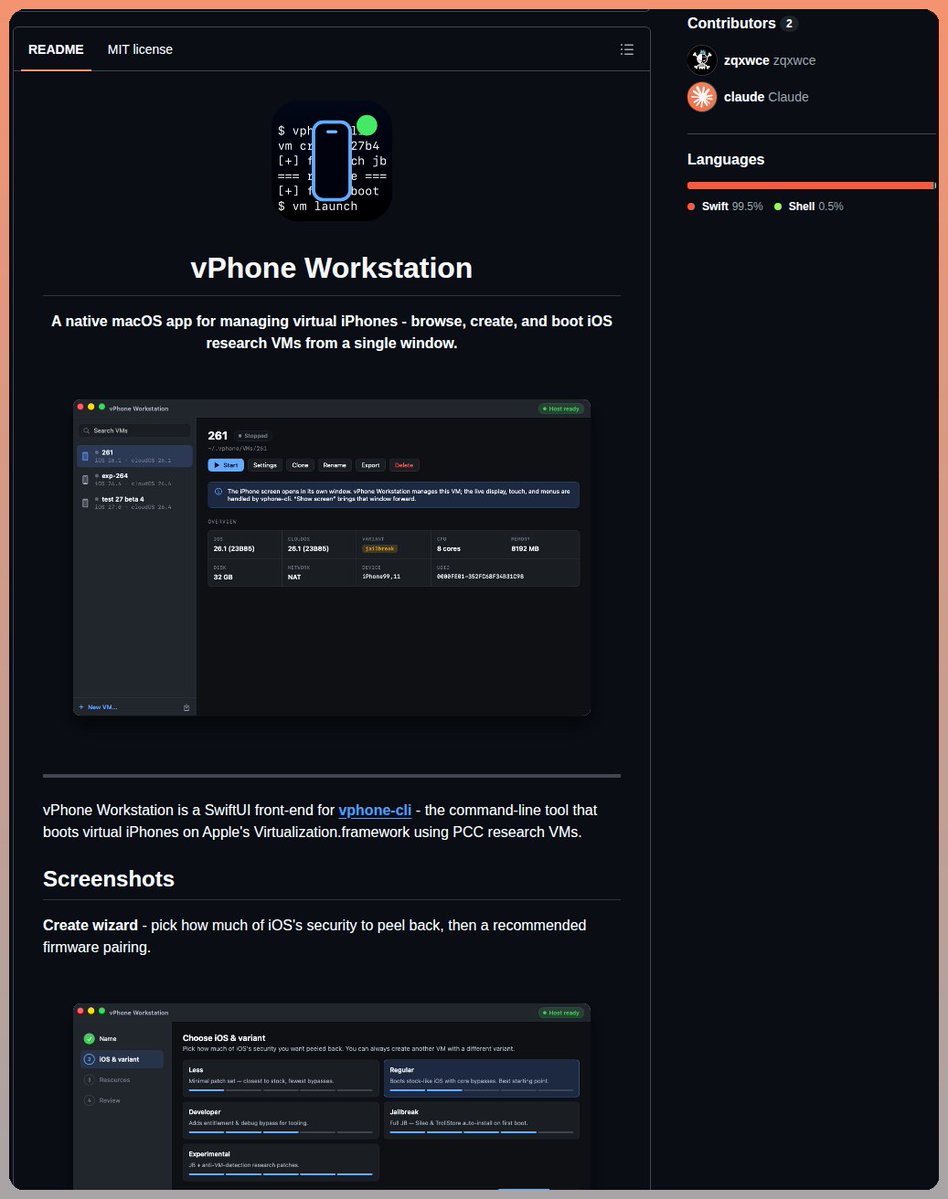
Manage virtual iPhones with vPhone Workstation. This macOS app boots iOS research VMs using the Virtualization framework and offers a wizard to configure security variants like Regular, Developer, and Jailbreak.
https://t.co/sXn2jAaMNb
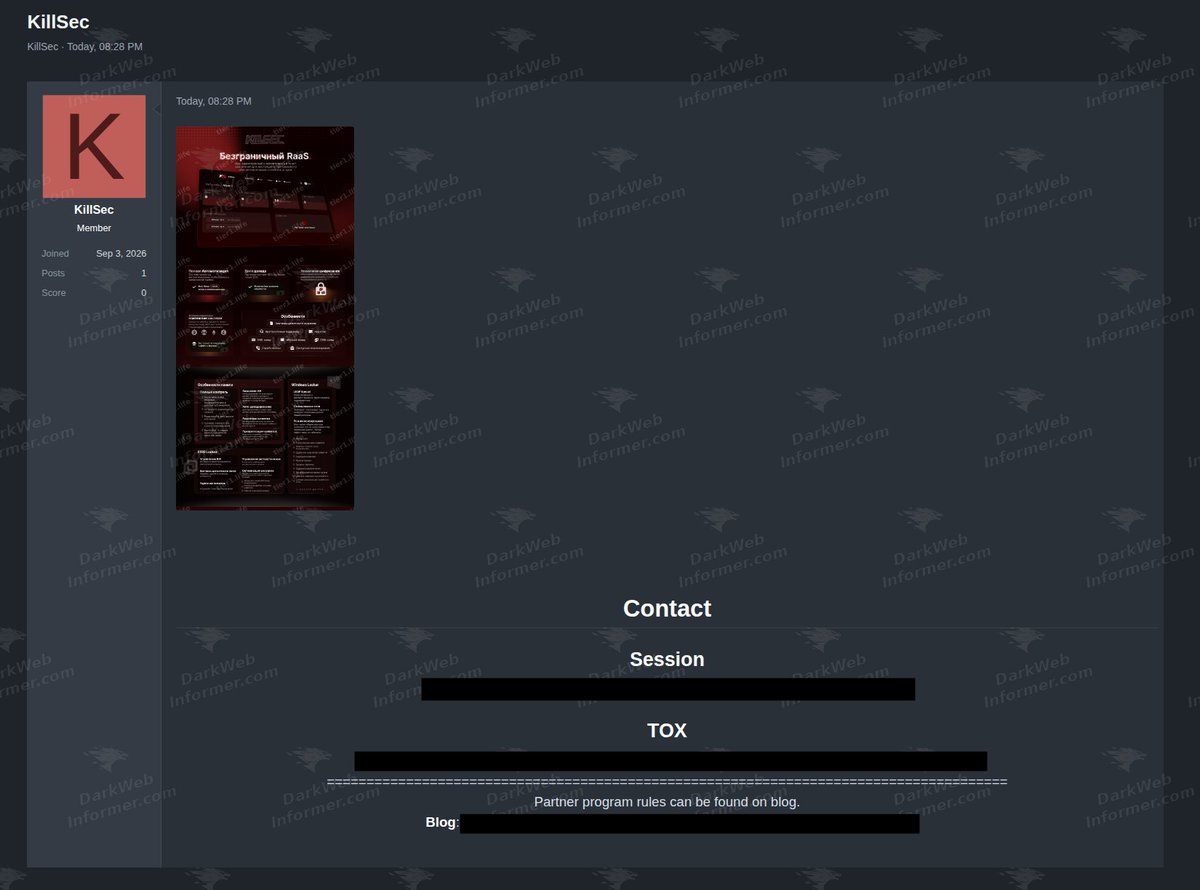
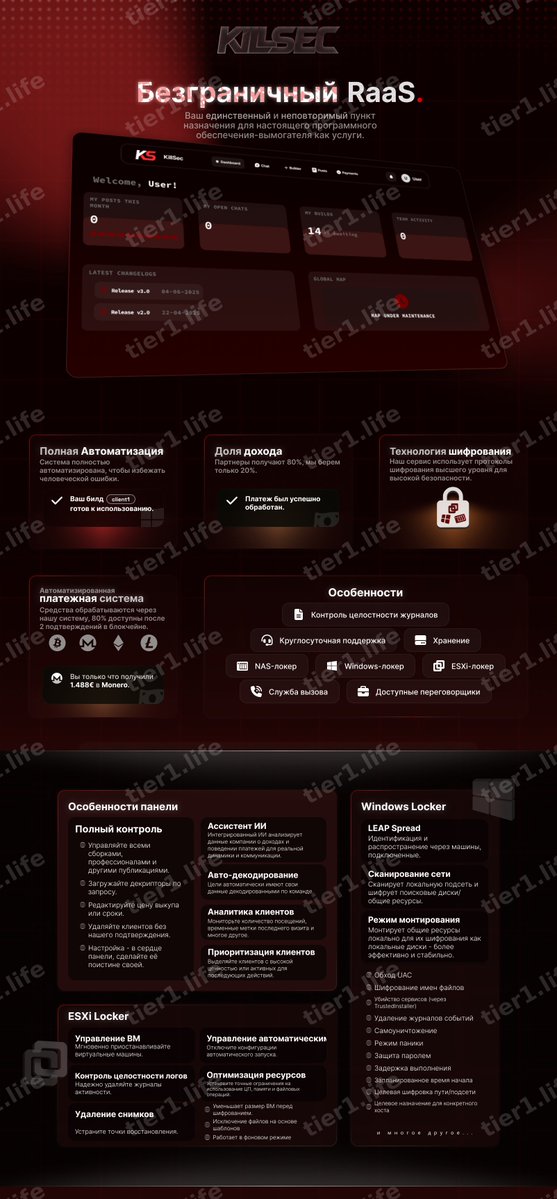
🚨 KillSec launches new ransomware-as-a-service affiliate program
A ransomware group using the name "KillSec" is advertising what it describes as a new "borderless RaaS" platform designed to provide affiliates with ransomware infrastructure, management tools, and victim-handling services.
⠀
Advertised capabilities include:
⠀
• Lockers targeting Windows, ESXi and NAS environments
• Affiliate dashboard for managing victims and builds
• Automated payment processing with cryptocurrency support
• Client analytics and victim prioritization
• Network scanning and lateral-spread functionality
• Encryption, execution-delay and anti-recovery features
• Log and snapshot deletion capabilities
• Built-in negotiator availability and call services
• 24/7 support and campaign-management tools
⠀
The advertisement claims affiliates receive 80% of successful ransom payments while the operators retain 20%.
⠀
KillSec is also promoting features for monitoring victim activity, managing ransom demands, generating builds, and coordinating negotiations through the platform.
⠀
The service, advertised functionality, payment structure, and operational capabilities have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6WSh
17 Platforms where you can begin Cybersecurity Journey
1. HackXpert - Free labs and training.
2. TryHackMe - Hands-on exercises and labs.
3. CyberSecLabs - High quality training labs.
4. Cybrary - Videos, labs, and practice exams.
5. LetsDefend - Blue team training platform.
6. Root Me - Over 400 cybersecurity challenges.
7. RangeForce - Interactive and hands-on platform.
8. Certified Secure - Loads of different challenges.
9. Vuln Machines - Real world scenarios to practice.10. Try2Hack - Play a game based on the real attacks.
11. TCM Security - Entry level courses for cybersecurity.
12. EchoCTF - Train your offensive and defensive skills.
13. Hack The Box - Cybersecurity training platform.
14. Vuln Hub - Material for hands-on experience.15. OverTheWire - Security concepts via challenges.
16. PentesterLab - Learn web-app penetration testing.
17. PortSwigger Web Security - General learning.
🔥 Top 25 XSS Parameters Every Bug Hunter Should Know
🔥 Telegram: https://t.co/upuP8k8ckB
✴️ Twitter: https://t.co/Za7rYILz6E
Finding XSS isn't always about the payload.
Sometimes, finding the right parameter is the first step. 👀
🎯 Common parameters worth checking:
q • s • search • id • lang
keyword • query • page • keywords • year
view • email • type • name • p
month • url • terms • key • l
begindate • enddate • and more…
🧠 Bug Hunting Workflow:
🔎 Discover parameters
➡️ Understand their purpose
➡️ Trace where input is reflected
➡️ Check the application’s output encoding
➡️ Validate safely in an authorized environment
⚡ Remember: A parameter isn't automatically vulnerable just because its name appears on a list. Always verify the application's actual behavior.
📌 Save this cheat sheet for your next web security assessment.
🔁 Repost to help another bug hunter!
#BugBounty #XSS #WebSecurity #AppSec #CyberSecurity #Pentesting #EthicalHacking #BugHunters #InfoSec #WebHacking
OSINT METHODS
39 step-by-step guides to the most common OSINT techniques. Beginner, intermediate and advanced levels.
https://t.co/e5WyEWbjMR
#osint#socmint