@raavanamavan7 Bro when we payed around extra 20rs instead of 50rs. Next 3 times they have tampered with my cylinder. When ever I plugged the new cylinder the gas will come out. Had to change the inner washer to make the leak stop. This is very very dangerous 🤕
@lavanyadeepak@ChennaiTraffic@COPTBM@reclaimchennai If ur thinking ur making good. Nope ur just stupid ask the govt to put good roods first. In night do u know how difficult to ride with no street lights all bike & cars struggle to drive at night
@lavanyadeepak@ChennaiTraffic@COPTBM@reclaimchennai This is just stupid. Making middle class people to pay fines, which they may have used for groceries or for their children. Now people like u & traffic police they have to pay. If u think govt really cares about people safety first thing they would &do is to put proper roads
2/2
மாண்புமிகு ஒன்றிய வெளியுறவுத் துறை அமைச்சர் டாக்டர் எஸ். ஜெய்சங்கர் அவர்களுக்கு மாண்புமிகு தமிழ்நாடு முதலமைச்சர் திரு. ச.ஜோசப் விஜய் அவர்கள் கடிதம்
#CMJosephVijay
Dear @TRAI,
Imagine your recharge plan is going to expire in 2 days.
Imagine someone is following your sister late at night, and she is trying to call you for help.
Imagine you are injured on the road and desperately trying to call a family member.
But before the call even connects, telecom companies play long warnings like “your plan is expiring soon, please recharge” in two languages. During this warning, the actual call does not connect, and valuable time gets wasted.
In emergency situations, even a few seconds matter. These repeated recharge reminders are extremely frustrating.
We already know when to recharge. Customers should not be forced to listen to long, nonsensical warnings.
Please order all telecom companies to immediately stop these nonsense warnings before calls, or allow the call to connect while the warning plays in the background.
Be serious.
@techNmak@grok let me have a good understanding of the Unsloth move by three metrics
1. How it works
2. Why it matters
3. What are potential impacts on existing Claude code ecosystem
The approach to solve this goes beyond simple rate-limiting to implement defensible in-depth posture.
1/ Request validation and throttling:
- Implement adaptive rate limiting per ip, user-agent, and other fingerprints. Token bucket or sliding window algorithm, enforced at the API gateway. Exceeded limits should trigger delays, not just blocks, to waste bot's resources.
- Request fingerprinting by analyzing bot signatures: missing/invalid headers. Impossibly fast form submissions, non-human click patterns.
2/ Filtering by progressive challenges:
- For suspicious requests, we can serve an invisible proof-of-work challenge (example: a small cryptographic puzzle solved). Legitimate users won't notice; bot scripts will fail or be slowed.
- For continued abuse from a fingerprint, present a CAPTCHA. This creates a significant economic cost for attackers.
3/ Behaviour analysis and intelligence:
- Deploy a solution like Cloudflare Bot Management, AWS WAF Bot Control, or a specialized vendor.
These services use ML to analyze request patterns, TLS fingerprints, and behavioural signals to classify traffic as human, good bot, or bad bot with high accuracy.
- For positively identified bad bots, shadow ban them. It means let them think they are succeeding but return fake error messages or infinitely slow responses. This invalidates their attack data and increases their operational cost.
4/ Auth hardening and monitoring:
- Reject known breached password. Enforce strong and unique passwords.
- Aggregate all login attempt logs (success, failure, challenges) into a central system. Then, set up alerts for spikes in failure rates, new bot fingerprints, or successful logins from anomalous locations.
Open-source AI video just got a massive upgrade 🤯
LTX-2.3 sets a new baseline…4K video, native audio plus:
→ New compression model for sharper textures and faces
→ Native portrait mode (9:16)
→ Better prompt adherence
100% Open Source: Weights, code, and training.
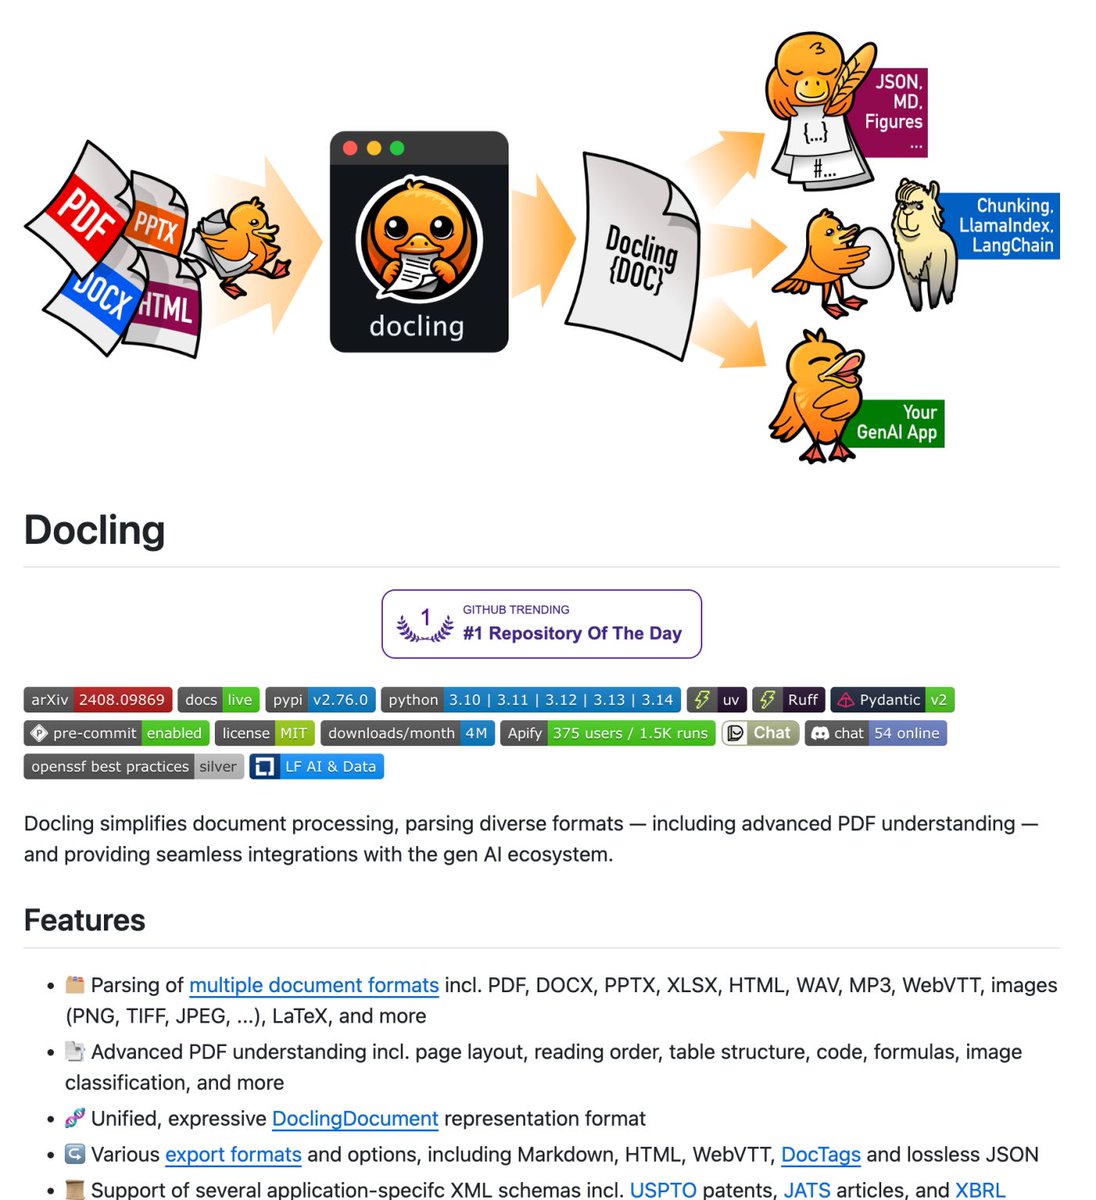
This open-source tool gives your AI agents the ability to read, parse, and understand ANY document format.
It's called Docling. It converts PDFs, DOCX, PPTX, XLSX, audio files, images, LaTeX, and more into clean structured data your LLM can actually reason over.
→ Understands page layout, tables, formulas, and code blocks
→ Exports clean Markdown, HTML, or JSON ready for any LLM pipeline
→ Native MCP server for direct agent integration
→ Plug-and-play with LangChain, LlamaIndex, CrewAI & Haystack
It also just got a production-grade 258M vision-language model that reads an entire page in one pass.
100% Open Source.
I have two EC2 instances.
EC2-A → client
EC2-B (10.0.2.15)→ server running an app on port 8080
From EC2-A:
curl http://10.0.2.15:8080 → works ✅
ping 10.0.2.15 → fails ❌
Security group is open for TCP 8080.
Why does ping fail while curl works?