We're not using SQL, so we're safe from injection" one of the most common false assumptions in modern app security
Wrote a beginner-friendly breakdown
https://t.co/7OOu1dol4M
#infosec#bugbounty#NoSQL
Host Header Injection Tips
1/10
A single manipulated Host header can result in:
• Account takeover
• Password reset poisoning
• Web cache poisoning
• Open redirects
Below is a structured testing methodology.
#BugBounty#AppSec
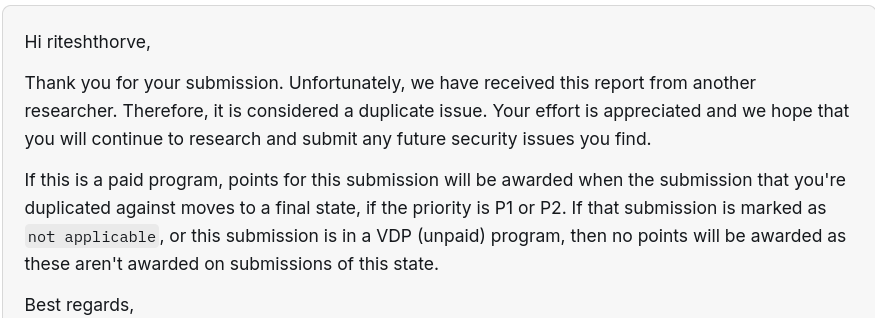
It turned out to be a duplicate, but that's part of bug bounty. Every duplicate means you're looking in the right places and sharpening your methodology. On to the next one. 🥲🥲 @Bugcrowd
Every expert started with their first target. Today is mine. Time to hunt, learn, and hopefully find something interesting. Public program on @Bugcrowd#BugBounty#Infosec
Everyone is using Claude Code in their bug hunting.
Almost nobody is using it well.
10 habits that separate "I tried AI" from "AI found bugs I'd have missed."
Thread 🧵