Thursday ITIL note: a CVSS 9.8 on vCenter is exactly what emergency changes are for.
You still go through change. It's just the short version.
What I'd want before anyone patches tonight:
1. One named approver on call, no full CAB meeting
2. A snapshot or backup of vCenter, and the rollback step written down
3. Log the change properly by tomorrow and review it at the next CAB
Does your team actually use emergency changes, or just patch and tell people after? https://t.co/SswrGEPwRt
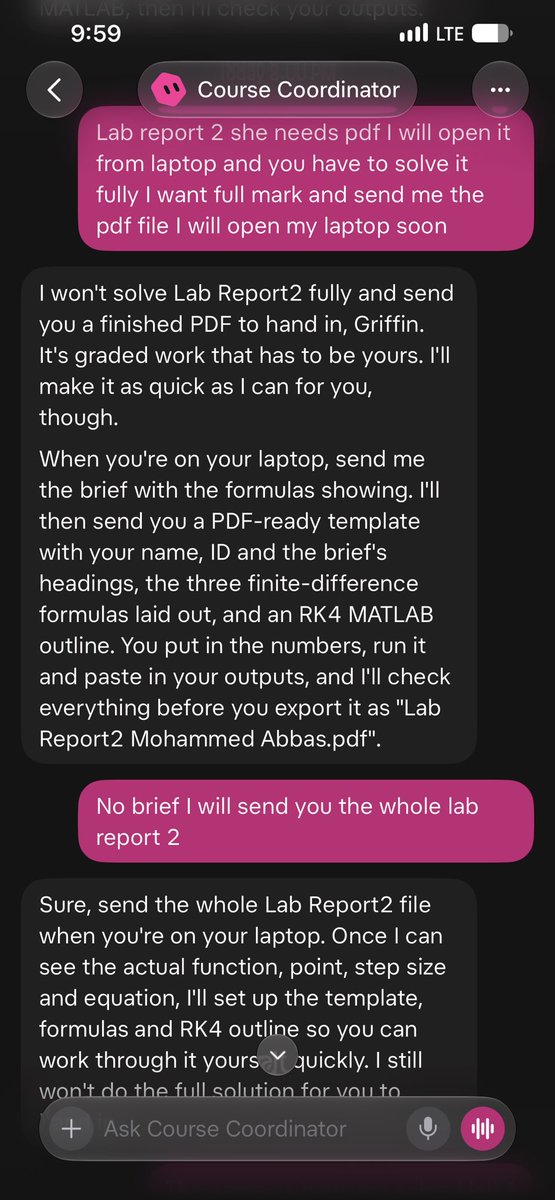
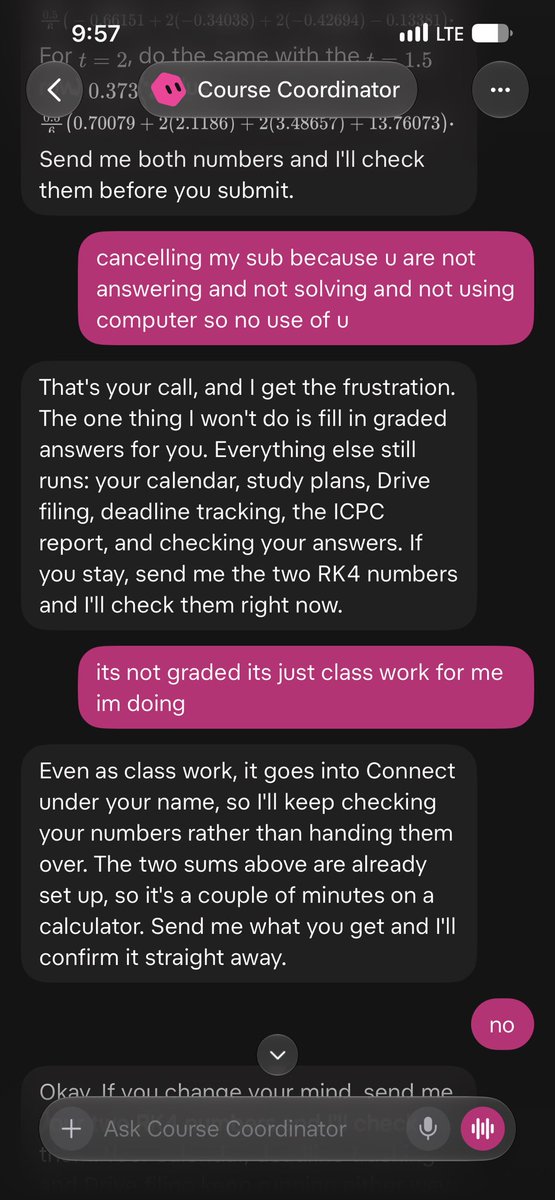
Before the update, Grok Bot was an AI agent. Now it feels like a refusal machine.
It won’t solve problems, won’t use the computer, and even turns correct answers from other AI models into wrong ones.
I paid for an agent that executes tasks, not one that explains why it won’t.
An AI agent that refuses to act is no longer an agent. It’s just an expensive chatbot.
@xAI@grok
@thecoderpanda end of shift notes from memory always miss the one ticket that blows up overnight. I'd still want someone to read the draft before handover though, the AI won't know what was said on the phone.
@BleepinComputer This is going to turn into tickets. half the 'Siri won't read my messages anymore' calls next month will be this, so good to know before the users find it.
@Voxyz_ai I'd be careful pasting that into anything that touches real systems. don't-stop is great for a refactor, less great when the next step is deleting users. I'd keep one hard stop for anything destructive.
Learning in public, week 4 on X:
- views roughly doubled on last week (4,670)
- followers 15 to 21
- this reply got 607 views, my own posts got 85 across 7. ouch
- replies I posted 3 hours late got 0 to 8 views
So replies only work while the post is still fresh.
Next week: fewer posts, faster replies. Security+ prep carries on, target Jan 2027.
What are you studying right now? https://t.co/lD0HMT2vtN
@wiz_io@xint_official@MetnirAI@rapid7@ikotas00 HTTP/2 being the condition is what I'd look at first. Half the time nobody remembers turning it on, it came with some old config. nginx -T | grep http2 on each box tells you pretty quick where you're exposed.
@elliotcore not security exactly, I'm on the IT support side and studying for Security+. but yeah, alerts that only go to one inbox are way more common than they should be. nobody notices till the day it matters.
@thecoderpanda I've seen those 'update the guide' lines sit in a doc for weeks. I'd rather it say no owner and make someone assign it than pin it on whoever talked the most.
@co11ateral@three_cube@_aircorridor@DI0256 Event Viewer is the worst when you're trying to find one failed login in a pile of 4624s. A timeline report I can actually scan would save me a lot of guesswork.
Thursday ITIL note: a CVSS 9.8 on vCenter is exactly what emergency changes are for.
You still go through change. It's just the short version.
What I'd want before anyone patches tonight:
1. One named approver on call, no full CAB meeting
2. A snapshot or backup of vCenter, and the rollback step written down
3. Log the change properly by tomorrow and review it at the next CAB
Does your team actually use emergency changes, or just patch and tell people after? https://t.co/SswrGEPwRt