Hezbollah has fired rockets from a high school in the village of Kfar Shuba, using the children inside as human shields in an attack on an IDF base on Mount Dov. A mosque is also in close proximity to the high school, hindering the IDF from neutralizing the Hezbollah fighters. Where is @UNIFIL? #Israel_under_attack
I was able to access thousands of companies’ passwords on #Azure and run code on their VMs.
This includes access to Microsoft’s own credentials… 💣
Here’s HOW I did it.
This is the story of #SynLapse. (1/11)
I was able to access #Azure user credentials and run code on other customers’ machines.
The vulnerability is called #SynLapse.
It was a vulnerability in Azure Synapse Analytics (@Azure_Synapse) & Azure Data Factory, exploiting a major flaw in the tenant separation.
(1/3)
😱😱😱 This is worse than ChaosDB for AWS. @orcasec gained access to all AWS resources in all AWS accounts! They accessed the AWS internal CloudFormation service.
https://t.co/2oCCRvo389
Separately, they did something similar for Glue.
https://t.co/BDFMLQI06B
Orca Security announces a 55M series B round led by @ICONIQGrowth, bringing overall @orcasec funding to over $82M since its inception less than 2 years ago! This funding will help further transform #cloudsecurity for global enterprises. https://t.co/i7fijhOJVz #cybersecurity
Our researchers were able to fingerprint and track PlayBit — a prominent exploit developer whose Windows LPE exploits were used by infamous crime groups like REvil and Maze.
We analyzed their exploitation techniques and share some intelligence about them.
https://t.co/M592nmSL3t
#Security has always been about transparency, & the #cybersecurity community should have free access to all of the facts. My thoughts on @PaloAltoNtwks' lack of transparency & wielding of dubious legal methods in response to our Cloud Punch-Out comparison: https://t.co/Kdx3UcbRab
TL;DR - We scanned most of the AWS Marketplace AMIs for known vulnerabilities, reported to individual vendors so they will update their AMIs.
We see many customers using marketplace images, and since they are essentially black boxes, they can become easily outdated & exposed
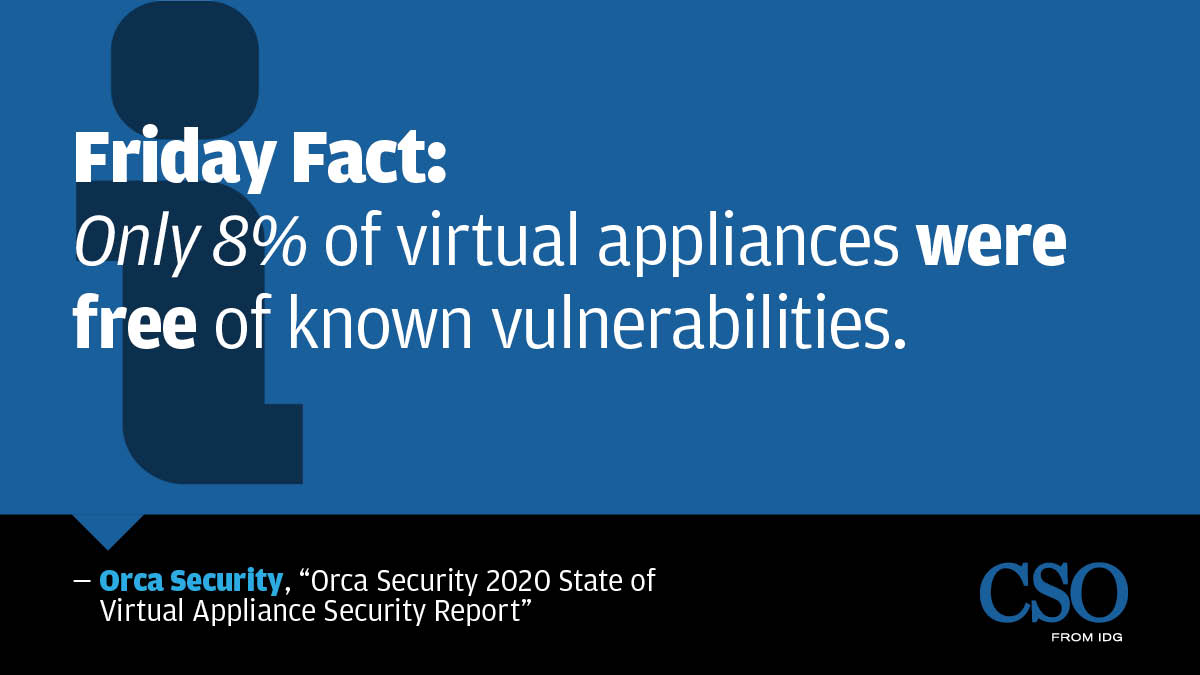
How responsible are your software vendors? Maybe not as responsible as you would think. @orcasec security researchers found that many software vendors fell behind on keeping #virtualappliances patched & secured. See the report: https://t.co/QcdWA08o6i #cybersecurity#ITsecurity
As orgs rapidly deploy more assets in the #publiccloud they’re leaving many paths open for exploitation. Our 2020 State of Public #CloudSecurity Report shows that 80% of orgs have a neglected frontline workload which can lead to devastating #databreaches. https://t.co/O2WRaILvNE
Operation Tripoli: The story of how a Libyan attacker took advantage of #Facebook pages, spread malware to tens of thousands of victims, and how @facebook and @_CPResearch_ eventually took it all down.
https://t.co/gesB7hU4nN
[New Blog] The need for solutions that can provide full-stack visibility for an entire cloud environment is more pressing than it has ever been. Find out why in our latest blog>>https://t.co/lxX8vEcwTB #cloudsecurity
At @_CPResearch_ we have just released our own vulnerability repository.
There is *a lot* of work put into each of these items. Enjoy (!)
Sharing is caring.
https://t.co/xKGKuDggHv