Here it is. If you are a professional, if you are under NDA with your clients, if you are a creative, a lawyer, a doctor or anyone who works with proprietary files - it is time to cancel Adobe, delete all the apps and programs. Adobe can not be trusted.
Breaking: #Ticketmaster has allegedly been hacked by ShinyHunters, extracting 560M user details, ticket sales, orders, event info, and card data, per Hackread's @WAK4S. The total data is over 1.3 TB as per the hacker - There is a post about it on the #BreachForums as well.
Breach Forums Update
An individual obtained the ring doorbell camera footage of former admin 'pompompurin' getting raided by the FBI in march of last year.
I've blurred the faces of agents and his mother for obvious reasons. All I ask is to please leave his family alone.
Strap yourself in because it's time for this weeks episode of "Microsoft being dedicated to security".
tl;dr wtf bro lol
Previously Microsoft unveiled 'Recall' – which will be deployed on Windows 11. Recall will take screenshots of your computer desktop, in unspecified intervals, and allow users to search through Recall data (aka your Desktop screenshots) using AI to allow users to ... find things they may have forgotten (???).
When Recall was announced numerous security researchers, cybersecurity firms, and privacy advocates called it a nightmare because Microsoft explicitly stated that Recall will make no attempt to perform content moderation. It will take screenshots of plain text passwords, financial data, etc. Users also expressed concerns over Recall recording sexual fetishes (i.e. them watching pornography) and called it a gross invasion of privacy.
Microsoft's retort was that Recall can be disabled in settings and Microsoft does not have access to any of the data. It is all stored locally. Researchers then questioned whether or not end users, who may not be as tech savvy, would even understand or know Recall is present and may not be able to disable it.
Microsoft also stated today to the BBC that because Recall is stored locally, the only way a Threat Actor would be able to access Recall data is if they have physical access to the machine, unlocked it, and then signed in.
This did little to persuade security researchers because, if the data is stored locally, they expressed concern of the possibility of Recall data being harvested by infostealer malware (e.g. Redline, FormBook, Rhad, etc.) or the data being exfiltrated in the event of a ransomware attack. Furthermore, if Recall is deployed on Enterprise environments, this may make Recall an even larger security risk due to the lack of content moderation (i.e. exposing crown jewels).
With Recall present, and if data can be imported or exported, it could essentially allow Threat Groups the ability to visually inspect and review victims machines using AI search.
Will researchers find a way to abuse Recall? Will Threat Actors find a way to abuse Recall? Will there be 'for educational uses only' proof-of-concepts on GitHub? Find out on the next episode of Dragon Ball Z
private trackers: a place where by definition everyone is doing something illegal (cracks, copyright infringement, etc)
also private trackers: PLEASE LOG IN FROM YOUR HOME IP ADDRESS. VPNS PROXIES AND NON-RESIDENTIAL IP ADDRESSES ARE NOT ALLOWED
???
Awhile back we heard rumors of a Telegram RCE 0day. We brushed it off as silly memes. Turns out the 0day was 100% real and you're all probably pwned.
It was unveiled on XSS. Nerds celebrated
(joking about pwned part... kind of)
More information: https://t.co/KNbNdS8aTw
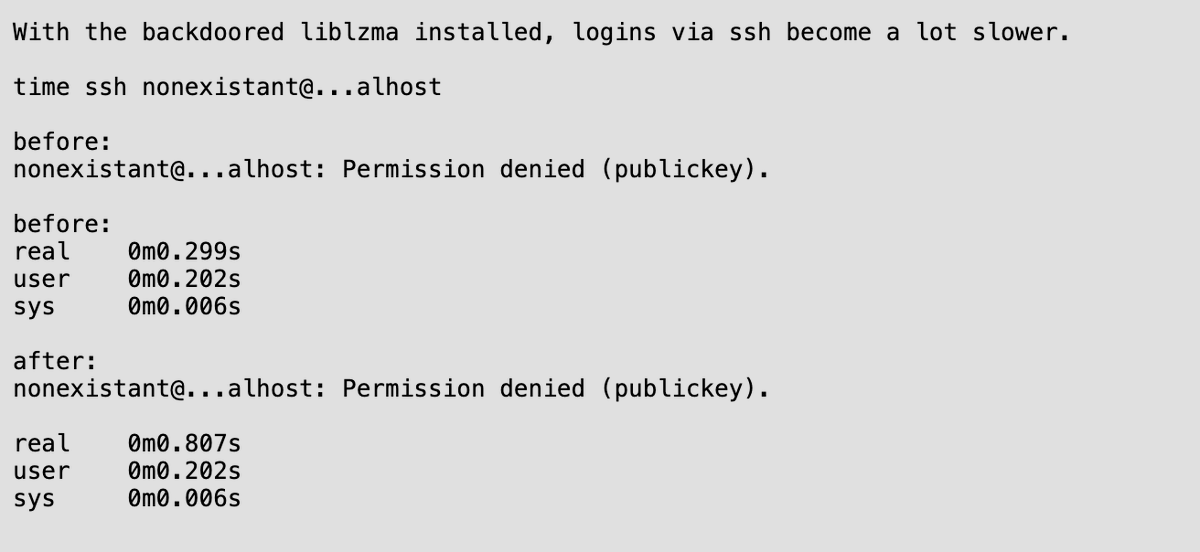
The xz backdoor was initially caught by a software engineer at Microsoft. He noticed 500ms lag and thought something was suspicious.
This is the Silver Back Gorilla of nerds. The internet final boss.
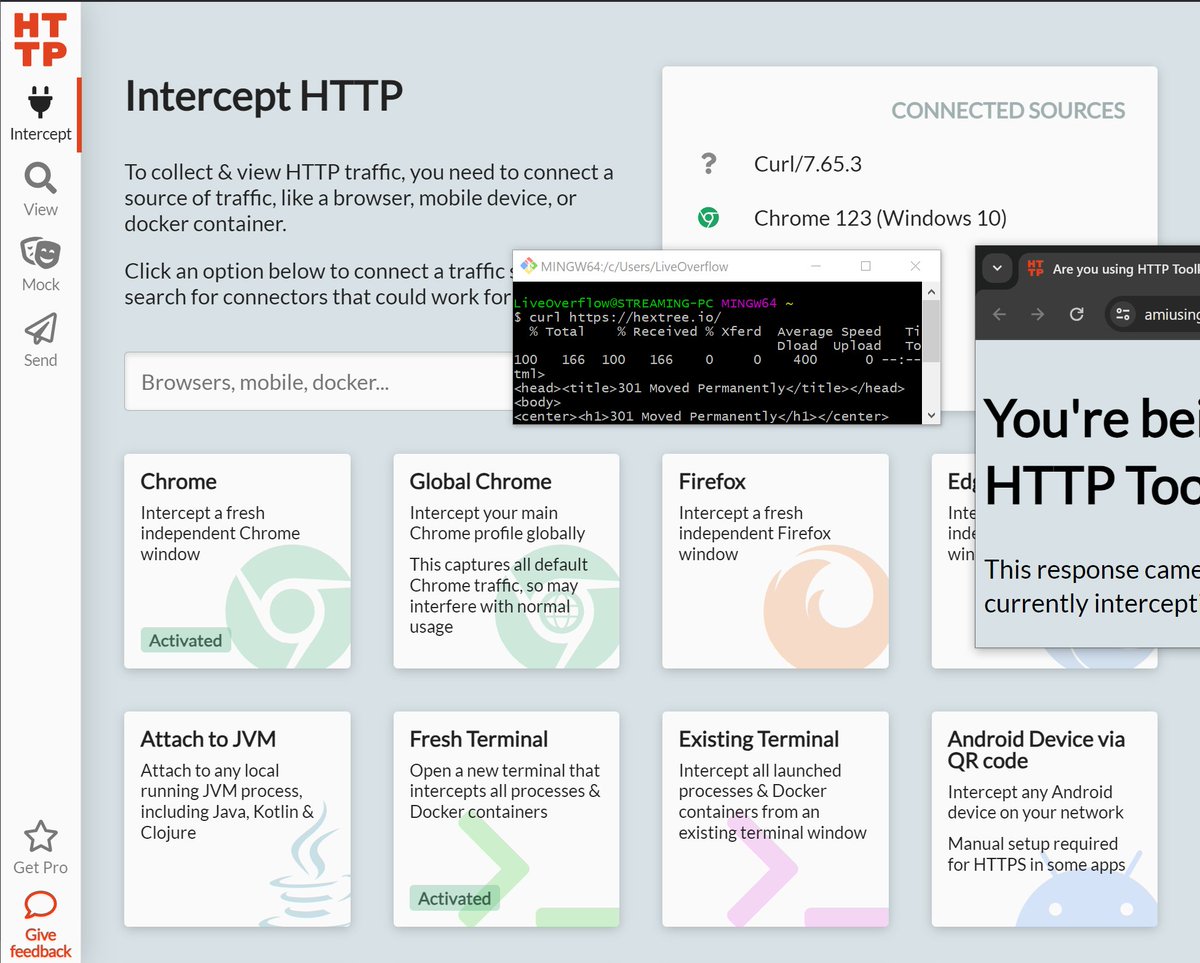
Shoutout to @pimterry and @HttpToolkit. Incredible convenient to quickly configure a proxy for various programs - including browsers, shells and Android.
Also great writeup about the technical details of the android interception changes in Android 14 🙇♀️
https://t.co/nimk8GdSPM
In interviews, meetings, and conversations, when asked about a topic you don't know much about, say you don't know much about the topic.
It makes people value the topics you do know a lot about much more!
Microsoft has discovered nobody actually wanted to install Uber Eats and micro-transaction-pay-to-win mobile games on their desktop computer
RIP Windows Subsystem for Android
2021-10-20 - 2025-03-05
One if our primary recommendations to younger people is to immediately, without hesitation, involve yourself in the cybersecurity-ecosystem. It does not matter if it is Twitter, Mastodon, whatever, but it needs to be done.
The reason why is not social networking (although this can help). The real reason why is the constant, nearly suffocating, flooding of information, news, and research. Every single day we see new malware analysis papers, research papers on nearly every IT-based field you can conjure, and news on cyber crime, technological advancements, or 'futurism'.
Of course the quality of the things mentioned varies on an almost hourly basis, but this constant stream of information will allow you to continually educate yourself and grow as a person. We are not recommending you be glued to Twitter (or whatever you choose), but simply logging in once a day, before bed or in the morning, and just simply doom-scrolling the website, seeing the horrors unleashed, will allow you to grow.
Also, you will collect a colossal 'to-read-list' in your bookmarks and every so often you'll read 1 or 2 papers and become depressed that you didn't think of the research they shared sooner.