El historial de versiones del documento. 214 revisiones. Cuatro horas y media de escritura repartidas en tres días, con sus borrados, sus frases a medias y sus pausas.
El profesor lo miró y me dijo que el sistema de detección es muy fiable.
Le pregunté qué margen de error tiene. No lo sabía.
Le pregunté quién había validado ese 97 %. Tampoco.
No denuncié a nadie. Presenté la revisión de la calificación por escrito y adjunté el historial.
Se la corrigieron a la semana siguiente.
Lo que me preocupa no es el cero. Es que a mi hija le dijeron delante de la clase que había hecho trampas, y la prueba de que no era así la tenía yo en una pestaña del navegador.
Están usando una máquina para acusar a adolescentes sin saber cómo funciona la máquina.
🚨 OUTRAGE: A man literally BEHEADED the historic Iwo Jima monument with a sledgehammer at Quantico. Hundreds of thousands in damage to honor our brave Marines! Is he here illegally? DEPORT HIM! The left attacks our history while we honor our heroes. Throw the book at him! 🇺🇸🔥
WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners.
Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads.
Firmware was locked down, so zero-days it was.
Got a root shell.
then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems.
This isn’t a bug, It’s the product bro.
‼️ BREAKING: Trend Micro posted several unpatched Linux kernel flaws to public mailing lists.
Two are critical remote code execution bugs in the kernel's SMB server, and one includes proof-of-concept code.
Linux maintainer Greg told them to "fix your submission process."
Removed all of the samsung spyware from my TV with Codex (Claude refused to root the tv lol)
It's insane how much bloat samsung packs into their TVs to track you and sell your data. Here's just some of what I turned off that made my tv 3x faster:
- screenshot your screen a few times a second to see what you're streaming and fingerprint you to sell your data
- reading your hdmi inputs to do the same thing while you have a game console plugged in
- Voice assistants: Bixby wake-word detectors listening and tracking what you say in your house
Before and after speed of my TV:
Internet encryption is currently having a nuclear meltdown.
Cryptographers are calling it "bigger than Heartbleed."
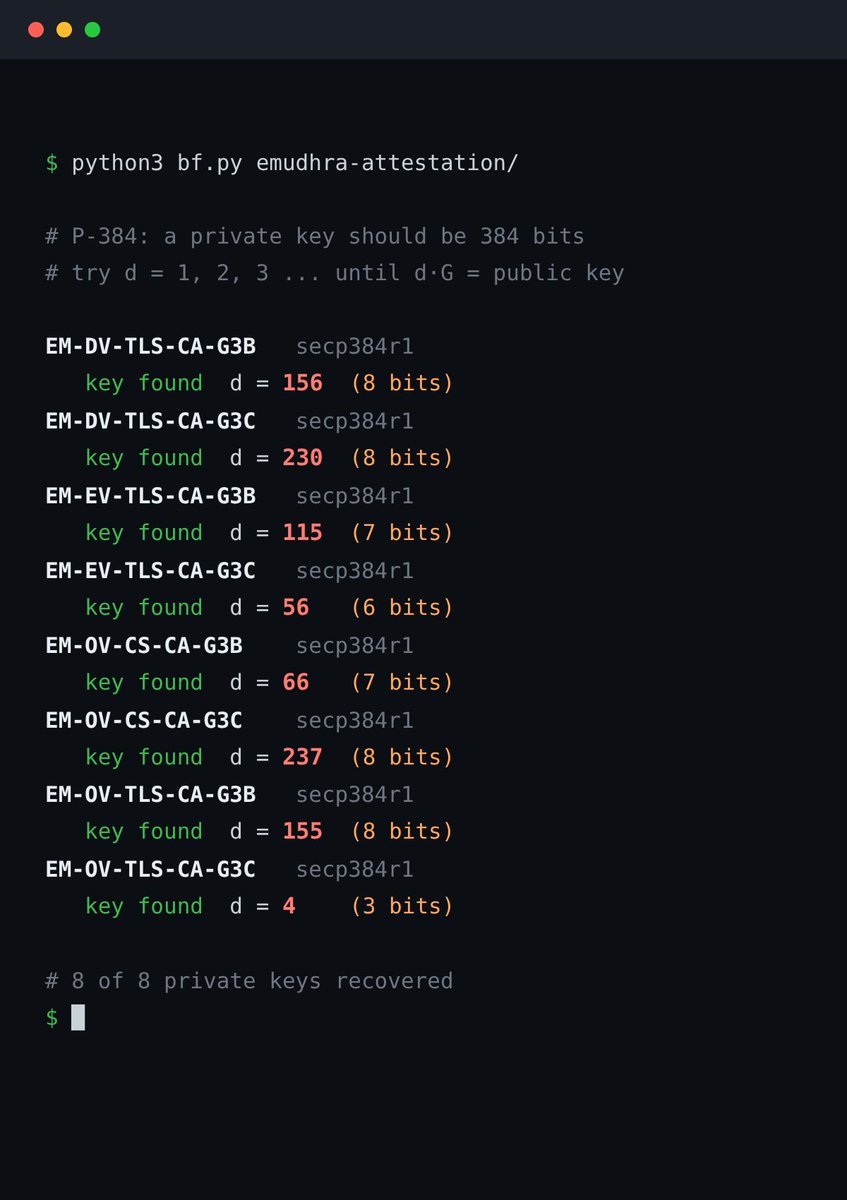
A global Certificate Authority just leaked 8 master private keys that allow anyone to impersonate any server on Earth (Google, banks, government sites).
A normal master key has 116 digits of entropy.
The actual leaked keys?
4. 56. 66. 115.
A toddler on a calculator could have cracked them.
While browsers patched it today, millions of IoT devices, Linux servers, and Docker containers will take years to clean up.
We bet global digital security on centralized human gatekeepers who forgot to check their math.
True security can't rely on trust cartels. It has to be governed by mathematical consensus.
See the signal. ♾️
‼️ BREAKING: Two leaked remote code execution flaws in PHP are real, watchTowr confirms.
PHP will ship fixes for two critical flaws, both rated CVSS 9.2, on Wednesday 21 October at 14:00 UTC, a day before the embargo was due to lift.
CVE-2026-109618 and CVE-2026-109619 first surfaced in a Hacker News post whose author admitted having no evidence beyond "source: trust me, bro".
Kevin Beaumont flagged the leak, and watchTowr confirmed it two hours later.
PHP says it may release sooner if details go public or exploitation appears. It has not named the CVEs or the affected versions.
> wake up
> take a shit
> get out of bed
> check beep boop
> everyone saying ooga booga PHP
> wtf why
> look inside
> ultra mega fuck off exploit coming
> php2shell
> so bad PHP devs begs nerds to patch tomorrow
> proof of concept video released
> pwn website easily
> video has dancing anime lady?
> nobody explains why dancing anime lady
> no one even asks why proof of concept has dancing anime lady
> ok
> cybersecurity nerds bamboozled
> some saying will be up there with Log4J in severity
> goopocalypse
pic unrelated
‼️ BREAKING: The private keys of 8 certificates from Indian certificate authority eMudhra were compromised, Mozilla says. Firefox blocked them within 3 hours.
Each key should be a 116-digit number, but one was just 4.
Anyone can guess them and forge HTTPS certs for any website.
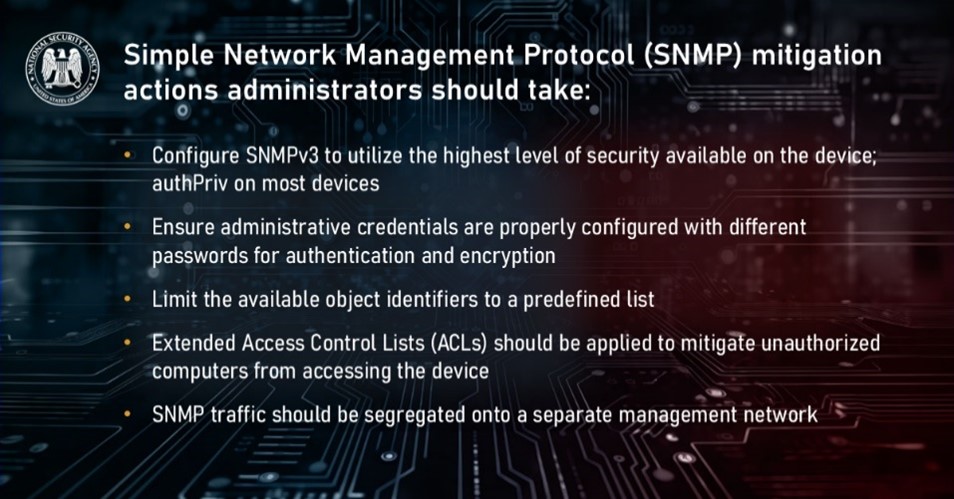
Stop Russian compromise of your network devices by hardening your SNMP. We urge NSS and DIB admins to move to SNMPv3 immediately to ensure payloads are authenticated and encrypted. Full hardening guidance here: https://t.co/dDj8IwwR3R
In Memory of Randolph “Randy” Mantooth
Randy Goes on one last run with his lifelong friend and co-star Kevin Tighe inside Squad 51.
On October 17th, a Flag Ceremony was held at Station 127 (Station 51) as Randy left the station for the last time.
Rest easy, Johnny.
📷:Los Angeles County Fire Museum
> be @malwrhunterteam
> on a legendary run on social media
> find silly website
> estrosa-dot-it
> website for italian cosmetics
> legit website, used by the pasta people
> notice something silly on website
> /js/analytics/assets/js/group.html
> look inside
> group.html checks browser agent
> detects iOS version
> loads different files depending on iOS version
> loads 49554fde7424c31c.js
> 49*.js doing lots of crazy stuff
> layers of obfuscation and pointer arithmetic
> lolwtf
> look inside
> exact match of Coruna EK
> Coruna Exploit Kit
> Coruna originally used by US government
> rumored to be made by US contractor
> rumored US contractor illegally sold to kremlin
> UNC6353 (kremlin) found using Coruna in 2025
Chat, someone is swinging the legendary goop around. It is Coruna, the state-sponsored iOS exploit kit. All this requires is your Apple device to visit a website and (assuming you're running the targeted iOS version) you're cooked.
Although, from my initial bonking of it, it appears this delivers two different payloads depending on the iOS version. Unfortunately, I know almost nothing about iOS exploitation and iOS malware, so I have no idea what I'm doing. I encouraged my peers and colleagues to review it. It is good goop.
I've archived the payloads from the compromised domain. The shared link is below.
pic unrelated
🚨 An unpatched Broadcom Wi-Fi flaw lets attackers within radio range execute code as ROOT on affected routers, without a Wi-Fi password or pairing.
Researcher demonstrated password extraction and a remote shell. Potentially impacting millions of routers.
Read - https://t.co/bm22ftXx1u
‼️ UPDATE: A researcher says the Broadcom Wi-Fi router bug affects way more countries.
The vulnerable code is also in ZTE's F680 v4, which ISPs from Spain to Vietnam, Egypt and Moldova offer.
Three Movistar Spain routers appear affected. Broadcom still won't assign a CVE.
‼️ A researcher disclosed six Linux kernel bugs that give root, escape containers and affects Android phones.
"Infinity Core" hits the timer, signal, memory, futex, scheduler and SLAB code, five with working root exploits.
One roots a Galaxy S26 Ultra from an ordinary app.