Heads up to fellow hunters: Please avoid hunting on Bitkub Capital Group Holdings on @HackenProof. I reported an unauth GraphQL endpoint with full CRUD on live content. The report was closed as OOS, my appeal was denied, and the company called it "intended behavior"
#BugBounty
Heads up to fellow hunters: Please avoid hunting on Bitkub Capital Group Holdings on @HackenProof. I reported an unauth GraphQL endpoint with full CRUD on live content. The report was closed as OOS, my appeal was denied, and the company called it "intended behavior"
#BugBounty
Went to DeepSeek to generate an XSS payload.
Ended up finding a Critical Stored XSS in its HTML Preview sandbox instead. 😂
Full writeup is live! 👇
https://t.co/WG8Qacfoq9
#bugbounty#infosec#Xss
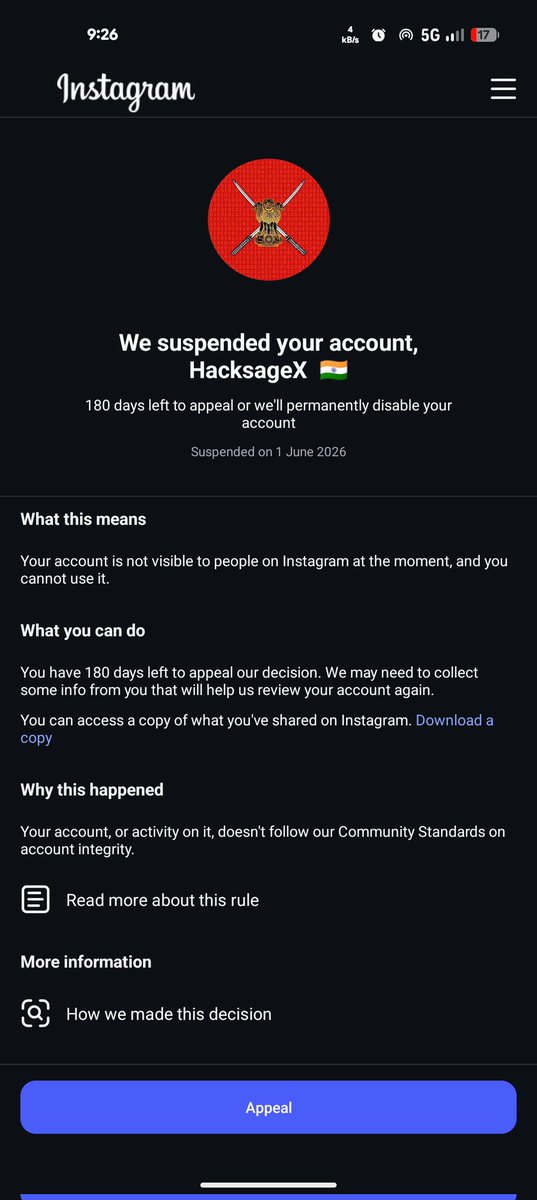
@Meta@MetaNewsroom And now, it’s completely disabled. Meta’s bots handled the ban, the same bots handled the appeal, and now the system says the decision is final with zero options to request a manual review.
@Meta@instagram
Really frustrating to see @Instagram's automated system killing security education pages. My account hacksagex was suspended and the appeal was instantly rejected with zero explanation.
2/2
There was no policy violation. Getting locked out of a research profile by an automated loop with zero human oversight is completely broken. If anyone at @Meta or @MetaNewsroom is paying attention, please look into this.
Just hit a duplicate on @intigriti 🥲 Triager bumped it to Critical (€1,500 value) which is awesome, just wish the platform showed the original report reference for clarity.
#bugbounty#duplicate#intigriti
I just published How I discovered Vulnerability in Bridge Reserve Management (CVE-2026–41204) https://t.co/cVjy13HDhE
#Web3#bugbountytips#CVE-2026-41204
🔥 Just dropped a new case study! How I crashed a Layer 1 blockchain node with a single vote.
Total impact: Critical | Bounty: 15,000 on chain coin | CVE: CVE-2026-40583
https://t.co/swbQ7Y5Hxh
#CyberSecurity#BugBounty#Web3