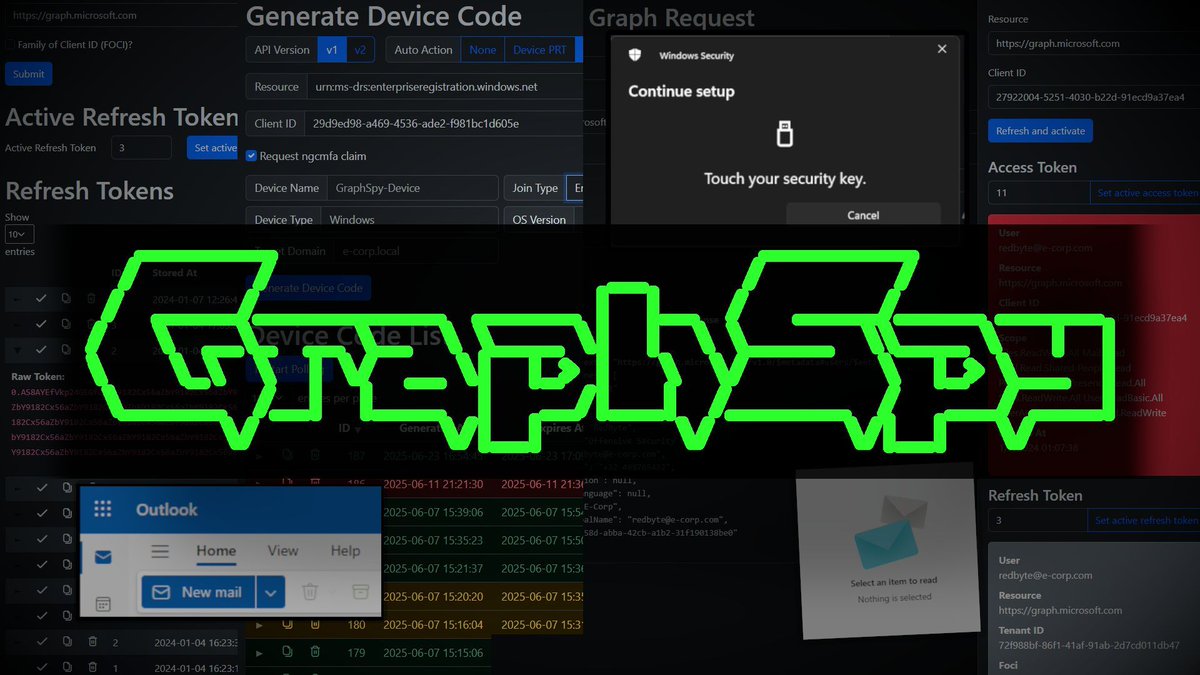
🚀I'm finally releasing GraphSpy to the public!🕵️
A powerful offensive security tool focused on making initial access and post-compromise enumeration in Microsoft Entra and M365 much more convenient during penetration tests and red team assessments!
https://t.co/OfI2TanQ61
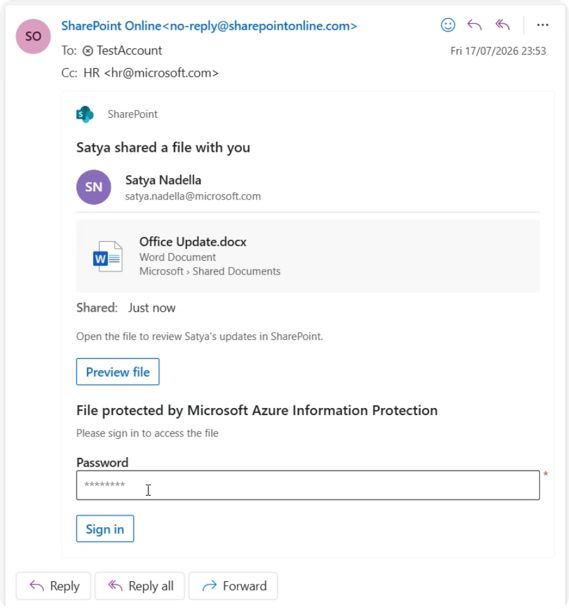
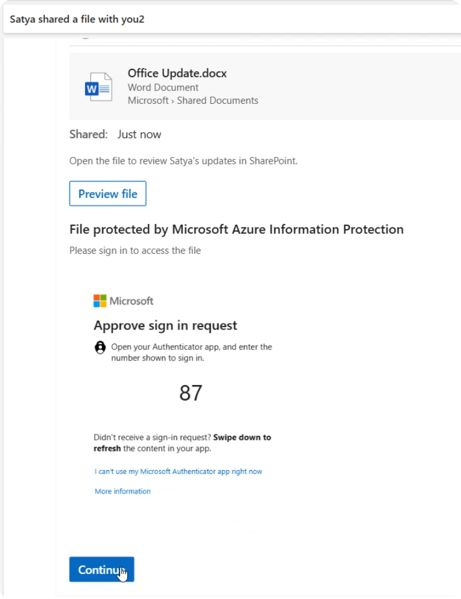
Have you ever seen a phishing email in which a working password prompt is in the actual email body + a dynamic MFA prompt? 😜
Come check out this (and several other) new phishing techniques in action during my talk tomorrow morning 11 am CEST on stage at @brucon, or its stream!
Excited to be back as a @defcon mainstage speaker in Vegas for the 2nd year in a row! 🎉
This year I'll reveal new techniques to get Microsoft to deliver any phishing email from official Microsoft addresses. Plus... interactive phishing pages rendered inside email clients!? 😜
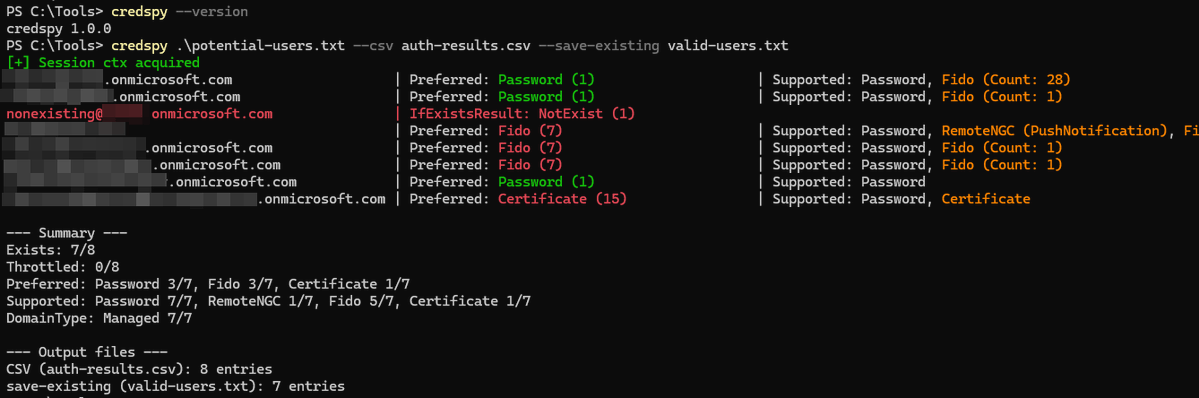
Just open-sourced CredSpy
Couldn't find any tools that allowed unauthenticated enumeration of auth methods for @Microsoft accounts, so I created it.
Shows whether target accounts use Passkeys, certificate auth, passwordless push, etc...
Find it here: https://t.co/BZ7XfHi5KW
@_dirkjan "Sadly this is another example where the documented restrictions we read about on Microsoft Learn are accurate for our applications, but not always for Microsoft’s own apps."
Microsoft:
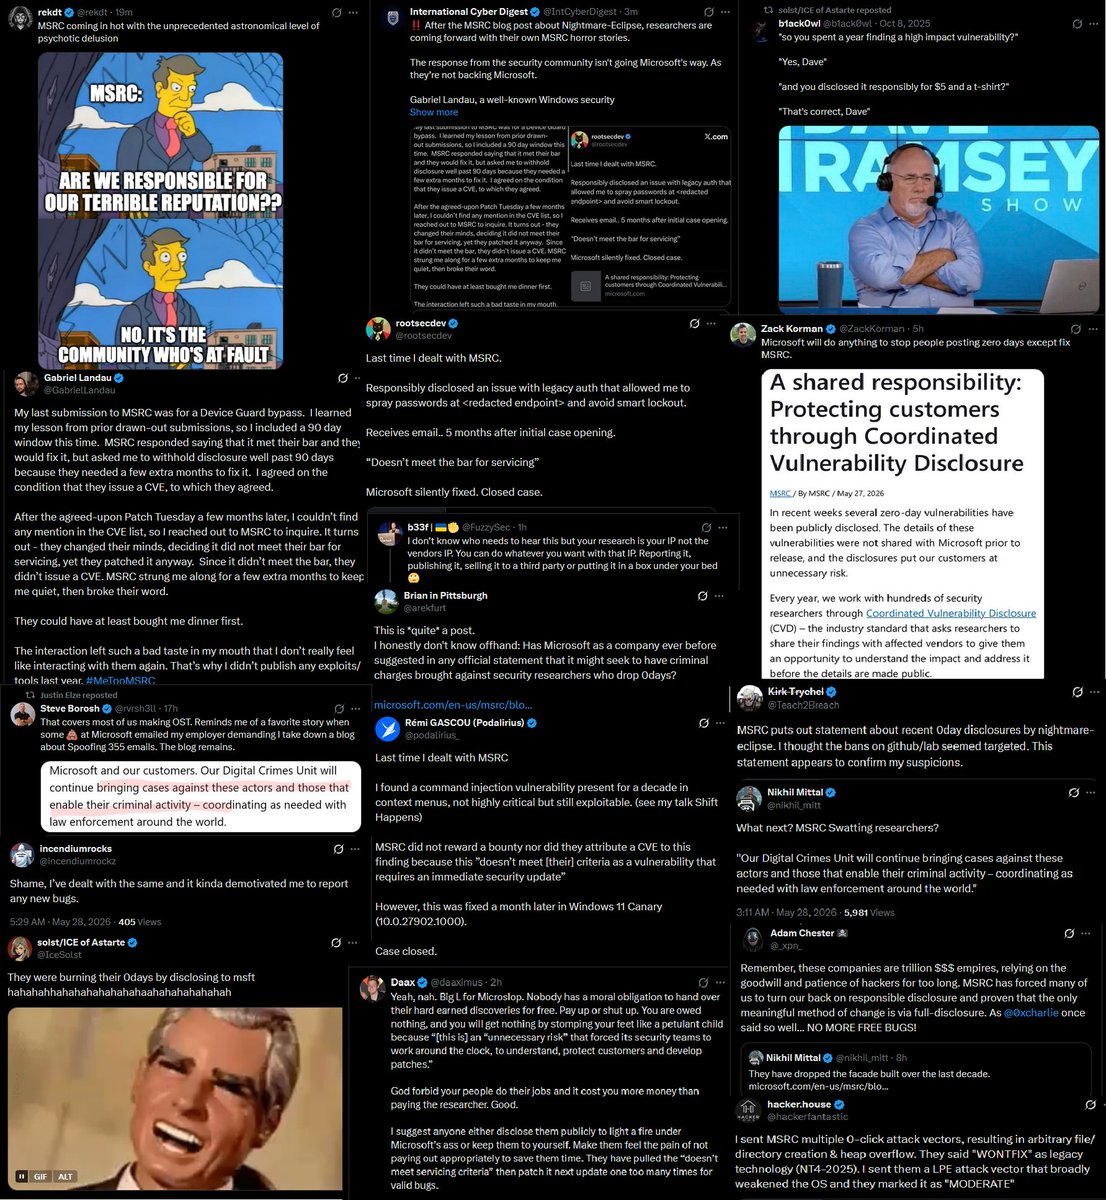
This is exactly why I did not share my research with MSRC before my talk last @defcon, to make a statement against their classic "does not meet the bar for servicing (unless you publish it)" response.
Next DEF CON will be interesting...
Chat, I don't want to be that guy, but I think Microsoft has really pissed off security researchers and we're approaching the tipping point.
This Eclipse guy has really rocked the boat for Microsoft.
@defcon I even dedicated the first three minutes of my talk to calling them out for these practices.
They came to me afterward and told me I would have gotten at least a $10k bounty if I had reported it. Sure...
https://t.co/MoPQiKgesd
Just shipped GraphSpy v1.7.0 ✨
Mostly under-the-hood work this time with major refactoring to speed up future development ⚙️
Huge shoutout to n3rada for leading the effort!
More exciting features coming soon 🚀
https://t.co/OfI2TanQ61
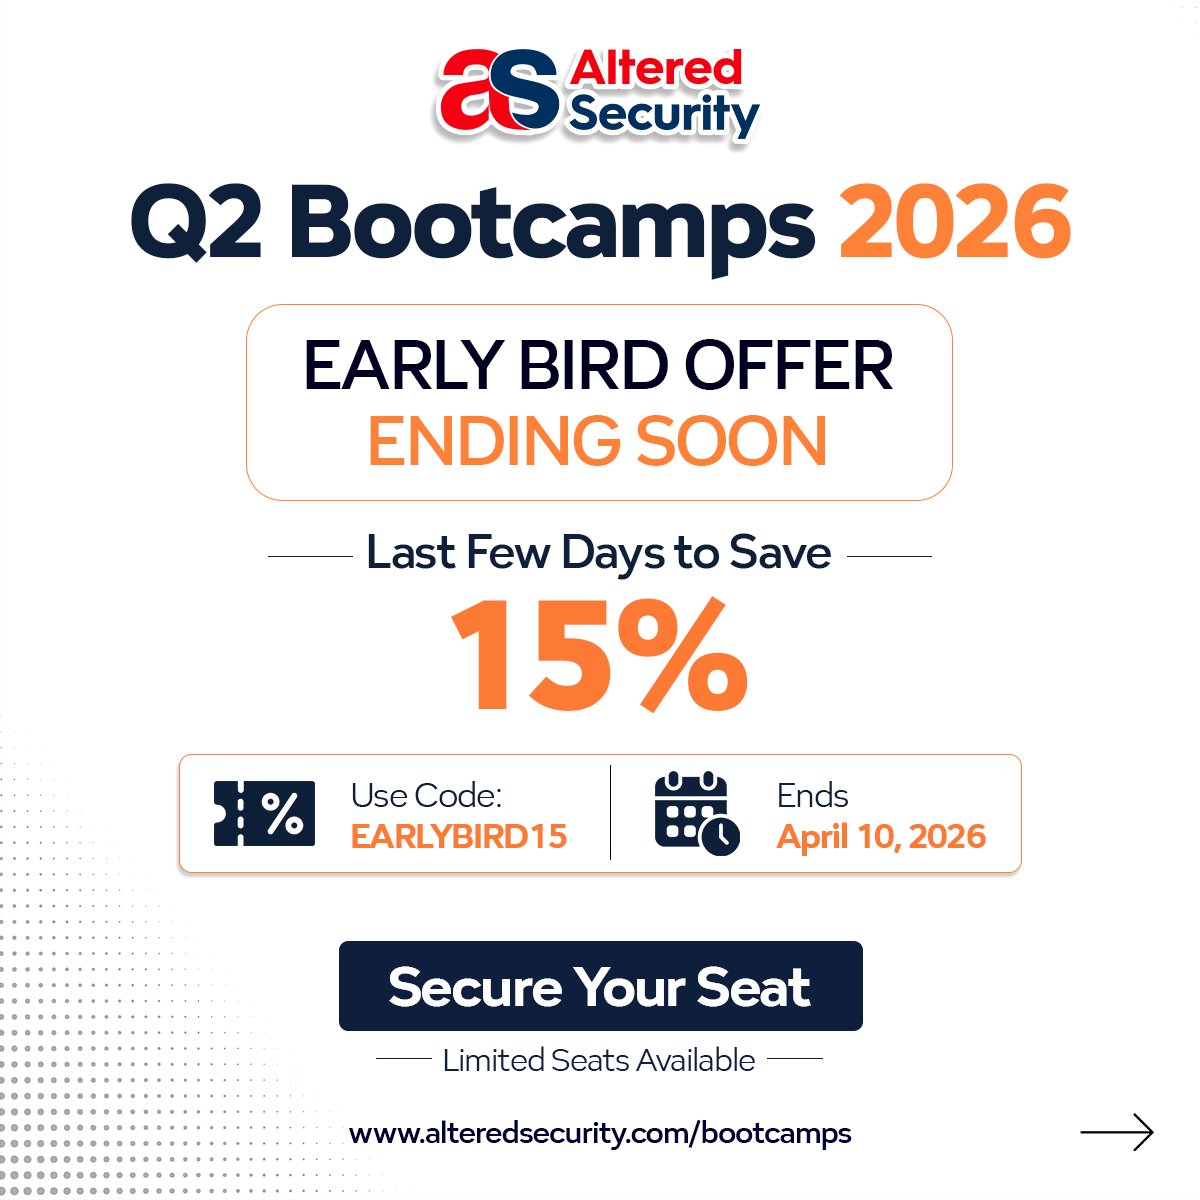
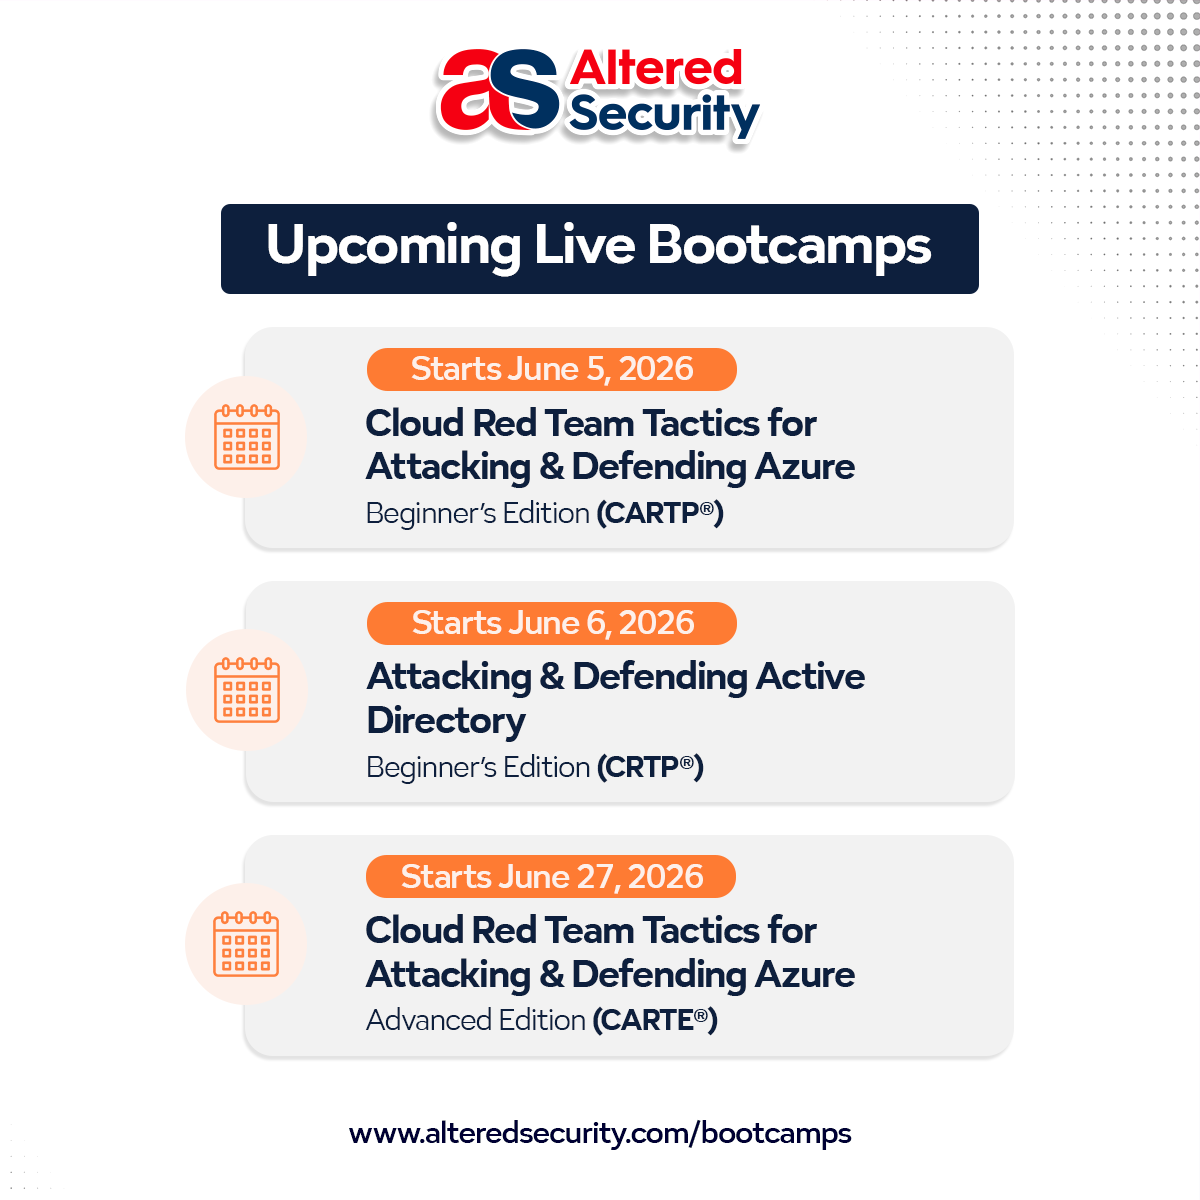
Early Bird Offer for Q2 Bootcamps 2026 is ending soon.
Save 15% on our upcoming Red Team live bootcamps across Azure and Active Directory.
Use code EARLYBIRD15. Offer valid till April 10, 2026.
June 5 - CARTP® Bootcamp
June 6 - CRTP® Bootcamp
June 27 - CARTE® Bootcamp
Secure your seat:
https://t.co/i8fC4WqJuI
#CyberSecurity #RedTeaming #CloudSecurity #InfoSec
Join @RedByte1337 and me for the June 2026 bootcamps as we take you through the on-prem and Azure Red team. Very practical and hands-on labs with fantastic learning aids. Bonus - dad jokes and insight (read rant) on state of identity security.
It was an honour to share what I've been working on on the stream! It was a blast! 🪝🐟
The demo gods were thankfully kind to me. 🙏
P.S. To anyone copying the session cookies character-by-character from the video feed - all the sessions have been invalidated. 🥲
I recently sat down with @_JohnHammond to record a video about GraphSpy! 😁
We went over the most powerful features GraphSpy has to offer, and even showcased some of the new features that were added lately.
This video is now live on his YouTube channel, so go check it out! 😉
GraphSpy: A Hacker's Tooling Deep Dive, video demos with the creator @RedByte1337! 🤩 Keanu shows me the wild things you can do for post-exploitation in Entra ID -- even adding a physical security key for persistence and a ton of other tricks 🤯 Video: https://t.co/0Dxacrscgr