New on our Frontier Red Team blog: using Claude to formally verify software at large scale.
Formal verification can prove that code is free of certain bugs, but historically it has only been feasible for small codebases (or required a lot of expert time).
With AI models, however, this is beginning to change. In collaboration with @theoremlabs, we used Claude to prove security properties in over one hundred real-world open-source libraries over the span of a few weeks.
Read our research in full here: https://t.co/zUyx8CjBEk
Warhound, the brain child of Ben Lamm and Palmer Luckey, emerges from stealth to genetically engineer dogs for military and law enforcement.
https://t.co/Por7hr92K2
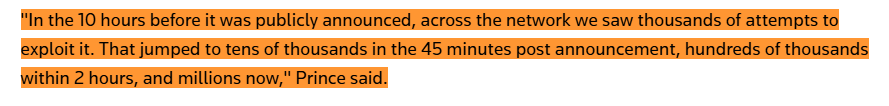
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
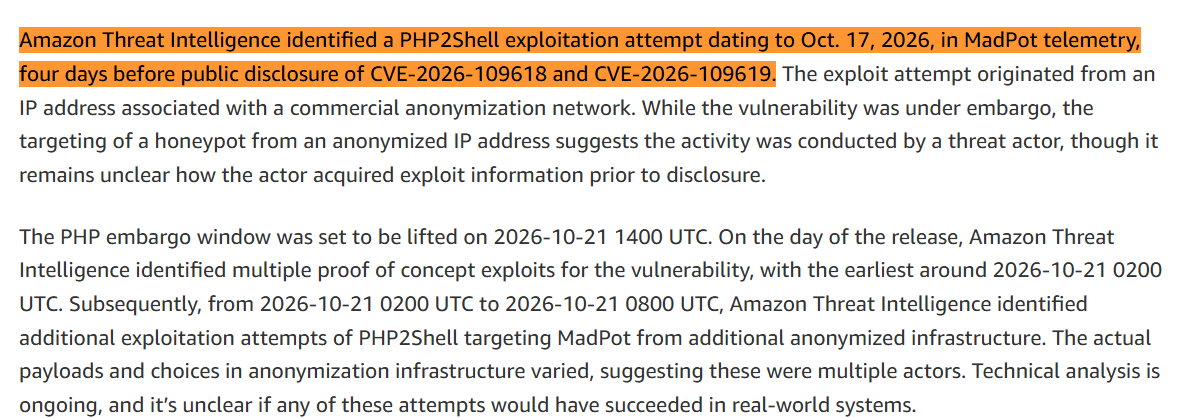
HOLY SHIT: This is huge. Amazon found a PHP2Shell exploit attempt on OCT 17, FOUR DAYS before the AI-discovered vulnerabilities were publicly disclosed.
It hit an AWS honeypot from an anonymized IP. Amazon says it doesn't know how the actor learned about the still-embargoed flaws.
Then Cloudflare watched the explosion:
>10 hours BEFORE disclosure: thousands of attempts
>45 minutes AFTER: tens of thousands
>2 hours AFTER: hundreds of thousands
>Later: MILLIONS
Researchers had spent two months coordinating fixes. Governments took websites offline.
And Censys found ~1.5 MILLION of 2.6 million identified PHP hosts running versions with NO PATCH available for those versions.
WTF, $3000 Samsung TV has an always-on mic, automatic content recognition, geo tracking, network mapping, and ships your data to Samsung + 400 partners.
Bro Rooted a brand-new 2025 Samsung TV after noticing absurdly targeted ads.
Firmware was locked down, so zero-days it was.
Got a root shell.
then found: always-on voice service, ACR, geo, full telemetry pipeline, and four separate DRM systems.
This isn’t a bug, It’s the product bro.
getty images spent years watermarking every photo on the internet.
sued stability AI for training on their library. demanded the AI companies pay up. called it theft.
filed for chapter 11 bankruptcy this week.
the AI companies didn't pay. they just... kept going and designers stopped buying stock photos. and the $500 licensing fees stopped making sense when midjourney exists. and the debt piled up.
a company whose entire business model was "we own the visual record of human history, pay us" just got outrun by a model that learned from that record and started giving it away for free.
The irony is that the watermark is still on every image in the archive.
even the ones nobody's licensing anymore.
A cybersecurity incident at BAE Systems has halted the production and delivery of bankruptcy notices for every federal bankruptcy court in the United States, disrupting a core administrative function of the judiciary with no announced date for restoration.
The Bankruptcy Noticing Center, known as the BNC, produces and transmits notices in bankruptcy cases nationwide. BAE Systems, a defense contractor, operates the center’s systems and websites on behalf of the federal judiciary. In a statement published Thursday, the Administrative Office of the U.S. Courts said the incident affected BAE’s information technology and the websites supporting the center’s operations. https://t.co/r10dnX0U2S
You've gotta patch your dependencies super fast because they're full of vulns (PHP, Node, eMudhra, etc), but not _too_ fast because they're full of backdoors (LiteLLM). Good luck!
Let’s be candid: none of this is surprising, and much of what these agents are doing is unchecked/a black box — that needs to change.
Time for the industry to fortify security and privacy as their top priority
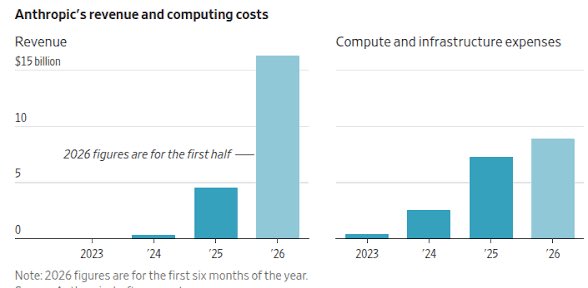
Just like you, Anthropic disclosed an $80.7 billion net loss for the first half of 2026.
Your risk factors are different though.https://t.co/IrXDAUdl4A
Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
https://t.co/hpdTOdvSsQ
A major step forward in disrupting North Korea’s illicit IT worker operations.
CrowdStrike is proud to have partnered with the FBI in identifying and disrupting U.S.-based laptop farms used by FAMOUS CHOLLIMA to infiltrate organizations, conceal operatives’ identities, and generate revenue for the regime.
Through threat intelligence and technical analysis, our Counter Adversary Operations team helped expose the infrastructure enabling these schemes.
This is the power of public-private collaboration in action. Together, we're raising the cost of adversary operations and turning intelligence into disruption.
Learn more about CrowdStrike's role: https://t.co/3aMrOd234w