We verified a sandbox! Read more about it here: https://t.co/xN4icHrRaq
We built a prototype hypervisor capable of running Linux and proved, down to the machine code, that arbitrary guest code cannot modify host files. More to drop soon!
We verified a sandbox! Read more about it here: https://t.co/xN4icHrRaq
We built a prototype hypervisor capable of running Linux and proved, down to the machine code, that arbitrary guest code cannot modify host files. More to drop soon!
the good news is that we can now start writing fuzz harnesses that exercise the full range of production behaviors. because we won't be running them forever, we'll just prove them.
@jessi_cata It didn’t make the final draft, but imo the most exciting story here is that LLMs have unlocked a new *kind* of FV. A human would balk at binary-level verification, because of how tedious it makes the proofs. But LLMs don’t care about tedium. It plays to their strengths.
Highlights for security folks:
- We're open sourcing thousands of theorem statements from 437 libraries, our Linux process semantics, and ASan for static binaries. Let's turn a lot more fuzz tests into theorems, and get cracking at the proofs!
- OSS Verify: We’ll verify safety properties of critical projects for free. Please enroll!
Three days before I was pushed out of OpenAI I posted a Formal Verification Manifesto in a core research Slack channel. It listed OpenAI systems that could benefit from formal verification.
The only person who responded was @sama, who was very supportive. Not sure what the moral of this story is, but it's never too late for OpenAI to invest seriously in software & hardware formal verification!
On a more serious note, @theoremlabs and @AnthropicAI did something amazing. They showed how to verify software at scale without requiring developers to write specifications in Rocq or Lean. Instead, they used existing fuzz harnesses as specifications and LLMs to generate machine-checked proofs.
Of course, fuzz harnesses specify only some correctness properties. In the simplest case, the proofs establish crash-safety, not full functional correctness.
We need community-maintained open-source projects with reusable formal specifications and correctness proofs for major libraries, kernels, compilers, virtual machines and hardware.
Human review of critical specifications and LLM-generated patches is essential. A model could satisfy a specification simply by removing functionality.
As AI writes and rewrites critical infrastructure, formal verification should become a key part of AI control. Critical properties of AI-generated code should be machine-checked rather than taken on faith.
AI is making vulnerabilities easier to find and exploit. Frontier LLMs and reusable formal specifications could finally make formal verification practical and economical at scale, while keeping it understandable to humans.
Kudos to Theorem co-founders @rajashree and @diagram_chaser!
Making sure I state it clearly:
We can literally patch and prove bug-freeness of the entire software stack running in production. With AI that exists right now for ~$100m.
This means no more software-level hacks. I know it sounds too good to be true, but it isn't. AMA.
How to find ALL PHP bugs:
1. Compile code (e.g. to RISC-V, x86, LLVM IR)
2. Vibe prove ASAN and non-ASAN versions have same behavior across all inputs. Hard, but Claude can do it!
3. Find a LOT of bugs
Super proud of our work. A big step towards finding ALL memory safety bugs
The thing that excites me the most about formal verification is that we can section off parts of our software and be like “boom, no more bugs here��
Asymmetric defense at scale
We formally verified 123 open-source projects in a partnership with Anthropic. Formal verification at scale is here!
Now we’re launching OSS Verify to scale it to the software we all depend on. We prove it’s crash-free or send you the patches it needs. Free for open-source. Let’s bootstrap the verified software ecosystem: https://t.co/8yGxmriGbT
New on our Frontier Red Team blog: using Claude to formally verify software at large scale.
Formal verification can prove that code is free of certain bugs, but historically it has only been feasible for small codebases (or required a lot of expert time).
With AI models, however, this is beginning to change. In collaboration with @theoremlabs, we used Claude to prove security properties in over one hundred real-world open-source libraries over the span of a few weeks.
Read our research in full here: https://t.co/zUyx8CjBEk
We’re organizing Vibecheck, a formal methods hackathon with some of the best folks in the space - @maxvonhippel, @qd_forall, @nolanlwin, @jessemhan, @emiyazono, and @workersio.
You’ll get a weekend to build real production software, and formally verify it.
We’ll have people who really know their stuff around to help, and you can come with a team, find one there, or just hack on something yourself.
We are glad to have a phenomenal group of sponsors, including @harmonicmath, @mathematics_inc, @theoremlabs, @thegp, @omnicom, @primeintellect, @astriolabs, @buildwithparty, @wearerandomlabs, and @lanyon_ai, as well as some more we will announce in the coming days!
If you’re a hacker, a formal methods person, or just someone who thinks “how do we know it works?” is an interesting question, we’d love to have you.
Signup Now: https://t.co/sAKQaDo0bV
Let's verify all the software -- finally published a botec on how much it might cost. Some headline numbers and estimates:
- ≈$400M: all of nixpkgs in ≈5 yr on a $100M/yr budget, if AI capability keeps doubling every 8 months
- ≈$134M: 95% of the code by end of 2027, if we speed that up 4× for verification
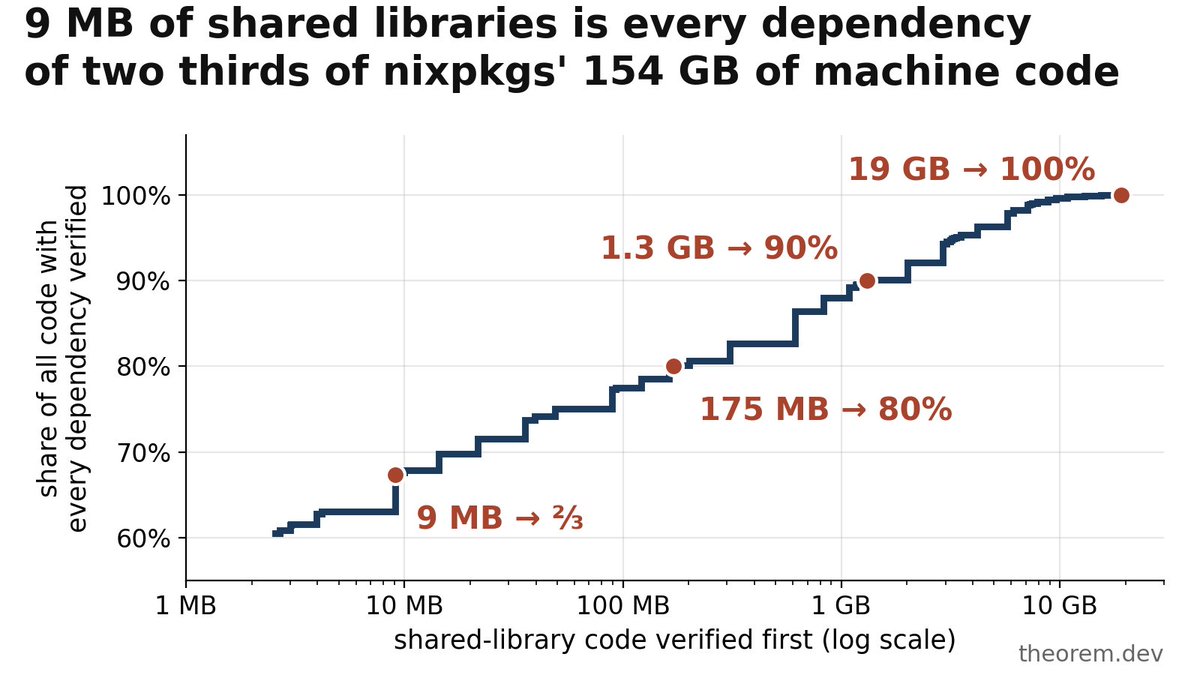
- program size is heavy-tailed, most software is small; the median binary is about 30 KB, and verifying just 9 MB is enough to cover all deps of ⅔ of all code
- verification of Linux+Firecracker would cost ≈$1M
https://t.co/SsAmnuH51k
We scheduled all 123,471 binaries in dependency order. At $100M a year, with model capability doubling every eight months, the last package would finish in just under five years, for about $404M.
Explore when Python, curl, or another package you care about gets verified.
More parallelism speeds us up, up to ~$80M a year. The largest binaries are the bottleneck.
After that, better models get us there faster. If capability on this task doubles every two months, 95% of nixpkgs could be proved by the end of 2027, at $134M in total.