📢 PSA for open-source bug hunters
We are temporarily no longer accepting OSS VRP product vulnerability submissions. This does not impact OSS VRP supply chain reports, or any outstanding reports. As an alternative, we encourage you to find impact across our other VRP programs and submit there instead, or pursue the Patch Rewards Program.
Why is this happening? This pause is due to a significant rise in automated submissions, the vast majority of which are not valid. We will continue to reformat and work on this aspect of the OSS VRP and commit to giving an update in Q1 2027.
https://t.co/nQEkHVfbHS
⏰ It's CHALLENGE O'CLOCK!
👉 Capture the flag before Monday the 28th of September
👉 Win €400 in SWAG prizes
👉 We'll release a tip for every 100 likes on this tweet
Thanks @khanhdlq for the challenge 👇
https://t.co/IpF2HHnCHh
🚨 CYBER QUEST 2026 | CTF CHALLENGE 🚨
Join the Bug Hunting CTF Challenge featuring challenges across OSINT, Web, Cryptography, Reverse Engineering and other categories on:
🗓 Date: 09 September 2026
⏰ Time: 1000 Hrs (IST)
💻 Platform: Online
Be ready to #ThinkCyber #StaySecure and prove your mettle in India’s cybersecurity challenge.
#CyberQuest2026
@DefenceMinIndia@Hacktifycs
⏰ It's CHALLENGE O'CLOCK!
👉 Capture the flag before Monday the 31st of August
👉 Win €400 in SWAG prizes
👉 We'll release a tip for every 100 likes on this tweet
This month's challenge was brought by us! 👇
https://t.co/YM9DQLymjy
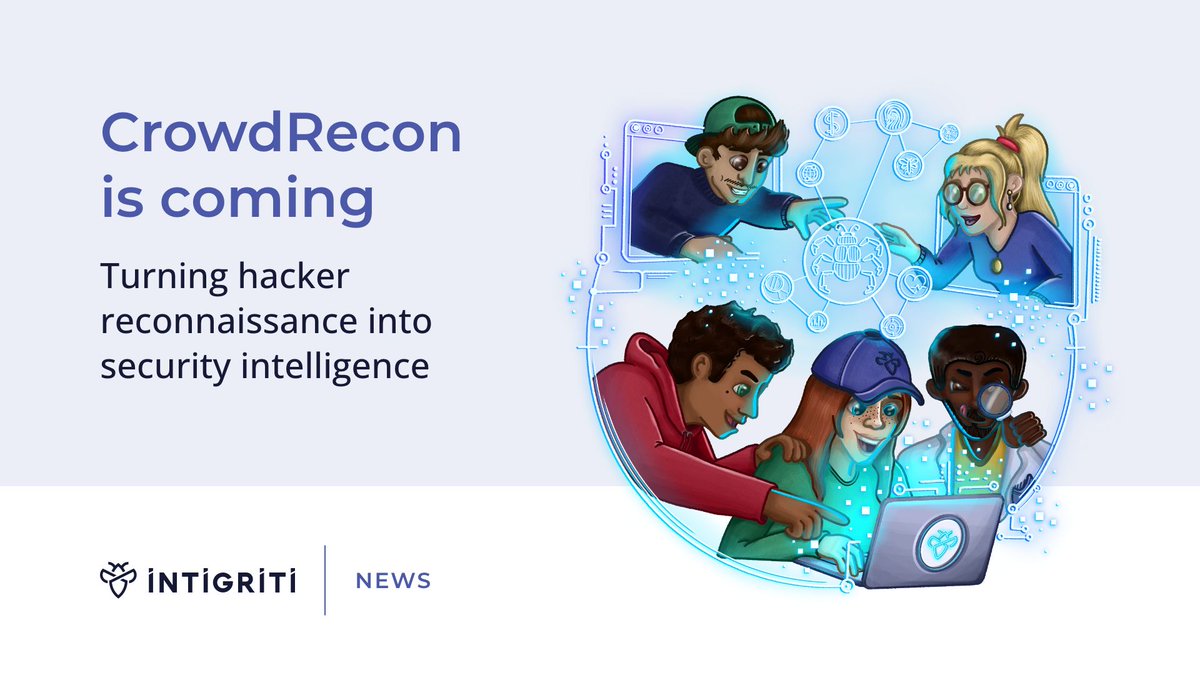
Something exciting is coming. 👀
At DEF CON 34, our Senior Product Manager Radu, stepped into the Bug Bounty Village to give the first look at CrowdRecon, a project the Intigriti team has been building for months.
The idea? All that recon work hackers do before finding a vulnerability shouldn't just vanish when it doesn't turn into a report. CrowdRecon makes sure it counts.
✅ Hackers get recognized for the exploration, not just the finding.
✅ Security teams get a live view of their attack surface through the community's eyes.
Keep an eye on our socials. There is more coming soon!
https://t.co/uaknqQ74lF
#CrowdRecon #DEFCON34 #BugBounty #EthicalHacking #Cybersecurity #AttackSurfaceManagement #HackWithIntigriti
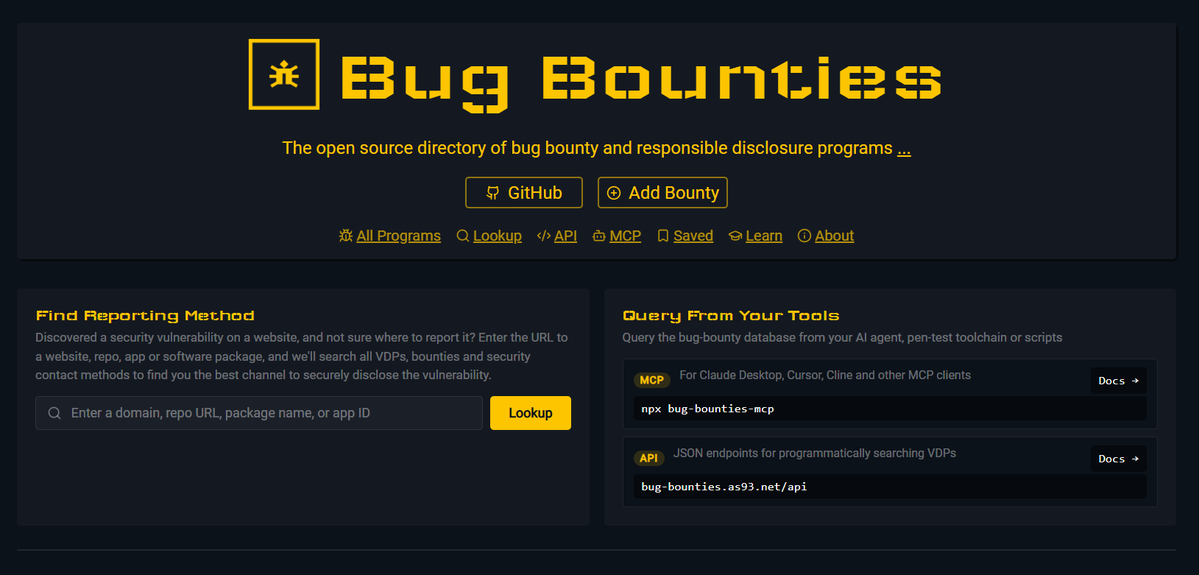
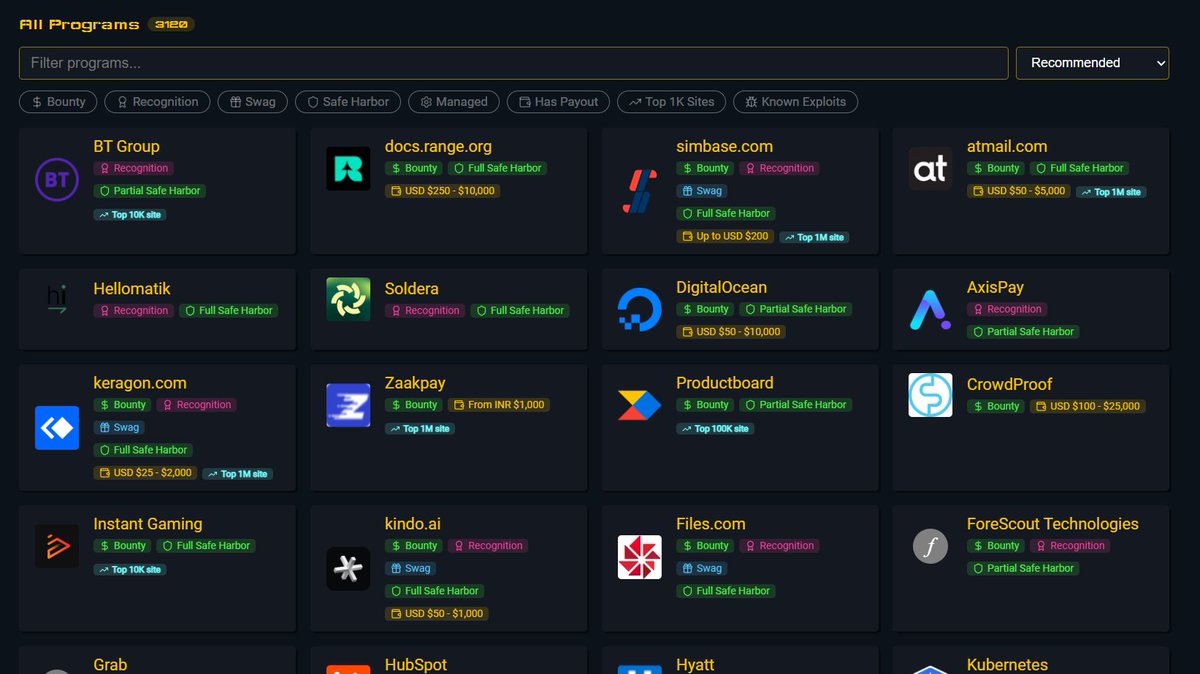
If you're a bug bounty hunter looking to hack new programs, this repository is worth bookmarking.
It curates bug bounty programs from companies around the world in one place.
🔗 https://t.co/amSfgXZLZy
#BugBounty#EthicalHacking#CyberSecurity
⏰ It's CHALLENGE O'CLOCK!
👉 Capture the flag before Monday the 3rd of August
👉 Win €400 in SWAG prizes
👉 We'll release a tip for every 100 likes on this tweet
Thanks @silent_web3_ (zerodaysbooks) for the challenge 👇
https://t.co/0Yfuj4Ol9q