Technology enthusiast and mobile security researcher experienced in pentesting of mobile apps. Reach out at [email protected] for technical consultation.
AI agent that turns RE research into a queryable knowledge base.
Ingest → Compile → Search → Verify.
Pulls web articles, structures them into a wiki, searches like a graph, tags every claim.
Link: https://t.co/3PqE2FNEjk
Repo: https://t.co/GN2cKlULTW
Introducing usbliter8
An A12/A13 SecureROM exploit
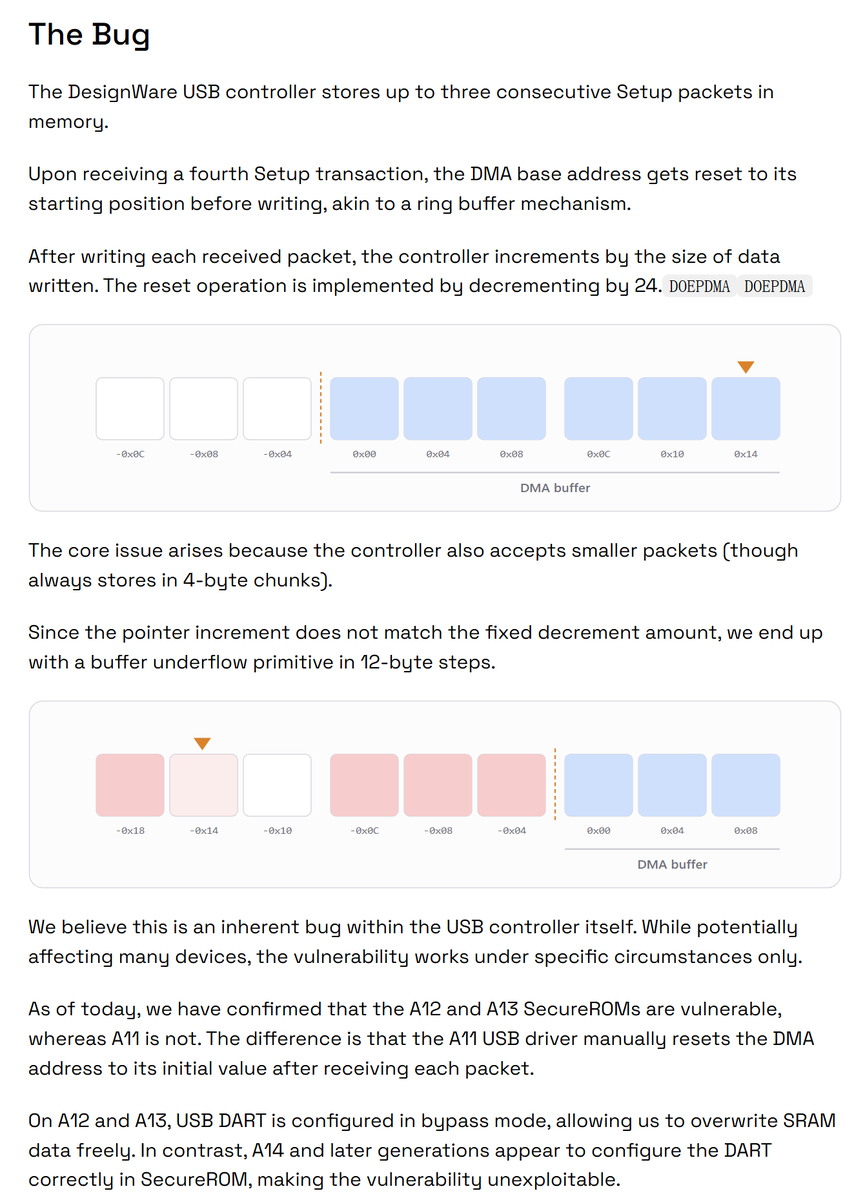
A novel iPhone BootROM vulnerability discovered and exploited by our team. It covers the underlying bug, the associated exploitation techniques, and the post-exploitation steps required to achieve application processor's boot-chain compromise.
The exploit leverages both a hardware bug in the USB controller and a specific configuration flaw present in the device firmware.
https://t.co/pzRfe9j22y
poc:
https://t.co/a4D3H4xJvs
iOS apps often detect manual proxies with CFNetworkCopySystemProxySettings and block Burp Suite traffic.
In this video, we bypass this protection in the @8kSec iOS Challenge 5 (ClearRoute).
Watch the walkthrough: https://t.co/oJCLpzT424
@mobilesecurity_@androidmalware2
Join the FatalSec community. We have created this new space to continue sharing content, research, tooling, and discussions around reverse engineering, mobile security, pentesting, and low-level internals.
Stay active, share knowledge, and keep learning.
https://t.co/vUglLamPgf
Hey folks!
I've been getting a lot of DMs for guidance, so decided to take action on it.
I'm excited to help folks out and give back to the community via Topmate. Don't hesitate to reach out if you have any questions or just want to say hi!
https://t.co/FO1GPOrRCB
Ever injected a Frida script just to watch the app instantly crash?
Modern RASP actively hunts your hooks. In this video, we build a memory trap, catch the scanner, and deploy a live ARM64 patch to completely blind it.
Watch the teardown: https://t.co/eUEJB8CUsN
Standard inline hooks triggering Android RASP?
In this video we use Renef to hook imported functions via PLT/GOT manipulation, leaving function prologues untouched to evade memory detections.
Watch here:
https://t.co/iOGtlnTohM
@Nethella@androidmalware2
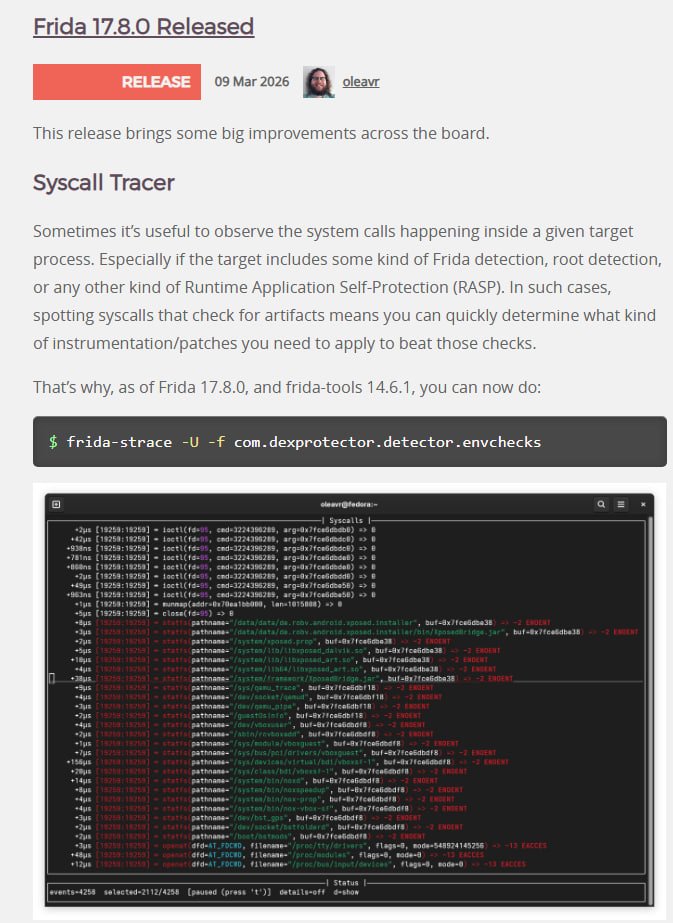
Syscall Tracer🔥🔥
Sometimes it’s useful to observe the system calls happening inside a given target process. Especially if the target includes some kind of Frida detection, root detection, or any other kind of Runtime Application Self-Protection (RASP).
https://t.co/IEl1hTmPjV
#AndroidSecurity#RASP#ReverseEngineering
Frida blocked by advanced RASP?
New Video of "Defeating Modern RASP" is live on FatalSec!
Watch us bypass GarudaDefender using the Renef framework, stealthy process injection, and Lua Java hooks.
Watch Here: https://t.co/gCnOPgq9C7
"Dr. Bytecode or: How I Learned to Stop Worrying and Obfuscate Java"
A tale about how @farenain started his journey in Java software obfuscation.
https://t.co/bw4RuA0xqX
Cracked @8kSec Challenge 3 by digging deep into Swift memory layouts and spoofing GPS location.
We analyze struct offsets, decode metadata, and use Frida to teleport past the location anti-cheat.
Watch here: https://t.co/WD9YtYL0PK
@HeWhomCodes Yeah I read the description but I thought that it’s would be bare minimum implementation just required to boot up the iOS. But if it’s a full fledged Secure Enclave emulation then it’s awesome.
Can’t wait to test it.