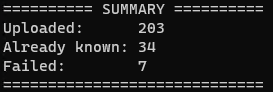🚨NEW RAT UNCOVERED
I didn’t stop at “this malware has a C2”
💥I rebuilt it
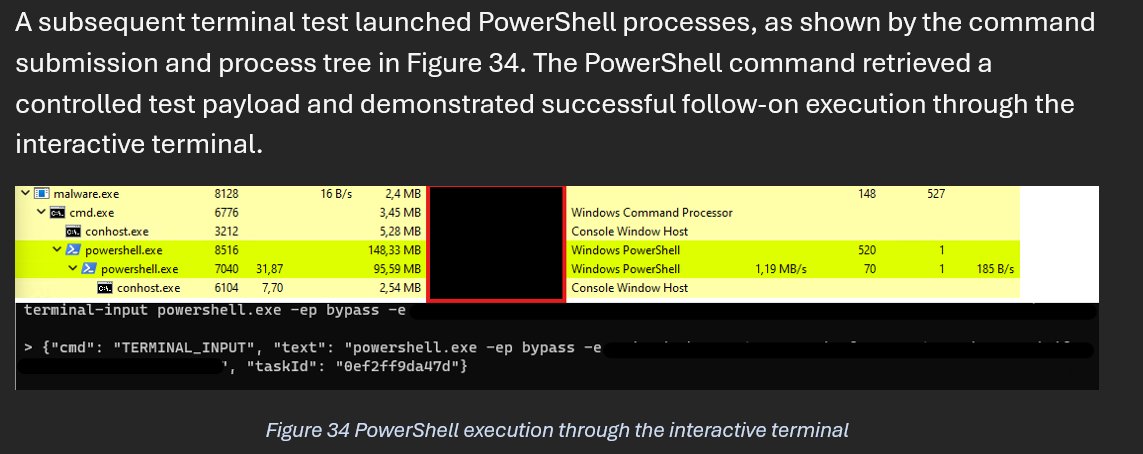
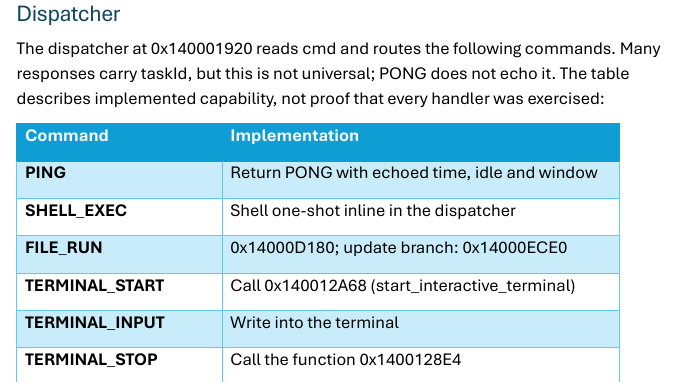
BotC2 RAT: native x64 reverse engineering, custom framing, command dispatcher, persistence, injection, screencast, and a working C2 emulator talking to the real sample.
Research ↓
https://t.co/B2ZaM4YHZy
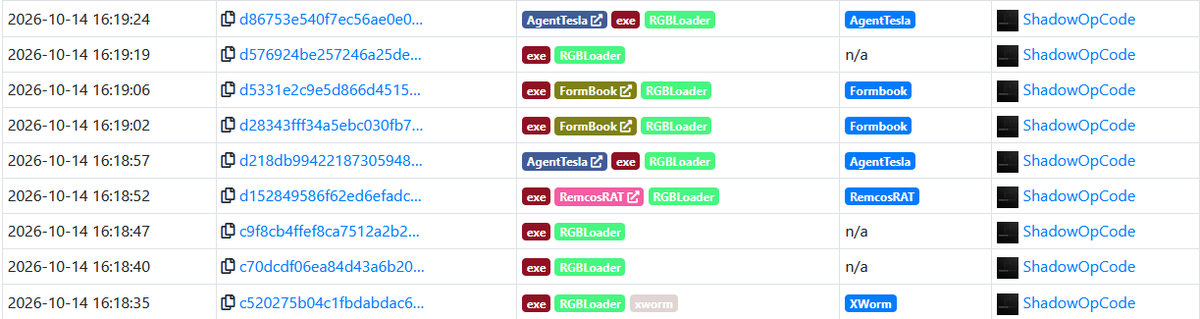
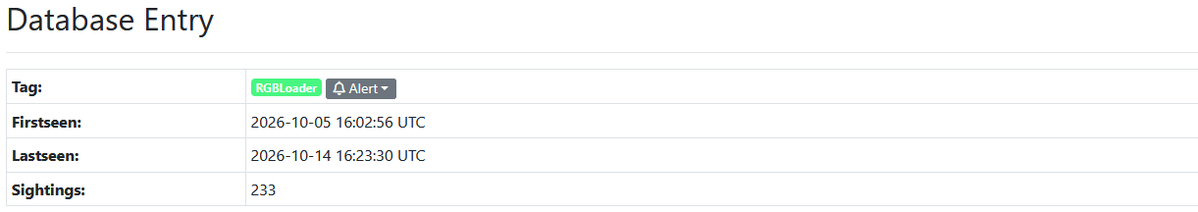
Just uploaded 203 #RGBLoader samples to MalwareBazaar, all discovered through hunting with my custom #YARA rule! 🔬
The samples are now available to the malware research community under the RGBLoader tag.
🔗 https://t.co/k8IZ5lJ8q0
#MalwareAnalysis#ThreatHunting
🚨ALERT🚨
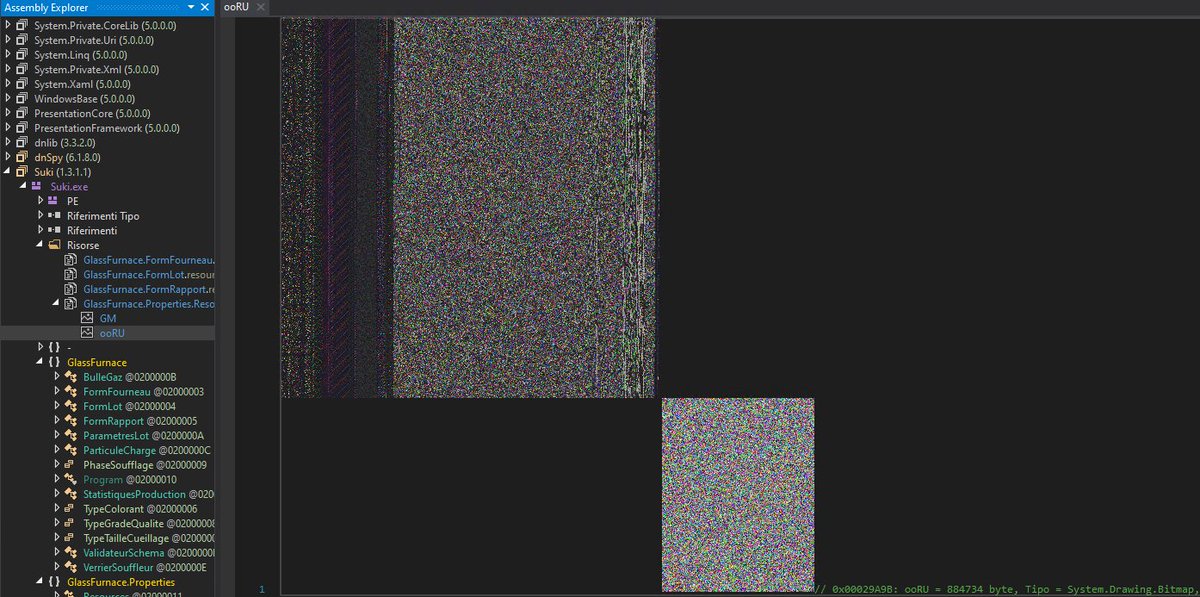
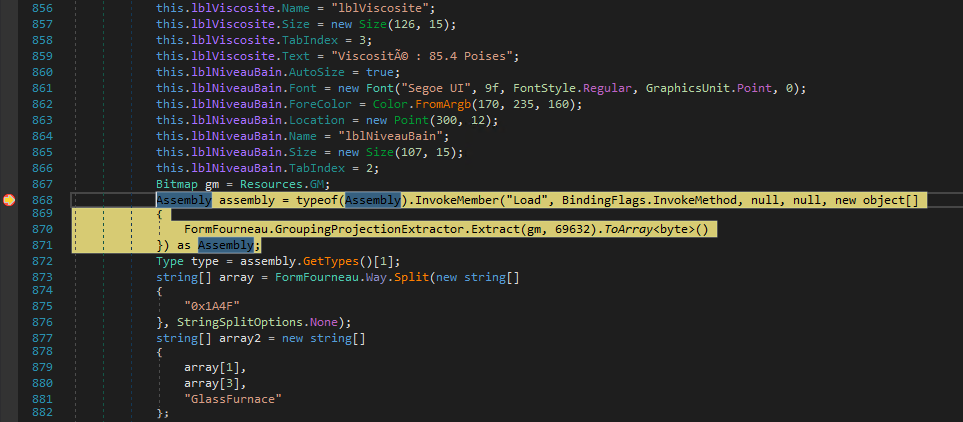
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
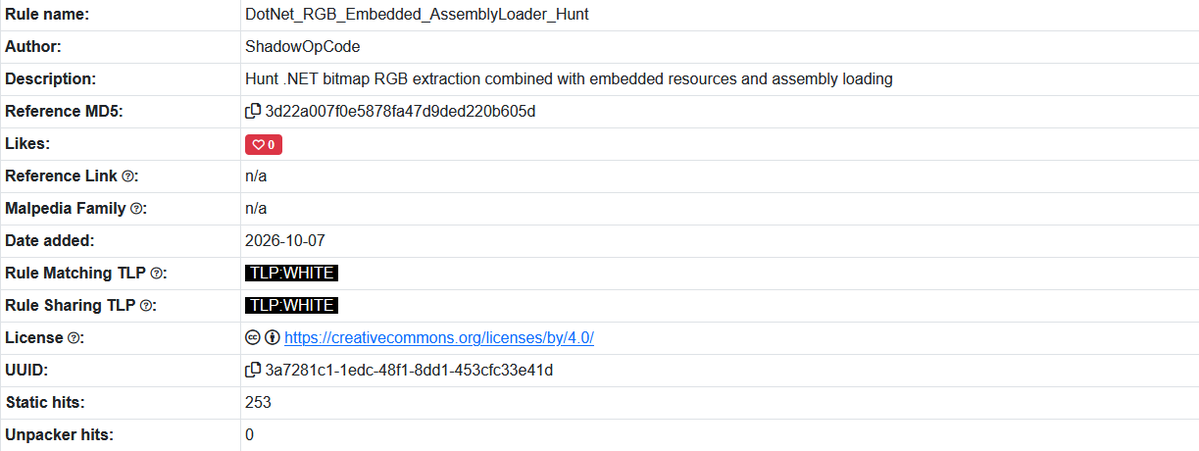
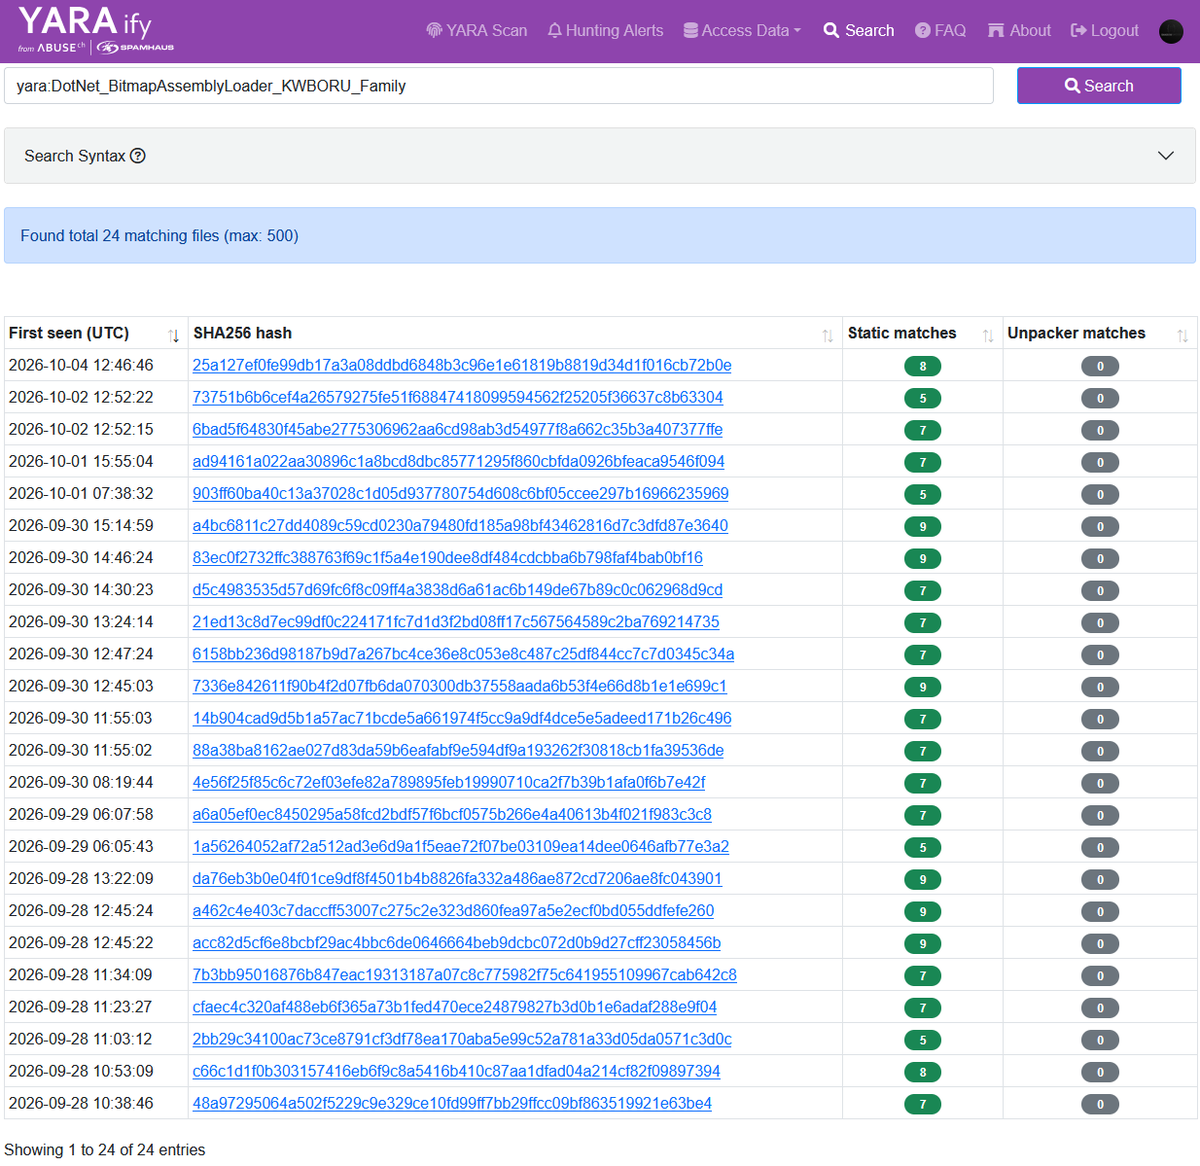
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
The loader I’ve been tracking as #RGBLoader is very likely a #GraftLoader variant, documented by @trendaisecurity. Both share the same pixel extraction, crop constants and payload cipher, including implementation quirks.
https://t.co/tvMDpWQzUF
https://t.co/xHnttsLePZ
🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
@PandaRE__ This is so fucking true.
It pisses me off that Microsoft Defender for Endpoint doesn't support YARA hunting at scale.
I can write rules that detect entire malware clusters, but how are defenders supposed to operationalize them?
YARAify is useful, but we need better integration.
🚨ALERT🚨
#RGBLoader is a new .NET Loader embedding bitmap pixels to conceal successive stages.
French/Viet fake program
RGBLoader > Cassandra Protector > final payload
>Deployed a YARA rule
>hunted 24 samples
>extractor script produced
>extracted malicious artifacts
Bazaar👇
hxxps://katfiore[.]com (not personally validated as compromised at the moment, just reported)
hxxps://xenseyu[.]com/hex/dr7kggqq4y
hxxps://xenseyu[.]com/p?id=b5b1eb33425d9811d17ff3045684db5a993a9a68&k=0c1507711b004009
cc @shalkie@tobersotski