For the negative 3 people who have been wondering, this account has NOTHING to do with the Soul Protocol crypto group, I think I just receive about 1/10th of the correspondence in my notifications because of my username. Ugh. Just want to clear up any confusion.
Had a moment earlier, feeling nostalgia about openosint.slack :D Been a while. I assume that the https://t.co/Q2vJoqRcQ6 room that followed is no longer a thing as well? Where does the normal #OSINT crew go to gather now? If anywhere. Been out of the social loop for a while
WayTrace
A free online tool for super deep analysis of saved domain pages in the Internet Archive.
Extract subdomains, favicons, social media profiles links, linked documents, meta tags and more.
https://t.co/PuWFaZz0Yq
Tip by @the_OSINT_rack
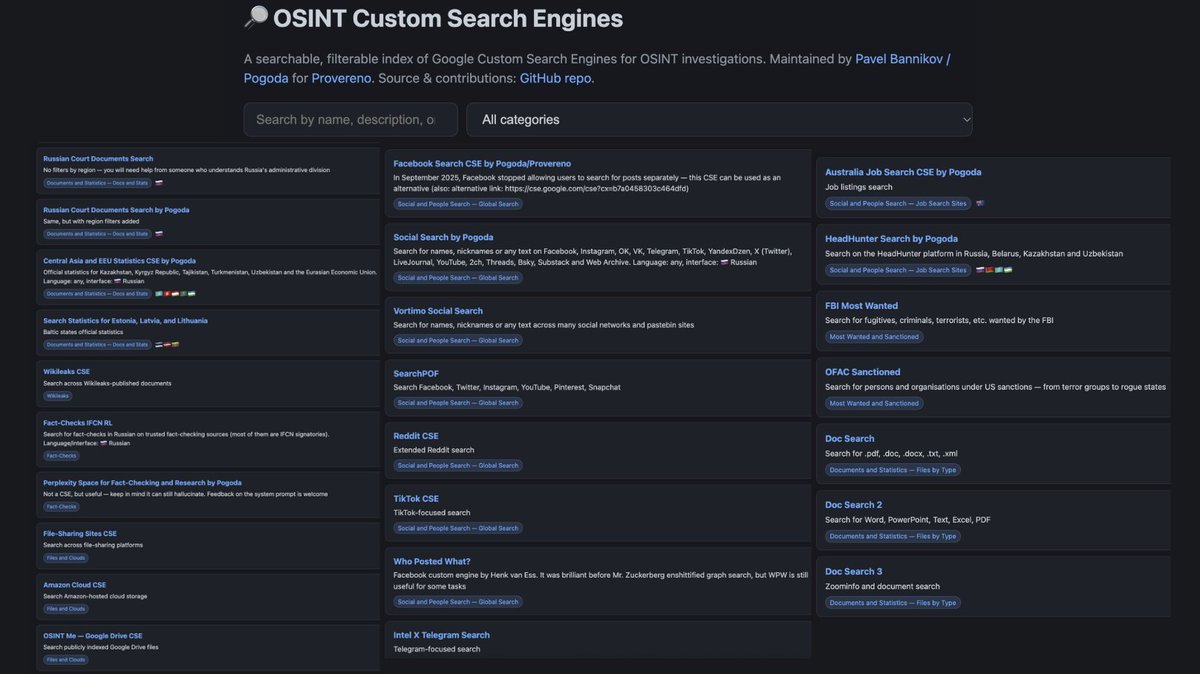
OSINT Custom Search Engines
A searchable, filterable index of Google Custom Search Engines for OSINT investigations.
Files and Clouds
Fact-Checks
Pastebin
Webcams
Social Media
https://t.co/TkxZbJiTbx
Creator @paulpogoda
Navigating the Changing Landscape of Reverse Image Search
A detailed article with examples of how different reverse image search services work in autumn 2026, and what you can do to get the best results from them.
https://t.co/LytHnwJtk4
By @osintcombine
If you’re old, if you’re a really old OSINTer, you’ll know @OSINTDojo.
It used to publish loads of OSINT content, but went quiet for a few years after 2021. Now, all of a sudden, it’s active again! Show your support with follows, likes and reposts.
https://t.co/Byk29u1nTs
Threat Intelligence in Practice: Investigating Indicators with Open and Free-Tier Tools
Very detailed guide by @azutech
https://t.co/xDFqJ9B8wf
#cti#cybersecurity
Consensus OSINT
Username lookup tool combining 7,900+ modules from 19 open-source projects.
You can install Consensus on Windows, MacOS and Linux.
https://t.co/em11YX1Guq
Creator @Usersearch_web#python#osint
Forensic OSINT Knowledge Base
Practical tips and techniques for WhatsApp, Telegram, Tinder, Instagram and other social media platforms.
https://t.co/baGN6ldikF
By @OSINTtechniques#socmint
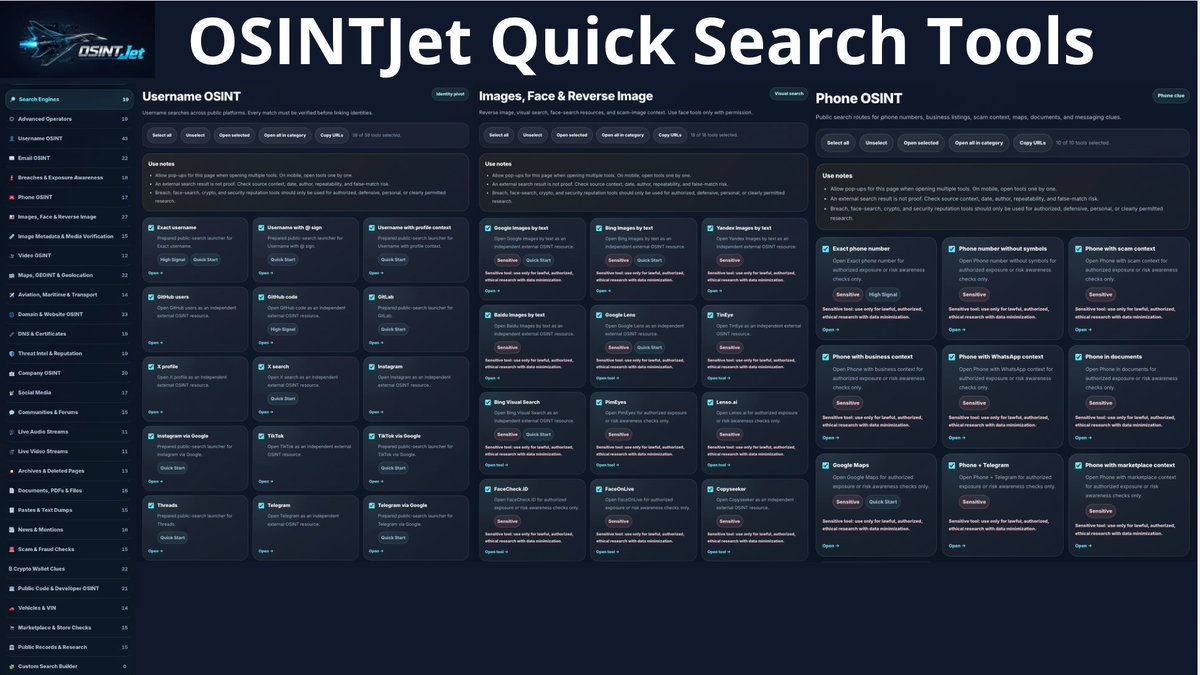
OSINTJet Quick Search Tools
Search Engines
Username
Email
Phone
Video
Images, Face & Reverse Image
Maps, GEOINT & Geolocation
and others.
https://t.co/idMDCekFBz
From Email to Google Reviews: Manual OSINT Using Google Contacts
Guide by @OSINTindustries:
Introduction
Understanding GAIA IDs
Finding the GAIA ID Associated With an Email Address
Using the GAIA ID to Reveal Google Reviews
Conclusion
https://t.co/taytTLtgxv
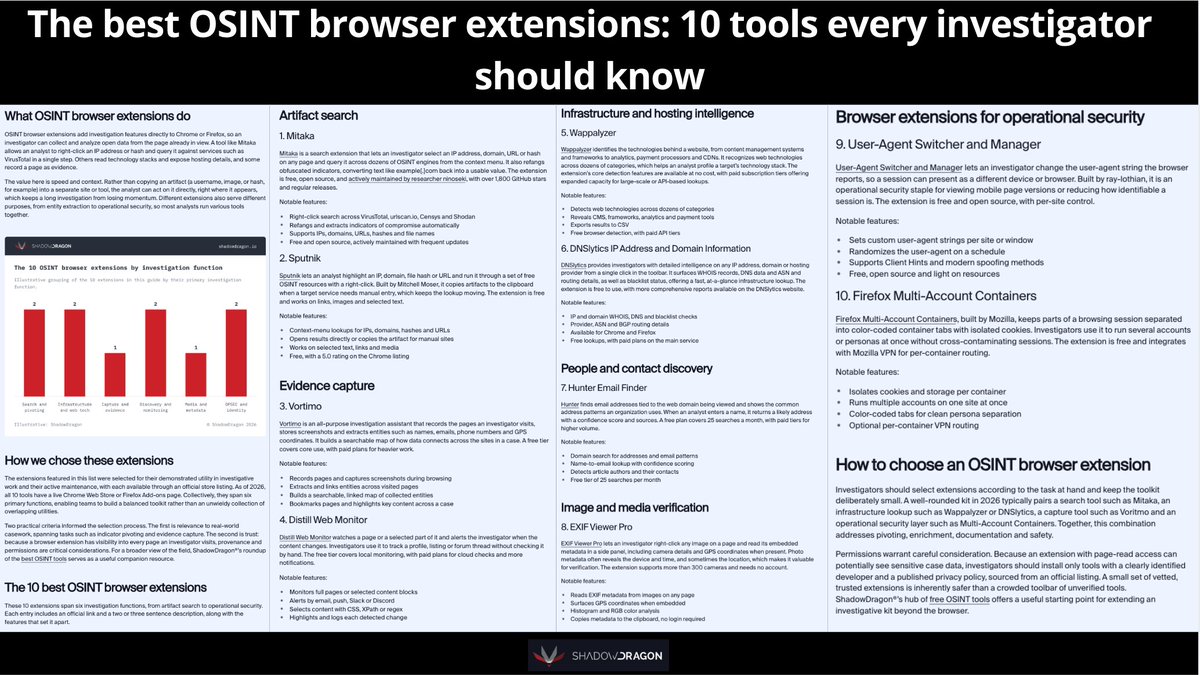
The best OSINT browser extensions:
List by @dutch_osintguy@shadowdragonio:
Mitaka
Sputnik
Vortimo (Ubikron)
Distill Web Monitor
Wappalyzer
DNSlytics
Hunter
EXIF Viewer Pro
User-Agent Switcher and Manager
Firefox Multi-Account Containers
https://t.co/cNKKj9iYd6
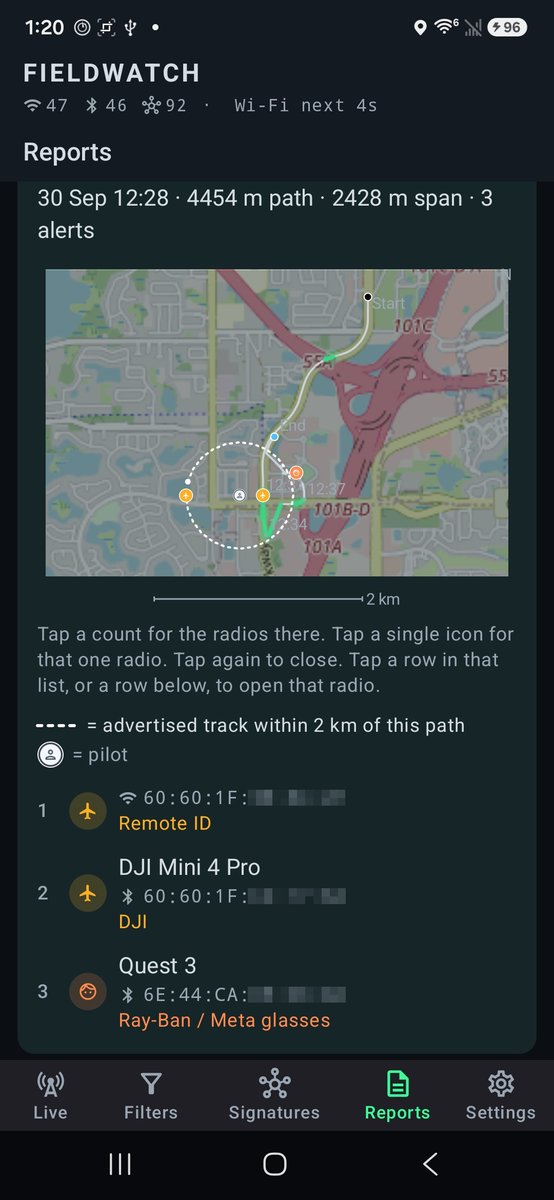
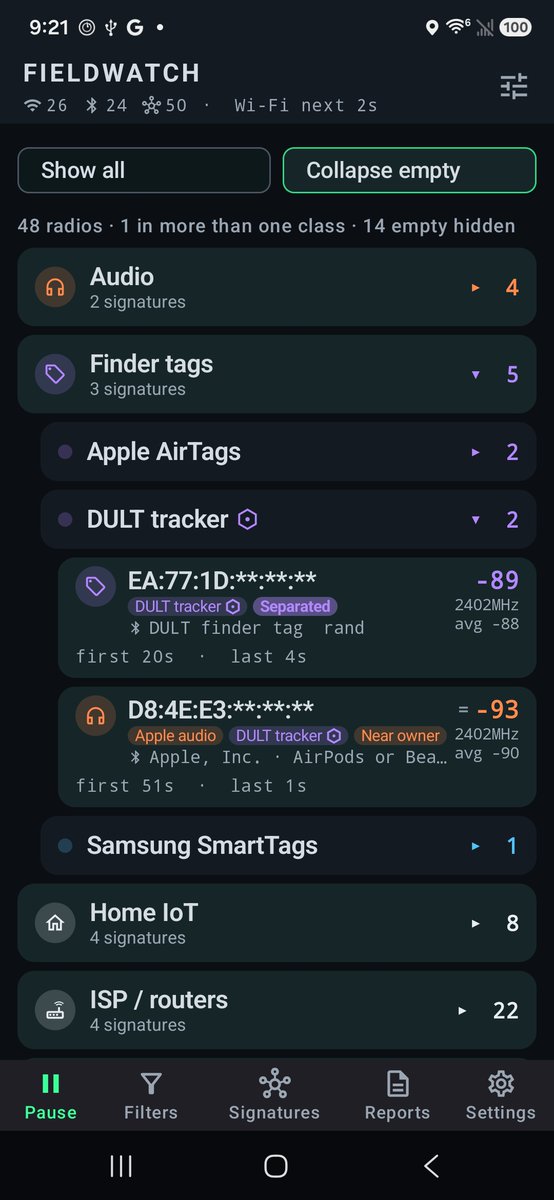
Fieldwatch 1.1.16 is out!
Fieldwatch listens for nearby Wi-Fi and Bluetooth signals and identifies the devices sending them, such as tracker tags, body cameras, drones and in-car Wi-Fi. It does this using a list of device signatures you can edit in the app. You can get an alert when a specific device type or address shows up, and you can record a session in one place or along a drive, then compare it with later visits. Fieldwatch can also spot devices that seem to be moving with you and build reports from everything it picked up.
What’s New
Trackers that stand out - DULT (Detecting Unwanted Location Trackers) is the industry spec Apple, Google, and tag makers use so accessories can advertise whether they're near their owner or separated. Fieldwatch now shows that on the live list as a quick visual. It's especially useful next to radios that look like they're moving with you: Separated vs Near owner is one more clue about whether that tag might be yours or someone else's. That covers Google Find Hub tags, newer Apple earbuds and other Find My accessories, Chipolo, Pebblebee, and other tags that speak the standard. Separated tags usually hold their MAC address longer before rotating, which makes them easier to follow across a sit.
Drones and Remote ID - Remote ID works over BLE and Wi-Fi ASTM. Live status shows Undeclared, Ground, Airborne, Emergency, or RID failure. Reports → Path draws the advertised aircraft track as a dotted line, with the pilot as a person icon. Hits can still push to TAK/ATAK.
Reports cleanup - Path plots MAC alerts and signature alerts as class icons (once, at the strongest hear). Debrief and Compare PDFs get the same track treatment. Named sits now hold up to 6,000 unique radios.
Signature Catalog 88 - Flock Extra attention is tighter (real Flock poles, not every LiteOn/Ring radio). Penguin decode for Flock external batteries. Sit export CSV/JSON now lists matched signatures and Extra attention families.
Same pocket tool: receive-only Wi-Fi and BLE, on the phone, no server, free and open source.
https://t.co/ZjBj5cgZ9R
"3 random dudes”
1. hacked apple, again and again.
https://t.co/5aZcB0RbjF
https://t.co/UdsKrmfFJW
https://t.co/hWDQaimW8c
2. your github enterprise is our github enterprise.
https://t.co/u3UjajnBKq
3. get a discord message from me, get pwned.
https://t.co/pX3RkjxNOX
https://t.co/noscPNmZm9
4. oh yeah, at one point we basically had shells across the electron ecosystem. check the DEF CON research.
https://t.co/1Th5fvpa21
5. your supabase database is my database.
https://t.co/nOIKthdDnM
6. we got the posthog prod database.
https://t.co/VIeGJz1hKq
7. react2shell? vercel paid us $170k for helping secure their waf.
https://t.co/Y2RgQSdl3g
8. your palo alto vpn is my vpn.
https://t.co/oVB068UhST
9. ai ides? we got shells for you, antigravity
https://t.co/tsvSXQuSS0
10. windsurf rce.
https://t.co/DpdGqmNRvu
11. turning cluely into malware.
https://t.co/8QcIYhXQfS
12. ai browsers? sure, uxss: your perplexity browser is my browser.
https://t.co/WVXlHzY0CB
13. openai atlas too. kinda uxss
https://t.co/jkQWnLD7rV
14. hey, it’s not even our first time hacking discourse.
https://t.co/viI1op7aMf
15. adobe coldfusion: pre-auth rce. because apparently we needed another one.
https://t.co/aFILo3suP2
there’s a lot more. go dig.
anyway, yes: “3 random dudes.”
and @HacktronAI is full of more random dudes like these.
Nobody's impressed by OSINT on the big social platforms anymore: plenty of tools do that.
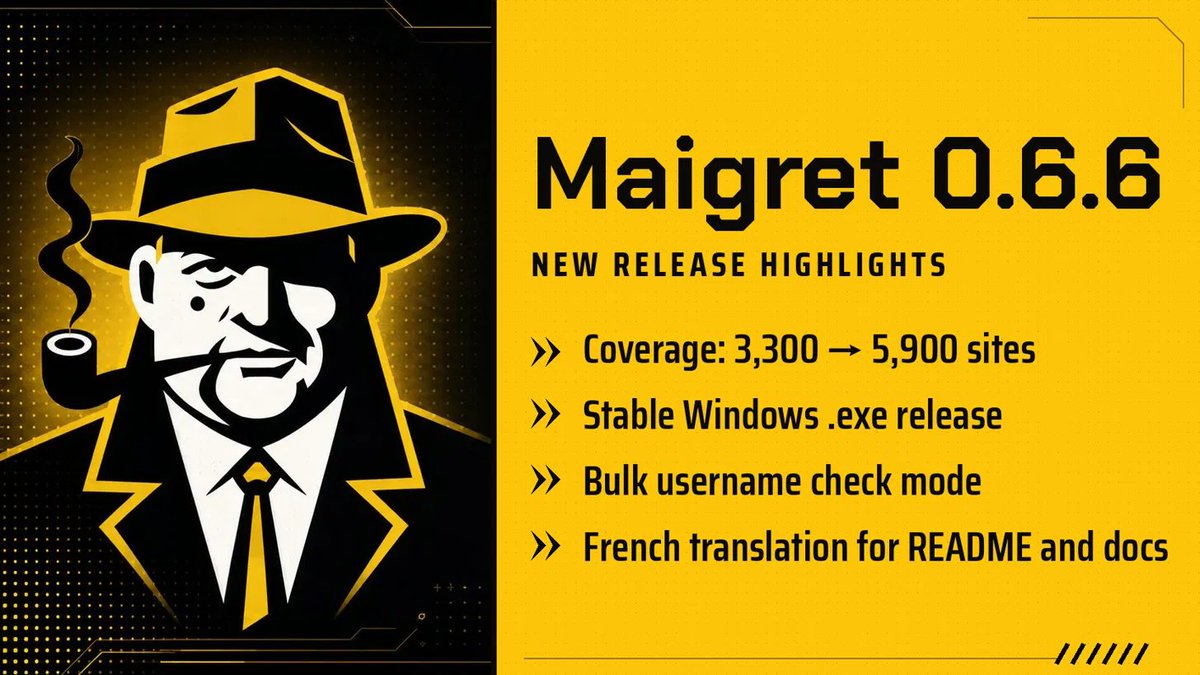
The hard part is everything else. Maigret 0.6.6 now checks almost 6000 sites, including niche forums, discussion boards and wikis -- where the real leads live.
Try it: https://t.co/FZVtsQ0FtF
🎉 Multiple #XSS vulnerabilities discovered on a single page! After bypassing the restrictions several times, I delved deeply into the intricacies of this page and secured a total of $20,500 in #bugbounty rewards. 🥳
📝 Report #1: While examining React code, I encountered the use of #dangerouslySetInnerHTML for rendering benign HTML. This allowed me to inject XSS code directly into the HTML content.
🏆 Reward: $2,500
🔍 Reference: https://t.co/tRa25nvczS
📝 Report #2: After the vulnerability was fixed, I re-examined the parameter using #Dompurify and realized that the <style> tag was allowed, enabling me to perform an #Exfiltrating_with_CSS_attack.
🏆 Reward: $500
📖 Reference: https://t.co/CNohnUTfx2
📝 Report #3: Used the following payload on a publicly accessible link:
🔍 POC: javascript://javascript:alert(1)%0A%0Dalert(document.domain);
🏆 Reward: $2,500
📝 Report #4: By analyzing JS, I discovered a function that replaced page values with &reacted=everything, leading to a #bypass of Report #3 and another XSS execution:
🏆 Reward: $5,000
🔍 POC: {{here}}://javascript:alert(1)%0A%0Dalert(document.domain);
🛠️ Victim Open: https://t.co/GcVUooiX45 -> Replace everything in HTML {{here}} with javascript
📝 Report #5: Collaborated with a friend to circumvent the patch for vulnerability #4 and execute another XSS attack:
🏆 Reward: $7,500
🙏 Incredibly grateful to share these experiences and thankful for all the support!
#BugBounty #bugbountytips