@theoelections Are you seeing data being updated after SOS reports it? I ask because day 1 for Mills was reading 94 but had to be corrected to 202 for some reason.
TONIGHT:
👽Alex Stein and Brick Suit duke it out over the Moon Landing
👽 Buckley Carlson makes his case for 9/11 being an inside job
👽Harrison Smith spars with Viva Frei and others over what the global elites will and won’t do to stay forever young
8 all time great CONSPIRACY THEORIES
8 believers and skeptics
DON’T MISS THIS!!
(See comments to watch):
Texas Comptroller @DonHuffines has issued a new executive order barring businesses that require COVID-19 vaccine passports from receiving contracts or grants from his office.
Businesses must certify compliance or face immediate termination.
Pou chèf gang yo ak manm gang yo k ap kenbe kat konpatriyòt nou yo an otaj ann Ayiti:
Mesye nou kidnape yo pa konbatan. Yo se teknisyen nan domèn avyasyon ki fè pati misyon nou ann Ayiti, nan kad yon misyon entènasyonal. Misyon nou an gen sèlman pilòt ak pèsonèl teknik, ki gen kòm travay prensipal fè evakyasyon medikal epi sove lavi moun, pa fè lagè.
Men, nou te kidnape yo yon fason lach pandan yo t ap retounen apre yo te fin achte manje nan yon makèt nan zòn nan.
Se poutèt sa, jodi a nou te lanse yon operasyon militè pou pote yo sekou. Nou gen yon sèl objektif: fè kat konpatriyòt nou yo retounen lakay yo vivan, san okenn mal.
Men, mwen vle pou nou menm, chèf gang yo, konprann yon bagay byen klè: atak jodi a pa anyen devan sa k ap vini si nou pa remèt toule kat otaj yo vivan.
Epi pa pran pawòl nou yo pou menas san fondman. Nou deja fini ak gang yo nan El Salvador, e nou kapab fini ak nou tou.
Nou toujou gen tan pou evite sa.
Remèt nou kat konpatriyòt nou yo vivan, san okenn mal, epi tout bagay ap retounen jan sa te ye anvan kidnaping lan.
Desizyon an nan men nou.
Security called me at 6:12 AM today.
"Patch every PHP server immediately."
I asked what happened.
"Two critical vulnerabilities. Remote code execution. No authentication required."
Cool.
How many PHP servers do we have?
According to inventory: 12
According to reality:
Nobody knows.
We found one running WordPress.
Three running old internal tools.
One under someone's desk.
Two inside vendor appliances.
A forgotten employee directory from 2016.
And a server named:
PHP-OLD-DO-NOT-TOUCH
Naturally, that one runs payroll exports.
Then we found a PHP 5.6 box.
I asked who owned it.
The documentation said:
BRIAN.
Brian left in 2019.
We called Brian.
He said:
"Oh wow, that's still running?"
Excellent.
By 8 AM, leadership joined the incident call.
CEO:
"Can hackers actually get in?"
Security:
"Potentially yes."
CEO:
"Without a password?"
Security:
"Yes."
CEO:
"Then why do WE need passwords?"
Not the lesson.
Finance asked if we could wait until the weekend to patch because downtime affects revenue.
Security explained that the alternative was letting strangers execute code on our servers.
Finance asked for a cost comparison.
At 9:17, someone suggested temporarily taking the vulnerable websites offline.
Marketing refused.
"Our campaign is live."
So for the next hour, the company officially decided maintaining a landing page for 20% off webinar registration was more important than preventing remote server takeover.
We finally patched everything we could find.
Then our scanner discovered another PHP server.
Hostname:
TEMP-PHP-2014
Uptime:
4,512 days.
Nobody knows what it does.
Nobody owns it.
Nobody can shut it down.
But every time we block network access, the warehouse stops printing shipping labels.
Security has classified it as critical infrastructure.
It is running PHP 5.4.
The vulnerability has existed longer than half our employees.
The emergency patch took four hours.
Finding out what PHP actually runs took eleven.
The internet isn't held together with code.
It's held together with servers everyone is afraid to turn off.
Good morning everyone
We are on day 3 of early voting in Texas.
So far, the turnout seems to be above 2022 and just below 2024.
While this was expected, this is a really high turnout for a midterm election. My current estimates show a turnout of around 10 million votes.
This is meant to give permission for Republicans to vote for a Radical Democrat.
It's referred to as Permission Structure. I think it's a damn good thing Texas has rejected the Bush Family and their cohorts. Drunk Dade Phelan, John Cornyn are all made from their same cloth and they're hoping the grassroots will break so they can jump right back into power.
How bout you'll have to pry this Party out of my cold dead hands before we go back to your policies!
For years the Bush/Cornyn wing told us we HAD to vote for the Republican, no matter what. Party unity. Hold your nose.
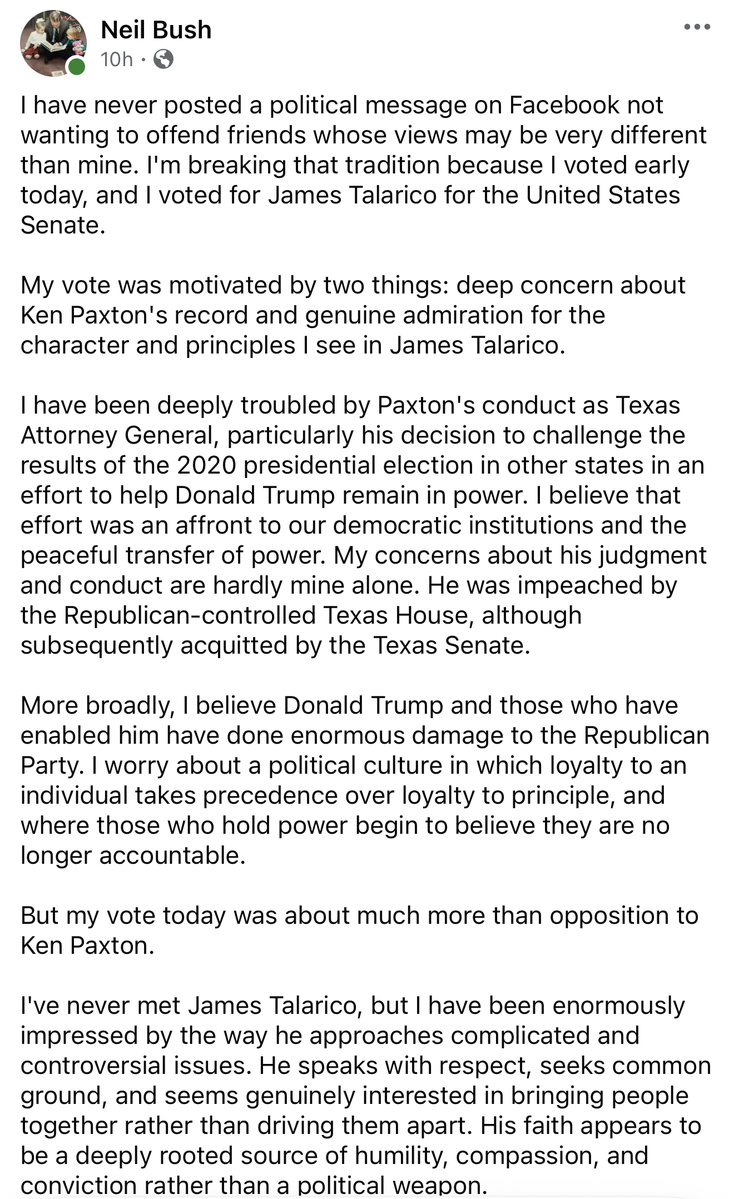
Now Neil Bush votes for a Democrat over Ken Paxton and says "character matters more than party."
Party loyalty was a rule for us, never for them. That's entitlement: they think the party belongs to them. Texas Republicans see it now.
Two critical vulnerabilities have been identified in PHP, a widely used programming language that powers websites and web applications. These vulnerabilities (CVE-2026-109618 and CVE-2026-109619) could allow malicious cyber actors to remotely execute code in PHP core, potentially compromising sensitive data and networks.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/rDrPSxB3zX. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/iqgVZIbCru. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information, follow PHP’s announcement on https://t.co/rDrPSxB3zX, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
Regarding the PHP vulnerability, I have seen some security researchers recommending people limit web browsing for a few days (due to the potential for common websites to be compromised via this vuln).
There is exploit code available for this vuln, though it is not known to exist “in the wild.” But with the weaponization of AI, it’s possible that the discovery and broad distribution of exploit code could happen fast - possibly reverse engineered after the patches are released.
I expect cyber security providers of web application firewalls and exploit prevention services will have protections deployed quickly today, and IT teams will be busy patching and upgrading.
And I think it may be wise to lay low on the Internet today. Do what you need to, but probably skip frivolous browsing.
Also:
Make sure you are running full service anti-virus / anti-malware on every device (including phones). I recommend BitDefender for home/personal use.
Update your browser apps and only use Safari, FireFox, or DuckDuckGo. No opinion about Brave (people keep asking). Make sure ad blocking is turned on and auto play of active content is turned off.
Be very cautious of links you receive in SMS messages, message apps, and email. Check and verify the source first and check the URL to make sure the website domain is as expected.
Keep your operating system and all applications up to date, and watch for new updates over the coming days. Regarding iOS, I do not recommend upgrading to 27. Stay on 26 and update as possible.
Make sure you have MFA turned on for all websites or online accounts. True MFA. Passkey has a major design weakness so I do not recommend it.
This is all to protect your devices and your accounts in case a website you visit is explored and does attempt to steal your credentials, information, or deliver exploit code to your device.
@PractiveSec will be following this today. Advisory coming for customers.
@MaryBowdenMD@acuity It's temporary. Massive Cyber threat so everyone is installing patches. NSA is posting about it, many others. Just hang tight. They started warning companies yesterday of the exploit.
Regarding the PHP vulnerability, I have seen some security researchers recommending people limit web browsing for a few days (due to the potential for common websites to be compromised via this vuln).
There is exploit code available for this vuln, though it is not known to exist “in the wild.” But with the weaponization of AI, it’s possible that the discovery and broad distribution of exploit code could happen fast - possibly reverse engineered after the patches are released.
I expect cyber security providers of web application firewalls and exploit prevention services will have protections deployed quickly today, and IT teams will be busy patching and upgrading.
And I think it may be wise to lay low on the Internet today. Do what you need to, but probably skip frivolous browsing.
Also:
Make sure you are running full service anti-virus / anti-malware on every device (including phones). I recommend BitDefender for home/personal use.
Update your browser apps and only use Safari, FireFox, or DuckDuckGo. No opinion about Brave (people keep asking). Make sure ad blocking is turned on and auto play of active content is turned off.
Be very cautious of links you receive in SMS messages, message apps, and email. Check and verify the source first and check the URL to make sure the website domain is as expected.
Keep your operating system and all applications up to date, and watch for new updates over the coming days. Regarding iOS, I do not recommend upgrading to 27. Stay on 26 and update as possible.
Make sure you have MFA turned on for all websites or online accounts. True MFA. Passkey has a major design weakness so I do not recommend it.
This is all to protect your devices and your accounts in case a website you visit is explored and does attempt to steal your credentials, information, or deliver exploit code to your device.
@PractiveSec will be following this today. Advisory coming for customers.