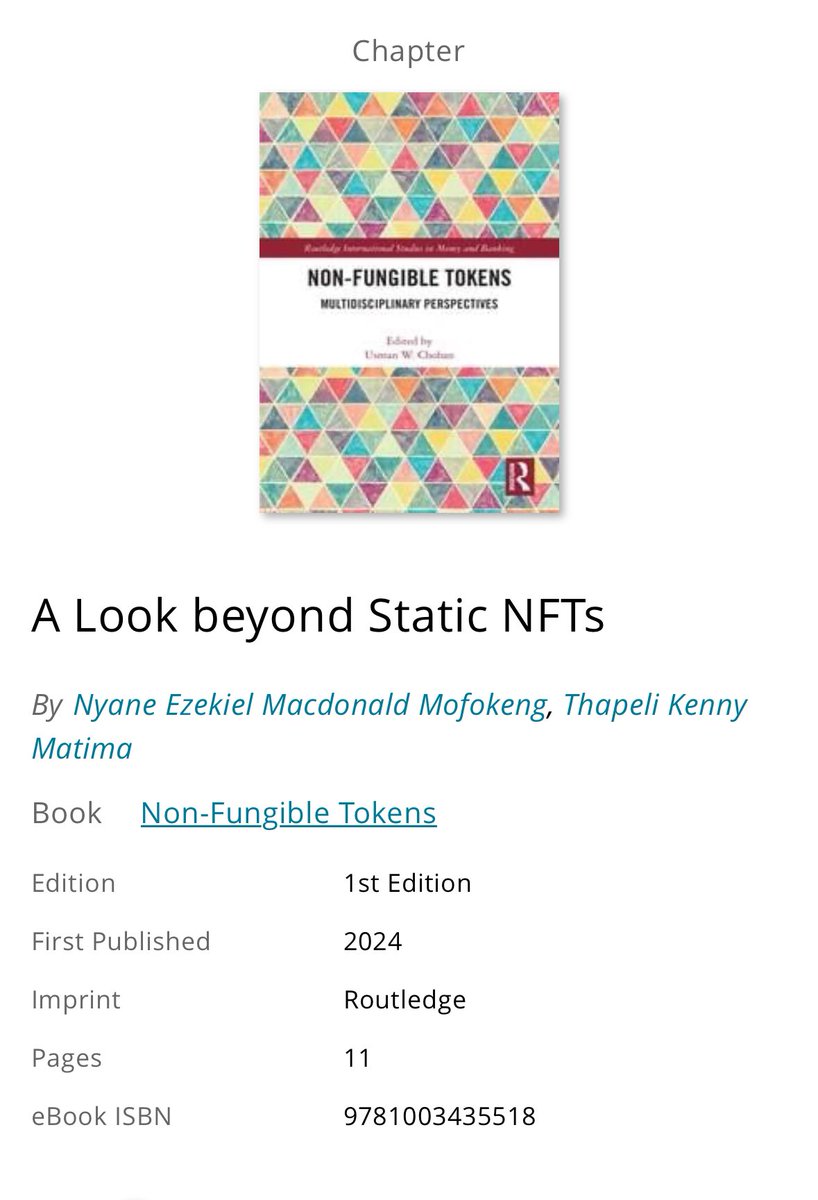
Months ago I was asked to contribute a chapter in this book
my daughter was just a few days old and i was also learning Swift/SwiftUI and developing a mobile app
But still managed to pull this off.
Glad it’s finally published
🎉
@TalBeerySec cyber is plagued on few fronts:
1- incentives - there's big business in selling vuln man, vuln tooling, etc, etc scaring people about CVEs (even though half are unexploitable)
2- leaders
3- marketing
4- incentives
AI turns new vulnerabilities into exploits within hours. Upgrading to patch is too slow.
In real codebases, @SocketSecurity can patch 25 to 50% of critical CVEs today without upgrading a single package. Every patch is human-reviewed. Critical patches are free.
https://t.co/ZZGlk1jkk6
this is the same playbook Anthropic, OpenAI, use of trying to get open source models banned by the U.S
Max China FUD == U.S gov ban "chinese" models under pretence of "national security"
and you left with only "american" models.
Regulatory capture speedrun
Of all the Cyber Security Awareness Months......i would say 2026 delivered.
EVERYONE is aware of PHP
takes one nasty bug to do the work of a thousand security awareness & phishing campaigns
this is the same playbook Anthropic, OpenAI, use of trying to get open source models banned by the U.S
Max China FUD == U.S gov ban "chinese" models under pretence of "national security"
and you left with only "american" models.
Regulatory capture speedrun
While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected.
Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions.
Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent.
But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models?
We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem.
Read the full report: https://t.co/TZSugXi2ZE
I will be making my debut on the Ethereum Consensus Layer Bug Bounty Leaderboard, at ~ #43 for finding a security bug in one of the consensus layer client (when they website updates shortly)
https://t.co/zWzcmV9bVr
https://t.co/PcfEVOoapd
I think we've discovered another critical vulnerability:
CVE-2026-BURNOUT: AppSec Professional Exhaustion
Severity: Critical (CVSS 10.0)
Description: A vulnerability affecting security professionals exposed to a continuous stream of critical RCEs, zero-days, emergency patches, and Friday afternoon disclosures.
Impact: Sleep deprivation, excessive caffeine consumption, and an inability to enjoy weekends.
Attack vector: Reading security advisories.
Affected versions: All AppSec professionals, regardless of experience.
Mitigation: No known patch. Air-gapping may delay the inevitable. Total system collapse remains a possibility. 🔥
"An unauthenticated remote attacker could crash the Axigen server process with a single small request"
Reported this to Axigen and they were quick to respond
https://t.co/yQn2tiycKL
Bug bounty platforms forcing people to pay money to submit reports is crazy.
“Its to filter out AI slop reports” - use AI yourselves for the triaging
And it’s the crypto platforms with this silly requirement
Maybe its just another revenue stream so atleast be upfront