I really recommending reading this.
In summary, a company which does ID verification for in-person interactions (hotels, car rentals, ID verification for alcohol or marijuana, etc) has some how exposed over 153,000,000 drivers licenses for people in the United States and Canada.
It is a catastrophic data breach, probably one of the worse I've ever seen. If you're in the United States and have traveled, gotten a hotel, purchased marijuana or alcohol, there is a high probability you're in this.
Unlike other breaches, this includes a photo of the person (from the license), making verification you've identified the person significantly easier.
This poses a significant threat to celebrities (musicians, YouTubers, streamers, adult entertainers, actors, etc), politicians, lawyers, wealthy people (CEOs, investors, people of public interest), Law Enforcement Officers, etc
Krebs himself, and several other security researchers, have already confirmed they're in the data leak.
tl;dr gah damn dawg this company is going to be sued into oblivion
https://t.co/QpsegBUzH5
Ready for a new adventure? 💛 An original Kingdom Hearts anime series inspired by the beloved video game franchise is coming soon to @DisneyChannel and @DisneyPlus
@Mister_MDM At my work we are doing device driven ESP and use an account afterwards so we can trigger IME to push apps to the device bypassing the wait.
Do you know if this will require a user login still?
Last week I hosted family for Thanksgiving.
My 12-year-old nephew asked for the WiFi password.
He wanted to play Roblox on his iPad.
I looked at the device.
Unmanaged. No antivirus. No encryption.
I’m an IT Professional. I don't run an open network.
So I didn’t give him the password.
Instead, I spent 45 minutes provisioning a Guest VLAN.
I set up a captive portal.
I throttled the bandwidth down to 56kbps.
Then I blocked all traffic on ports 80 and 443.
He came back crying. He said it wouldn't load.
My sister screamed at me to "just let him play."
I told her that Zero Trust architecture doesn't care about bloodlines.
We didn't have a "fun" Thanksgiving.
But we had a secure perimeter.
You’re welcome for the compliance.
🚨🚨CVE-2025-52665 (CVSS 10.0): RCE in UniFi OS
A malicious actor on the management network could exploit a UniFi Access misconfiguration exposing an unauthenticated management API.
Search by vul.cve Filter👉vul.cve="CVE-2025-52665"
ZoomEye Dork👉app="UniFi OS"
279.8k+ live targets.
ZoomEye Link: https://t.co/Z9QJS5Lm5n
In-depth Analysis from @3zizMe_: https://t.co/Wn4DqQz0zw
Refer:
1. https://t.co/c4HIEB89aD
2. https://t.co/oLxqufExHf
#RCE #ZoomEye #cybersecurity #infosec #OSINT
⚠️ Heads up!!! Big warning for HP AI Devices! ⚠️
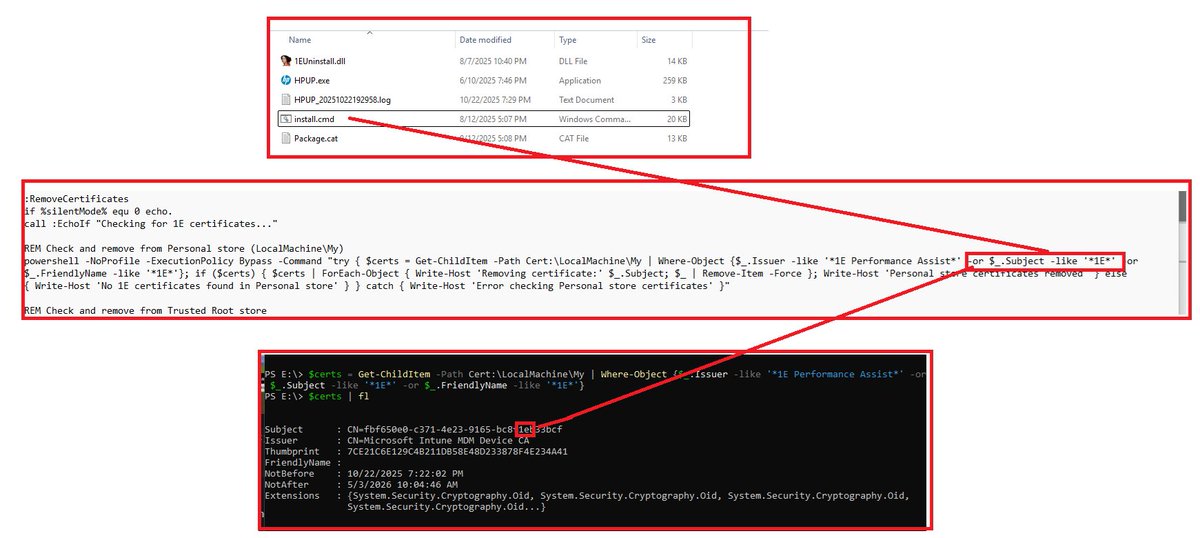
Some of HP’s latest Next Gen AI PCs, including the EliteBook X Flip G1i, are getting the updated OneAgent 1.2.50.9581 build.
That version seems to run a cleanup script removing any certificate containing “1E” in its subject .... which can delete the MS-Organization-Access cert.
Once that happens, your device is no longer Entra joined or Intune Enrolled!.
#Intune #MSIntune #Windows #Windows11 #Entra