🔍 Here is an upadated version of https://t.co/UNZmZoumRp website
Most people still bookmark https://t.co/UNZmZoumRp as their go-to tool map.
The problem is it hasn't been updated in a while, and OSINT tools die or change fast.
I switched to Malfrat's OSINT Map, an actively maintained alternative built on the same idea.
What it gives you:
✅ The same category tree structure (usernames, emails, phone numbers, domains, images, and more)
✅ A legend that flags each tool as web-based, requiring install, paid, or offensive
✅ Categories the original never had, like cryptocurrencies and military
✅ An open GitHub repo where anyone can submit new tools or flag dead ones
🔗 Tool: https://t.co/mZfYTxWx3q
__________
P.S. ♻️ Repost if you found this helpful.
The only reason the protesters here get to do that is because our military pays the price to give them that freedom. And I hope the protesters use one tiny ounce of that energy to find one of our nation’s heroes here and say THANK YOU.
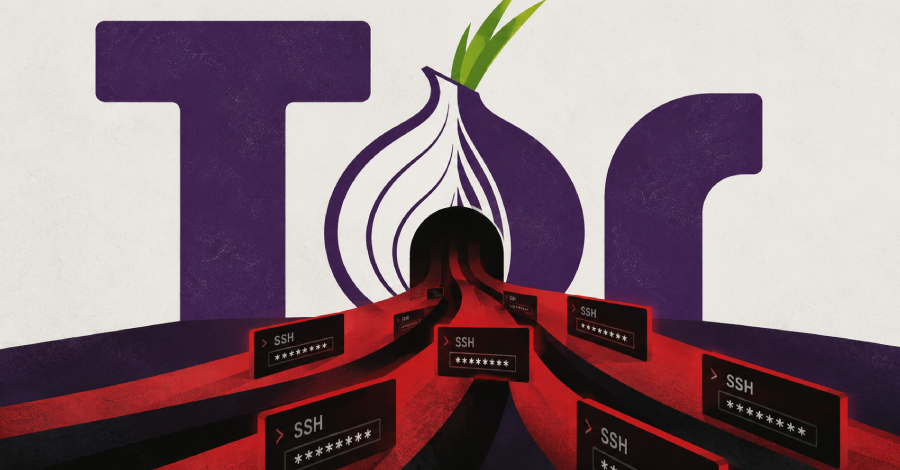
🛑 Attackers hijacked over 300 Tor exit relays to intercept SSH connections and steal login passwords.
A researcher found 333 exits redirecting SSH traffic to 12 interception servers.
The Tor Project has since blocked the affected relays.
Here's how the attack worked: https://t.co/eJsVNeh5xA
I'm working on a unique #DFIR training for next week.
You've never seen anything like it.
It's free. Invite only. But I'll invite anyone interested.
It's the highest professional risk training I've ever attempted.
I'm letting people in my head, in real-time, on a real thing, that can have real effects in the physical world.
Standby for the what, why, where, how....
A real Calendly link. A fake Bloomberg interview. A phising chain designed to target people in AI and osint.
The first domain was genuine. The downstream workflow was not.
I break down how the campaign worked—and the checks that matter before you trust an “interview” invite. 🎥
Read the blog here:
https://t.co/wIeUrBHITJ
#OSINT #phising
Let me spell out what this means for privacy:
Surveillance is hidden all through opaque software. You are never meant to find it.
But AI can decompile, analyze, & expose exactly what your apps are doing.
The age of "trust us" software is ending. Privacy revolution incoming.
One minute of vigorous exercise may be worth 4–10 minutes of moderate activity, depending on the health outcome
In one study, 1 vigorous minute was associated with a similar reduction in all-cause mortality risk as about 4 moderate minutes
For cardiovascular mortality, the equivalent was nearly 8 minutes, and for developing type 2 diabetes, nearly 10
These findings suggest that making some of your exercise more intense could substantially increase the return on your time
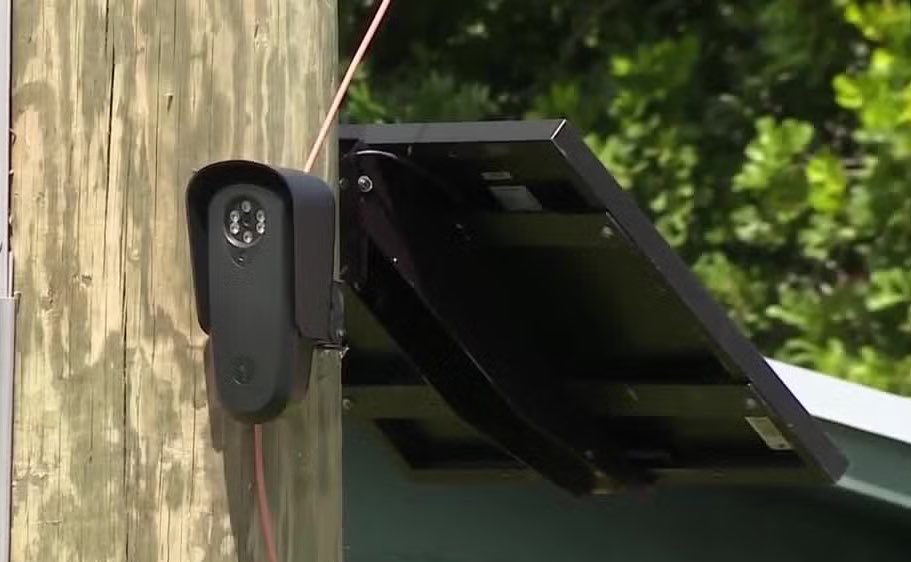
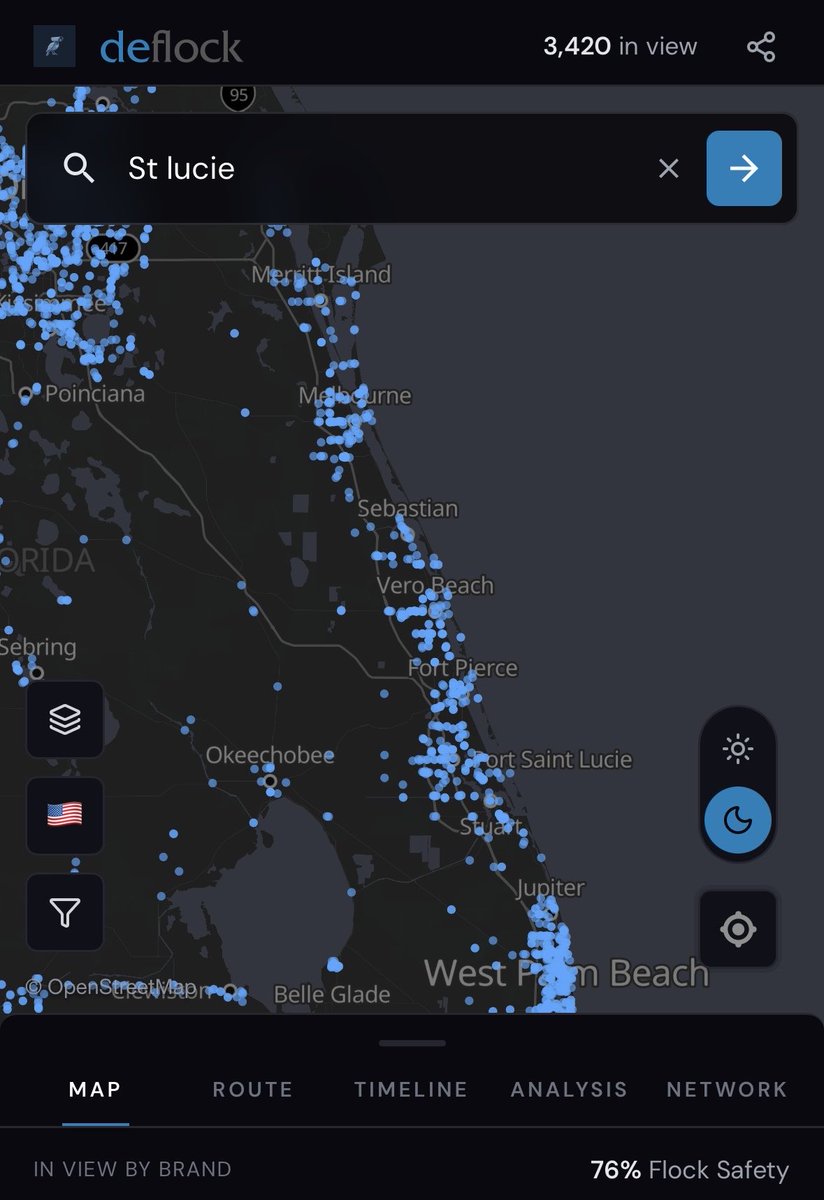
St. Lucie County, Florida voted to rip Flock cameras off county roads. Then staff found at least 14 more sitting in the right-of-way with no permit and no owner on file.
Nobody has claimed them. Officials can’t say who installed them or who’s been reading the plate data. Residents are unnerved.
Cameras nobody authorized, tracking every car that passes, and the county can’t even tell you who’s watching.
.@SECWAR “The power is back in the hands of Commanders and NCOs. NOT LAWYERS AND HR REPS.
Telling someone to get in shape, shave, fix their uniform, or start busting their ass—that’s not discrimination; it’s leadership.
We have ended the poisonous culture of risk aversion and empowered leaders—at every single level—to simply enforce standards.”
Coffee may be one of the most overlooked tools for healthier aging
In one study, each additional daily cup was associated with an epigenetic age roughly 0.7–1 years younger
Another analysis linked 3+ cups daily to a 34–41% lower likelihood of accelerated biological aging
Coffee drinkers also show up to 27% lower all-cause mortality risk compared with non-drinkers
Similar longevity benefits appear with decaf, pointing to a potential role for coffee's polyphenols and other compounds
🚨 Identity verification company, IDScan, hid its own breach notice from the web. They leaked over 150 million drivers' licenses to a hacker group.
The webpage notifying of the breach contains a "noindex" directive, instructing search engines not to index the page.
Yet another Android leak enabling malicious apps to send traffic outside the VPN tunnel has recently been discovered.
Read more here: https://t.co/M6gR7A4qKw
GrapheneOS is done waiting for Google.
It's replacing Android's old default apps with its own.
Instead of relying on neglected AOSP apps, it's building modern alternatives from scratch.
What's changing:
• New Gallery app
• New Keyboard
• Massive Messaging app overhaul
• Secure Paste that blocks apps from reading your clipboard
• Future RCS without Google Play Services
The goal is simple:
Own the entire privacy stack.
Would you switch to GrapheneOS for features like these?