To anyone worried Microsoft 365 has become Microsoft 364, don't panic!
2028 is a leap year, so you'll get your missing day back. Assuming they fix the outage by then. 😂
🪟#microsoft365down#MicrosoftOutage
30 years ago today, Phrack 49 published Aleph One’s “Smashing the Stack for Fun and Profit”.
A legendary paper that inspired generations of hackers and helped shape modern exploit development.
Still an essential reading.
https://t.co/qAQ5CWgNj0
Phrack 73 is coming soon!
‼️ BREAKING - Critical Rails flaw (CVSS 9.8) could let unauthenticated attackers write arbitrary server files via crafted uploads.
The bug affects Active Storage apps using ImageMagick and could also expose application secrets in certain setups.
Rails patches are out.
Details: https://t.co/ic1dUe7KBT
Very quick vibe coded little local proxy called https://t.co/qLTi9cKpEZ to opportunistically catch if you're being served a revoked cert till apps/IoT devices catch up.
(It doesn't decrypt app traffic - it makes a separate connection with the pros & cons that comes with.)
One tap was enough to bypass a Chrome for iOS security check.
We found a way to use shortcuts to reach tel: or facetime: without Chrome applying its normal user-interaction checks to the final URL.
The issue, CVE-2026-13795, has been fixed.
Details 👇
https://t.co/tGbidj8LzG
#appsec #doyensec #security #ios
New blog post!
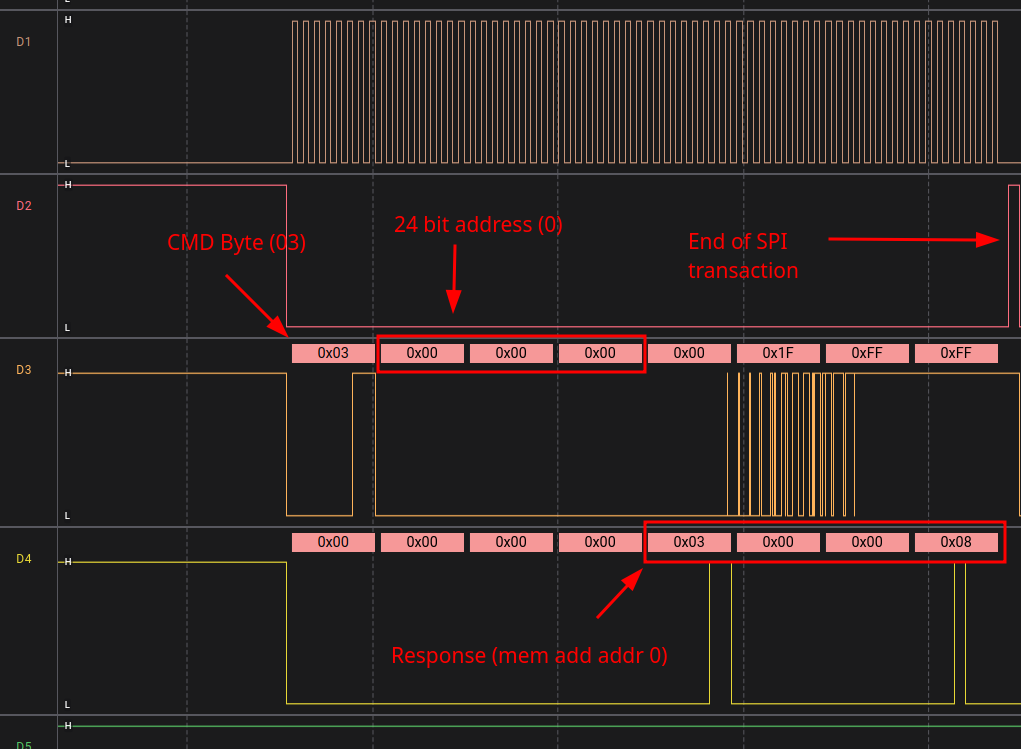
Extending Scapy for Hardware Reverse Engineering
https://t.co/cvezXY4RXp
In this post we use Scapy to reconstruct a SPI flash image from a logic capture, with an introduction to QSPI!
~ Personal news ~
I left TechCrunch. I will now focus on finishing my book about Hacking Team and the history of government spyware.
After that, and in the meantime, I will be freelancing.
Contact me: [email protected] or Signal @ LorenzoFB.1337 (+1 917 257 1382)
This is unpopular but correct. Modern bug bounty participants have gotten spoiled by super chill responses to CFAA violations (like this one) and the whole edifice is a house of cards. Wanna know why OpenAI asked for detailed logs? Google “Sullivan + Misprision of a Felony”
I really can’t stand this fake "BREAKING/JUST IN" communication style on X. In particular in my "For you" feed. Most of the time the story is days old or even months, but people still slap urgency labels on it like newspaper hawkers. Just give the damn source date! </rant> :D
We escaped Docker's hypervisor with three lines of bash. CVE-2026-77179: A container gets complete read and write access to the host filesystem.
When you mount a folder into a container, Docker's VMM uses virtio-fs, and the file server runs on the host.
Because of a TOCTOU bug, if a container opens a file, deletes it while holding its file handle open, and replaces the parent folder with a symlink, the kernel will follow the symlink to anywhere on the host.
Full technical breakdown:
https://t.co/jwsc5aozru
A name that has shaped how the world connects is joining https://t.co/g3vGGlphWi Netherlands 2026.
We’re pleased to welcome @Cisco as a Silver Sponsor.
📍 Amsterdam Marriott Hotel | 16–20 November 2026
Register now: https://t.co/aO21bK1ojD
#HardwearNL2026#SilverSponsor
Today we published WeWorm, our zero-click worm that spreads across iOS and Android.
All it takes is one phone call. You don't have to answer. Seconds later, your WeChat account is compromised, calling your friends and spreading the attack.
We reported the bug to Tencent, and it's now mitigated for all users.
We hope this sets an example. The US and China disagree on plenty, but keeping billions of people safe online shouldn't be one of them.
AI gives us a chance to find and fix these bugs faster than ever. We should work together to make the world safer for everyone.
Our story and demos: https://t.co/YsoYFduv60
So, most mainstream LLMs down, means a single point of failure given by , I guess, a single data center provider going down? That’s what’s the world is actually standing on?