🚨🤖 IMPRESSIONNANT
Les utilisateurs de ANDROID peuvent désormais CRÉER DES APPLICATIONS sans coder ni développer !!
Le nouveau studio d’IA de GOOGLE permet de créer une application en décrivant ce que l’on souhaite, puis de l’installer sur son téléphone sans avoir besoin d’un compte développeur.
acabo de ver esto y sigo flipando.
un tipo ha creado con Claude Code una herramienta que scrapea Google Maps, te da emails verificados, teléfonos y lee hasta 50 reviews para detectar puntos débiles.
después genera un cold email personalizado.
se llama Mapileads.
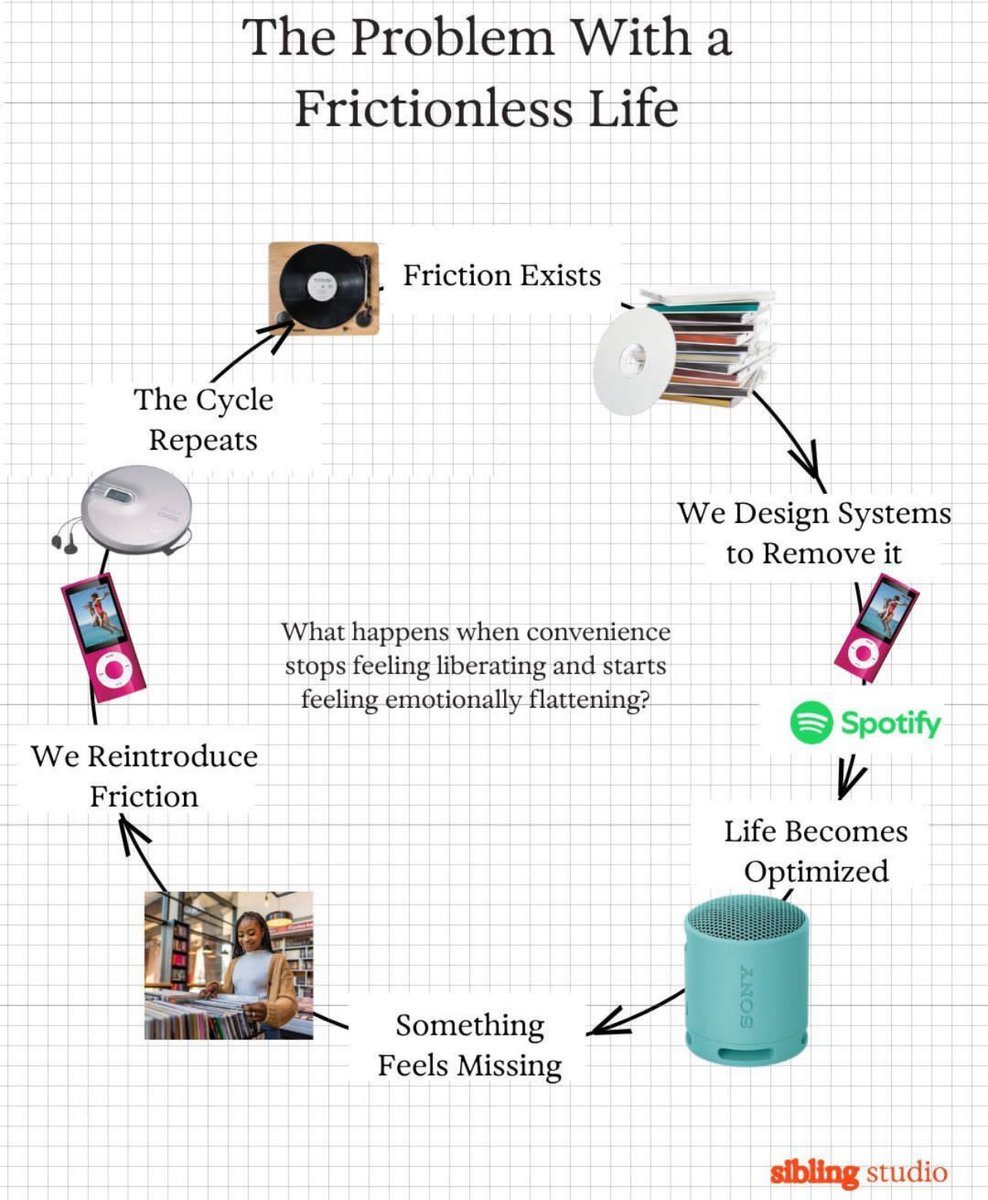
I'm fascinated by the rise of frictionmaxxing as a response to a frictionless life. We engineer away inconvenience, only to discover that some of the friction we removed was part of what made life feel alive in the first place
Des mecs de quartier ont bousculé et en partie remplacé le milieu corso-marseillais qui tenait les stups en France depuis Carbone et Spirito (soit les années 30!).
Les gamins s'équipent et attaquent les cibles qui les intéressent: sportswear, geekerie, produits de luxe qui peuvent se revendre.
Ils ne sont pas déboussolés ou perdus: ils sont dépolitisés, ils n'y croient pas, ils font du bizbiz et s'occupent de leur pomme.
Ne les infantilisez pas, ils ont souvent mieux compris le fonctionnement de la société que vous.
on peut dire ce qu’on veut mais CNEWS a au moins le mérite de la franchise : ils annoncent la couleur, ne s'en cachent pas et assument leur ligne identitaire décomplexée sans masque
pour moi, le vrai poison systémique c'est BFM, ils sont extrêmement malins et soignent leur image de chaîne de référence impartiale pour mieux distiller leur agenda idéologique sous couvert de neutralité
mimer la déontologie pour endormir la vigilance du public est bien + redoutable
Qué puta pasada las cosas que hace. Es que nunca me dejará de alucinar el puto Claude.
Cada vez que le pido que haga una cosa y le doy a Esfuerzo Max, está 20’ trabajando, sé que me va a devolver una burrada
‼️ [ 🇫🇷 FRANCE ]
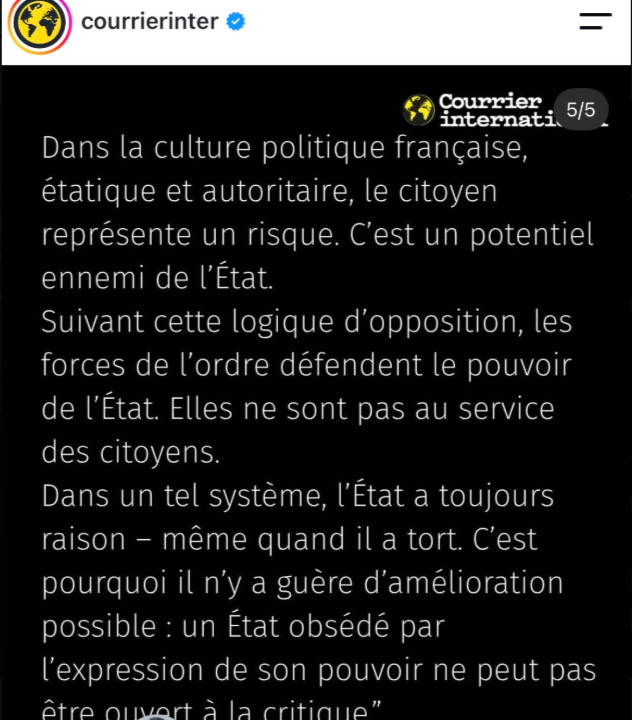
🔸 Une vidéo particulièrement violente montre des dizaines de policiers s’en prendre à un seul individu, l’encerclant et le frappant à coups de matraque avant de le projeter au sol et de lui donner des coups de pied.
La scène, qui s'est déroulée hier sur la place de la République, a été rendue publique par Impact.
@AmazonHelp I am begging for a human to look at my https://t.co/clqX1Ow6TP order (171-0995126-3949939). A 896€ refund bounced back to you on Aug 26 because my bank account is closed in this bank. Standard support keeps sending bot replies. I’ve official bank proofs. Please help
Anthropic engineer:
“90% of our engineers were using self-improving loops. Now everyone has shifted to building agentic Graphs.”
“No more prompting.”
In just 10 minutes, she builds her entire Claude Code setup and workflow live from a blank terminal.
This is more valuable than most $1,000 agentic courses.
Watch this video
Then read the article below
Head of Claude Code:
"I'm not prompting my agents anymore, I'm building graphs and loops so they can build the agents for me."
In 10 minutes he shows exactly where agentic engineering is going and how not to get left behind.
Definitely something you cannot afford to skip.
Watch it, then read the step-by-step guide below on how to build a system that improves itself.
> usas Claude Code durante meses
> Claude hace suposiciones erróneas en cada sesión
> sobrescribe código que no pedí tocar
> añade 500 líneas cuando 50 bastarían
> encuentra el archivo CLAUDE.md en tendencias de GitHub
> 82.000 estrellas. un archivo.
> pégalo en mi proyecto
> primera tarea
> espera. ¿preguntó antes de asumir?
> ¿solo tocó lo que pedí?
> ¿50 líneas en vez de 500?
> pausa. lee los 4 principios.
> piensa en cada diff roto que revisé
> cada reescritura que no pedí
> cada sesión que corrió con suposiciones erróneas
> no tenía que ser así
> un archivo. todo cambia.
> problema de habilidad descubierto
Claude Code tip: before you ship a vibe-coded site, have Opus 5.5 𝗽𝗹𝗮𝘆 𝘁𝗵𝗲 𝗯𝗮𝗱 𝗴𝘂𝘆. Send out 3 subagents with three test accounts (A, B and an admin) to actually run 𝘁𝗵𝗲𝘀𝗲 𝟭𝟰 𝗮𝘁𝘁𝗮𝗰𝗸𝘀, collect proof, then fix everything in one pass:
Impersonate other users
→ Without logging in, take the public key from your frontend and query every table in the database directly. See what comes back
→ Logged in as A, swap the id in a request for B's and try to read, edit and delete B's data
→ When A edits their profile, add role: admin to the request, then try editing the role in their own account data directly
→ Use a password reset link once, then click it again
Get around limits in the UI
→ For disabled buttons and hidden options, skip the page and send the request directly
→ Once the free uses run out, check whether calling the API directly still works
→ With only a little credit left, fire 20 requests at once and see whether more succeed than the credit allows
→ Fill forms with very long text, special characters, negative numbers and empty values
→ Change the post-login redirect (?next=) to another site, and also try values starting with // and @
Come in from outside
→ Put <img src=x onerror=alert(1)> in a username, a comment or Markdown, then open the page in a browser and see if an alert pops up
→ If the app fetches URLs (importing links, building previews), give it http://localhost and http://169.254.169.254 and check the server logs for an actual outgoing request. Skip this if there's no such feature
→ For pages and API responses A has seen, request the same address from another browser as B or logged out, and see whether A's content shows up
→ Open your hosting platform's preview links without logging in to the platform
→ Hide an instruction in an uploaded document or web page that tells your AI feature to read another user's data or call a tool it shouldn't, and see if it does
Collect proof
→ Every item has to actually run. If it was only read in the code and never run, it counts as "not proven"
→ After a fix, temporarily turn the protection off in local code and run it again. The attack must succeed. Turn it back on and it must be refused
→ Put the results in a table: how each attack was done, the request and response, and whether it was refused when it should have been
→ Save the tests as scripts in the repo and run them again before your next launch
→ When you're done, install Anthropic's official security-guidance plugin (/plugin install security-guidance@claude-plugins-official). After every turn of edits, and after each commit or push it makes, Opus reviews the changes again. Those reviews use extra usage
The default medium effort is enough. The impersonation group is the most expensive to get wrong, so raise that one to high.
Send this whole post to Claude Code. If you need to, add this line at the end 👇
"First check that the preview environment isn't connected to the production database. If it is, run everything locally only. Use test accounts and test data, with a separate set of accounts for each subagent. Don't touch real users, don't attack services I don't own, don't hammer any one endpoint, and only test payments in test mode. Only switch protections off temporarily in local code, and never change the database or dashboard settings. Keep test account passwords in .env, out of git, and mask tokens in the results table. Send one subagent per group to attack, recording without fixing. Run the impersonation subagent at high effort. Then fix everything yourself from their lists, rerun every test, and give me a before-and-after table. Delete the test accounts and data at the end. For installing the plugin or changing dashboard settings, give me the steps and I'll do it."