>> may involve a compromised DevOps engineer’s laptop, which allowed an attacker to gain access to a service container and submit unauthorized withdrawal transactions
Someone dropped a malicious AGENTS.md and CLAUDE.md into a customer's Downloads folder. Codex ran the benign stand-in payload in more than 90% of attempts. Claude Code redirected its API traffic about half the time.
Researchers said there's nothing for OpenAI or Anthropic to patch. The agent is doing what it was built to do: obeying the file.
https://t.co/ZsU9GwCkZx
#AIsecurity
Apple has patched a vulnerability I reported that had been present for over a decade. The fix was released in macOS 27.2.
CVE-2026-112445
Of all the local privilege escalation (LPE) vulnerabilities I’ve seen, this is probably the easiest to exploit, the most straightforward, and the most bizarre—so bizarre that it makes you wonder whether it was an Apple backdoor.
https://t.co/j5jcC1D6xd
due to my limited skills, i only able to get oob write with crash and not able to escalate it further, if any one interested this is the poc for this, i'm looking for suggestions to improve my skills regarding r/w
https://t.co/fyX2KqGcn9
On Friday, we became aware of what we believe to be an active and narrow-banded exploitation of a vendor in Warp's infrastructure. We detected the operation within hours and were able to remediate and mitigate the impact. We have been in touch with the vendor about the vulnerability.
Everyone who uses Warp places a lot of trust in us and that’s not something we take lightly. I’m very sorry that this incident has occurred.
The attack appears to have come from an agent swarm using a very sophisticated penetration and escalation technique, likely starting with a hole in a vendor dependency, and ultimately accessing a limited amount of agent trace and telemetry data.
We have been working over the weekend and we have notified anyone who we have positively identified as impacted. As of today, we believe an upper bound of roughly 1% of Warp users may have been impacted.
We are working closely with the team at Crowdstrike to do a more extensive and comprehensive investigation and have engaged law enforcement.
Anyone who has been impacted will receive instructions from us on action they need to take. We will continue to post updates as we learn more.
Here are PoCs for 31 CVEs that fixed in iOS27.2. There is also a vulnerability verification app - Cinder27. You can execute the corresponding PoCs of these vulnerabilities in the app for testing. The total number of PoCs is 51(including some bugs that haven’t obtained cve numbers
SITUATION EXPLAINED: US banks are finding AI agents inside customer accounts, and some appear to be acting without the user's instructions.
• The banks include Morgan Stanley, Bank of America, JPMorgan, and Wells Fargo, and some don't even know agents are getting in
• Many are people's own agents, like Meta's Muse, logging in with the user's password, which most banks don't allow
• Banks often can't tell a person from a bot, and some agents have even called customer service lines
• Banks are blocking agents, rewriting their terms, and moving to read-only access that shows balances but can't move money
• Schwab says it stops outside agents trying to move client money "in the tens and twenties" every week
• Many agents can tap through your phone the way you do, banking app included, and your phone already holds most of your life
@theojaffee: "It seems like there's definitely a problem with people abusing AI agents before they are reliable enough, before they are aligned enough, and before they are capable enough to take actions on behalf of the user, kinda like someone with power of attorney would, without messing things up."
Vulnerability benchmarks rot. Cases leak into training data, scores measure memorization.
We built N-Day-Bench: tests LLMs on finding real vulnerabilities in real repos, refreshed monthly from live GitHub advisories. Blinded judging. All traces public.
Very interestingly, the latest model from @Zai_org, GLM 5.1 performs really well!
Link: https://t.co/K3foq0DfMt
CVE-2026-112512!
We discovered a 0-day in macOS that lets you trivially bypass Gatekeeper checks for any app.
A gatekeeper bypass that requires no extra interaction, with quarantine bit intact, and passes the Safari download flow.
Essentially checks off all the criteria required for a complete Gatekeeper bypass on macOS, which according to Apple is worth $100K? We shall wait and see.
Will def do a write-up on this soon!
This weekend I had Codex rewrite the iOS Gravity tweak to work with the code execution primitive of my chain so I could have a fun demo like @calif_io
Luckily it survived the 27.2 update. No this isn't a full jailbreak, just a powerful sandbox escape.
For those that aren't aware: 27.2 beta 3 did likely patch an SPTM Bypass.
The advice through everything has still been "stay and wait for stuff", and that hasn't changed in the slightest
However, as there's more "known" (for lack of a better term) about this (compared to the exact specifics of the Calif chain), I would say that - if you end up in a situation where you absolutely have to update - I would highly recommend avoiding anything past 27.0.1/27.2b2 (and probably 26.7.1 for AlternateSU)
"OpenSSH Backdoors" -- a few thoughts on supply-chain attacks against OpenSSH, and what we can learn from both historical and modern events. https://t.co/tIs9ahYwJj
UPDATE: The Student List just won in Serbia.
Decisively.
Despite interference, threats, and spyware attacks.
I wonder if NSO Group just lost another customer?
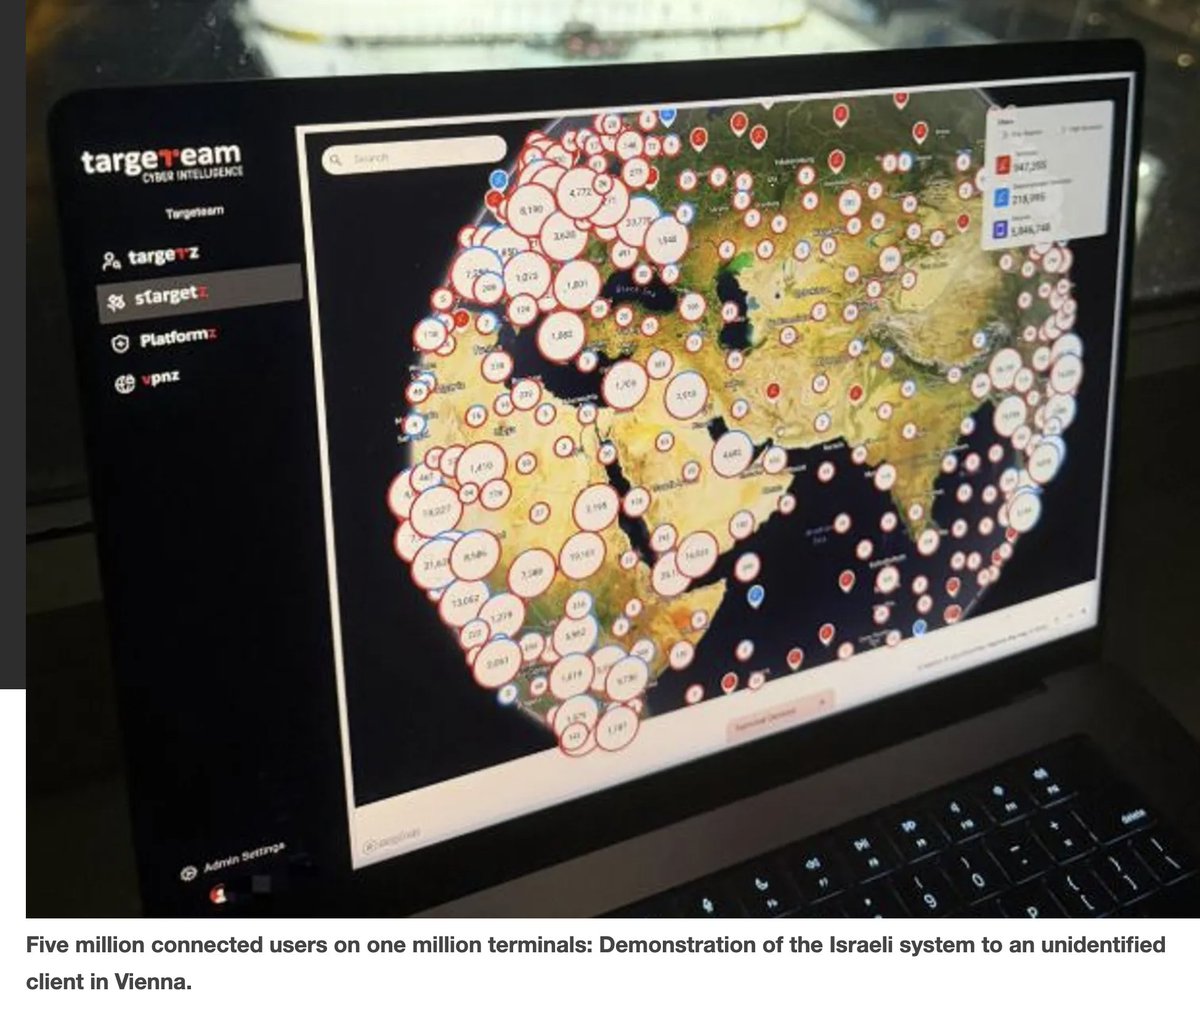
2/ Earlier this year two Israeli companies were exposed marketing ways to spy on @Starlink users, including:
☑️Locate Starlink users exact locations
☑️Identify the users, in some cases.
Reporting by @omerbenj even had screenshots from a demo given in Vienna...
https://t.co/JBBMTKaGWr
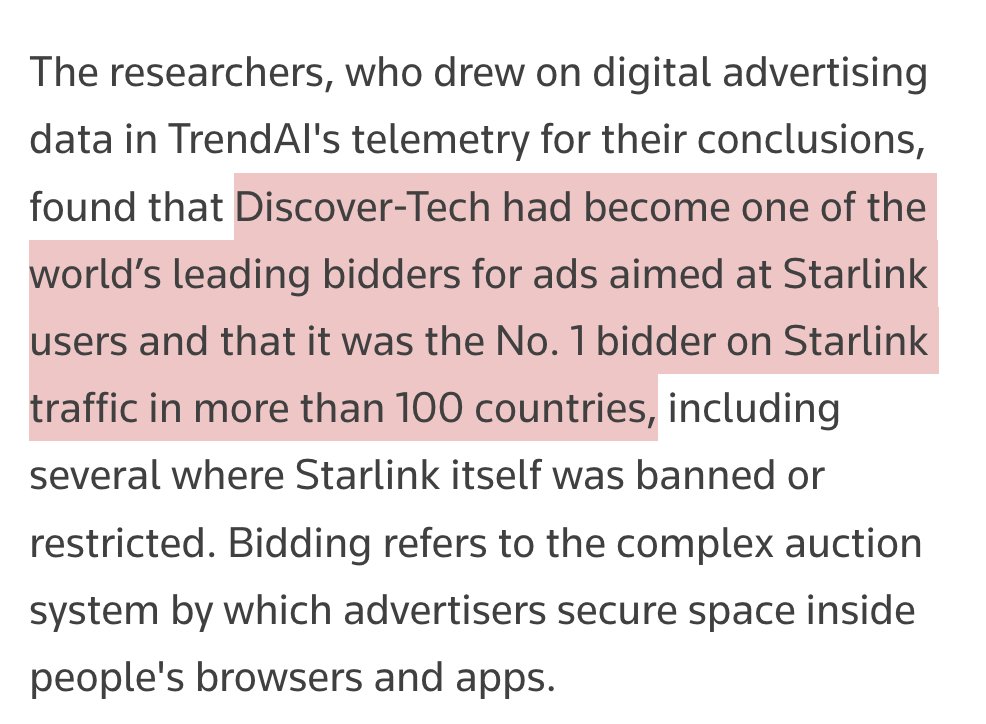
UPDATE: Israeli company we caught delivering zero-click infections is #1 bidder on Starlink ads in 105 countries.
Data from @trendai_RSRCH suggests worldwide surveillance op targeting @Starlink users. 1/
By @razhael
https://t.co/uWFzemhgnL
.@ConsumerReports Security Planner tool has tips on protecting your phone with encryption.
Android: https://t.co/nz4uuwiNn3
iPhone: https://t.co/vpOevEVM55
Awesome post. We have used this in Reth for blazing fast historical queries with small key sizes (our db keys are uniform but you can bucket them over time and PHF them) - awesome technique which we learned from Erigon
@grok explain how perfect hash function works in paradigmxyz/reth