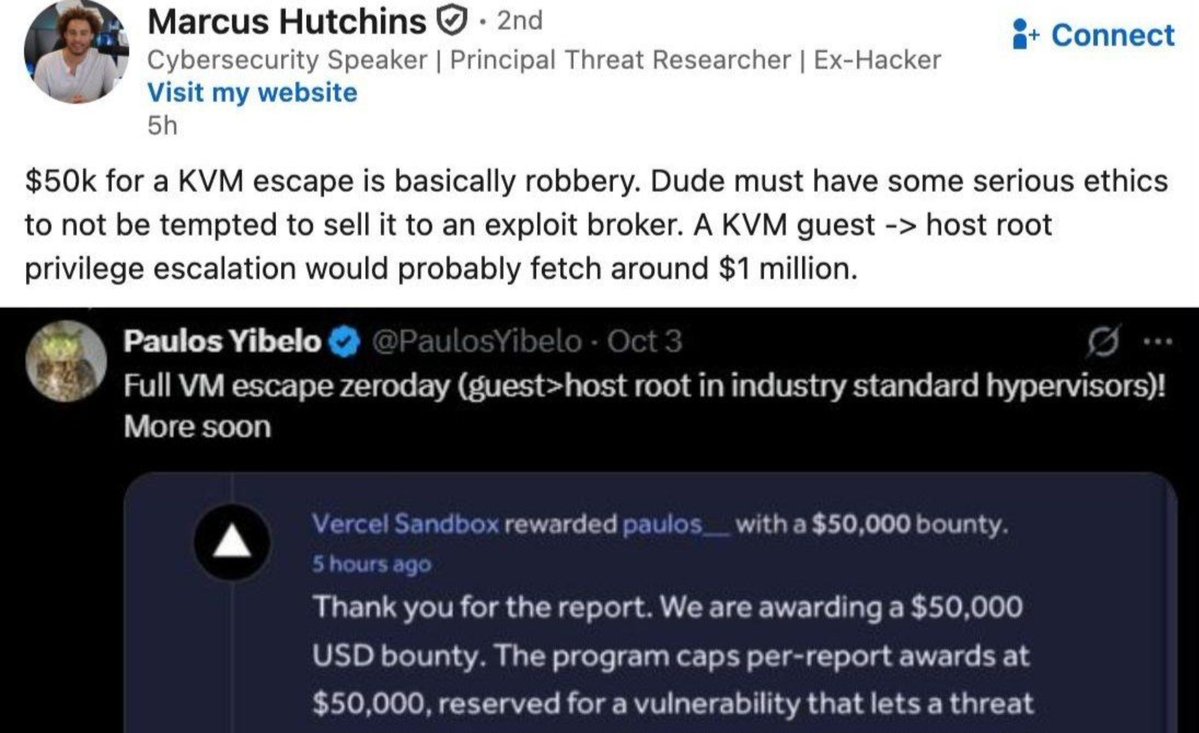
A lot of speculation on if KVM bugs have gotten cheaper, and why id do it for 50k instead of a milly. I wasn't born yesterday. I know I couldve sold it for waayy more. I didnt want to. I did it for the love of the game. I wanted to know if I could do it, and now we know i can. Maybe I am a big dreamer?
Very powerful bug. In the past, we also submitted few one-shot to Chrome GPU via ANGLE ( but before 250k era 🥲).
This report may include the trick for escaping from the GPU to the CPU ( but i guess too easy for AI atm )
Looking forward the details when the bug is de-restricted.
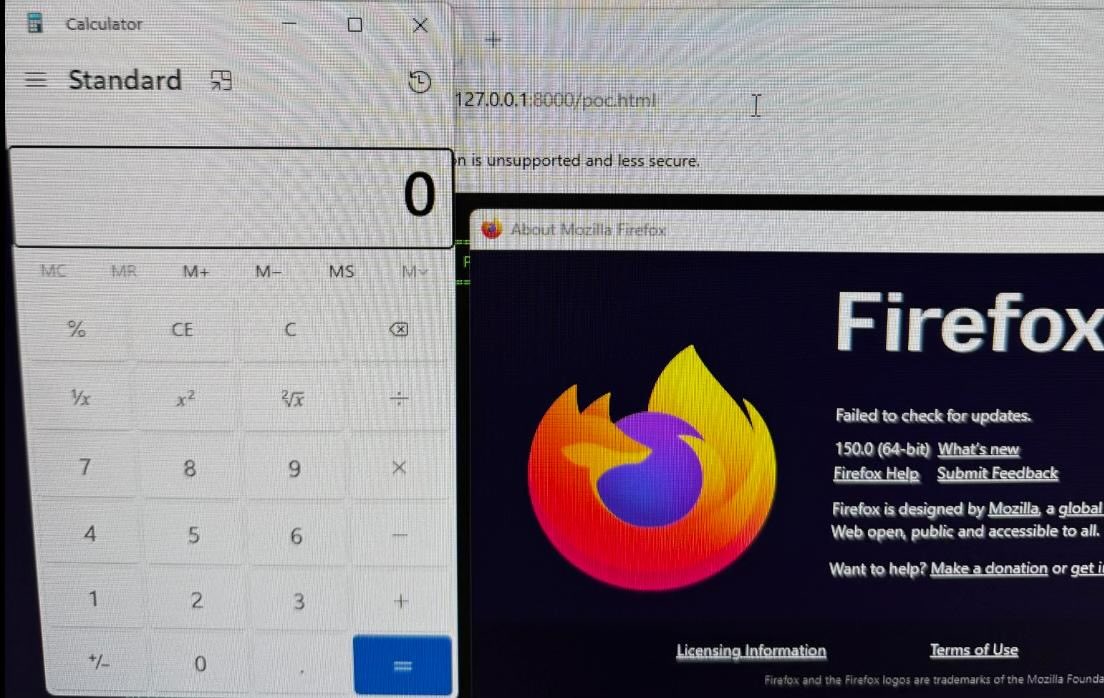
The released firefox 150.0.3 today has killed our renderer exploit component, since only 1 day left we have no choice but withdrawal our entry.Kudos to our teammate @trichimtrich , @lanleft_ and @wiz1340 for their hard works that created 2 fullchains work flawlessly from firefox 147-150.0.2 ( 4m+ alive) but was being killed one week and 1 day before the event
Good luck for the rest of participants!
And thanks everyone for wishing us luck 🙏
Like usual, we will share writeup in future when the affected version is irrelevant, Cheers!
We’ve been through all kinds of situations: exploits failing, vendors turning off services during demos, patches being released the night before a demo, and more but we happily accepted and continue to play.
And if you don’t participate in the game, who cares about your opinion?
Despite 271 bugs massacred by Anthropic, our renderer rce and sbx escape alive and well ready unless there is sudden patch before p2o ( mean we dont have enough time for prepare new one ) - wish us luck!
https://t.co/3oTRESGt5r
Not a single LLM can correctly explain the root cause even given the crash poc of this bug, let alone talk about how to write the exploit code. Kudo @lanleft_ for her great works!
We may publish writeup when it no longer hot.
Last month, I gave a talk at @POC_Crew about ATLANTIS and the tech behind our #AIxCC win.
We dove into competition details, using LLMs for deep bug discovery, and what's next for AI in security.
https://t.co/nWeUr3i24o
A quick review theses Chrome libAngle issues found by Big Sleep likely from fuzzer output more than AI reasoning, 1 or 2 issues even not exploitable because of libc++ mitigation enabled by default in Chrome.
https://t.co/GKswpZ2xhB
The fuzzer still producing many crashes:
https://t.co/jQet7e0s7S
Check out our newest blog about how we took advantage of a WebGPU feature to turn an integer underflow bug into an arbitrary read in Chrome’s WebGPU. This bug was fixed by Google long ago, but our ticket is still restricted.
https://t.co/vYvVPtF2PP
by @lanleft_ + @__suto
We released our Fuzzilli-based V8 Sandbox fuzzer: https://t.co/eVkR1bl76n
It explores the heap to find interesting objects and corrupts them in a deterministic way using V8's memory corruption API. Happy fuzzing!