Know someone who is getting started in security?
I am teaching my Pay What You Can Intro To Core Security Skills class next week!!
At @Antisy_Training we are trying to make world class security training affordable for everyone.
https://t.co/DloQ3T8C7Y
Hey, I am hiring (Virtual US Support) to help me run the Bug Bounty program over here at AWS. Looking for an experienced TPM and Security Engineer that want to help drive new program initiatives, expand our program, build a community and of course day-to day operations.
I’ve been putting out an infosec bootcamp to help new people get into security and ramp up for SOC work. Feel free to follow along or send the course to new ppl: https://t.co/rI0UROZ1ZF
Folks, my next Pay What You Can SOC class starts March 28th.
Many of you are in the security space. If you can pass the class on to someone you know who needs to get past the gates of infosec, I would appreciate it.
https://t.co/DloQ3Tqdwy
🚨🚨WARNING 🚨🚨 We have confirmed that #Emotet is dropping CS Beacons on E5 Bots and we have observed the following as of 10:00EST/15:00UTC. The following beacon was dropped: https://t.co/imJDQTGqxV Note the traffic to lartmana[.]com. This is an active CS Teams Server. 1/x
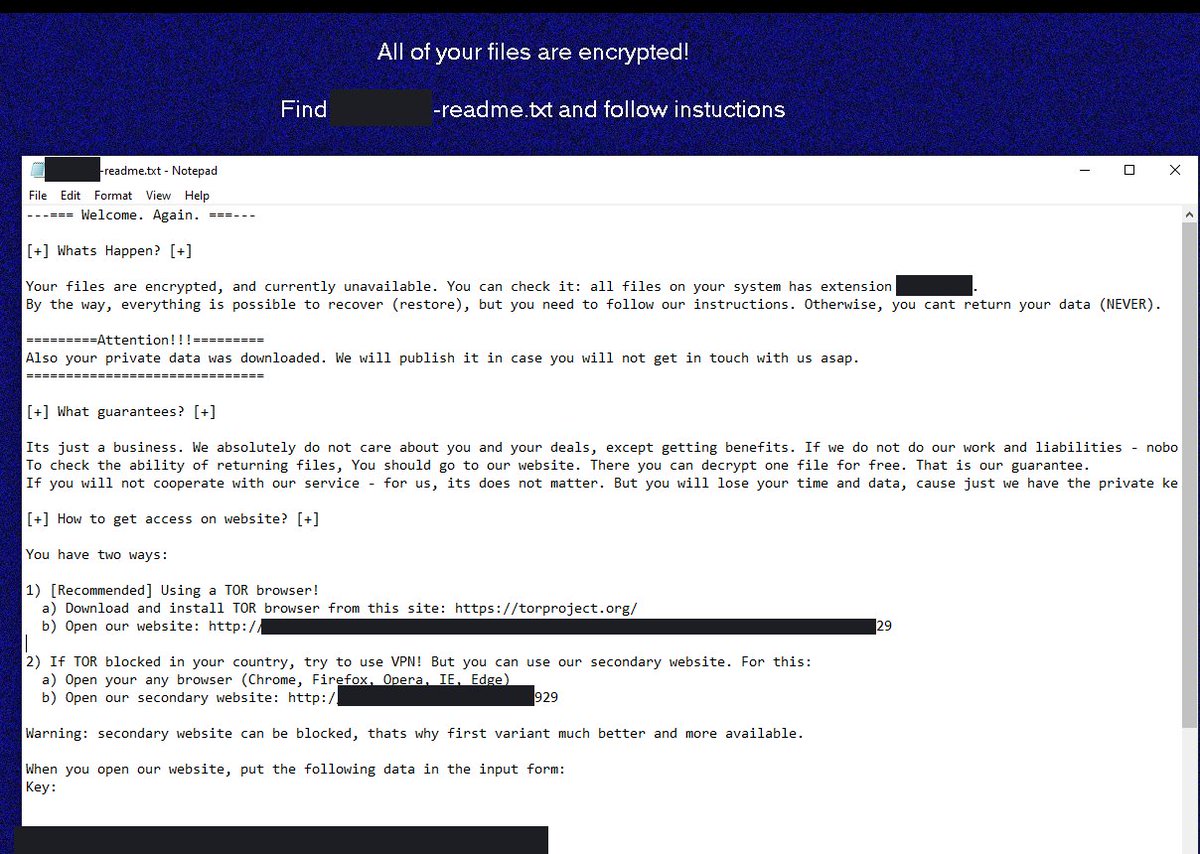
Looks like during the takedown of parts of the REvil infrastructure several months ago LEA got their hands on the secret key required to decrypt the ransom note key blobs which include the secret key for the system. Great news for older victims who can decrypt their files now. :)
Mass exploitation of Atlassian Confluence CVE-2021-26084 is ongoing and expected to accelerate. Please patch immediately if you haven’t already— this cannot wait until after the weekend.
One of the developers for Babuk ransomware group, a 17 year old person from Russia, has been diagnosed with Stage-4 Lung Cancer. He has decided to leaked the ENTIRE Babuk source code for Windows, ESXI, NAS.
You can download the Babuk source here: vx-underground[.]org/tmp/
CrowdStrike has released a new X-Ways Forensics X-Tension to the #DFIR community, allowing users to harness the power of X-Ways to run YARA scans natively from within the tool to save time + find evil faster. Read more and download it from our GitHub page: https://t.co/MePMzEKtrt
Hey all. My next Pay What You Can (PWYC) SOC Core Skills class is coming up this August. If you, or someone you know, is getting started in IT or security it is a great place to start.
https://t.co/4igtVmgKoV
I highlighted the interview talking about my new book “Adversarial Tradecraft in Cybersecurity” from the episode of Infosec Decoded with @sambowne this morning. Hope you all find the discussion valuable and checkout the book https://t.co/FUNqfW1fS9
Attackers have targeted US critical infrastructure several times over the past few years, putting at risk electrical grids, pipelines and water supply systems. Here are a few ways in which we feel these organizations can prep for the next #ColonialPipeline https://t.co/r6P8LvFZzy
Excellent article on the User Access Logging artifact from my team at @CrowdStrike. I've found it extremely useful in multiple cases and am happy to share it with the #infosec community! https://t.co/mOhUhNqYNT
By popular request, my workshop on Cobalt Strike detection is now available as a free on-demand recording. Sign in with your SANS account (the button says "Get Registered.") You will also find links to download the slides and labs. Enjoy!
https://t.co/yX5NKYJVLh
🚨 Critical RCE bug in Pulse Secure (CVE-2021-22893)
⚠ 0day was exploited in the wild by APTs
Report:https://t.co/wmDCdmWv04
Advisory:https://t.co/mWMUqBZFqd
JUST RELEASED: Emergency Directive 21-01 calls on all federal civilian agencies to review their networks for indicators of compromise and disconnect or power down SolarWinds Orion products immediately. Read more: https://t.co/VFZ81W2Ow7
#Emotet's had quite the year. And after a period of silence, it's back now bigger than ever. Here's what you need to know about where the infamous #botnet is at now #cybersecurity#threats https://t.co/F7dxO2IJzL