I’m excited to announce that OdinEye is now in public beta! Thanks to everyone who has tested it out so far.
I’m building OdinEye with one mission, to provide a definitive answer to the question "Is this computer compromised?"
Launch it from a one-liner and visualise the scan in real-time in your browser. No install, no setup.
Join the beta at https://t.co/mOwoTehvPy
Fifteen years ago, I co-founded MDSec. Today, that journey comes to an end.
In that time, we’ve written books, spoken at almost every major conference, and discovered and exploited more 0-days than I could count. We’ve hacked banks, $tock exchanges, tech giants, frontier AI orgs and all manner of companies in between. We’ve jackpotted ATMs, intercepted money from payment systems, compromised mainframes, beaconed mobile devices and got r00t more times than I can remember.
A huge thank you to everyone on the MDSec team and all the MDSec alumni, who helped make it such a wild ride. I’m immensely proud of what we built. And to all our customers, past and present, thank you for the trust and opportunities you gave us.
I’m excited for the next chapter. If the next 15 years are anything like the last, it’s time to strap in.
I just released the first public version of @BintracerLabs, a malware-analysis sandbox focused on macOS.
Bintracer can:
- Detonate Mach-O binaries, app bundles, and dylibs
- Extract DMG and PKG files
- Analyze JXA, AppleScript, Python, Perl, and shell scripts
This project is still early, but I can't wait to see what y'all think!
For more than 2 years now the Red Team at MDSec have been running riot in environments by abusing ServiceNow. Today we are releasing more of our research in this space:
https://t.co/li3KP1zgWP
The TLDR - popping ServiceNow is one of the most impactful things you can do.
I’m excited to announce that OdinEye is now in public beta! Thanks to everyone who has tested it out so far.
I’m building OdinEye with one mission, to provide a definitive answer to the question "Is this computer compromised?"
Launch it from a one-liner and visualise the scan in real-time in your browser. No install, no setup.
Join the beta at https://t.co/mOwoTehvPy
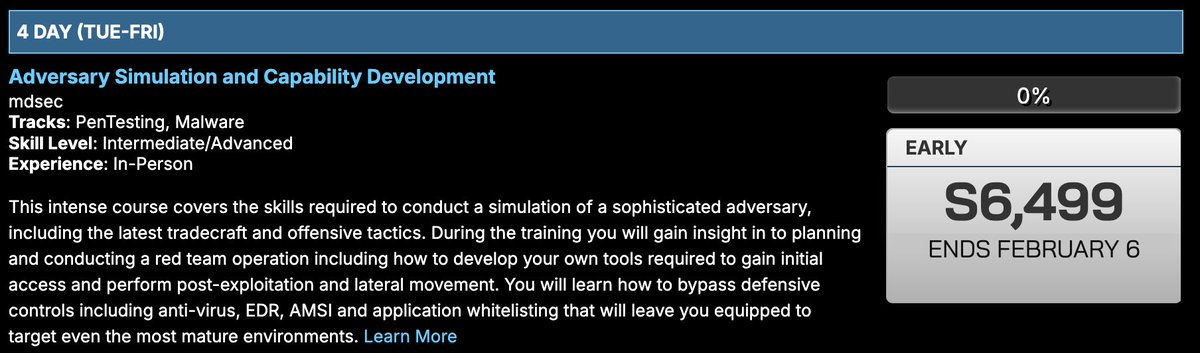
We're bringing the latest and greatest red team TTPs to @BlackHatEvents this year in our Adversary Simulation and Capability Development training. Learn from seasoned red teamers @domchell and @_batsec_, with fresh content updated for 2026! 🔥 https://t.co/8RSHoMyQ5S
This week we launched our Offensive Security Accelerator - a fast track training programme for those looking to start their cyber security careers... if you're in the UK and a graduate or looking to pivot in to offensive security, here's how... https://t.co/CZ2463KqW3
@MDSecLabs will be running our Red Team Capability Training out in #BlackHatUSA26 again this year. This year the course features a big refresh, with a bunch of new additions on the latest evolving techniques!
Early bird discounts end this month! @BlackHatEvents
https://t.co/l3uAga4TS5
This year we're bringing our Adversary Simulation and Capability Development training to Asia for the first time with @BlackHatEvents#blackhatasia26 https://t.co/ipPoV0UwvJ
If you want some hands on red teaming and tool development training from seasoned experts (@_batsec_ ), the early bird pricing is now available!