Mirage Kitten expands operations in the Middle East & Africa using #NightLedger.
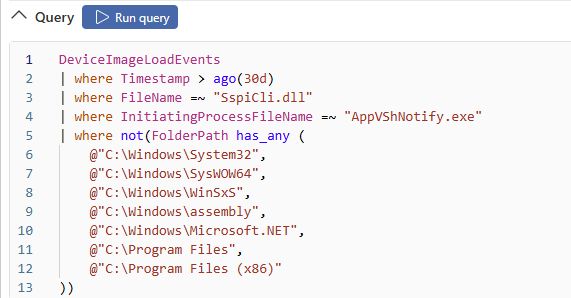
The backdoor abuses DLL search‑order hijacking by side‑loading a malicious DLL.
High‑confidence signal #defender#KQL#hunting
APT Intelligence
Threat Nexus
https://t.co/ViGL8Pb8Wb
APTMap
https://t.co/DoCFCYlTZm
Threat Group Cards: A Threat Actor Encyclopedia
https://t.co/GwOJeGmpSW
Global Threat Map
https://t.co/dgdoRLcbue
APT & Threat Actor Resources
https://t.co/n8HWwOsNBb
#cti#cybersecurity
@iamTiresias@cyb_detective Threat Intel without an actionable is just a fancy news. 🙌
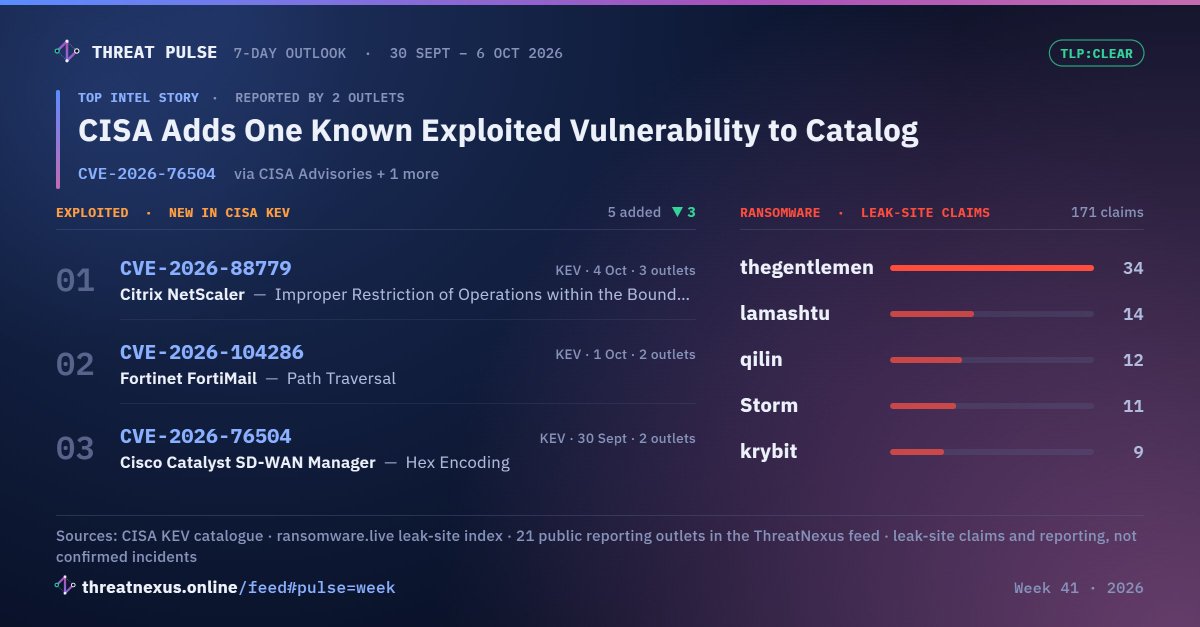
#ThreatNexus ensure analyst get the whole lifecycle to utilise intel in term of IOCs, TTPs, hunting and detection engineering.
Feed tab provides real freshness on tactical intel. APTs freaheness is the goal.
Thanks @cyb_detective#ThreatNexus is a community project built to deliver strategic, operational & tactical nation-state APT intel in one place.
More coming soon. Would love reviews & contributions to make it even better!💛
#CTI#ThreatInt#ThreatHunting