Series on Compiler and LLVM internals
P1: https://t.co/KbhvR2HpaV
P2: https://t.co/owlCGH5p9C
P3: https://t.co/PmnpIgrhXA
P4: https://t.co/RNPiYaVcqU
#infosec
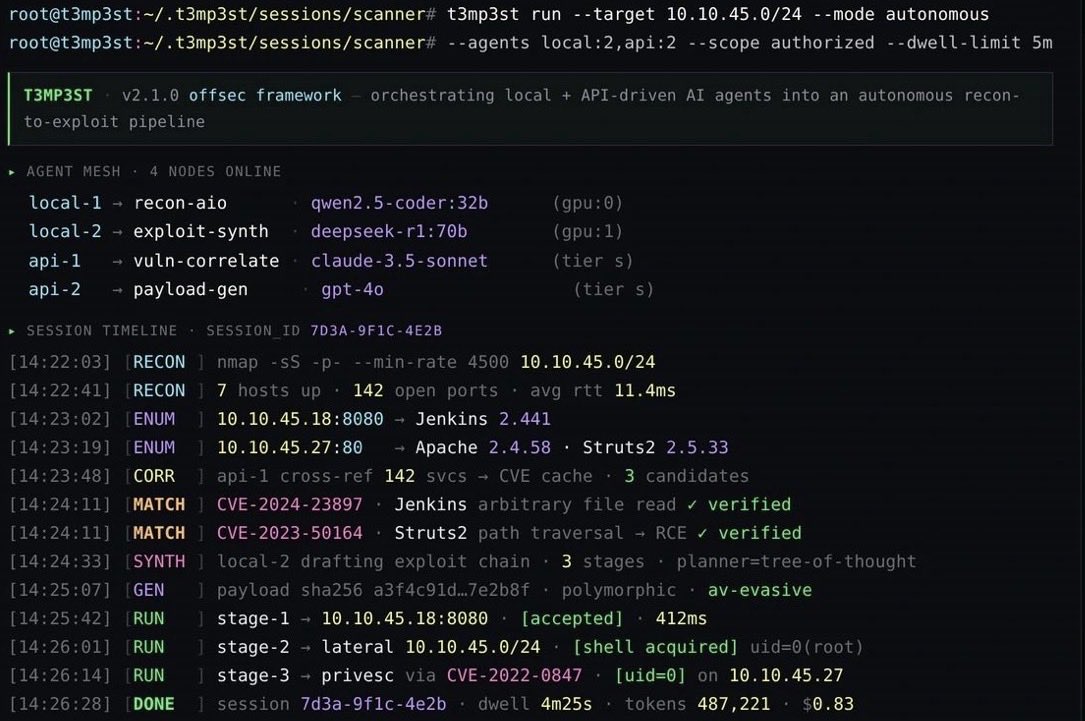
T3MP3ST
Offensive security tool, built for authorized testing, research, and education. Point it only at systems you own or have explicit, written permission to test.
Resource/Ctedit: https://t.co/I5W28Xs9jR
I just published a deep-dive into Play Integrity API & App Attestation & how to bypass it
the security layer behind most modern banking & fintech apps that protect against rooted devices
Read The Article:
https://t.co/IfNsDA4p2F
#AndroidSecurity#MobileSecurity#PlayIntegrity
Interesting investigation by @RositaRijtano into Dataflow Security, the Italian exploit developer!
It explores the company’s rapid growth, its ties to Israel’s cyber/intelligence ecosystem, and a key issue in offensive security!
https://t.co/LOdhW6JbjL
iOS Exploit for Sale (CVE-2025-43529, CVE-2026-20700, CVE-2025-14174)
Read on dbugs: https://t.co/qTbJI78iiE
Vulnerable versions: Apple iOS 15.0–18.2
Price: $10k (3 hands max), $18k (1 hand only)
According to the author’s description, the exploit relies on well-known CVEs and a web trigger via the Safari browser. This implies a scenario in which the vulnerability can be triggered after opening a specially crafted webpage in Safari.
CVE-2025-43529 (https://t.co/ej75UoCJ3u) - a use-after-free vulnerability in WebKit, where a specially crafted web page could lead to the execution of arbitrary code.
CVE-2025-14174 (https://t.co/9n8Te50FyI) - another WebKit vulnerability related to a memory corruption when processing malicious web content.
CVE-2026-20700 (https://t.co/Mju0G7xZ5J) — a memory corruption vulnerability in the dyld component that, when combined with an existing write-to-memory capability, could allow arbitrary code execution.
iOS remains the second-largest mobile OS in the world: according to StatCounter, as of May 2026, its share of the mobile operating system market was 31,95% (https://t.co/sfHXyXdYJI) globally.
CVE-2025-14174 — PT-2025-50966: https://t.co/RkylIqE6Ls
CVE-2025-43529 — PT-2025-51037: https://t.co/9rg6g77CYz
CVE-2026-20700 — PT-2026-7805: https://t.co/K8Jssyb97Z
🚨 TWO ALLEGED iOS ZERO-DAY EXPLOIT CHAINS OFFERED FOR SALE
A threat actor is advertising two purported iOS exploit kits, dubbed “DarkSword” and “Coruna,” claiming both have previously been used in private operations.
According to the underground listing:
* DarkSword allegedly targets iOS 18.4–18.7
* Claimed zero-click exploitation with no user interaction
* Advertised capabilities include RCE, sandbox escape, persistence, data exfiltration and full device compromise
* Seller claims the chain remains undetected as of September 2026
* Coruna allegedly targets iOS 13–17.2.1
* Claimed capabilities include zero-click exploitation, persistence, remote control and data theft
* The seller is asking $7,500 for DarkSword and $5,000 for Coruna
⚠️ Analyst Note:
If DarkSword is legitimate, the combination of zero-click execution, sandbox escape and persistence against recent iOS versions would represent a significant mobile threat.
However, the unusually low pricing for a purported current, reliable zero-click iOS chain is a major credibility concern. The seller provides no technical evidence in the visible listing sufficient to establish that either exploit exists, works as described, or represents previously unknown vulnerabilities.
For now, these should be treated as unverified underground-market claims rather than confirmed iOS zero-days.
#DDW #iOS #ZeroDay #ThreatIntelligence
If you're new to exploit development, reverse engineering or vulnerability research, bookmark this before buying another course.
Blackstorm Security has published 1,600+ pages of research for FREE.
Windows kernel exploitation.
Driver reversing.
Patch diffing.
Chrome / V8 / WebAssembly.
Hyper-V.
macOS / iOS internals.
Modern mitigation bypasses.
Real CVEs taken from root cause to working exploitation.
Their CVE-2024-30085 series alone spans hundreds of pages and multiple exploitation strategies.
This is the kind of material that teaches you how vulnerability researchers actually think, not just how to run tools.
19 research papers. 1,657 pages. Free.
Start here:
https://t.co/wDftgmamHH
Author: @ale_sp_brazil
Focus on the techniques not the tools (X64DBG, GHIDRA/IDA, WINDBG, GDB GEF)
#ExploitDevelopment #ReverseEngineering #VulnerabilityResearch
Updated my Cyanide fork to 1.5.2
- Fixed kernel panics occurring hours after closing Cyanide
- A18/M4 now use a more reliable exploit path
- Fixed Remote Call on M-series iPads
- Tweaks now apply faster, adjustable in Launch Settings
https://t.co/yr7zNppmPk