🚨🗣️ Zinedine Zidane Proposes Separate Awards for Club and International Football
“The Ballon d’Or organisers need to be more consistent with their decisions.
They used La Liga performances to award Lamine Yamal the Kopa Trophy over Pau Cubarsí, relied on World Cup performances to award Unai Simón the Yashin Trophy over David Raya, ignoring a whole season of club football and used Bundesliga performances to award Harry Kane the Gerd Müller Trophy over Kylian Mbappé, despite Mbappé's incredible scoring record.
They also prioritised Champions League success when selecting Club of the Year, yet placed greater emphasis on international tournament success when choosing Coach of the Year over managers who delivered outstanding results at club level.
So, which criteria actually matter: domestic league performances, Champions League success or international tournaments?
If the organisers cannot apply consistent standards across every category, they should separate club football awards from international football awards.
Players and managers deserve recognition based on clear, fair criteria, not standards that appear to change from one award to another. The Ballon d’Or needs reform.
#BallonDor
microsoft quietly open-sourced one of the best ai data analysis tools out there.
it's called data-formulator.
connect any source, csv, postgres, bigquery, even a live url, then build charts with a mix of drag-and-drop and plain english.
the ai agent writes the sql and transforms underneath and hands back a chart you can actually edit, not a code dump.
> drag fields onto x/y/color and it builds the chart
> anchor a cleaned result so follow-ups don't drift back
> branch any chart to explore a variation
> connect live data with auto-refresh
bring your own model key and run it locally.
dsregcmd /status answers more WHfB questions than any portal.
It also dumps 60+ fields across 7 sections with zero explanation - so most admins read the 3 lines they recognise and guess at the rest. Here’s the field-by-field legend nobody gives you 🧵 #WHfB#EntraID
Installed PrivacyNotes on your Mac from the App Store? That was the iPad build, so it renders at iPad size. We have switched that off.
The real Mac app: https://t.co/hLpKLJGkeN
Same recovery phrase, same notes. Pro carries over.
I wrote a new Task Manager that runs natively on Windows, macOS, and Linux. You can get it now at https://t.co/OZcq1axGTb ... but why?
Well, it started as an argument over whether you could vibe code Microsoft Word today. I didn't think so. But I figured... maybe something simpler like Task Manager. But you can't just tell Claude, "Hey, write a task manager!" Well, you can, but it'll be hot garbage.
Then my kid blew out his appendix and needed surgery, so I had a couple of days in waiting rooms to tinker with the idea. I broke out my new M5 MacBook Air, and I put together a 107-page spec, like I was some caffeine-addled PM from the 90s. Everything you could ever want to know about a task manager, how it works, what it should do, and what it should look like.
By the time he was out of the hospital, I had a rough app working. But then he started bleeding internally, needed emergency surgery and a blood transfusion. Happy to say he's all better now - but suffice to say I had the rest of the week to tinker as he healed.
But why write a Task Manager? Because when I wrote the original in '95, it was on a P90 or something equally weak. Updating, scrolling, and painting without using more than a percent or two of the CPU was the modest goal.
Now that we have 5 GHz CPUs and GPUs to help, why not push the limits? Animate everything at 60Hz, instead of once a second. History mouse tracking, a summary page, and all the features I would have added then if the hardware had allowed it.
My autism leads me to embrace neon and high contrast in a way that's not to everyone's taste, so there's a saturation slider to control the color. But this one goes to 11.
You can also select from a bunch of DEC VT220-inspired themes like Green Phosphor, Amber, or White. And I added Blue to match my VSCode theme!
The code is fully native: Direct2D/DirectComposition on Windows, UIKit on Mac, and Qt on Linux. The UI communicates with a shared CPP core, which branches out to platform-specific helpers. There's NO electron, HTML, JSON, etc.
Thanks to David and Rutger for their help along the way, I couldn't have done it this quickly on three platforms without them!
If you've got some cycles to spare, give it a try and let me know if you run into any issues!
https://t.co/OZcq1axGTb
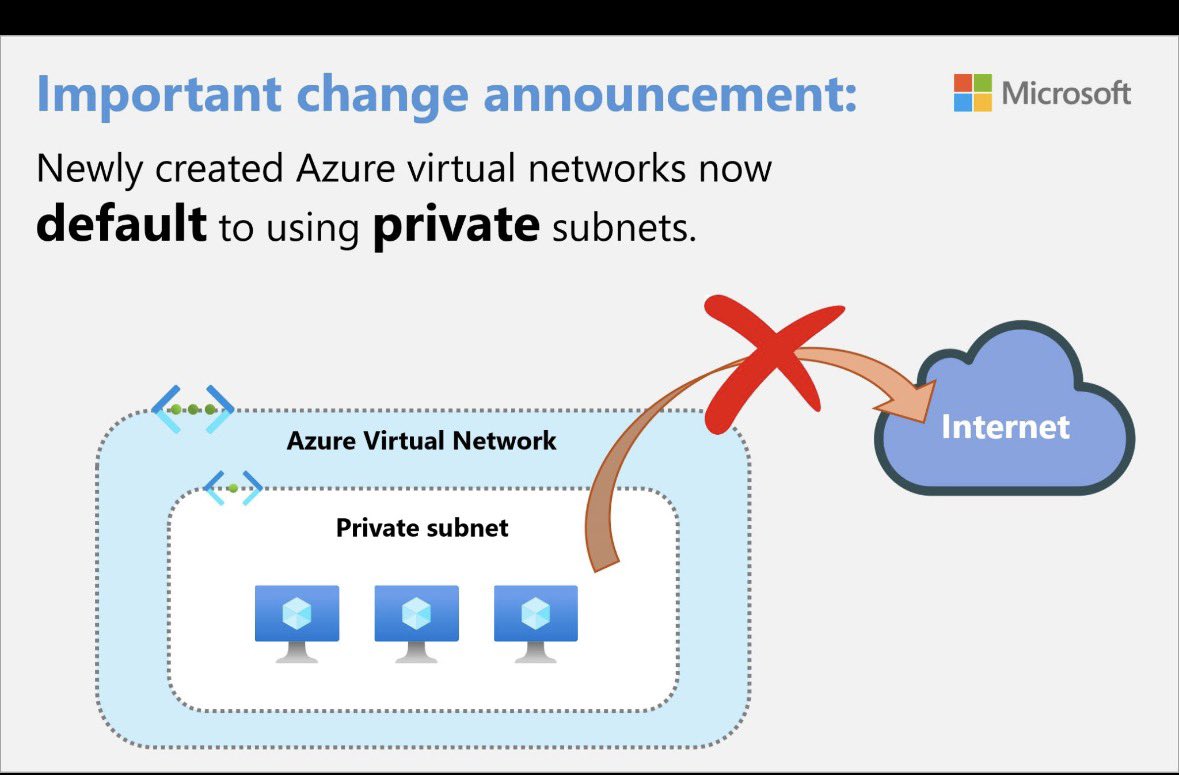
Your new Azure VM can't reach the internet.
That's not a bug → it's the new default.
After March 31, 2026, every new VNet ships private by default.
No NAT Gateway = no apt update, no Windows Update. Nothing. 👇
Why Microsoft killed default outbound:
❌ IP owned by Microsoft — could change anytime
❌ No ICMP, no fragmented packets
❌ Inconsistent across NICs & VMSS
❌ Zero Trust violation by design
Your 4 fixes (in order):
✅ NAT Gateway ← do this
Standard LB + outbound rules
Instance-level public IP
Firewall/NVA + UDR
Why NAT Gateway wins:
→ 64,000 SNAT ports per IP (vs ~64)
→ Scales to 1M+ ports
→ You own the egress IP
→ Attach once per subnet. Done.
The migration (don't skip step 4):
Find affected NICs → Advisor → Operational Excellence
Attach NAT Gateway to the subnet
Set defaultOutboundAccess = false
Stop + deallocate the VMs ← everyone forgets
Start. Verify egress IP.
Gotchas:
⚠️ Old Terraform AzureRM → still permissive
⚠️ LB backend pool by IP → leaks default outbound
⚠️ Windows Activation/Update → silently fails
The lesson:
Implicit defaults feel free. They're never free.
You pay at 3 AM when an IP rotates or SNAT ports dry up.
Explicit > implicit. Always.
One KQL query you should have saved in your toolkit (most don’t):
SigninLogs
| where TimeGenerated > ago(24h)
| where ResultType == 0
| where AuthenticationRequirement == "multiFactorAuthentication"
| where RiskLevelDuringSignIn in ("high", "medium")
| extend DeviceId = tostring(DeviceDetail.deviceId)
| summarize
SigninCount = count(),
IPs = make_set(IPAddress),
RiskDetails = make_set(RiskDetail),
Apps = make_set(AppDisplayName),
DeviceId = any(DeviceId),
TimeGenerated = max(TimeGenerated)
by CorrelationId, UserPrincipalName, RiskLevelDuringSignIn
| where array_length(IPs) > 1
or isempty(DeviceId)
| project TimeGenerated, UserPrincipalName, IPs, Apps, RiskLevelDuringSignIn, RiskDetails, CorrelationId, DeviceId, SigninCount
| order by RiskLevelDuringSignIn desc, SigninCount desc
This surfaces successful MFA sign-ins that Entra ID still flags as medium/high risk — the exact pattern many default analytics rules miss because “MFA passed = safe.”If it returns results, investigate immediately.
High risk + MFA satisfied + proxy indicators (multiple IPs on the same CorrelationId or an empty DeviceId) is a classic AiTM phishing signal.
Save it. Run it daily. You’ll catch stuff your alerts don’t.
👋 Here's a quick birds eye view of Microsoft Agent 365 licensing
Enjoy!
Disclaimer: I'm not a licensing person. Please refer to the official licensing FAQ for details https://t.co/fdlvvskauh
Microsoft will release DNSSEC Enablement Wizard for Exchange Online!
To simplify the adoption of SMTP DANE with DNSSEC, Microsoft will release a DNSSEC Enablement Wizard in the Exchange Admin Center in Q3 of calendar year 2026.
This guided workflow includes:
- Validates DNS prerequisites
- Provisions the customer-specific DNSSEC‑capable mail flow endpoint
- Reduces configuration risk during MX transition
- Prepares the domain for SMTP DANE adoption
If you wish to fully enforce SMTP DANE with DNSSEC, you can already do so. However, it requires PowerShell.
Learn more:
https://t.co/vYqLTLR6Lq
PS: I will make sure to announce this when it's available. Connect to stay up to date!
#Microsoft365 #ExchangeOnline #Cybersecurity
If you’re an IT admin and you’ve never had your internal environment pentested and can’t afford one right now, do this instead:
1. Run Locksmith - fix anything that’s a High risk
2. Run ADeleginator - make sure everyone, authenticated users, domain users and domain computers doesn’t have any unsafe permissions
3. Run ScriptSentry - check for credentials in logon scripts
4. Run PingCastle - check the control paths section. It’s like bloodhound. Look for non-admins that have control paths
If you do this, your environment will be much better when you’re done fixing everything.
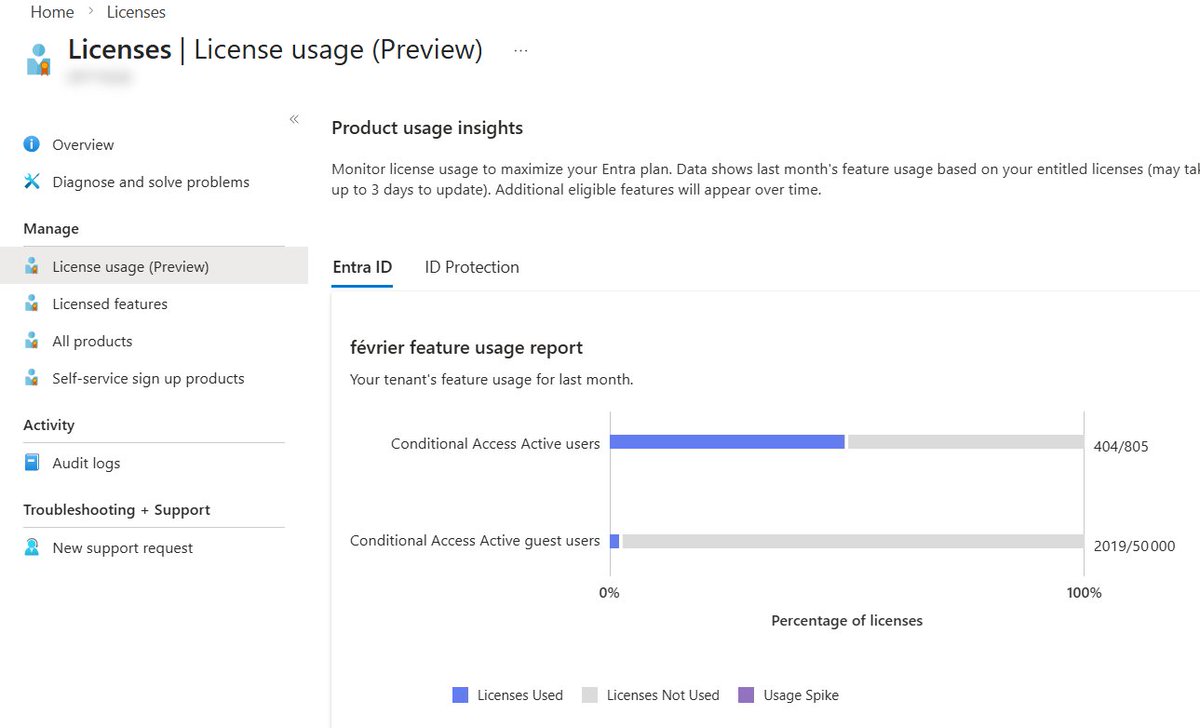
📣 For years, Microsoft has been fairly permissive with Entra ID P1/P2 feature usage: you could buy a single license and it would effectively “unlock” features for the entire tenant.
This creates a lack of visibility to know whether tenants are complying with licensed feature usage limits, such as:
* Conditional Access (minimum Entra ID P1)
* Risk-based policies (Entra ID P2)
Microsoft has updated its page to track license usage and identify “spikes” (overages).
🔺 Where to find it:
Entra ID portal > Licenses > License usage (Preview)
Direct link: https://t.co/jWqsSozeRU
The real question: will Microsoft eventually start going after the €€ from tenants that exceed their limits?
Wait and see…
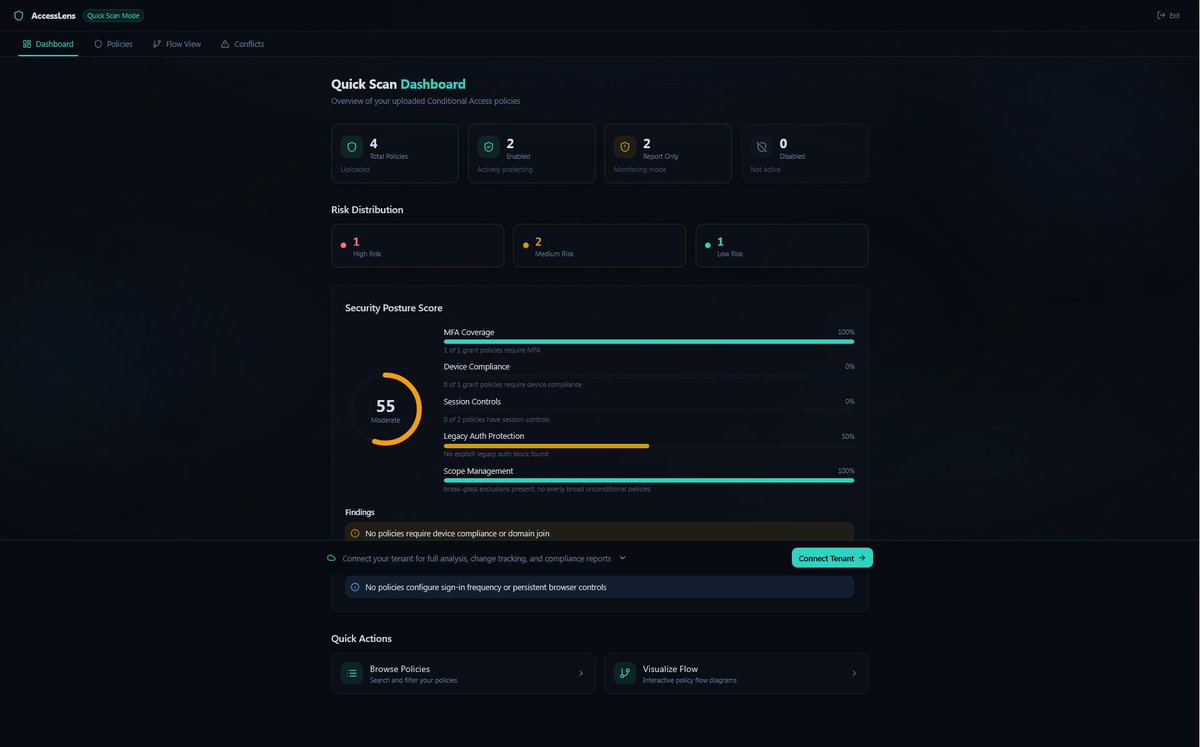
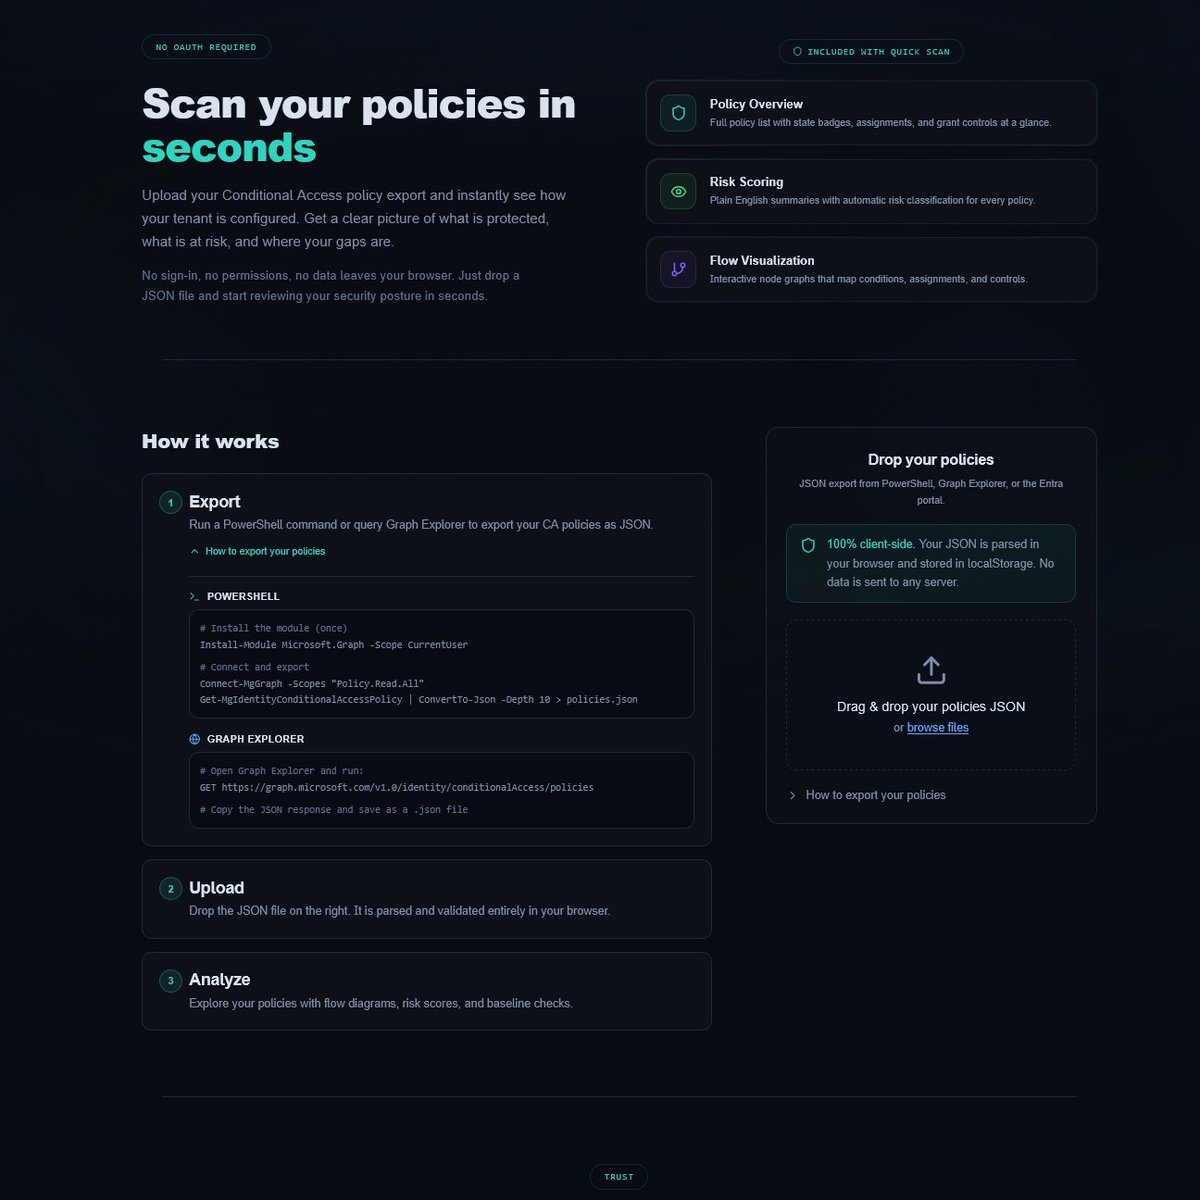
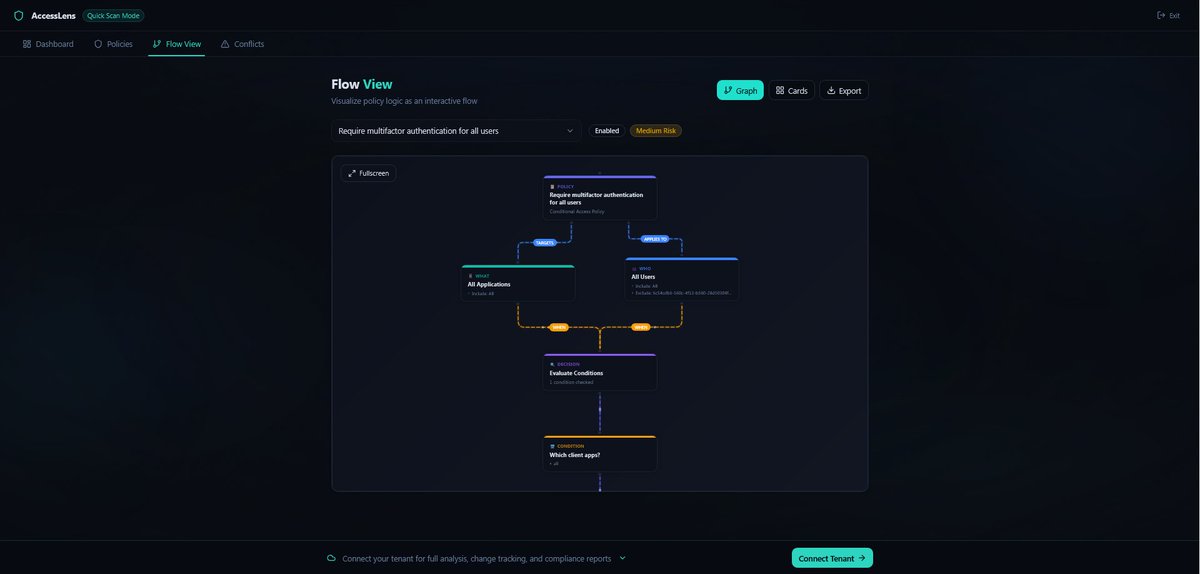
Audit your Conditional Access policies in 60 seconds:
1️⃣ Export your CA policies as JSON from Microsoft Entra
2️⃣ Upload them to AccessLens Quick Scan
3️⃣ Get an instant security breakdown
You’ll see:
🔍 Policy conflicts
⚠️ Security gaps
📊 Risk scoring
📋 Compliance mapping
No sign-in. No permissions. No data leaves your browser.
🔗Free at https://t.co/7Gs95iNXm5
#MicrosoftEntra #ConditionalAccess #InfoSec #ZeroTrust
🔒 Secure Bits 💡
𝗘𝘅𝗰𝗵𝗮𝗻𝗴𝗲 𝗪𝗲𝗯 𝗦𝗲𝗿𝘃𝗶𝗰𝗲𝘀 (𝗘𝗪𝗦) 𝗶𝗻 𝗘𝘅𝗰𝗵𝗮𝗻𝗴𝗲 𝗢𝗻𝗹𝗶𝗻𝗲 𝗶𝘀 𝗼𝗳𝗳𝗶𝗰𝗶𝗮𝗹𝗹𝘆 𝗴𝗼𝗶𝗻𝗴 𝗮𝘄𝗮𝘆.
Microsoft will start disabling EWS in Exchange Online from October 1, 2026, with 𝗳𝘂𝗹𝗹 𝗮𝗻𝗱 𝗽𝗲𝗿𝗺𝗮𝗻𝗲𝗻𝘁 𝗿𝗲𝘁𝗶𝗿𝗲𝗺𝗲𝗻𝘁 𝗼𝗻 𝗔𝗽𝗿𝗶𝗹 𝟭, 𝟮𝟬𝟮𝟳.
If any of your apps still rely on EWS, they 𝑤𝑖𝑙𝑙 break unless you act.
This often goes unnoticed because EWS is mostly used by background services, not end users — until workflows suddenly stop.
🤔 𝗪𝗵𝘆 𝘁𝗵𝗶𝘀 𝗺𝗮𝘁𝘁𝗲𝗿𝘀
EWS is still widely used for mailbox, calendar, and service-to-service integrations.
When it breaks, the impact is operational and visible — missing emails, failed automations, broken syncs — but troubleshooting often starts in the wrong place.
Migration is rarely a checkbox. It usually requires application changes and testing.
🧠 𝗧𝗼 𝗴𝗶𝘃𝗲 𝘆𝗼𝘂 𝗺𝗼𝗿𝗲 𝗰𝗼𝗻𝘁𝗲𝘅𝘁
Microsoft is enforcing the long-announced shift from legacy Exchange APIs to Microsoft Graph.
- 📆 October 1, 2026 - EWS will be blocked by default unless explicitly allowed by tenant admins, they can re-enable this setting temporarily
- 📆 April 1, 2027 - EWS access in Exchange Online will be permanently removed - no re-enablement, no exceptions
- on-premise Exchange Server is not affected, this change applies only to Exchange Online
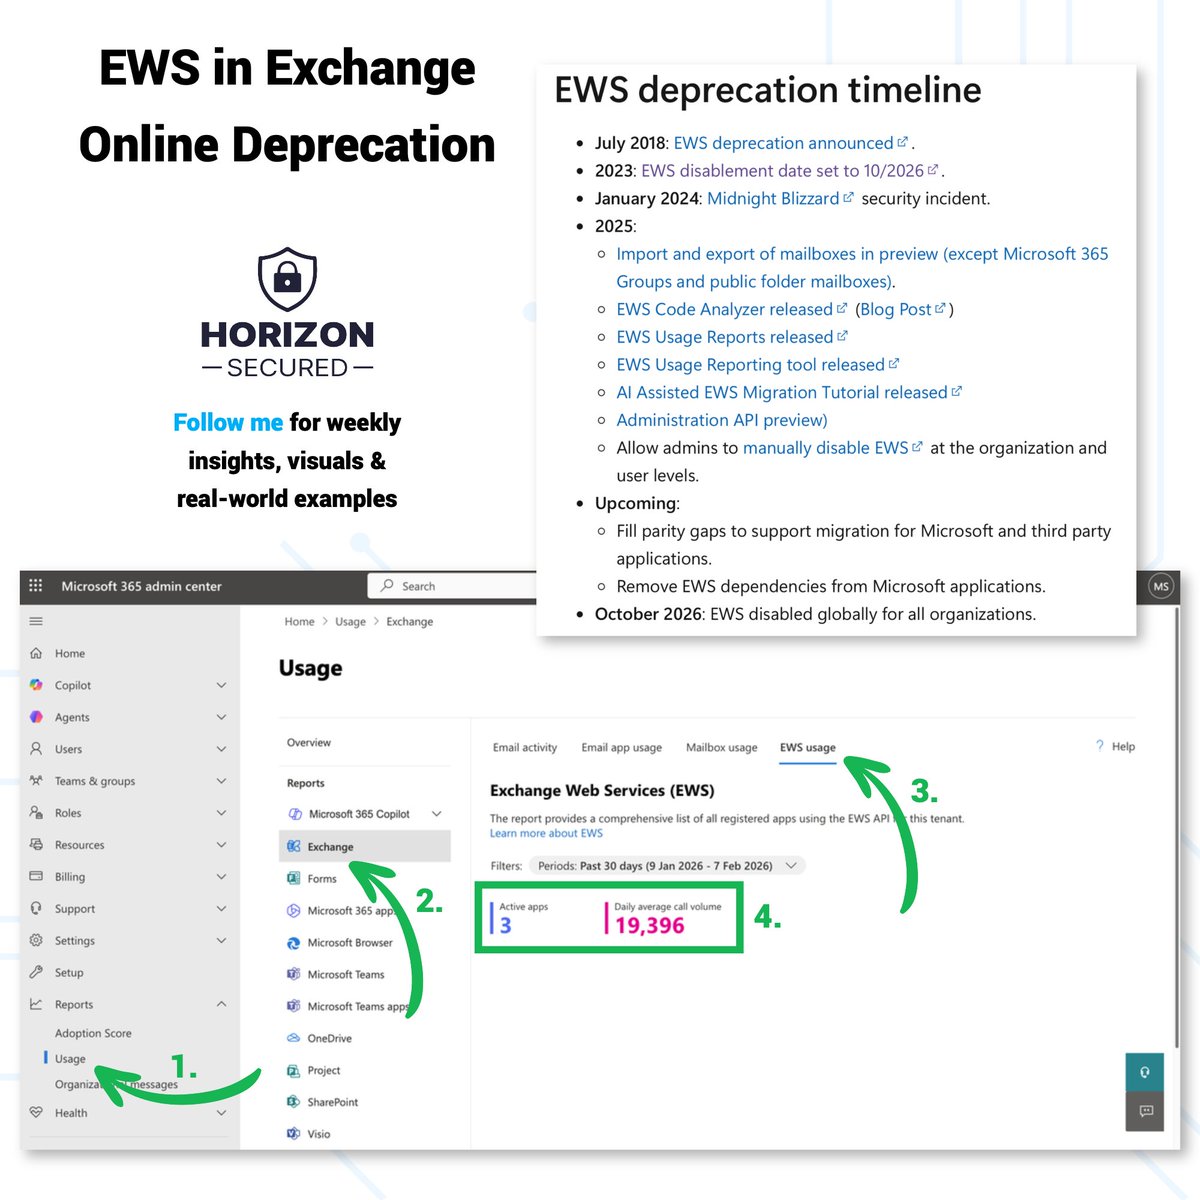
🛠️ 𝗜𝗱𝗲𝗻𝘁𝗶𝗳𝘆 𝗘𝗪𝗦 𝘂𝘀𝗮𝗴𝗲 𝗻𝗼𝘄
Use the built-in report to see all apps and identities using EWS in your tenant:
- Microsoft 365 admin center → 𝗥𝗲𝗽𝗼𝗿𝘁𝘀 → 𝗨𝘀𝗮𝗴𝗲 → 𝗘𝘅𝗰𝗵𝗮𝗻𝗴𝗲 → 𝗘𝗪𝗦 𝘂𝘀𝗮𝗴𝗲
🛠️ 𝗣𝗹𝗮𝗻 𝗺𝗶𝗴𝗿𝗮𝘁𝗶𝗼𝗻 𝘁𝗼 𝗠𝗶𝗰𝗿𝗼𝘀𝗼𝗳𝘁 𝗚𝗿𝗮𝗽𝗵
Microsoft Graph provides near-complete API parity, but migration usually involves:
- Code changes
- Permission model updates
- Regression testing
🛡️ 𝗨𝘀𝗲 𝘁𝗵𝗶𝘀 𝗮𝘀 𝗮 𝘁𝗲𝗺𝗽𝗼𝗿𝗮𝗿𝘆 𝘀𝗮𝗳𝗲𝘁𝘆 𝗻𝗲𝘁
If EWS is still required after October 2026:
- Configure the AllowList
- Explicitly set 𝘌𝘞𝘚𝘌𝘯𝘢𝘣𝘭𝘦𝘥 = 𝘛𝘳𝘶𝘦
- Treat this as a short-term exception, not a long-term design
⚠️ 𝗜𝗺𝗽𝗼𝗿𝘁𝗮𝗻𝘁
Microsoft may run temporary “scream tests” before October 2026 to surface hidden dependencies.
If something suddenly breaks during those tests — that’s your warning sign.
Assume EWS exists somewhere in your tenant unless you’ve proven otherwise.
The earlier you identify and migrate dependencies, the cheaper and calmer this transition will be.
💬 𝗤𝘂𝗲𝘀𝘁𝗶𝗼𝗻 𝗳𝗼𝗿 𝗮𝗱𝗺𝗶𝗻𝘀
Do you know exactly which apps in your environment still rely on EWS — or would this retirement catch you by surprise?
𝘈𝘶𝘵𝘩𝘰𝘳 𝘰𝘧 𝘵𝘩𝘦 𝘱𝘰𝘴𝘵: @strnad10
#Microsoft365 #ExchangeOnline #EWS #MicrosoftGraph #SecureBits #HorizonSecured #CloudSecurity
R.I.P. GOOGLE FLIGHTS IN 2026.
R.I.P. BOOKING DOT COM IN 2026.
R.I.P. SKYSCANNER IN 2026.
$1,412 flight. I paid $186.
These 7 ChatGPT prompts quietly break airline pricing: