@CAF_Media Please update the regulations :
- Spectators have the right to invade the pitch, to assault stewards & to destroy equipment (the federation will pay a symbolic $)
- A towel is more protected than stadium equipment.
- Stealing a towel is equivalent to not finishing a final
- …
🚨Major #CyberAttack Alert 🚨
🇮🇹#Italy / 🇱🇾#Libya:
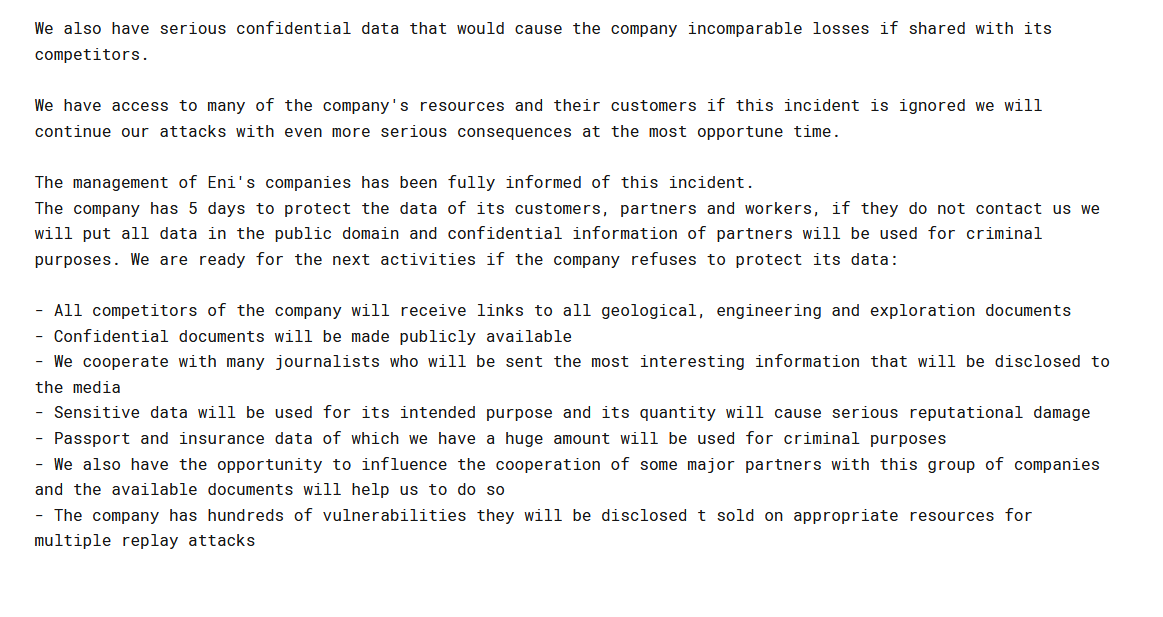
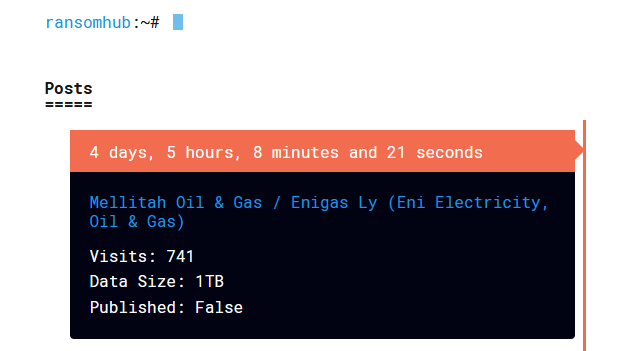
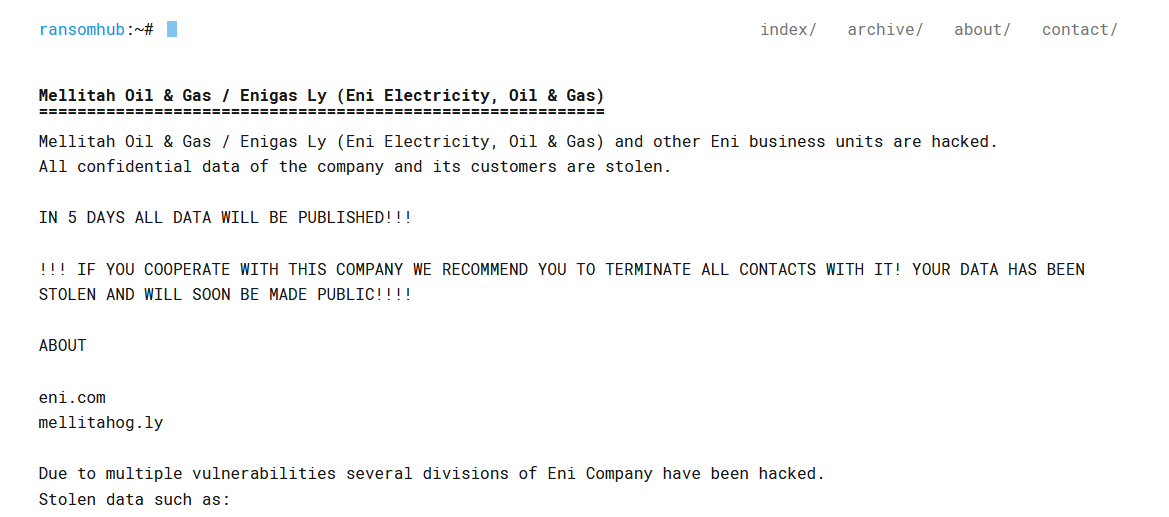
Mellitah Oil & Gas, the Libyan branch of Eni and other Eni business units allegedly compromised by RansomHub ransomware group.
"Mellitah Oil & Gas / Enigas Ly (Eni Electricity, Oil & Gas) and other Eni business units are hacked. All confidential data of the company and its customers are stolen," the hacking group states.
Several samples have been published, and the countdown for the ransom demand is set for May 4th.
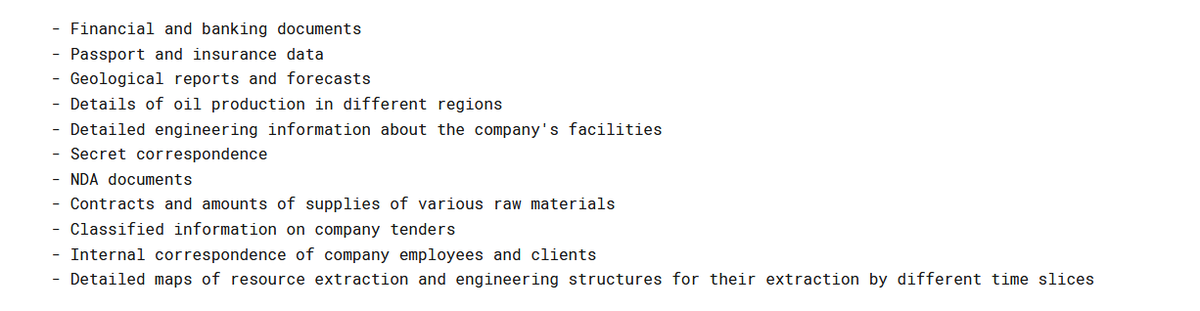
According to the post, the criminal group managed to exfiltrate 1 Terabyte of data including:
- Financial and banking documents
- Passport and insurance data
- Geological reports and forecasts
- Details of oil production in different regions
- Detailed engineering information about the company's facilities
- Secret correspondence
- NDA documents
- Contracts and amounts of supplies of various raw materials
- Classified information on company tenders
- Internal correspondence of company employees and clients
- Detailed maps of resource extraction and engineering structures for their extraction by different time slices
The confirmation or denial of these claims has yet to be verified.
#Ransomware
ChatGPT a désormais un corps physique.🤯
C'est le fruit d'un partenariat entre OpenAI et Figure.
🔹OpenAI assure la gestion du langage et du visuel.
🔹Les réseaux neuronaux de Figure fournissent des actions robotiques rapides et précises.
Vidéo réalisée sans trucage.👇
Working Windows and Linux Spectre exploits found on VirusTotal
Unprivileged users can use the exploits to dump LM/NT hashes on Windows systems and the Linux /etc/shadow file from the targeted devices' kernel memory.
[ ATTENTION ] Par décret la semaine dernière, @gouvernementFR vient de s’autoriser à ficher les personnes en fonction de leurs opinions politiques, leurs convictions philosophiques, religieuses ou leur appartenance syndicale. #surveillance
Thread ⤵️
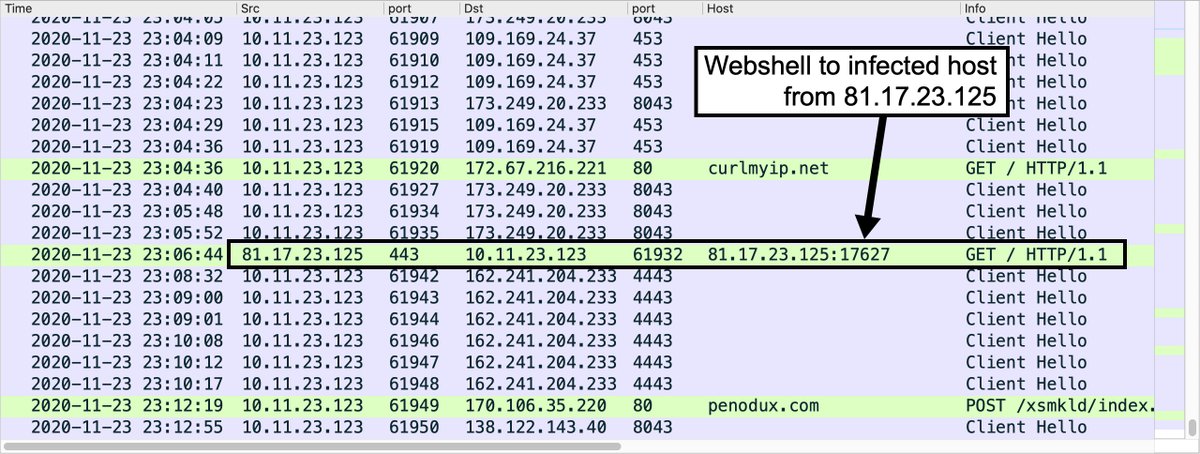
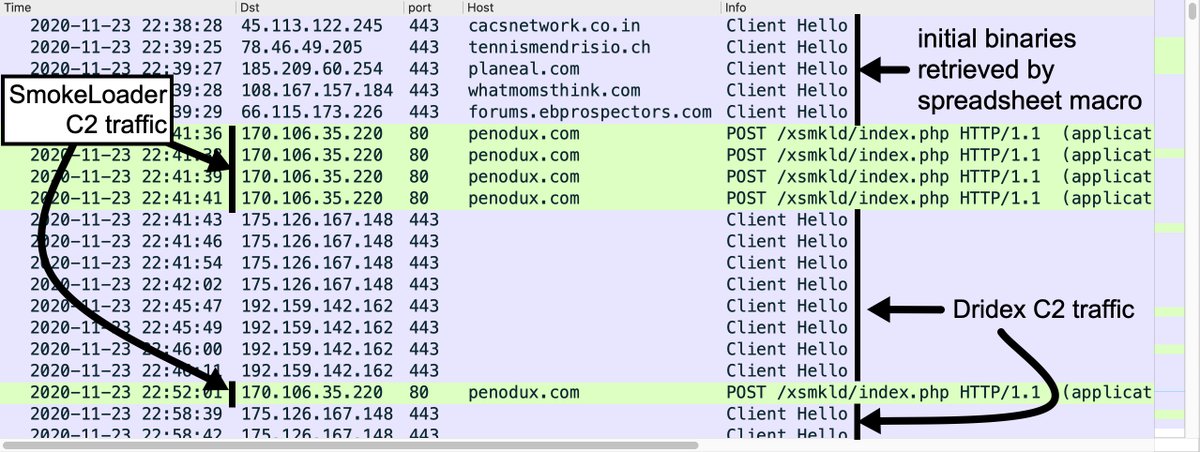
2020-11-23 (Monday) - #malspam pushing #Dridex uses #SmokeLoader, and we saw #webshell activity on our infected lab host. IOCs available at:
https://t.co/D4KgFSJPTR - includes info on getting the #pcap of the infection traffic
#Ransomware: une menace majeure⏭ énorme travail de @ValeryMarchive pour recenser les dernières attaques👏👏
🎁 Les données dont vous avez besoin pour aller chercher les budgets et changer la situation
❤️ la timeline ! Bientôt dans #panocrim? https://t.co/3WJYMOgC6J
🎁GIVEAWAY🎁
I will be giving away 3 copies of my PenTest+ Book. Retweet to win! Winners will be announced on Sunday afternoon (EDT). @PearsonITCert
#PenTest#Pentesting#BugBounty#bugbountytips
After days of implementing the new ANSSI rules, I'm finding out that 33 rules are not covered by any French paper.
That's far better than the 114 rules not covered by any framework in Germany and 83 for the US.
As a reminder, #PingCastle has 130 rules (for the moment)
I've mapped so far 21 ANSSI rules (baseline is 57 rules).
I've added a section about this in the rule report which is updated each time I push my commits.
Location:
https://t.co/zmVwNNTdbT
Note: This is a exact 1 to 1 mapping
Cortex-Analyzers 2.7.0 is out! Including 5 new analyzers for @anyrun_app, #OpenCTI, @abuse_ch MalwareBazaar, #CyberChef & a revamped, much faster @MISPProject Warning Lists analyzer.
It also includes a responder to create tickets in RT.
#FOSS#CTI#DFIR
https://t.co/myXGp5tgkZ