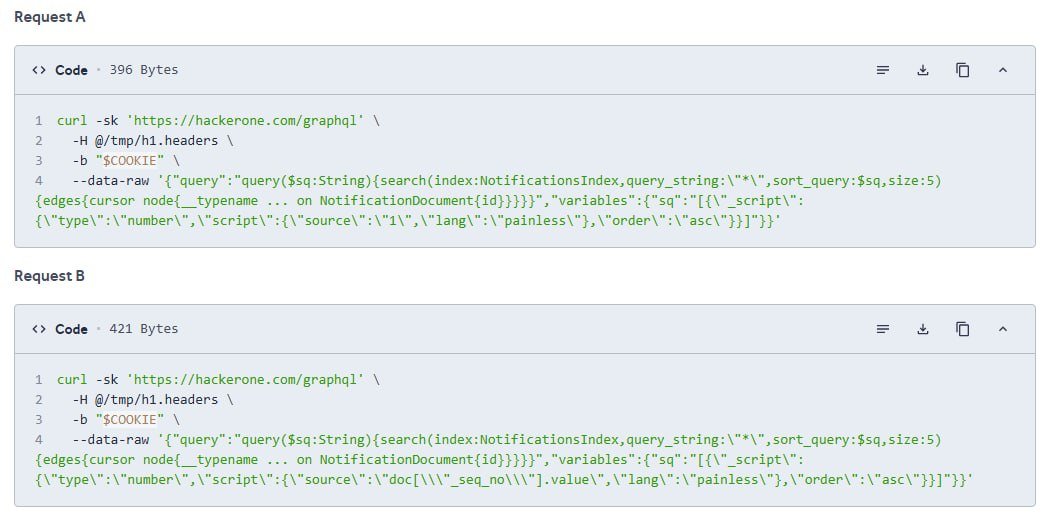
A $7,400 bug on HackerOne's GraphQL API — and the methodology is what makes it elite.
The bug: sort_query: String passed unsanitized into Elasticsearch → Painless script injection.
The 3-step proof:
1️⃣ Sent [{"id":"asc"}] → results sorted by ID → proves raw JSON parsing
2️⃣ Swapped script.source:
• "" → 500
• "unterminated" → 500
• "1" → 200
→ proves input reaches the Painless compiler
3️⃣ Compared "1" vs doc["_seq_no"].value → zero overlap in returned IDs → proves scripts execute per document
No data exfil. No DoS. Just clean, differential testing.
Payout: $7,000 + $400
Severity: High (8.8)
🔗 https://t.co/MX3tW8ZJ5X
#BugBountyTips #HackerOne #AppSec #Elasticsearch
Join team 👉https://t.co/CRSus3yB9T
AWS @awscloud Loom @AWSOpen - CRITICAL 10.0 - Unauthenticated super-admin (auth bypass) - CVE-2026-103956.
Big one for my cloud-native friends and lovers!
Exploit:
https://t.co/Rs4yjUeHjC
bacaan yang bagusss banget 👍
i think dalam hal apapun kita bakal beneran ada hasil kalo fokus ke performance pribadi. jangan liat keberhasilan orang lain sebagai titik yang harus kita kejar, apalagi mostly yg kita liat di sosmed itu fana 😂
bakal mudah banget "terpukul" kalau yang kita fokusin selalu angka2 yang dipamerin orang. well, on chain never lies katanya but banyak juga yg sebenernya make money dari berbohong wkwk. at this point ga peduli mereka sih, lebih peduli orang yg serius belajar dan bisa dibuat tersesat
ini educational purpose, faktanya ada banyak cara larping tanpa harus edit AI atau pinjem wallet orang 👇
bayangin bakal jadi apa kita kalau terpaku improve skill cuma karena hasil pamer orang lain, yuk fokus aja sama progress diri sendiri 😋 serius deh profit $20 is a massive achievement daripada ribuan tapi fake.
percaya aja sama cumulative progress!
¿Sigues perdiendo horas configurando herramientas fragmentadas para buscar vulnerabilidades en tus desarrollos? El pentesting autónomo basado en múltiples agentes de IA acaba de dar otro paso gigante.
El repositorio open-source `BugTraceAI` ofrece un escáner de seguridad autónomo y multi-agente, diseñado para ejecutarse de forma local y 100% *self-hosted* mediante Docker.
Lo que nos ofrece:
• Orquestación multi-agente: despliega agentes coordinados para auditar código y superficies de ataque sin intervención humana constante.
• Despliegue sin fricción: arquitectura lista para levantar en contenedores Docker en tu propia infraestructura.
• Control total y privacidad: al ser autohospedado, mantienes el código y los hallazgos confidenciales dentro de tu red.
Mientras la mayoría sigue dependiendo de escáneres estáticos tradicionales que generan ruido constante, integrar agentes autónomos especializados cambia las reglas del juego en el desarrollo seguro.
Te dejo el repositorio oficial completo por acá abajo para que lo despliegues y lo pruebes en tu entorno 🛠️👇
AI security stack is getting f...cking important
10 open-source GitHub projects for letting agents use real tools without giving them the keys to EVERYTHING
01 E2B
▸ https://t.co/DrzCf9dj69
→ isolated sandboxes for agent execution
02 gVisor
▸ https://t.co/nuwxaXyQd3
→ sandbox untrusted workloads
ISOLATE THE AGENT
03 Firecracker
▸ https://t.co/M5EyDiSyPb
→ lightweight microVM isolation
04 Kata Containers
▸ https://t.co/1z6kgws9aX
→ containers with VM-level isolation
CONTROL THE TOOLS
05 Open Policy Agent
▸ https://t.co/852OIL1z5C
→ policy checks before actions execute
06 Casbin
▸ https://t.co/zjncieEueO
→ permissions + access control
PROTECT THE SECRETS
07 Infisical
▸ https://t.co/Wt9v5hKOro
→ secrets management for AI infrastructure
08 SOPS
▸ https://t.co/WDWZjquEgp
→ encrypted secrets inside repos
WATCH WHAT HAPPENS
09 Falco
▸ https://t.co/BXQUlwne2c
→ detect suspicious runtime behavior
10 Trivy
▸ https://t.co/S8LWn7YH88
→ scan code + containers + infrastructure
the security loop:
request → permission → sandbox → tool → execute → inspect → allow / block → log
3 layers I'd actually build:
agent:
E2B → OPA → Casbin
runtime:
Firecracker → Falco → Trivy
secrets:
Infisical → SOPS
and this is where it gets interesting:
giving an AI agent more tools makes it more useful
it also gives it more ways to break something
the next agent stack isn't just memory + tools + reasoning
it needs permissions ⭣
10 GITHUB REPOS WHERE AI MEETS CYBERSECURITY.
1. PentestGPT — an AI assistant for penetration testing.
Helps security researchers reason through pentesting workflows, interpret findings and organize the next steps.
https://t.co/upqarmmnK5
2. Caido — modern web security toolkit.
A fast, extensible platform for web security research with an interface designed around intercepting and analyzing HTTP traffic.
https://t.co/9saYABm3Dg
3. HexStrike AI — AI-powered security automation.
An MCP-based security framework that connects AI agents with a large collection of cybersecurity tools.
https://t.co/76ocSIap9w
4. Strix — autonomous AI security testing.
An open-source AI-powered system that can investigate applications, discover vulnerabilities and produce security findings.
https://t.co/OfaDzLxML7
5. Nuclei — vulnerability scanning at massive scale.
A fast template-based scanner that can detect security issues across websites, APIs, networks and infrastructure.
https://t.co/c3EFneObUT
6. Semgrep — find vulnerabilities before they ship.
Code-aware static analysis that can scan large codebases for security bugs and custom patterns.
https://t.co/I2bUgqt1Fs
7. Gitleaks — hunt secrets hiding in Git.
Scan repositories and commits for leaked API keys, passwords, tokens and other sensitive credentials.
https://t.co/lfluln5JaL
8. OWASP Amass — map the attack surface.
Discover domains, subdomains and infrastructure to build a detailed picture of an organization's external attack surface.
https://t.co/n0WtHpDnBw
9. Wazuh — your open-source security control center.
Host-based detection, log analysis, vulnerability detection and security monitoring in one platform.
https://t.co/E7MeHPWfAs
10. Prowler — cloud security from the command line.
Automatically assess AWS, Azure, GCP and other environments against security best practices and compliance frameworks.
https://t.co/B5qoMAWIDu
All are open-source.
Bookmark this before your next AI + security rabbit hole.
A different approach to Bug Bounty Hunting:
Instead of using your time and tokens searching for attack vectors and then looking for their impact, start with the impacts that the BB accepts.
1. Start from the impact
Identify the valid impacts accepted by the BB and focus your thinking there.
2. Guide your AI from the impact
Point your AI system toward a specific goal instead of asking it to find arbitrary attack vectors. For example: find a vulnerability that leads to unauthorized fund loss.
3. Filter for valid findings
Use the goal to guide the AI and focus its reasoning only on findings that can actually produce an accepted impact.
4. Go deep
Once you have a potential finding, go deep. Start from the end and work backward toward the root cause.
It’s like reverse engineering the vulnerability. Instead of:
Attack vector → Impact
Try:
Impact → Attack path → Root cause
Start from the end, not from the beginning.
Day 1 of landing a private audit
Today, I’m starting something different.
I’m going to publicly document my journey into smart-contract security.
I started my tech journey in 2024 as a developer.
Since then, I’ve gone from frontend → backend → Web3 → Solidity → smart-contract security.
I’ve built projects, learned from tutorials, entered audit contests, submitted bug reports, found real bugs, found plenty of invalid ones, and experienced more duplicates/informative reports than I’d like to admit 😂
But I’ve realized something:
Learning security and becoming a security researcher are two different things.
So for the next 3 months, I’m going all in.
I’ll document the audits, the mistakes, the dead ends, the research, the findings, and everything I learn along the way.
No pretending I have everything figured out.
Just doing the work and showing the receipts.
@alexabelonix@CyfrinUpdraft@blockaid_@0xBiyyah@pashov@PashovAuditGrp@biggids@CryptoJobsList@Web3_Vinay@yourweb3jobs@that_young_girl
$50,000 goes to a Junior security researcher who joined Immunefi just last month! 🔥
@n0_Be3r found a high-severity vulnerability, earning $50k from their very first paid report.
With just one payout, they’ve already jumped to #22 on the 90-day leaderboard.
What a debut.
Congrats @n0_Be3r! 🎉