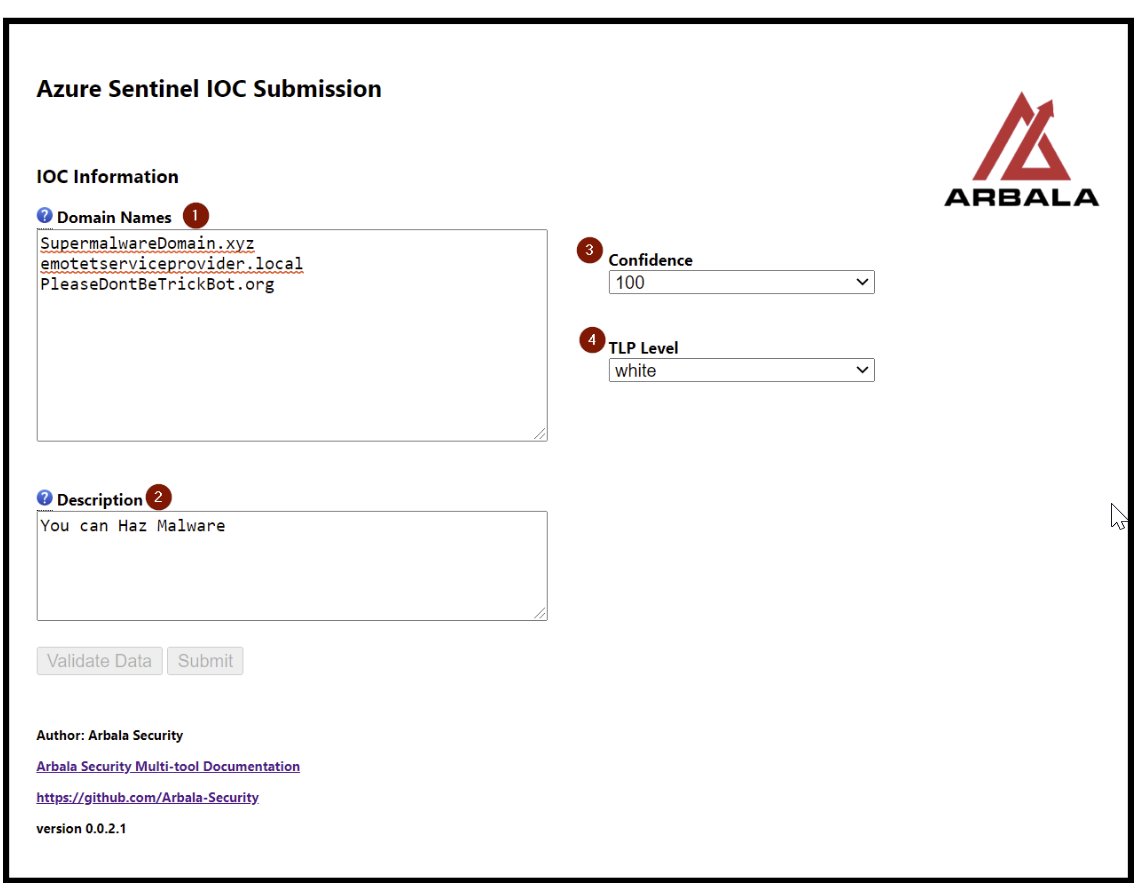
If you are looking for one of the easiest ways to get IOCs into Azure Sentinel, this is it. The next update being worked on will allow hashes, and IPs to be added. @MsftSecIntel#Security#opensource https://t.co/65nw2wS15N
#AzureSentinel *Updated* Arbala Security Multi-Tool browser extension for Azure Sentinel. You can now copy & paste multiple IOCs. Adjust confidence score, TLP level & customize descriptions. Like many of our other offerings, this is free and open source. https://t.co/3A9VBwh8gJ
This is extremely useful when a Sentinel Incident identifies a malicious domain communication and you want to quickly add it to your Zscaler Block list.
If you use #AzureSentinel - You might find this ARM template useful beyond the #Zscaler purpose because it introduces JavaScript in a Playbook. I hope you enjoy! Feel free to contact any one on our team for questions or assistance. https://t.co/e3ttdQUXUq
This ARM template will deploy an Integration Account and a Playbook. It will pull domains from Sentinel Incidents and add them to a Zscaler URL Category of your choice. URL Categories can be configured to Block and Allow domains in the Zscaler Access Policies.