@TurkTelekom 28 Mayıs tarihinden beri Urla'da Genel Arıza olmamasına rağmen bu bahaneyle internet hattım için gereken altyapı hizmetini @TurkNet'e sunmuyor. Dolaylı olarak iletişim hakkımı da engelliyordunuz. @TurkNetDestek@iletisim
🥇 FREE Certified AppSec Practitioner (CAP) exam! 🥇
** No Discount Code Needed**
To get the offer:
1. Retweet this post.
2. Fill this Google form -
📄 https://t.co/WVFmLaO3CZ
3. We will email you the exam details. 💯
🔗 Read more about our CAP exam -
https://t.co/iW47bEhG0s
#pentesting #CAPExam #Applicationsecurity #informationsecurity
Hello everyone, we have new website to boost donations to Turkey. https://t.co/ZwNJd7p1aW
Could you please share this with all your friends.
This is for non-turkey residency
Yurt dışından yardım yapılabilmesi için Trendyol uygulaması lütfen yayalım arkadaşlar 👇
How To Grasp Container Networking 🧵
A tricky topic... Container networking can feel like magic at times. But it's not!
Rather it's a bunch of more primitive "LEGO bricks" like net namespaces, veth pairs, and bridges combined into a handy (but complex) higher-level abstraction.
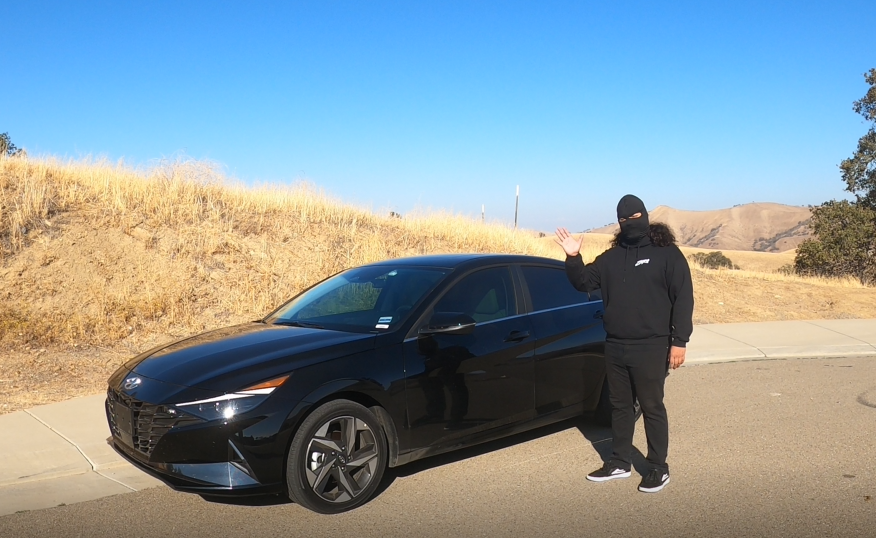
We recently found a vulnerability affecting Hyundai and Genesis vehicles where we could remotely control the locks, engine, horn, headlights, and trunk of vehicles made after 2012.
To explain how it worked and how we found it, we have @_specters_ as our mock car thief:
After two years of negotiations with Microsoft, the joint committee of the German federal data protection authority and 17 state regulators (DSK) published a devastating statement that essentially says that organizations currently cannot use MS365 in a lawful way under the GDPR.
🧵 In part 4 of the C2 Development Series, we finally look at writing a Stage 0 and 1 Implants. As well as doing this, we go on a bit of an adventure with the history of offence/defence over the past 15~ years. https://t.co/Sw9dA567T6 1/2
One funny way to use procdump to dump lsass and not get flagged by defender is to redirect it to smb share where only current user can authenticate (you can use dummy user with runas /netonly). Defender will not be able to scan dump file and will not flag it.
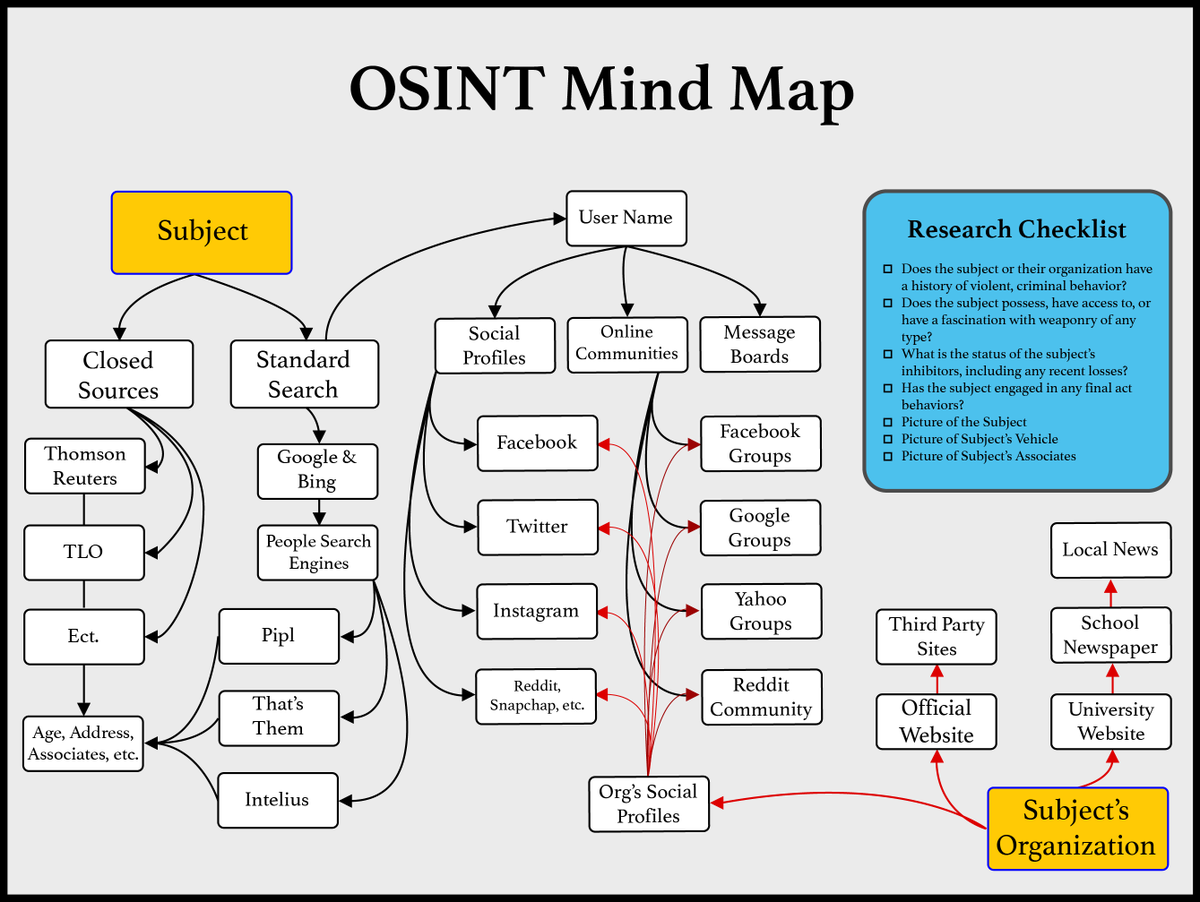
The most visited and followed #OSINT page on our platform last week has been the Ultimate OSINT collection by the @hatless1der And for good reason! https://t.co/323Lvz1v19
I've spent the last couple months doing extensive dev/testing to achieve shellcode injection in a remote process against a couple of top tier EDRs. I've learned a lot but I really can't overstate the value of the *concepts* presented in this blog post: https://t.co/CerFaumNGM
Access to the raw disk or MBR is not fundamentally malicious, but it's a weak signal often present in destructive malware such as HermeticWiper. I updated these #100DaysofYARA rules for signed & unsigned variation & mutations of PhysicalDrive toolmark https://t.co/yE2HG04O4K
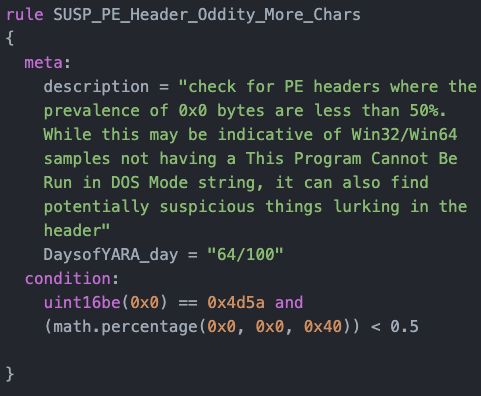
Day 64 #100DaysofYARA looking for PE headers where the prevalence of 0x0 bytes are less than 50%.
Normalish PE headers from offset 0x0 to 0x40 are composed of roughly 80% 0x00 bytes
LAPSUS$ extortion group have successfully breached both NVIDIA & Samsung.
-March 1st: They demand NVIDIA open-source its drivers, or else they will
-March 4th: LAPSUS$ released Samsung proprietary source code.
See attached images for more details directly from LAPSUS$
A Collection of Notes, Checklists, Writeups on Bug Bounty Hunting and Web Application Security.
https://t.co/flU6G5TsJG
#cybersecurity#bugbounty#hacking
1\ How to prove malicious macro was enabled & clicked? 👀 #DFIR
HKEY_LOCAL_MACHINE\USERDAT\Software\Microsoft\Office\<VERS>\<PROGRAM>\Security\Trusted Documents\TrustRecords
Look ONLY for values where last four bytes are "FF FF FF 7F".
These files had macros enabled
👇👇👇
From carding to conspiracies, Discord has in recent years become massively popular platform
That’s why myself and @jakecreps have built Serverse, which gives you the ability to search some of the most popular servers using keywords 🤖
https://t.co/aqBXmQhxzJ
#OSINT#infosec