📣📣📣 PSA for all Cloud bug hunters! 📣📣📣
We've created a new $250,000 tier for Google Cloud VRP. Want to know more about why we are introducing this tier and how we expect it to support high-impact architectural research? 👇
https://t.co/Q4gcTsMy5j
Missed one more from the drop lol
CVE-2026-43783 - macOS LPE via DesktopServicesHelper. One XPC request -> arbitrary chown -> root.
PT SWARM writeup:
https://t.co/uEaHXKbLhb
My blog:
https://t.co/TlMOqux5lW
PoC:
https://t.co/qH1LnxXbjj
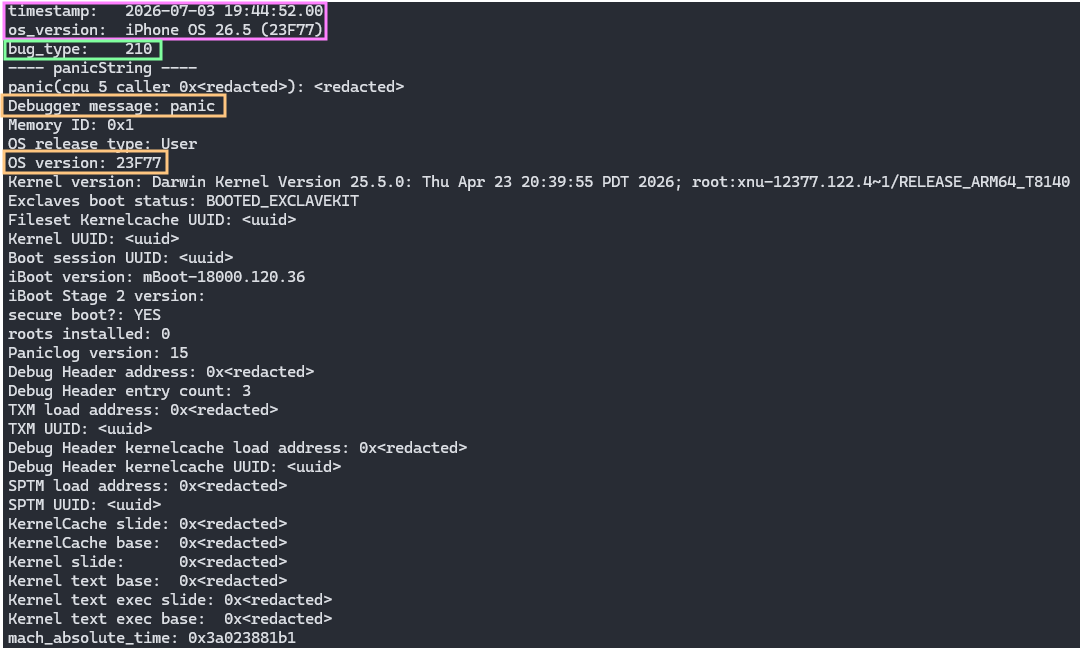
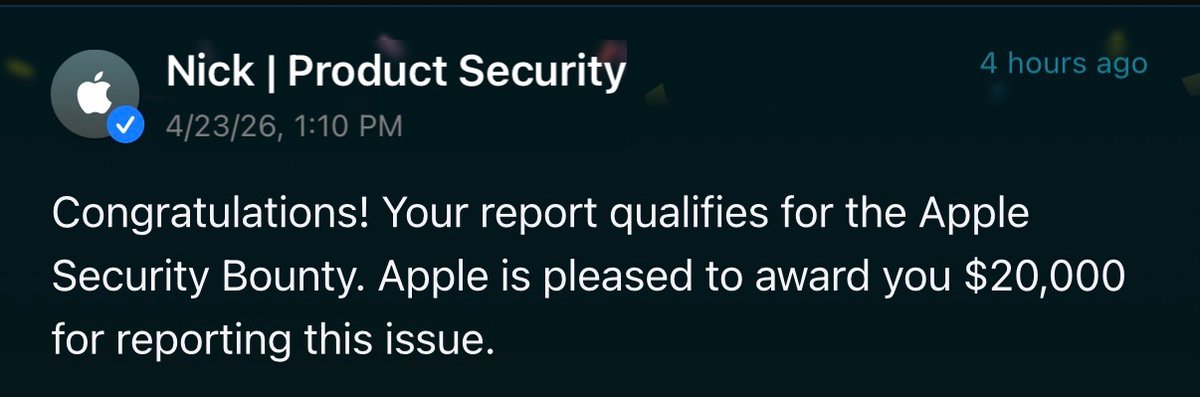
I’ve been hacking on for quite some months now, and it’s been a rewarding journey. Huge shoutout to their security team! 🙌
There are still some bugs pending for payout. The grind continues! 🚀 #BugBounty
Finding vulnerabilities in iOS is just the beginning. The real challenge starts in the subsequent stages, where getting a leak and a data-only read/write primitive are just two of the problems to be solved ;)
Someone open-sourced a fully jailbroken iPhone you can run on your Mac.
→ run one script
→ connect over VNC
→ fully jailbroken iOS, ready to go
100% open source.
An absolute goldmine for bug bounty hunters 👀💥
A massive collection of real, disclosed HackerOne reports — organized by vulnerability type, impact, and target 🎯
If you want to go beyond theory and actually understand how real-world exploits work… this is it.
Study patterns. Learn impact. Hack smarter. 🚀
🔗 Source: https://t.co/yMey4fzDbn
#BugBounty #InfoSec #CyberSecurity #EthicalHackin
🚨 $2,000,000 Bounty for Android Full-Chain 0-Day 🚨
At ZeroZenX, we are actively looking to acquire a fully functional Android Full-Chain 0-Day exploit. We are offering up to $2,000,000 USD for high-quality submissions.
Scope:
- Android full-chain exploit
- Remote or browser-based initial vector preferred
- Privilege escalation to full device compromise
- Reliable and previously undisclosed vulnerabilities
What we offer:
✔ Competitive acquisition price (up to $2M)
✔ Professional and confidential vulnerability handling
✔ Fast evaluation and payment process
✔ Direct collaboration with our security research team
If you are a security researcher, exploit developer, or vulnerability hunter with a qualifying chain, we want to hear from you.
📩 Contact: [email protected]
🌐 Website: https://t.co/ZpjjzcPv9H
🛡 Submission Portal: https://t.co/QDtBacaWC9
Let’s push vulnerability research forward and ensure responsible acquisition and handling of critical discoveries.
#CyberSecurity #AndroidSecurity #ZeroDay #ExploitDevelopment #BugBounty #SecurityResearch #android #news #0day #zeroday #bounty
It took me 6 months to learn, I'll teach you in 1 minute
How I make audits structured:
Pick main function (deposit, withdraw, swap)
Branch out into sub-folders:
> validations
> external calls
> state changes
> return logic
Inside each branch, I explain everything till I get it.
> direct explanation
> code screenshots
> own reflection
> attack vectors research
Mirror code architecture in notes.
Review anytime without re-reading code.
This structure keeps codebases from overwhelming you.