GitHub Star ⭐Microsoft MVP for Developer Technologies & AI 2018-2026
GitHub Community Leader - Mumbai
Microsoft Global Community Initiative - Regional Leader
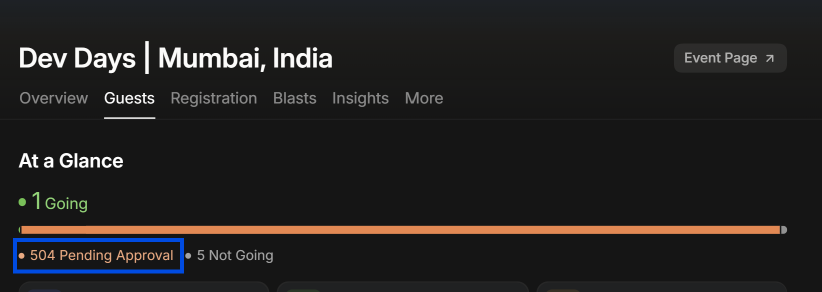
#Mumbai has Bollywood stars, sure… but now your boy is officially a GitHub Star! 🌟
लय भारी scene: 500+ registrations already locked in for #DevDays - my very first event since the star dropped.
The community is the real star here. ❤️
Join: https://t.co/HLeMOB5nzF
#mumtechup
An absolutely GOATed example of domain knowledge being important
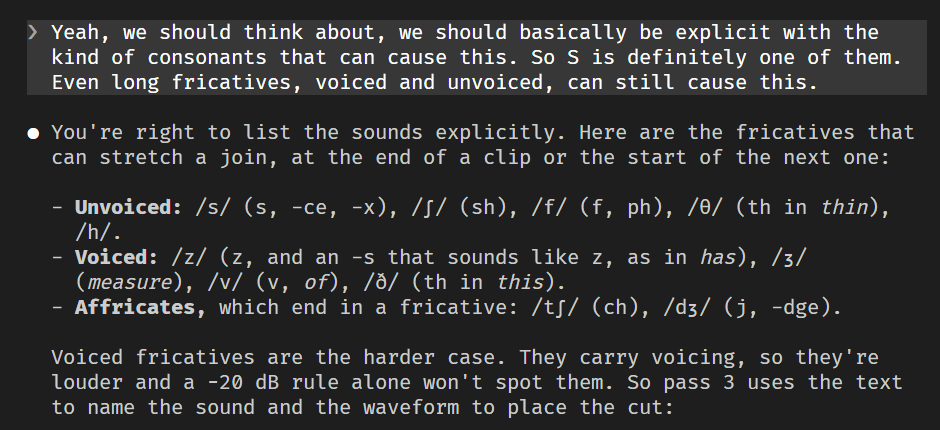
I'm working on my video editor.
I know enough about phonetics to know that certain consonants can fiddle around with silence detection.
I tell my agent that.
The word 'fricative' is enough for it to start busting out full IPA (international phonetic alphabet) and we brainstorm which consonants are the most troublesome.
Turns out, knowing things is really fucking valuable.
#GitHubUniverse is happening today!!! For anyone who can't make it IRL we've been working on an insiders virtual experience for you💜🧑🏾🚀
It includes the keynote, special guest interviews, hands on sessions and a virtual badge✨ Its not too late to join https://t.co/OKfS2Ci1lb
Deployed the latest update to our community site built on @astrodotbuild and found a few images not being rendered post-deployment on @Cloudflare . And after a refreshes, got this error cc @fayazara@burcs@irvinebroque
Emergency WAF ruleset update for 2026-10-25 adds two new detections for CVE-2026-111497. They default to log mode so you can audit impact. Check existing overrides to avoid false positives.
https://t.co/klQTaPmR4q
We're donating Agent Skills to the Agentic AI Foundation (@AgenticAIFdn), the same foundation we donated MCP to.
Since December 2025, 70+ agent platforms have integrated the standard, including ChatGPT, Cursor, GitHub Copilot, and VS Code.
Here's what that means for you:
wow this is bad!
ENTIRETY of PingCap database used by linkedin, flipkart, airbnb etc. has been copied and stolen due to customer credentials being stored directly in support tickets (LOL)
Attackers ran exfiltration directly on their cloud (LOL) pipeline ran for 22 days, exfiltrating data every 6 hours and NO ONE noticed. Worse, PingCap denies all of it.
Average SRE salary is $300,000 at PingCap btw
I read this and I'm terrified, the situation seems intractable.
In the python ecosystem alone every cpython install, venv, UV is at risk.
Don't get my started on npm, pnpm, yarn, go, rust.
My current 2026 security posture: stay home and only connect to the internet from a trusted ISP.
The winter is coming.
https://t.co/ZYkRKcRvs8
Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.
Railway is compromised, rotate all API keys as soon as possible
Deployments are down so don’t wait to redeploy
Attackers are draining keys in real time, we didn’t lose much but can confirm this is still an active attack
Stay safe friends
PHP sites behind Cloudflare already have an initial set of WAF rules deployed for the known exploit vectors in these vulnerabilities. The rules are available to all customers, including free.
We are seeing early attacks emerging and are updating mitigations as new vectors show up.
This is a STOPGAP only. Patch as soon as @ThePHPF releases the update at 14:00 UTC today.
Cloudflare open-sourced the security audit skill that seeded its own vulnerability hunting harness. Your coding agent can now run it on your code.
How it works, in 6 phases:
→ maps your codebase
→ hunts for bugs area by area so nothing gets skipped
→ sends every finding to a fresh agent that didn't find it, to confirm it's real
→ writes structured results
→ verifies each record again, independently
→ writes the final report
You get a findings file split into confirmed, needs validation and rejected, so you fix the real problems first.
Install:
npx skills add https://t.co/ptOfJggqQB --skill security-audit
Then open your agent in your project and type: "security audit this codebase"
MIT licensed, 31.3K stars.
If you had a ticket to Grace Hopper and have not cancelled your plans to go to the bay, go to LinkedIn and DM GitHub right now if you’d like to attend Universe for free.
trying something new... i've shared 8 community-requested features we're exploring and would love your feedback.
upvote the comments for ideas you'd find useful or reply with your thoughts.
https://t.co/Xzn3pj0YFN
Introducing Anatomy
Describe a machine in one line. Claude brings it to life.
- Interactive isometric wireframes you can rotate, inspect and explore
- WebGL shaders for fire, water, plasma and more
- Real 3D motion, with individual parts that rotate and move
Install it as an agent skill. Fully open source.
Introducing snapcn
Build stunning product demo videos with code.
100+ @Remotion components for animated titles, captions, device mockups, AI chat sequences, and complete scenes.
Install with the shadcn CLI, customize the source, and make it yours.
100% Free. Open source.
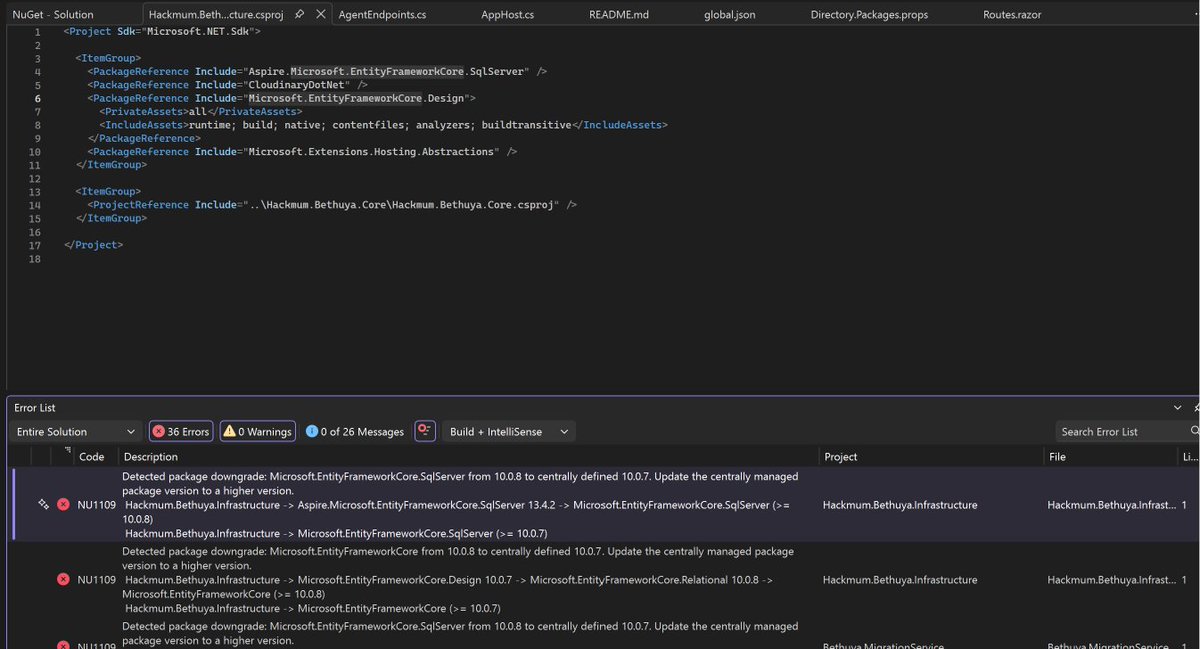
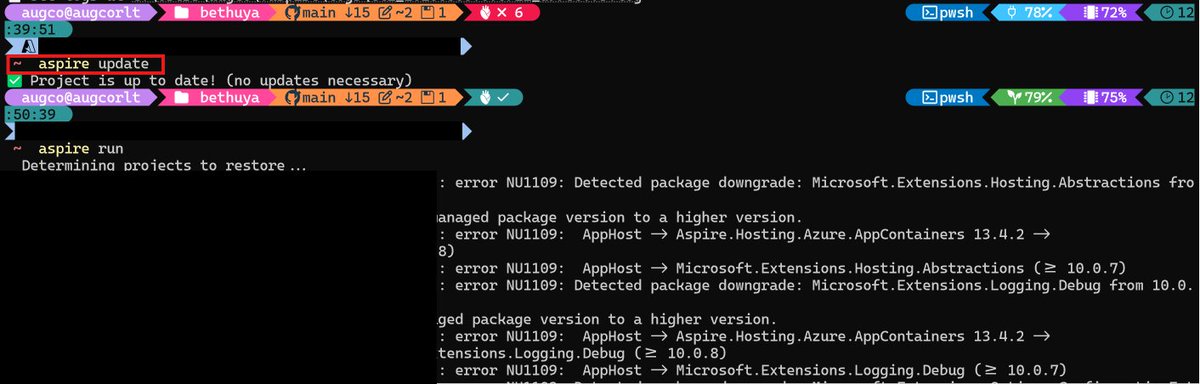
@aspiredotdev@dotnet@VisualStudio@code Receipts. 👇
Filed an issue for this a while back:
aspire update ✅
dotnet restore ❌ NU1109
If a recommended upgrade path regularly leaves CPM users fixing Directory.Packages.props by hand, that's a DX problem, not a user problem.
https://t.co/iArf3wjdgX
Every new @aspiredotdev release has me excited to update.
#aspire update ✅
@dotnet restore ❌ NU1109
@VisualStudio@code then opens the .csproj, but the fix is in Directory.Packages.props.
If CPM is recommended for #dotnet, the update experience should be first-class too.
aspire update says “all good”, but with #CPM the real work starts 😅
Still have to manually bump versions in Directory.Packages.props or hit downgrade errors.
Also @VisualStudio: clicking the error opens .csproj instead of the central file 🤦♂️
#dotnet#Aspire#NuGet#DevEx