‼️ BREAKING: Go has issued an URGENT security update blocking 8 certificate authority keys over undisclosed security concerns.
It will reject certificate chains using these keys, potentially breaking connections for rebuilt applications.
The filter cannot be disabled.
Here's what we know: https://t.co/X0uIVXrlp1
NEW CERTIFICATION ALERT! The new Burp Suite Certified Practitioner certification launches today! Learn more and get your exam here! 🎆
#burpsuitecertified
https://t.co/jjc4nX42tC
Did you know, DOM Invader can inject the canary into every source automatically? Set the canary to an injection and improve automated bug hunting - let DOM Invader do it for you!
Finally CrackMapExec can now fetch all domain users when the DC is vulnerable to NULL Session 🎉
Prior to this, CME what useless except for the password policy option 😓
No more enum4linux, rpclient etc, all great tools but I prefere one tool to rule them all 🔥
#Parallels Desktop RDPMC hypercall interface and vulnerabilities: @renorobertr details how he found a heap overflow & a TOCTOU bug in his latest blog. https://t.co/D2OoRXed1o
Wow - with just 10 seconds left of their 2nd attempt, Daan Keuper and Thijs Alkemade were able to demonstrate their code execution via Zoom messenger. 0 clicks were used in the demo. They're off to the disclosure room for details. #Pwn2Own
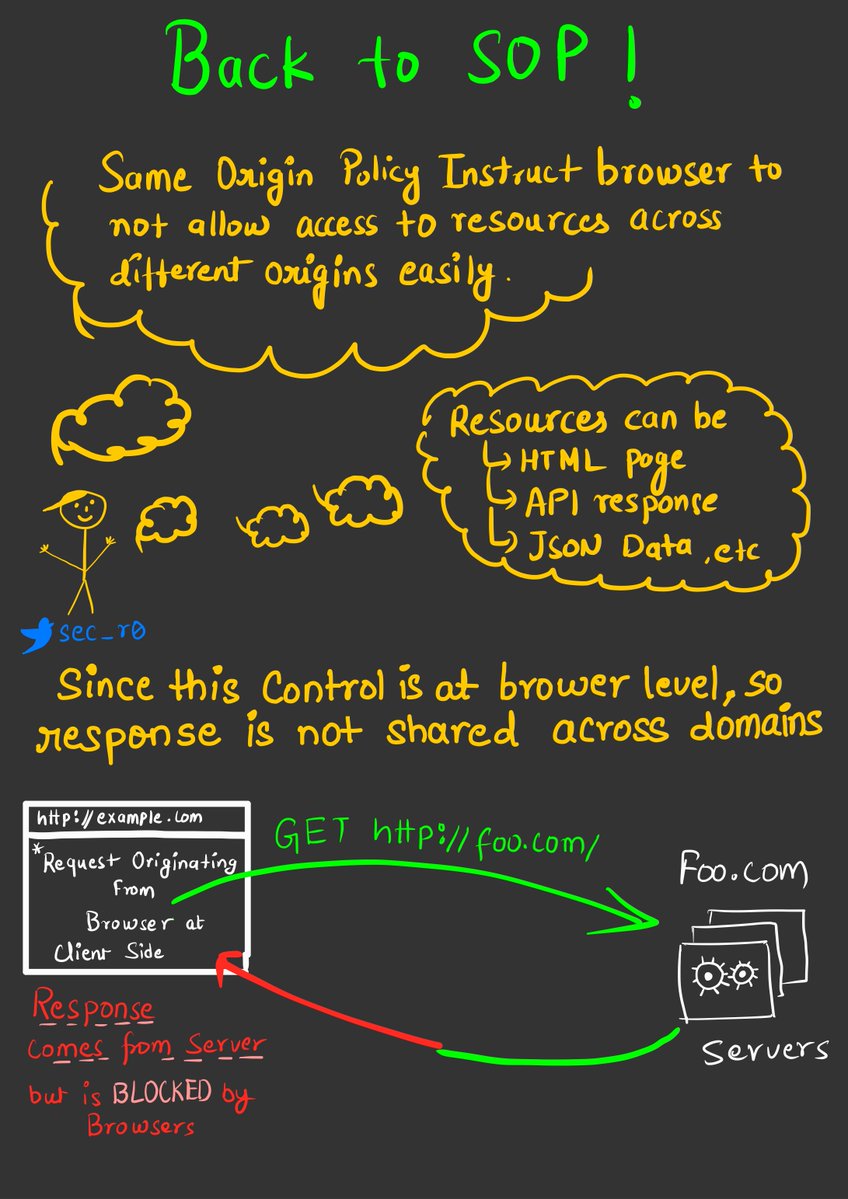
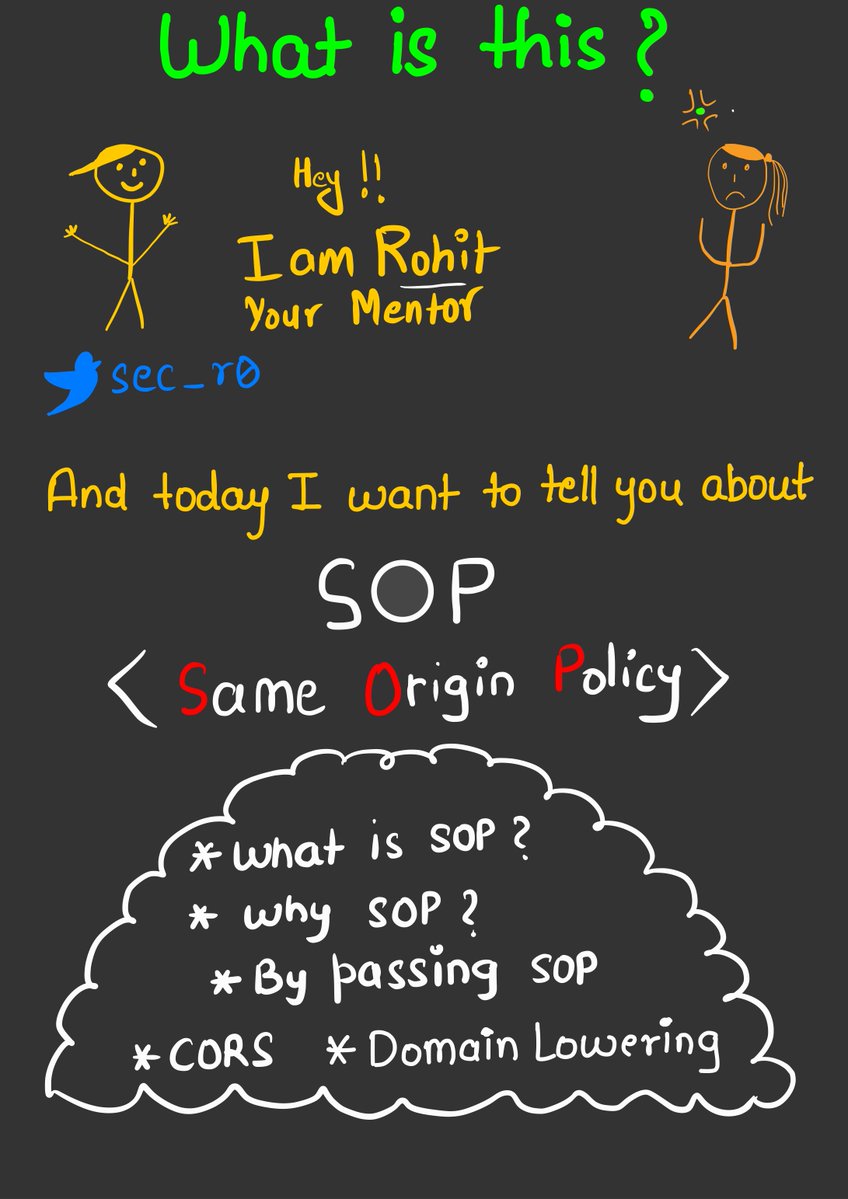
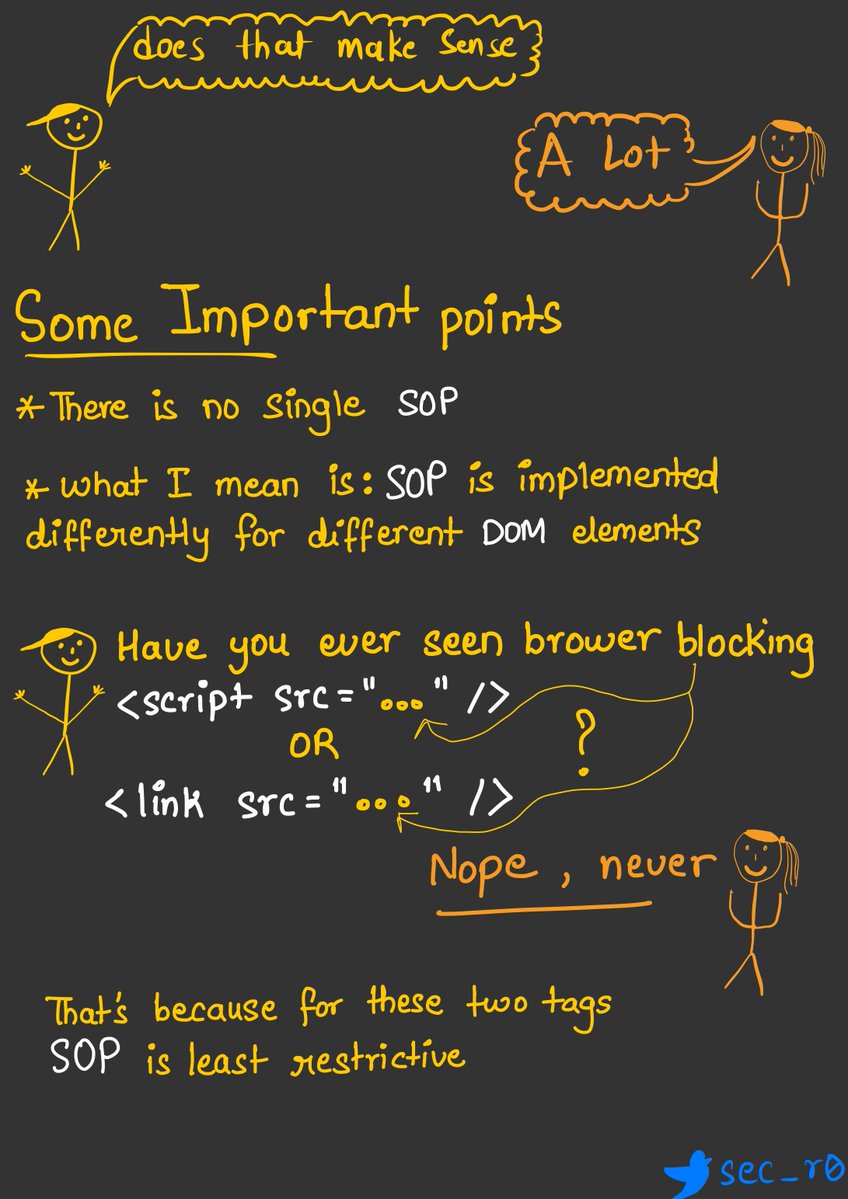
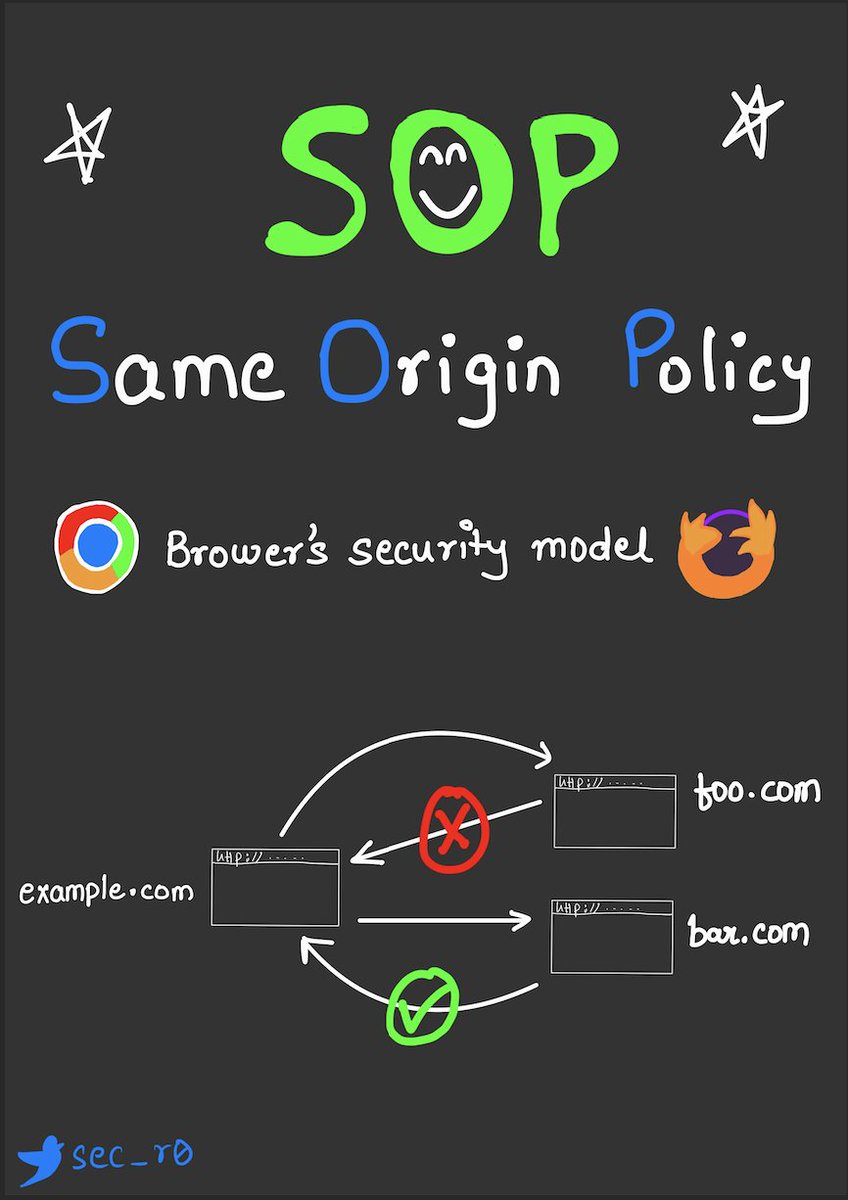
🥳🥳 Learn SOP the most simplest way ever. If you are bug hunter/pentester or web dev, knowing SOP really helps.
🍻SOPZine for free @gumroad : https://t.co/AdrXzB7r4l 🎉〽️
Please RT for good reach.
#infosec#zines#webdev#DeveloperJobs#security
Are you a #student of a #security related program at the university? Join our virtual #event on February 5th at 10 am (CET). This event is will give you insights into the security industry and how companies like Riscure work. Check it out and register now: https://t.co/wy5DIMCaud
New version 5.1.4 of CrackMapExec is available on @kalilinux and for sponsorware of CME 🎉
Few improvements:
- thanks to @byt3bl33d3r CME now uses asyncio over gevent 💪
- some issues have been fixed (spider, pass-pol, MSSQL thx to @D1iv3 🙏)
- CME now use Impacket v0.9.22 🚀
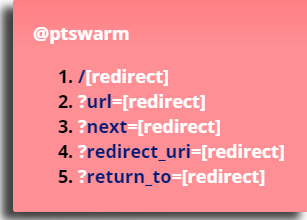
Open redirect parameters from every disclosed @Hacker0x01 report ever, composed in one wordlist
The full list (48 unique): https://t.co/YBItx0k2wH
Top 5 sorted by popularity 👇
#ptswarmTechniques
I'm proud to announce the release of #BloodHound 4.0: The Azure Update!
Blog: https://t.co/pQxmjauZ5F
BloodHound 4.0 Release Poster: https://t.co/I6UuJtePhe
Get BloodHound: https://t.co/jQMzLJ9Fl4
Docs: https://t.co/QngrCQTOWb
Join the BloodHound Slack: https://t.co/oSzPG75Gei
👿 Hackers, behold... A new tool for dem bounties 💸💸💸
Generate oneliner Windows and Linux file download commands faster than ever with 📢 uberfile 📢
Coded with love with @_1mean
➡️ https://t.co/8FUaiy4LJn
#bugbountytips#ElMásHermosoDeLosCamiones
New gadget chain for deserialization in Zend Framework applications. Triggers on __destruct(), gives RCE and works in PHP 7.
https://t.co/BJ5LCdC0lB
#ptswarmTechniques
Burp Scanner lets you record login sequences using your browser, and use these to log in during the scan.
In the latest release, you can test your recorded sequences in Burp's embedded browser to confirm they are working.
Finally, the Most awaited write-up is here , SSRF (Server Side Request Forgery) worth $4,913 | My Highest Bounty Ever!
Kudos to @TechFenixSec Red team for helping me throughout the research
Retweet if you like it.🙂
#bugbounty
https://t.co/qfLCiAo0sg