The only way out is through.
They're calling it the Bugpocalypse. LLMs are being used to find long-hidden cracks in the software infrastructure, and it's happening at a furious rate. 3% of all compromises in computing history happened in the last week, claims one source? I believe it.
There are people saying public access to the frontier models ought to be locked out, or heavily guardrailed, over this. The problem with that idea can be summed up in one sentence: when lockpicks are outlawed, only outlaws will have lockpicks.
The lockpicks will be Chinese open-weight models, if nothing else. There's no way to stop those from becoming ubiquitous.
There are two futures in front of us. One in which only the bad guys have lockpicks, and security holes go undiscovered until they're exploited. Another in which everybody has lockpicks and is aggressively red-teaming their own software so it gets fixed before the holes are exploited.
The corpus of human code is huge but finite. The number of defects in it has to be finite too. We can fix those defects now; we have a million friendly robots to do it with.
The only way out is through.
Stealth browser extensions are underrated. Nobody ever finds them. Especially not EDRs.
If you hang around in the browser long enough, you collect almost everything you need 95% of the time
It’s also not about the value of the certification itself; The problem is if you’re the type of person who RELIES on a cert for getting anywhere
“What cert should I get” if that is the first question you’re asking, you’re not even close to being on track
Relay attacks are underrated in red team assessments.
You don't need to clone the card.
You don't need to crack the crypto.
You just need to be close enough to the target and have a partner near the reader.
Real-time signal relay.
The door thinks the card is right there.
No cloning.
No cracking.
Just physics.
Most access control systems have zero defence against this.
#RFID #RelayAttack #RedTeam #PhysicalPentest #AccessControl
Some people at frontier AI labs told me they believe startups are over.
OpenAI, Anthropic, Google, xAI will absorb every industry as AGI nears. Coding today, science, medicine, and finance next. Then everything else.
If they’re right, that’s a pretty boring end of the world.
@techspence And hard for defenders to be strict on security of developers endpoints if the company is a SaaS - Plus, EDR protection on Linux systems is much, much more immature than in Windows.
From an internal threat perspective, developer machines are as good as getting Domain Admin, and many times even more "lucrative" from an attack pov
They have the keys and typically much less oversight.
https://t.co/0XjCQ9I6kV
By breaking the typical chain of
Suspicious Activity -> 2nd Suspicious Activity -> Yet Another Suspicious Activity
with
Suspicious Activity -> Normal User Behavior -> Another normal behavior -> Suspicious Activity
you can reset model analysis and lower your threat profile
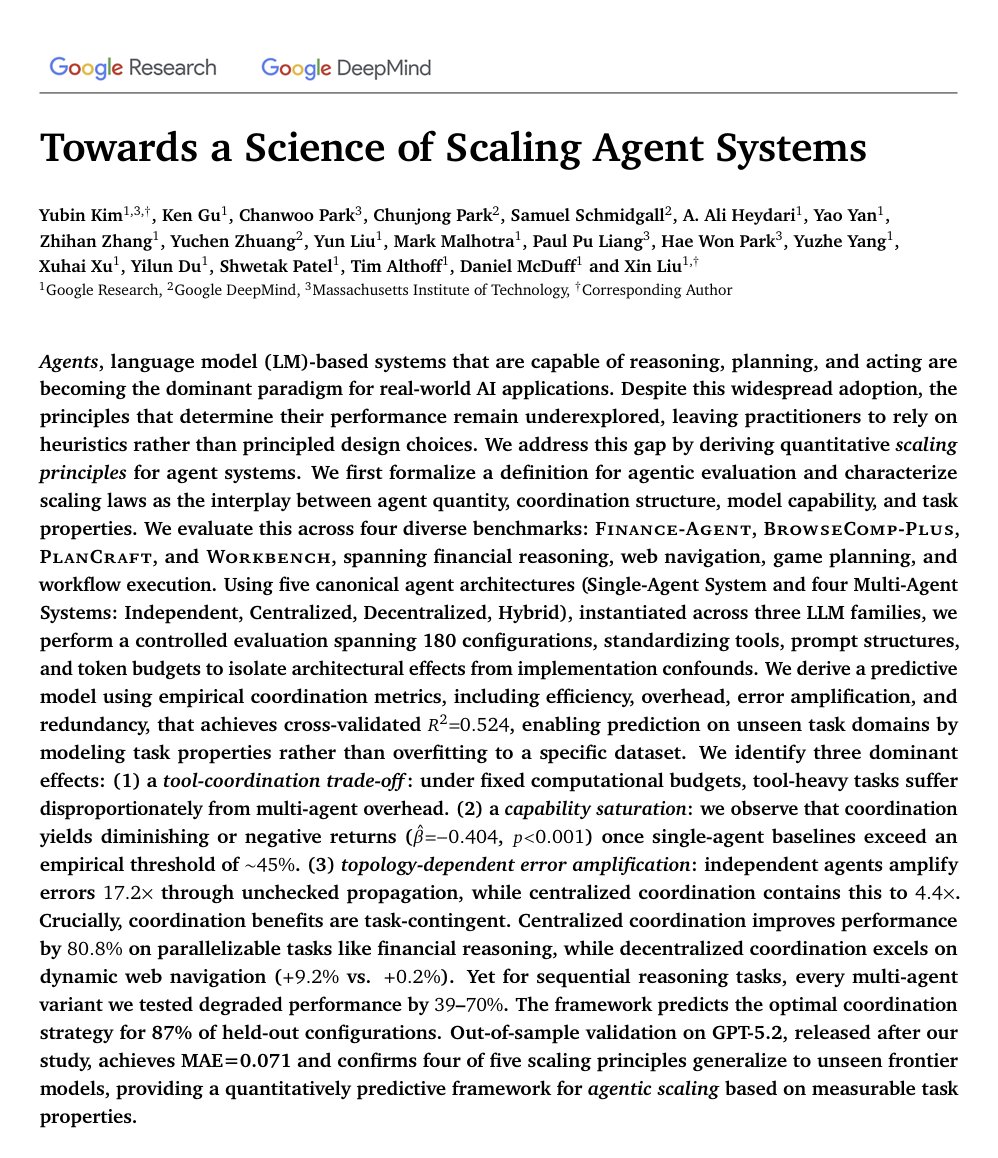
There's a common assumption in AI right now that if one language model can do a task reasonably well, having several of them collaborate — splitting up the work, checking each other's outputs, debating answers — should do it better.
This paper puts that assumption under a controlled experiment across 180 configurations and finds that the reality is messier and more interesting: multi-agent setups improved performance by up to 81% on some tasks and made things worse by up to 70% on others, with the difference coming down to whether the task can be broken into parallel pieces or whether each step depends on the previous one.
In a financial analysis, one agent can look at regulatory filings while another reads market news and a third examines earnings data — none of them need to wait for the others.
In a Minecraft crafting puzzle, on the other hand, each action changes the inventory that the next action depends on, so the steps have to happen in order and splitting them across agents just adds overhead without any benefit.
The paper fits an equation that predicts which architecture will work best for a new task 87% of the time.
For anyone building or thinking about building systems where multiple AI models work together, this replaces a lot of hand-waving with something concrete.
Read with an AI tutor: https://t.co/w1aX6BKPkW
Download the PDF: https://t.co/1YHNcFh7Dt
I want to share a quick thought for people in cyber security. This will be my longest tweet ever.
I’ve spoken to many lately who are having an existential crisis from the constant posts about “the end of cybersecurity jobs.”
Yes, things are changing quickly. This is a significant moment for the tech industry. Change can be uncomfortable. But we’ve seen cycles like this before.
• When GitHub and open source took off, people said software engineers would disappear because code was free.
• When AWS and cloud computing emerged, people said infrastructure jobs would vanish.
• When fuzzing and SAST tools improved, people said vulnerability research would disappear.
• Virtualization would eliminate infrastructure jobs.
• Mobile computing was going to end desktop dev.
• Exploit mitigations would end exploitability. It didn't.
Each time automation improved, the amount of software grew faster than the automation. It does feel "different" this time as it's explosive.
Some roles will shrink:
• repetitive pentesting
• basic vulnerability scanning
• tier-1 SOC monitoring
But other areas are expanding rapidly:
• AI system security
• supply chain security
• identity architecture
• autonomous agent security
• critical infrastructure protection
Historically, every time we eliminate one class of bugs, new classes emerge. Right now people are vibe-coding entire systems, giving AI access to their machines, crossing trust boundaries, and deploying autonomous agents with excessive permissions. The legal and regulatory world is nowhere close to ready.
There will absolutely be new failure modes. Humans are amazing and always adapt, finding new ways to do things.
The worst thing you can do right now is fall into a doom loop.
...and I’ll be honest, I too have felt the "psychological paralysis" a few times thinking, “Is this time different?” It's especially impactful when it comes from someone I respect in the community. There are certainly unknowns, in an industry where we've become accustomed to predictability.
But... the majority of those reactions are usually driven by social media, not reality. Platforms like X reward engagement, and sensational doom posts spread faster than measured thinking.
If you see something like:
“Holy #$%^! Opus 66.6 just found every bug in Chrome and replaced 50 startups!”
…mute it and move on.
Instead:
Stay curious.
Learn the new technology.
Adapt your skillsets.
Build things.
We’ll get through this transition the same way we always have. If I'm wrong then Sam Altman better be right about UBI! :) I'm sure that if this tweet gets any engagement that I'll get some heat for it, but a good friend of mine reminds me often to focus on what you have control over. I'll revisit this tweet at DEF CON 40!
Dumping LSASS is old school. If an admin is connected on a server you are local admin on, just create a scheduled task asking for a certificate on his behalf, get the cert, get its privs. All automatized in the schtask_as module for NetExec 🥳🥳🥳
Blog post: On the Coming Industrialisation of Exploit Generation with LLMs https://t.co/aK4pysY1wD
TL;DR: I ran an experiment with GPT-5.2 and Opus 4.5 based agents to generate exploits for a zeroday QuickJS bug. They're pretty good at it.
Code: https://t.co/47xHRObhRy