Goooood morning everyone!
Our team is looking for another Senior Technical Threat Researcher!
So, check out our blog! Tell your friends and ping us if you awesome and interested!
Check it out:
https://t.co/WPou4iFP7D
@NinjaParanoid Thanks for the rule. As feedback I would like to address the fact, that altering via "any of ($hash*)" will generate a bunch of FP as you can see on my test run against the VT Goodware corpus.
#ProgressUpdate The project now uses a staging system🥳. This prevents me from debugging in production and can be considered an invest into stability!
The cat likes it!
#ioc_one#cti
The recent #XZBackdoor caused a lot of agitation in the Open Source Community.
Today we publish a #ComprehensiveOverview what happened and how to check your system for affection.
Read more at https://t.co/jdkOHGaXs3
#DCSO#DRIF#Cyber
@adulau@fr0gger_@MsftSecIntel@MISPProject Hey @adulau, Microsoft updated the threat actor list and now provides a json formatted version of it on github as well. Based on your commit I wrote a script which converts this data into the MISP format.
Maybe it is useful for you ;)
https://t.co/GvF7jdVm5X
I converted the new threat actor naming taxonomy from Microsoft (@MsftSecIntel) to json in case someone else needs the data in a machine readable format.
https://t.co/DNvWh56lcq
#threatintel#research#apt
We are announcing a new taxonomy that better reflects the complex tapestry of the threat ecosystem.
Name mapping list and industry aka's:➡️ https://t.co/QHNRQekGX2
Read more:
⬇️⬇️⬇️
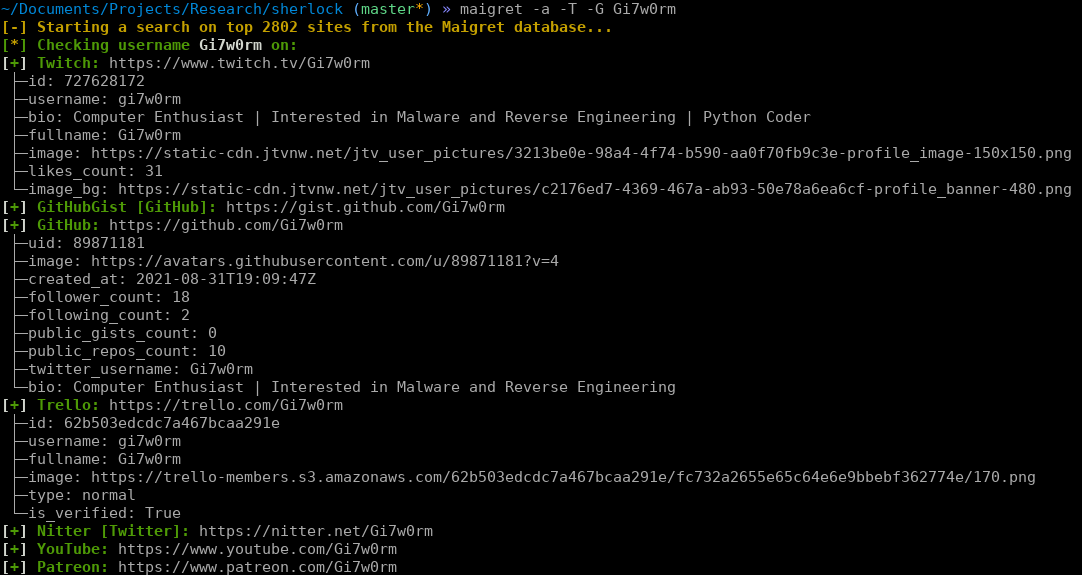
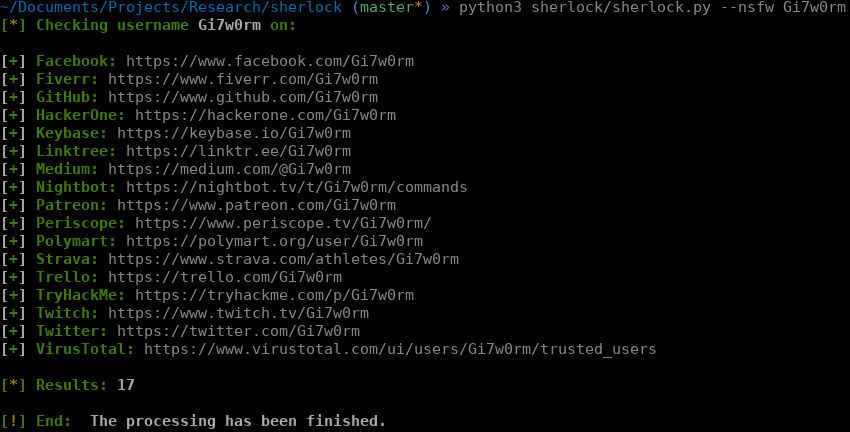
@Gi7w0rm Adding to this: Not so fancy but still my current favorite with a low false-positive rate is #sherlock.
A fork of it is called #maigret, which comes with more false-positives but contains sometimes additional information.
https://t.co/6CLAMb93pX
https://t.co/63YfXAOpjK
Check out our new blog post!
This time we analyse and follow HZ Rat. A previously undocumented malware delivered through malicious documents and self extracting archives. We tracked the campaign and identified a lot of C2 servers.
https://t.co/nwWGWGxQxn
#HZRat#DCSO#CyTec
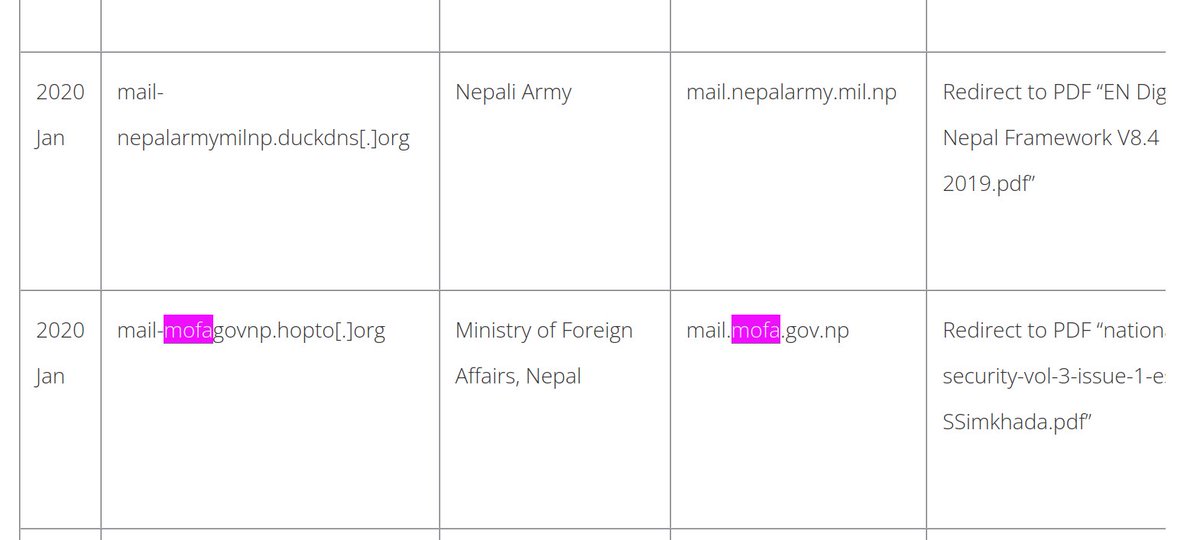
@jaydinbas It is MAYBE related to #Sidewinder.
The domain pattern is similar to Domains mentioned in a TrendMicro report about this group
https://t.co/PhYlUycxBE