Friday afternoon (vibe)coding project that was on my to-do for a while: obtaining Entra ID tokens from an endpoint by asking the WAM. This alternative to using the PRT cookie follows the legitimate SSO flow used by apps like Teams to obtain tokens. Code: https://t.co/qAEk8lXGYG
Detection performance shouldn’t be buried across alerts and metrics. 📊
In our latest blog, we introduce and open-source #FalconDash - a modular dashboard built to make Microsoft Sentinel detection performance visible, explorable, and easier to tune. 🚀 https://t.co/0EVJcKB0VY
@Romerrn@OutflankNL@mpgn_x64 The Hetzner bench was outdated. I retried with the latest version on Hetzner and benched 28 minutes for single HDD (for two DES halves, so 14 minutes per lookup). Updated the blog post with the disk details
@Romerrn@OutflankNL@mpgn_x64 For two DES halves: SSD (virtual on netcup) was 1 minute. HDD on hetzner was 220 minutes.
On our current host we have 60k IOPS provisioned with 1.5GBps speed where a DES half takes around 50s.
NVMe on PCIE4/5 should be faster than this but i still need to try (expecting 5x)
NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
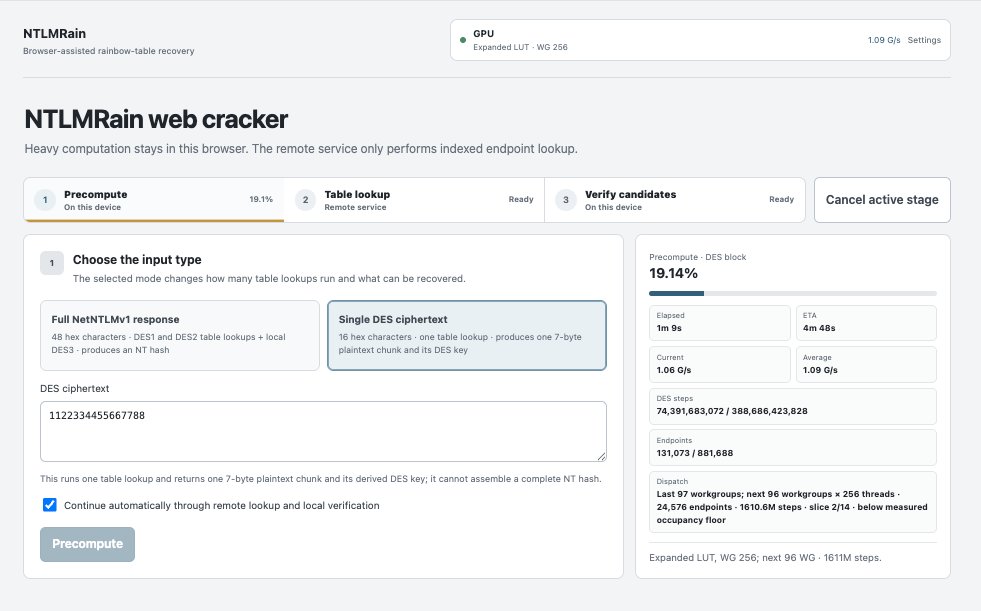
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: https://t.co/fnNqGzJ9O0
I just released the first public version of @BintracerLabs, a malware-analysis sandbox focused on macOS.
Bintracer can:
- Detonate Mach-O binaries, app bundles, and dylibs
- Extract DMG and PKG files
- Analyze JXA, AppleScript, Python, Perl, and shell scripts
This project is still early, but I can't wait to see what y'all think!
In one week I will be presenting at @SpecterOps SO-CON 2026 about CyberArk PAM. I will share our practical experience and insights on PVWA edge cases and CCP API misconfigurations. #SOCON2026
More information and registration: https://t.co/dHORi2Jooo
Pushed a major redesign and improvement of https://t.co/ZRVQgWfEKI for the old-school PowerShell warriors out there. Includes five more recent patch methods and tons of fixes, thanks to my best friend Claude 🤠
1. There's little to no value giving away someone's hard work to public only to feed threat Intel feeds, signature databases and APTs in return for a few likes and kudos 🙃
2. Private Discord servers offer Signal/Noise ~ 1.0 + friendly atmosphere🫢
Initial Access Guild FTW! 🍻
Added a feature to ADExplorerSnapshot script today to gather useful information about the environment via the classes, now it will tell you if SCCM, ADCS etc are active in the environment https://t.co/cOeOyf3PRe . Thank you @c3c for the awesome tool and the quick PR approval
📢 Big News! @mariuszbit is joining Outflank! He ticks all the boxes:
Experienced #offsec researcher ✓
Respected name in red teaming ✓
Built RMF tooling for initial access ✓
His work is coming to OST✓
The red hoodie fits perfectly ✓
Welcome Mariusz!
https://t.co/EBbODaWPBB
I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
@ze_ts_@SEKTOR7net The bigger risk with enclave vulns is that sensitive data/key material may be compromised, which is what they were designed to protect.
@ze_ts_@SEKTOR7net Abusing an enclave for running malicious code is tough (custom gadget chains needed) and most interesting functions (file IO, network IO) will go via VTL0/be subject to analysis in VTL0 anyway.
For post exploitation their use is limited - at least for now
@ze_ts_@SEKTOR7net Identifying what is exported in existing DLLs requires some reverse engineering to figure out the playing field for that enclave.
The offensive use is limited to memory ops within the same process - anything more interesting will go via VTL0 and is subject to ETW/EDR analysis
@ze_ts_@SEKTOR7net Thanks for the mention 😊
@ze_ts_ are you looking for defensive guidance? For developing enclaves it’s indeed important to limit the exported functions and follow the recommendations by microsoft :
https://t.co/fByQjHp847