Henri Hambartsumyan took the artisanal approach of manually reverse engineering the small Windows binary werfault.exe. He wrote down his findings in this new blog. Hope this helps SOC analysts and incident responders with incidents involving werfault.exe. https://t.co/zS2v1vseRu
🚨 BLOG ALERT 🚨
The #DetectionEngineering maintenance series continues!
As a detection engineer, the real challenge is keeping your detections effective, tuned, and maintainable as your environment evolves.
That’s exactly what we explore in the third post of the series: #FalconDash, a tuning companion designed to help detection engineers understand, prioritize, and review their detections.
If you’re building and maintaining detections, this is worth a look.
https://t.co/pcwtuNEXBK
#ThreatDetection #BlueTeam #CyberSecurity #ThreatHunting #SOC
Detection performance shouldn’t be buried across alerts and metrics. 📊
In our latest blog, we introduce and open-source #FalconDash - a modular dashboard built to make Microsoft Sentinel detection performance visible, explorable, and easier to tune. 🚀 https://t.co/0EVJcKB0VY
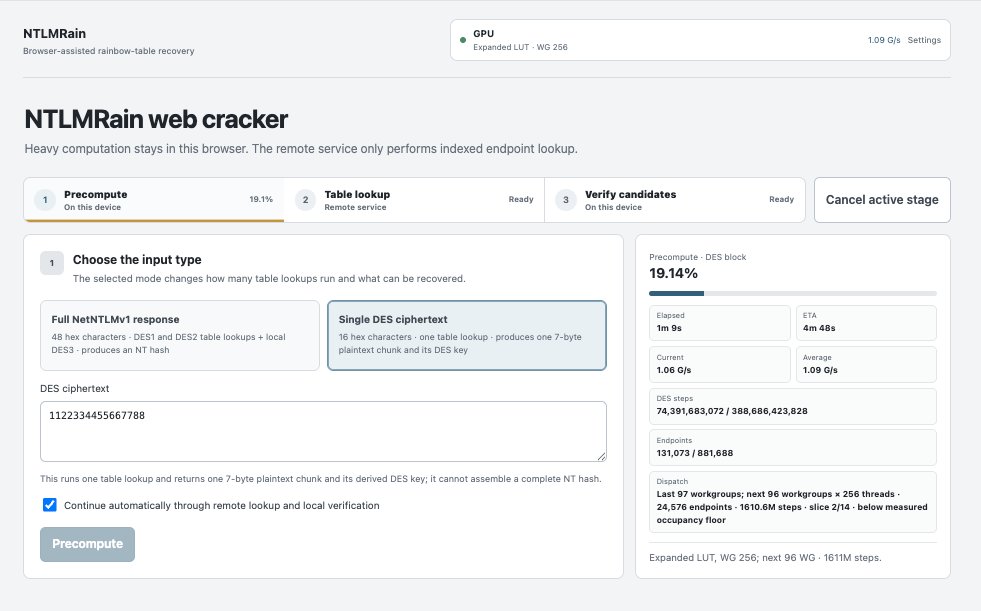
NetNTLMv1 is dead. Long live NetNTLMv1. 🌈
Today we're releasing NTLMRain: recovering NT hashes from NetNTLMv1 responses.
🌐 Browser-based cracking
⌨️ Cross-platform CLI with GPU/CPU support
💾 Searchable tables that fit on a 4 TB disk
Read the blog: https://t.co/fnNqGzJ9O0
Another great RedTreat! Awesome new location and great talks as always. Was really good to catch up with old friends and meet some new ones too.
Thanks @StanHacked, @domchell and @MarcOverIP for putting it all together!
And thanks @CyberSummoner and @max__grim for the badge 🕹️
Had a blast working with my buddy @max__grim creating this badge! Thanks to @OutflankNL and @MDSecLabs for the conf. It was a blast again ❤️ Looking forward to the next one!
New blog: I’m in your logs now: deceiving analysts and blinding EDRs
Based on my BlackHat talk from last year, so you don't have to listen to my voice ;) Some exploration into ETW spoofing and buffer pool exhaustion.
https://t.co/YNpJBYUuP3
#FalconForce#ETW#EDR#Evasion
In a few weeks it is time! Looking forward to meet everyone joining. There are still tickets available @BlackHatEvents to those interested.
https://t.co/2mD07Fu3HM
Very excited to facilitate this training!
Next august, we'll host our newly designed advanced defensive engineering training at @BlackHatEvents in Las Vegas. Next to detection engineering we'll also cover topics like enrichment, lifecycle management and AI. There are still some spot left!
https://t.co/2mD07Fu3HM
Last week, we joined @SpecterOps' SO-CON conference in Arlington, US. It has been an exciting week, with two FalconForce presentations on stage from @_mnigma_ and @olafhartong .
We look back at a great time at SO-CON!
CyberArk is built to protect your crown jewels, but what if it becomes the attack path?
@_mnigma_ shows how misconfigurations in PVWA & CCP can be abused to extract credentials and escalate privileges in just a few steps. #SOCON2026
In one week I will be presenting at @SpecterOps SO-CON 2026 about CyberArk PAM. I will share our practical experience and insights on PVWA edge cases and CCP API misconfigurations. #SOCON2026
More information and registration: https://t.co/dHORi2Jooo
FalconForce is proud to be part of @SpecterOps' SO-CON conference in April.
And this year, there’s not one but two FalconForce talks at #SOCON!
More information and registration: https://t.co/lDO1QFpNux
At FalconForce, we are always looking to enhance our detection engineering practices. In our latest #FalconFriday blog, we present the applied research that was done and our observations on near-real-time (NRT) analytic rules in practice: https://t.co/vDjMWhS3KZ
New year, new training dates! First stop of the year will be at @1ns0mn1h4ck, March 16-18 in Lausanne, Switzerland. Tickets for my Entra ID class are now on sale. More info and registration: https://t.co/DmFc24HKwW
Thrilled to speak at @SpecterOps SO-CON 2026! 🔥 Expect to learn about CyberArk PVWA edge cases & common CCP API misconfigurations to access "hidden" secrets: "4 GET requests = 3 Domain Admins – CyberArk magic you didn't know." #SOCON2026
FalconForce is proud to be part of @SpecterOps' SO-CON conference in April 2026. @_mnigma_ will present a talk on abusing misconfigurations in #CyberArk to get high privileges: “4 Get requests = 3 Domain admins: CyberArk magic you didn’t know about”.
https://t.co/lDO1QFpNux
#MDE custom collection is finally in public preview! It's a centrally managed solution to improve visibility and detection opportunities.
We're releasing a management tool and rule repository in YAML format to share new rules with the community.
https://t.co/kxit8fFjhU