My foundation research on synthetic insider risk is out today with @abovesec.
AI agents can create serious insider risk without stolen credentials, exploits, or malicious intent.
Research:
https://t.co/sEMcKjQ658
Matrix:
https://t.co/cCOmsEjvE0
Took DSO 1 - Mal Dev by @SilentBreakSec at @NorthSec_io. Great training and highly recommended for anyone interested in malware development / attacking framework development and understanding the internals of MS Windows systems in general.
Check out the latest post by @vartaisec. A real-world attack chain walkthrough covering RDS compromise, bypassing AppLocker/Defender protections, lateral/vertical priv esc, and hopping domain trusts. https://t.co/Wr8QZche9h #pentest#ActiveDirectory#remotework
📢New Stealthy Office Persistence Technique📢
Tomorrow night I'll be publishing a new article about a persistence technique in Microsoft's Office. An in-depth explanation of inner workings of Word and a new stealthy implementation! Excited!
#Persistence#T1137#ThreatResearch
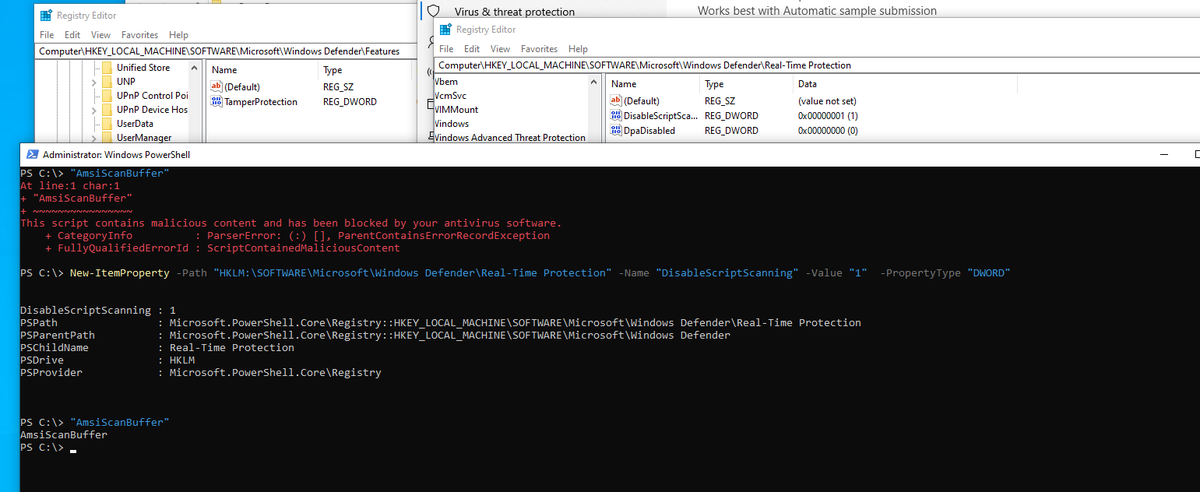
Another way to disable the script engine in win10 1903(rs6) with Tamper protection enabled. the only difference is this method requires you to run PowerShell with TrustedInstaller privs.
win10 1903 Tamper Protection Feature is pretty cool been playing around with it all night. cant kill defender with Set-MpPreference -DisableRealtimeMonitoring $true anymore but, using Set-MpPreference -DisableScriptScanning $true and everything else works.