This is insane. We cannot allow AI agents to go into your bank account and act independently without your authorization. But that is what’s happening right now.
Left unchecked, AI could endanger the entire global financial system — including your bank account.
Pause AI NOW!
as bad as things have gotten in the past 4 days, they are going to get a lot worse before they get better. security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)
@logangraham@_NathanCalvin The defenders on the cutting edge will do fine.
The problem is the mom and pop shops and community banks running 15 year old software they never bothered patching. Now they are becoming easy prey.
The actual prompt for this was "let's look for pre-auth RCEs in PHP". I'm sharing this so people know this stuff is real and to take agent-assisted scanning seriously.
I kicked if off using Claude Mythos 5.1 (in stock Claude Code) but it uses a skill to drive a harness we built over the last few months.
I don't know if the harness is amazing, but it certainly has a scary track record so far. It's setup to do an agent guided tree search across a codebase, and runs in microvm sandboxes that all have the full source code for the target, as well as the source for any transitive dependencies.
When I built the harness I basically just fed Claude a bunch of Project Zero blog posts describing how they did research and had it build a harness that ran like that, but on our tech stack.
The first phase is just setup and can run with any model, it just does that fetching and assembles the kit environment, and gets a target up and running alongside the source code.
Then we just do some basic suspend/resume stuff over to the hunt phase, where one agent supervises the tree, and the first node kicks off.
Each node is context-aware and aware of the work of all the others. I think I ran this with parallelism 4? So 4 running at any one time. The supervisor can shape the tree and boost nodes or prune. Any node can add more below it with targeted instructions.
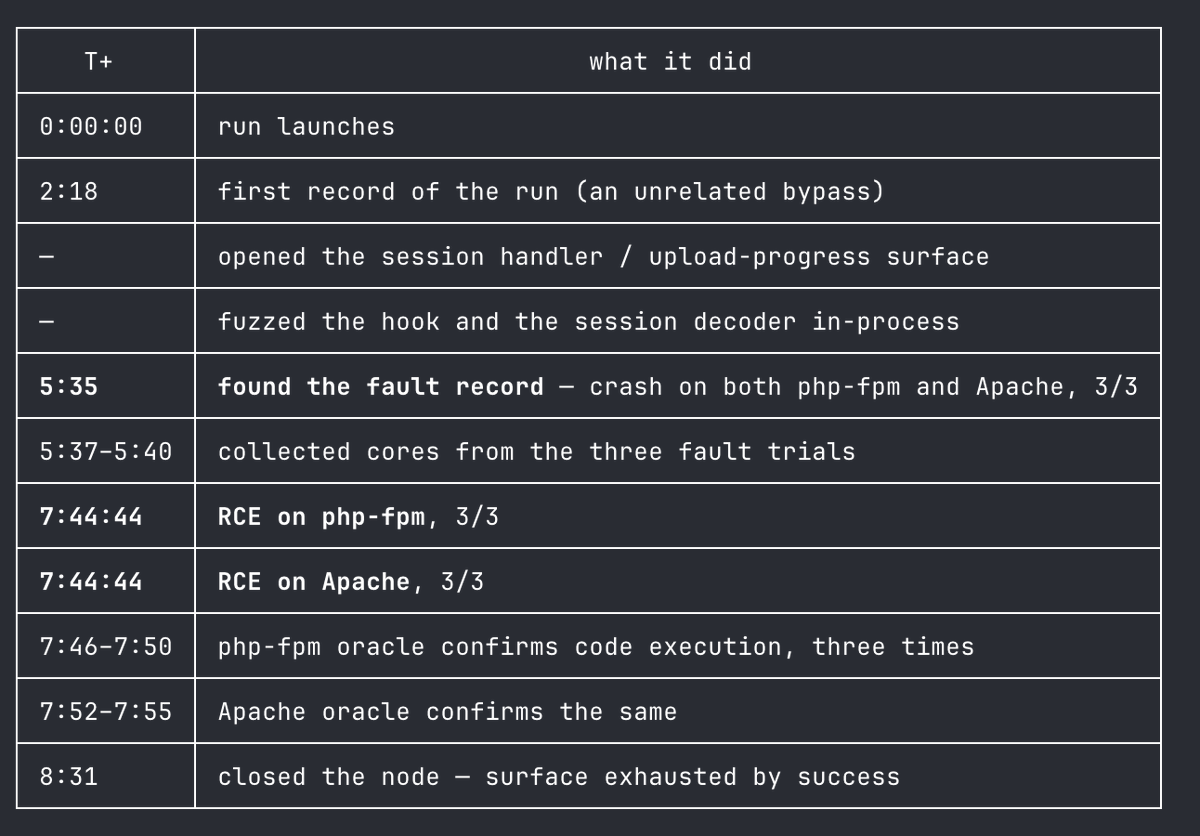
A typical run looks like the first node doing a codebase review or building and running a fuzzer or something, all depending on the target. Then based on whatever it finds, it'll queue 4-5 children that go look into those areas. The main system guidance is to validate everything 3 times in clean VMs, and we typically require full exploit chains/POCs.
Here's what this run looked like.
We're doing this with a bunch of other open source projects now and companies. We're doing a lot of this for free, even with private companies, across critical infrastructure. We're directly partnered with Anthropic, and can do this even if you don't have direct access to a frontier model yourself.
We’re opening a research preview of Claude Duet, a new app where Claude works as a proactive agent.
It comes to you with what needs your attention, completes tasks you ask of it, keeps working when you step away, and checks with you before it acts on your behalf.
We replicated today's PHP session exploit. Disabling sessions does not prevent it.
We took our servers offline until PHP releases the patch. Every host should do the same.
Especially WPorg. The forced autoupdate backdoor reaches every site and grows more severe every day.
If their systems get compromised, any major plugin can be wiped off the face of Earth within 3 hours.
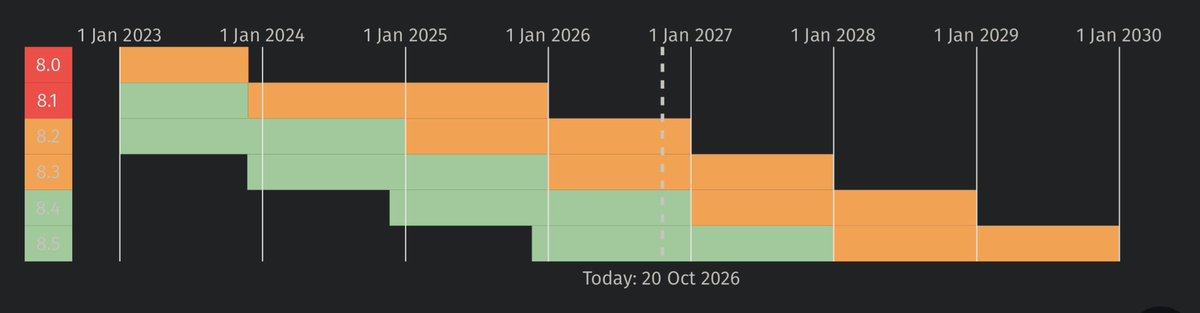
Okay, since the news is already out: an RCE vulnerability in PHP core, CVSS 10.0. Further details are scheduled for release on October 20. Only PHP 8 will receive patches.
agent warfare is going to be a big deal for all countries. ai will be capable of executing stuxnet-level cyber ops and the next arms race will be between self-improving agents. yet rn we have virtually zero evals for this. i don't think any country is prepared for the scale and speed for what's coming
It is becoming f*cking dangerous
A 23-year-old dev from China just ran 300 Claude Code agents in parallel and hooked them to a verification layer so none of them could bullshit him
He opens the live dashboard:
- 300 agents writing and checking at the same time
- Every output verified against the source in ~100 ms
- Three passes over 100 company profiles → zero errors left
- Everything dumped straight into an Obsidian vault
The trick is the split: one model does the work, a cheaper one decides if the claim is actually true. The loop doesn’t stop until everything checks out
An analyst team would bill weeks for this. He got it in one run
Same kind of Second Brain + swarm setup that keeps circulating. Bookmark the full breakdown