Dr. Russell Barkley’s blunt truth to parents of ADHD kids: Stop talking. Start acting. Your child’s brain needs external consequences and accountability — not more lectures.
In this 8:08 clip he lays out the practical playbook:
- Be radically consistent with rules and immediate consequences (ADHD is not an “information deficit”).
- Touch, look in the eye, keep it short and sweet — then enforce.
- Use timers to proactively check on them and catch problems early.
- Break tasks into tiny chunks (reduce expected attention span by ~30%).
- Use “time off the clock” accommodations (stopwatch they control) instead of useless “extra time.”
- Do transition planning before every change of activity: stop, review rules, state incentives/punishments, get their input.
- Use behavior monitoring cards everywhere (school, sports, grandparents, babysitters) — frequent ratings from other adults, points delivered at home.
The core message:
Reactive parenting = constant firefighting.
Proactive structure + external accountability = dramatically fewer problems and a less disabled child.
This isn’t about “fixing” ADHD — it’s about engineering the environment so the child can succeed despite it.
Which of these strategies have you tried (or wish you’d known sooner) with an ADHD child?
Recently @smica83 posted on X some information about a relatively low score file uploaded from Romania.
This is the malware analysis conducted on the file.
https://t.co/ouVfyl1fvS
#CyberSecurity#ThreatAnalysis
If you want to focus on Linux security and malware in particular, you better learn C, shell scripting and Python. Knowing network protocols also a requirement.
Astăzi a fost Duminică, dar nu ne-am odihnit. Ne-am întâlnit cu Remus Cernea (https://t.co/AjYTMSAr0G), Alex Craiu din partea @Veridica1 si Bianca Bulgaru din partea https://t.co/txFdaCEpLt Getotac a răspuns separat la întrebările fiecăruia și o să avem se pare o săptămână viitoare de mediatizare intensiva a Getica, dacă ținem cont și de interviul de săptămâna trecută pentru un cotidian cu acoperire națională. Clipul de mai jos a strâns 30000 de vizualizări in două ore, pe TikTok și sperăm că mesajul nostru ajunge in Romania cat se poate de sincer și obiectiv.
----------------------------------------------------------
Fiecare contribuție contează!
Donațiile voastre vor susține organizarea activităților de instruire, achiziția de echipamente necesare și implementarea proiectelor noastre. Împreună, putem construi o Românie mai puternică și mai pregătită pentru viitor. Donează acum și alătură-te misiunii noastre:
https://t.co/htwyPzlI9O
Adrese crypto:
BITCOIN
1ApaRegQL7ko99oWQ3X6EQcisUZfnXUP3x
ETHEREUM
0x293D2503fbbB419BC5c4624ABb63B35B0B4814C7
MONERO
4B6pK9gTQUtJjsVdbYL5iwdJUoih8hGTmX2XY9dwhsnoAsMUTpZy8Jd8ZcW1TXMfrH2DGV66BEpJLaZUF9yvP5b52UJ34Ti
This new Linux script from THC will encrypt and obfuscate any executable or script to hide from on-disk detection. I'm going to show you how to detect it with command line tools in this thread.
https://t.co/5BkzpPBHv5
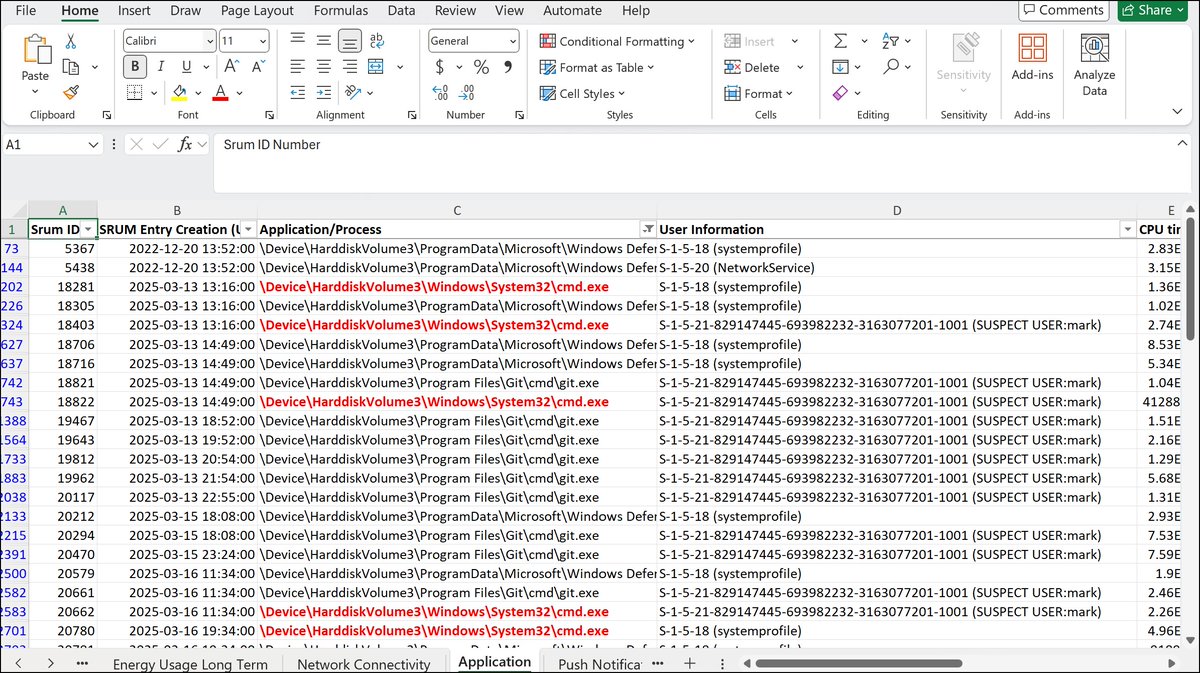
Exciting news for the forensics and incident response community! I'm thrilled to announce the 3rd BETA release of SRUM-DUMP v3. This powerful tool leverages Windows SRUM (System Resource Usage Monitor) to uncover malicious process execution over the past 30 days.
Key features include:
- In-depth analysis of SRUM data.
- Easy to use wizard
- Quickly identify malicious processes & users with dirty word tagging
- Output in both XLS and CSV formats for easy reporting.
This BETA is a significant step forward, and I'm eager for your feedback! It is now the version3 branch of the SRUM-DUMP repo. Give it a spin: https://t.co/wDGPBzVmL8
Let's make incident response faster and more effective! #DFIR #Forensics #IncidentResponse #WindowsSecurity #Cybersecurit @ovie@sansforensics
We've seen old-school default Linux users enabled by intrusions. You'd be surprised how long an account like "lp" or "uucp" can hang around unnoticed with a password. In this video I go over this threat and what to look for to find it.
A ieșit ideologul lui Putin să spună că: "România va fi parte din Rusia!". Candidatul Calin Georgescu este susținut fățiș de Dugin. Și uite așa se vede cu ochii limpezi dragostea Kremlinului pentru candidatul lui Putin pe teritoriul României. Ce voiam eu să spun este altceva și sper să se audă până la acest Rasputin de mâna a doua: România nu a fost și va fi niciodată parte din Rusia. Duminica aceasta toți românii trebuie să spună asta răspicat: România este Europa - România nu este Rusia.
* Același Dugin l-a descris pe tovarășul Călin Georgescu drept un ‘politician remarcabil’. Mai mult: ‘Și dacă, prin voia lui Dumnezeu, acest candidat patriot, Călin Georgescu, va câștiga, Moldova nu va avea unde merge. Dacă se îndreaptă spre România, vor ajunge mai aproape de un bloc aliat cu noi. Aceste rezultate sunt foarte importante și neașteptate. Toată lumea credea că va câștiga un naționalist român clasic, mai puțin favorabil Rusiei."
Dați mai departe și spuneți-le oamenilor să meargă la vot duminică!
1. Mihai Viteazu
2. A.I Cuza
3. MSR Carol I
4. MSR Ferdinand I
5. MSR Carol II
6. MSR Mihai I
7. C-tin I. Parhon
8. P. Groza
9. I. Gh. Maurer
10. Gh. Ghe. Dej
11. C. Stoica
12. N. Ceaușescu
13. I. Iliescu
14. E. Constantinescu
15. I. Iliescu
16. T. Băsescu
17. K. Iohannis
18. ???
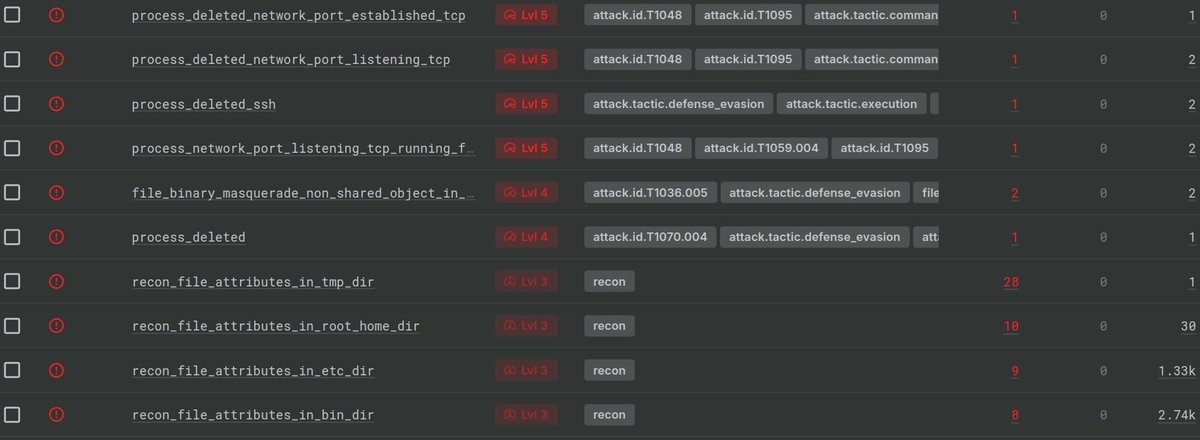
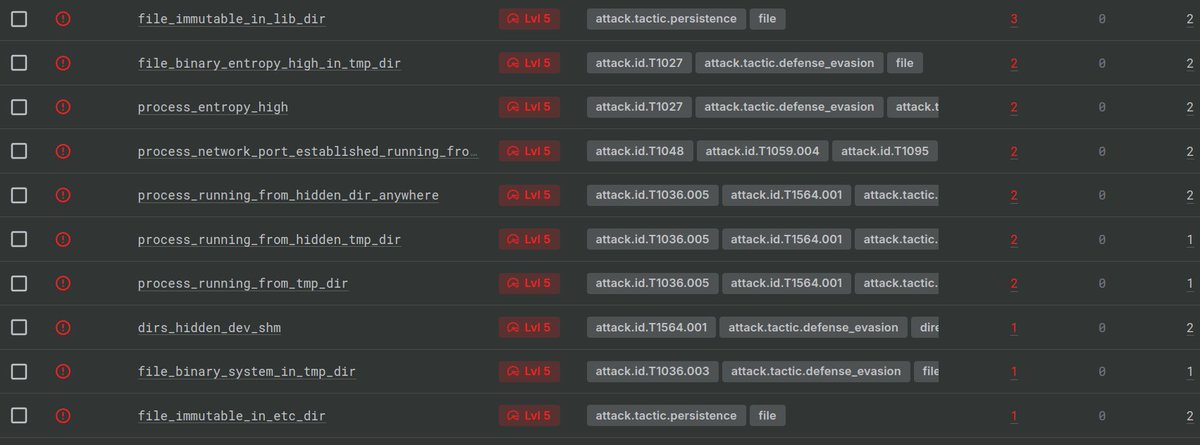
The perfctl Linux malware reported by @AquaSecTeam now holds the record for largest number of alerts ever seen by Sandfly post-compromise. The malware has some stealth, but mostly it's just hyper-aggressive at staying around. Here is a quick rundown.
Windows doesn't verify the file extension if the file is executable, allowing malicious actors to spoof files and evade detection (PE files)
A POC script for generating the payload more efficiently has been uploaded to: https://t.co/q1DUWPFFLY
Today's Training Tuesday Highlight is @binaryz0ne!
He has several great DFIR videos on his YouTube channel! He also created FREE DFIR challenges! In addition, he has talks and workshops on GitHub related to Linux Forensics, Windows Forensics and more!
He also co-founded @cyber5w. Check out the previous Training Tuesday Highlight for Cyber5W here: https://t.co/a14ho1Vf8d
Links:
YouTube: https://t.co/PFUvvpxhrG
GitHub: https://t.co/j1TdSGIya4
DFIR Challenges: https://t.co/3vOqNxorqB
#DFIR #IncidentResponse #DFIRDivaTTH
@DfirDiva@13CubedDFIR@davisrichardg with @13CubedDFIR are a constant resources of knowledge on DFIR. Last year I went through Window Endpoint investigation and it was a game changer. Everything was perfectly described and just in time. I highly recommend @13CubedDFIR training and YouTube videos.
🎁 GIVEAWAY! 🎁
I partnered with @13CubedDFIR for a giveaway of his Investigating Windows Bundle!
This bundle includes 365-day access to the Investigating Windows Endpoints & Investigating Windows Memory courses. It also includes a certification attempt for each!
To Enter: Like, Repost, and Leave a Comment.
On September 28th, entries will be combined from both LinkedIn and Twitter(X) and a winner will be selected and announced.
Learn more about the Investigating Windows Bundle here: https://t.co/ElUg3beE3i
#DFIR #DigitalForensics #IncidentResponse