“Obsession” (2026), is an allegory for bad prompting and misaligned AI.
If Bear had phrased his One Wish Willow request with proper safety constraints (“while remaining herself, happy, and not a demonic entity”), the whole movie would’ve been a rom-com.
I doubt it.
As I said before, we're going full Agorist.
Remember the Clarity act BS?
The crypto market specifically has decided we're going full agorism mode, we don't give a fuck anymore, we already priced in the collapse of the government.
Stockcucks should be worried tho, not us.
Zigher
ZeroCash, the previous name for the project, had all these intelligence agencies funding it along with in-Q-tel, unless I am somehow mistaken?
It's a bjt strange the zerocash team also mentioned making backdoors or having the ability to make backdoors, since it seens like that'd be very hard ti find in an audit if its just a solution to decrypt the ZKPs, r-right?
@CryptoCyberia cybercriminals use Bitcoin all the time as well. They have methods for laundering bitcoin that sidestep the need for robust ledger secrecy.
it's not particularly interesting that criminals find monero to be "slightly better than bitcoin"
sounds like they simply have bag bias
@CryptoCyberia you might've been talking to feds who were pushing you to use something that will have the entirety of its transaction graph revealed the moment someone gets a quantum computer
in a very real sense, it's a blessing ZEC wasn't adopted prematurely
yeah, some overlap in the team, and while the exact cryptography has evolved a lot over the years, insights from zero-cash remain in modern Zcash and in many other protocols like TornadoCash, which suffered and survived a much worse crackdown than Monero, making XMR look like a toy.
"decrypt the ZKPs" is not a statement that makes sense.
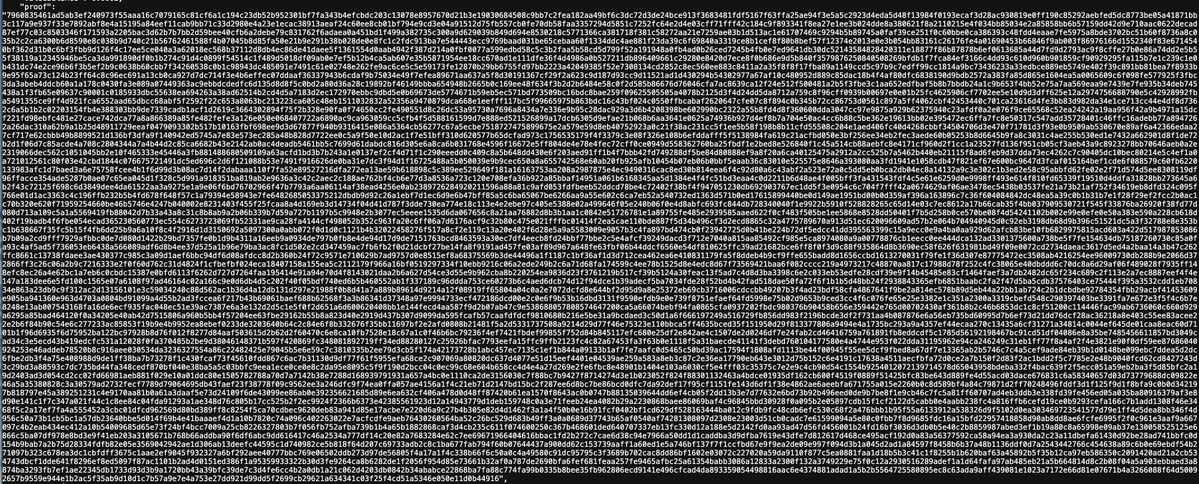
You are implying there exists a way to recover the private witness from the proof data, typically 5 kB mostly comprised of Vesta curve points and Vesta scalar field elements.
Mathematical proof of this infeasibility are included in the papers and audits- but even if the rigorous proofs of its zero-knowledge property were wrong, that still doesn't imply an attack exists.
Here's one from a recent transaction. If you want to recover the private witness from this, how would you go about doing it? What would be your approach?