🚨 Google reveals undercover Mandiant analyst infiltrated TeamPCP during massive supply-chain hacking spree
Google says an undercover Mandiant analyst infiltrated TeamPCP's inner circle as the hacking group compromised open-source software and ultimately breached more than 1,000 companies.
⠀
The analyst gained access to TeamPCP's core "CanisterWorm" chat in March, joining a group of roughly 12 members and watching the operation from the inside.
⠀
The mole also gained access to a server containing credentials stolen from victims, including usernames, passwords, and access tokens.
Google used that visibility to alert cloud and technology providers, revoke compromised credentials, and send hundreds of notifications to affected organizations.
⠀
The operation also exposed a TeamPCP member developing an AI-assisted zero-day capable of bypassing two-factor authentication in widely used login software.
Google obtained the exploit code, verified that it worked after minor modifications, and privately notified the developer so the vulnerability could be patched.
⠀
TeamPCP's campaign compromised hundreds of open-source packages and affected organizations including GitHub, Mistral AI, Mercor, the European Commission, and employee devices at OpenAI.
⠀
Google says operational security mistakes later helped investigators identify an alleged TeamPCP member, with information passed to the FBI.
Two Australians accused of being principal participants in TeamPCP were arrested last month.
‼️ Researchers broke Intel TDX’s confidential-computing protections with a $159 DDR5 interposer.
New "DDRop" attack silently drops memory writes so the CPU trusts stale encrypted data. In lab tests, researchers read protected VM memory and forged attestation.
No CVE. No patch. Full details here → https://t.co/cHAX1ojqpI
@HDFCERGOGIC Raised my first reimbursement claim in 7 years (₹60K+ annual premium) — it’s been over a week, and still no resolution.
No ownership, only auto-replies.
RM says “limited access.”
Doctors reviewed it — still stuck.
Not a single call back to understand the issue or the pain the
@HDFCERGOGIC Raised my first reimbursement claim in 7 years (₹60K+ annual premium) — it’s been over a week, and still no resolution.
No ownership, only auto-replies.
RM says “limited access.”
Doctors reviewed it — still stuck.
@HDFCERGOGIC@pmfby 🔴 Extremely disappointed with @HDFCERGO
Raised my first reimbursement claim in 7 years (₹60K+ annual premium) — it’s been over a week, and still no resolution.
No ownership, only auto-replies.
RM says “limited access.”
Doctors reviewed it — still stuck.
Are you the type of admin who likes to update right away, or do you prefer to delay updates?
Check out our latest blog and take control of how and when your Android Enterprise corporate devices receive system updates: https://t.co/Oq7rp8H5ui
#MSIntune#AndroidEnterprise
Great news! Azure Virtual Desktop Watermarking Support is now Generally Available (#GA). Watermarking provides an optional protection feature to Screen Capture that acts as a deterrent for data leakage. Read this awesome blog from Ryan Clark to learn everything about it. ⬇ https://t.co/6J1Pdwck2U
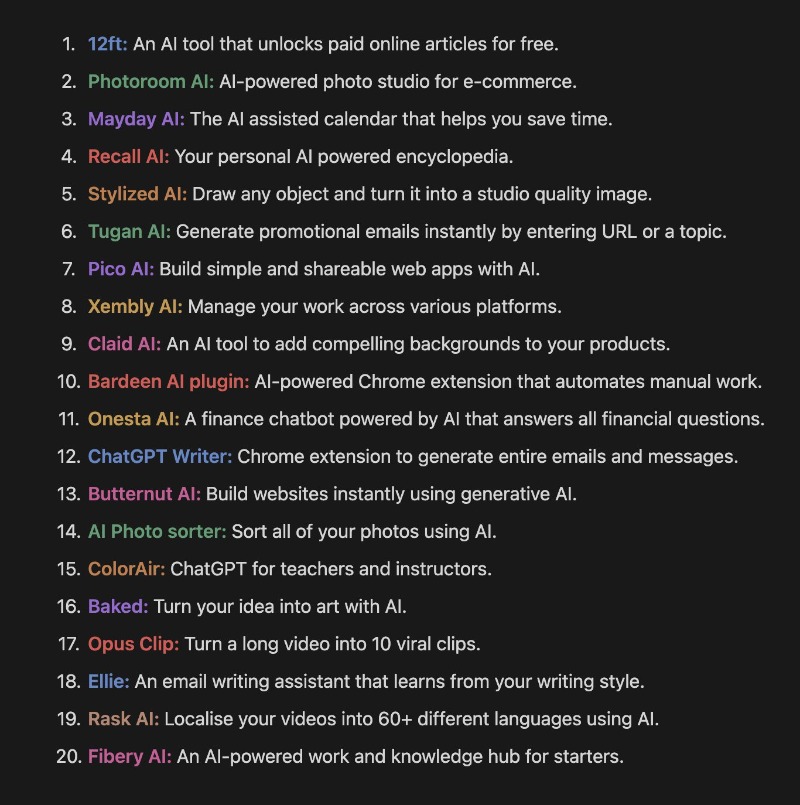
Using the right AI tools is like having your own personal army of robots.
20 AI tools to supercharge your productivity:
If you want tools and insights about AI, follow along for more.
What’s new in Microsoft Intune 2307 (July) edition: In our July 2023 service release (2307), we're adding some major capabilities to Microsoft Intune. First, we’re enabling users to uninstall Windows apps in the Intune Company… #MSIntune#SCCM#MEM https://t.co/T8pxeDiRyo
Intune Offboarding Tool
This PowerShell script provides a WPF GUI-based tool that facilitates the offboarding of devices from Microsoft's #Intune, #AutoPilot, and #AzureAD services. The tool leverages Microsoft Graph APIs to authenticate, search, and remove devices.
Every Microsoft 365 admin/infosec team should already have a variation of this as a baseline policy or at the very least planning on deploying this.
Did you know this policy gives you protection from most phishing attacks?
To learn more about how you can deploy this see
https://t.co/jstX5cJOFE
Yes. This requires a TON of work if you don't already have an MDM solution or hybrid joined devices.
It is ABSOLUTELY worth the effort. You can start with small groups of users and expand. See this guidance for privileged accounts: https://t.co/UmZrpbIk65
PS: You would typically need to make exclusions for guests, break glass accounts and BYOD devices. They should be 'exclusions' though with session controls and access reviews applied on them.
Do you already have this deployed? Congratulations! You are a PRO!