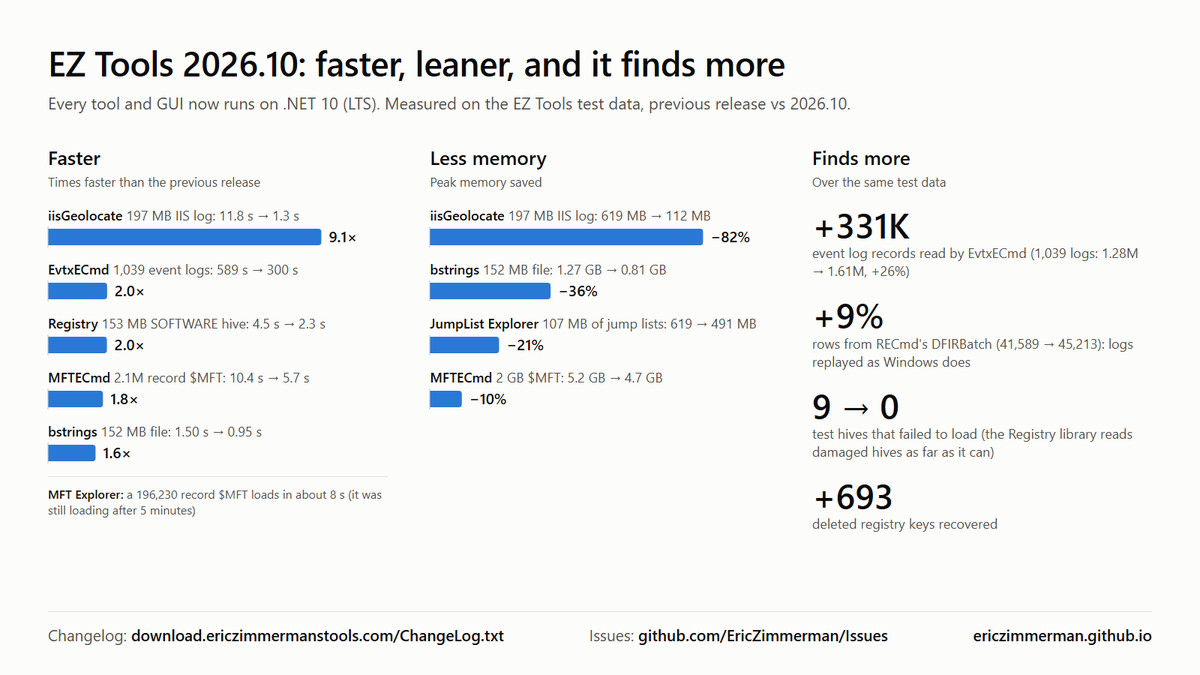
1/ EZ Tools 2026.10 is out, all on .NET 10 (LTS)
✅ More accurate: 331K more event log records, hive logs replayed as Windows does, every test hive loads
⚡ Faster: up to 9x; EvtxECmd and Registry 2x
📉 Less memory: up to 82% less
Update with Get-ZimmermanTools 🧵 #DFIR
@malmoeb Honestly, this isn't as rare as it seems. It depends on how mature the market is where the incident occurred. Sometimes total destruction leaves no firewall logs or machines, so creativity—not tools—saves you. I wonder how top DFIR experts from mature economies would handle it.
Provides 7 new IP addresses potentially connected to the mentioned group:
38.180.235[.]177
91.107.163[.]28
91.199.147[.]252
141.11.123[.]56
185.125.202[.]145
185.162.250[.]87
188.245.58[.]123
All with good reputation.
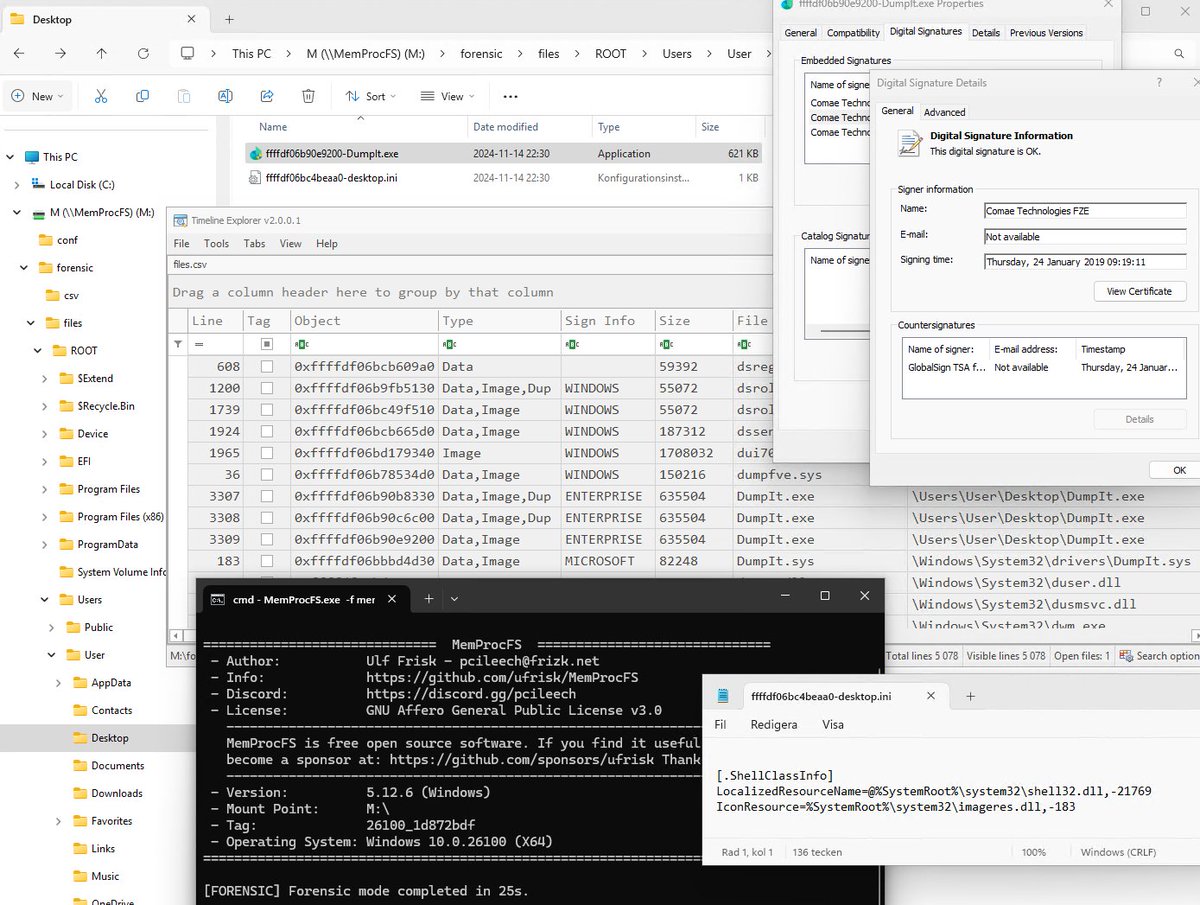
Improvements to MemProcFS forensic file recovery in 5.12.6. More data is now recovered, with correct file sizes, and with file signing info!
MemProcFS super fast memory forensics and analysis: https://t.co/inOM3l2eyd
MemProcFS memory forensics now supports Windows Hibernation Files!
Thank You @k1nd0ne for your excellent blog entry about the file format!
https://t.co/inOM3l1GIF
Just started work on a new tool. Native sigma scanner for cloud logs. (Starting with AWS first). (Basically Hayabusa for cloud logs) It should be out later this year. Please contact us if you do AWS DFIR/Threat Hunting and are interested in helping out.
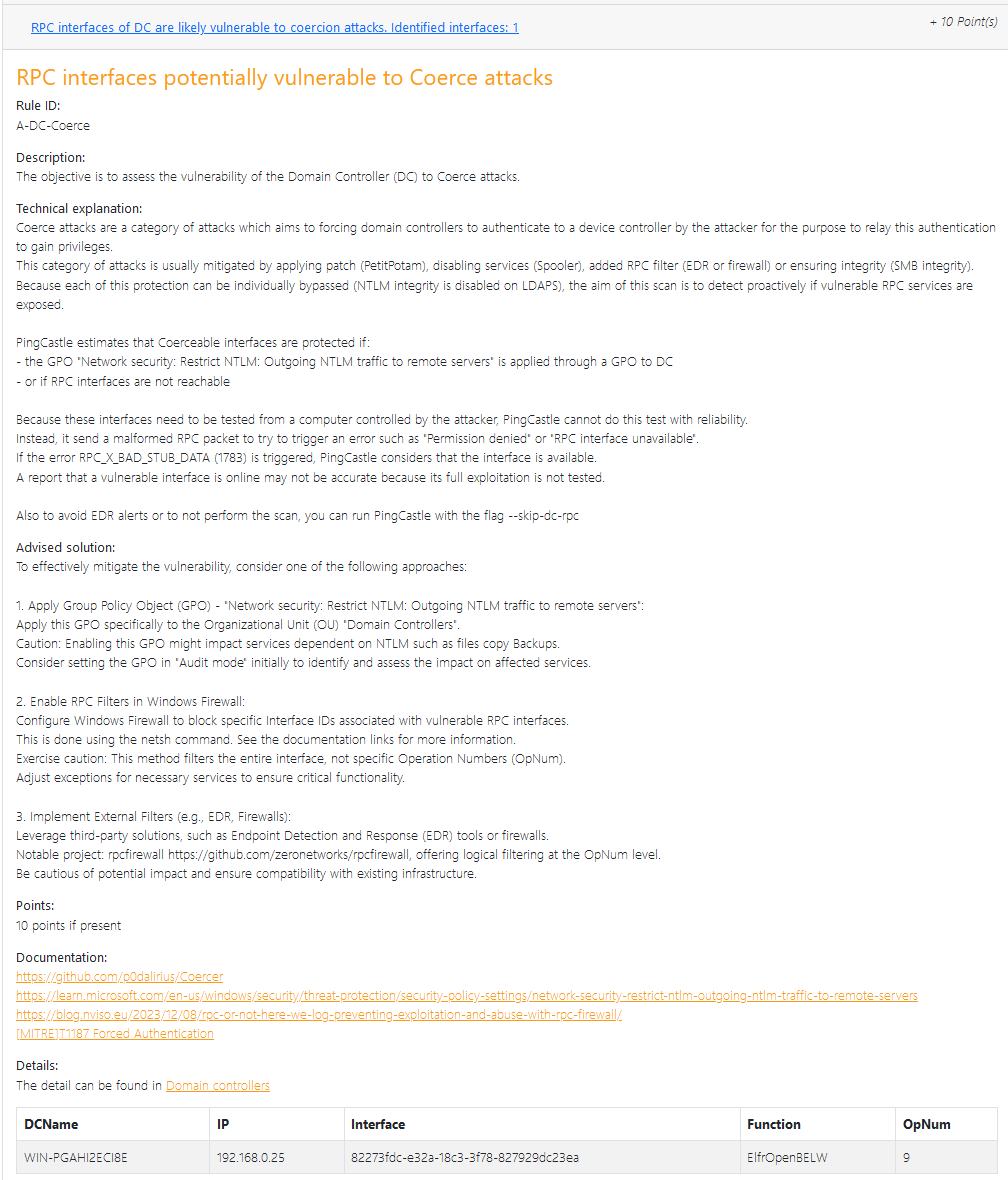
I've added the rule A-DC-Coerce to test for potential vulnerability of Coerce attack (https://t.co/mj5HptSfIf)
Feedback of the wording / logic welcomed before the imminente release of the next Beta of PingCastle.
However, I'm puzzled as to why I couldn't find a similar rule in the Sigma public repository or in any public paper—there's only one for 4769. What might I be overlooking, and what are the potential pitfalls?
While experimenting with the S4U2Proxy Kerberos extension, I discovered a distinctive 4624 event on the destination with a populated transited service field.