🚨 PoC RELEASED: A public PoC is now available for CVE-2026-94545, a critical Next.js RCE vulnerability in the Node.js implementation of ImageResponse (CVSS 9.5).
An unauthenticated attacker can inject crafted SVG markup through attacker-controlled values, potentially leading to arbitrary code execution with the privileges of the Next.js server process.
⚠️ Affects Next.js 16.2.0–16.3.5.
🔴 Fixed in Next.js 16.3.6. Update immediately.
PoC: https://t.co/TS2R93sMEk
Source: https://t.co/uyAvMe9WkB
#CVE #CyberSecurity #InfoSec #NextJS #NodeJS
⚠️CVE-2026-85706 (CVSS 10.0)⚠️
Your GitLab will hand a stranger its files. 😱
No login. No account. An attacker just URL-encodes one letter of commits → %63ommits, and GitLab-Workhorse waves the request through — so a single unauthenticated POST to the repository commits API reads files straight off the server filesystem. Config, internal logs, source paths, versions… all without ever signing in.
Already in CISA KEV — exploited in the wild. 🚨
If you self-host GitLab, patch to 19.1.8 / 19.2.6 / 19.3.2 now.
🔥PoC + setup: https://t.co/qgJaKGxJ04
#GitLab #ArbitraryFileRead #CVE #PoC #Exploit #CyberSecurity #CVE_2026_85706
35 WEBSITES GOOGLE DOESN'T WANT YOU TO KNOW
1. Explee .com — sends cold emails on autopilot
https://t.co/stniMlW9jN
2. NoteGPT — turns docs into podcasts
https://t.co/LnV8bZbYZO
3. Napkin AI — turns text into diagrams
https://t.co/AnkuX7aOdd
4. Ideogram — generates text in images perfectly
https://t.co/0DXFIzvLjn
5. Suno — makes full songs from a prompt
https://t.co/VjO6GxCOib
6. HeyGen — clones your face into videos
https://t.co/XrUTh8llTO
7. Kling AI — best AI video generation
https://t.co/5Cn0KJka61
8. ElevenLabs — clone any voice instantly
https://t.co/ftGCJjICdf
9. Gamma — AI presentations in seconds
https://t.co/QMla9avM3T
10. Perplexity — AI search with real sources
https://t.co/ansIDk2EBM
11. Pika — animate any image into video
https://t.co/Q4pnxHlWS5
12. Runway — cinematic AI video generation
https://t.co/GQuTAgs5BC
13. Cursor — AI code editor that builds for you
https://t.co/3eApj9WntR
14. v0 — generate UI components with AI
https://t.co/mYZP1mnv48
15. Lovable — turn ideas into working apps
https://t.co/bX5DVwQLf2
16. Descript — edit video by editing text
https://t.co/7ryIZGTlRX
17. Opus Clip — auto cut long videos into shorts
https://t.co/B5RaFRp4pP
18. Krea AI — real time AI image generation
https://t.co/Mn2DjN1aWS
19. Magnific — upscale any image with AI
https://t.co/u4YSRlffpH
20. Viggle — make characters move realistically
https://t.co/q5uOCPYiqv
21. tl;dv — record and summarize any meeting
https://t.co/qHCXf1l3Lj
22. Fireflies — AI meeting notes automatically
https://t.co/lSRFVMFqwm
23. Castmagic — turn audio into content pieces
https://t.co/XCpaWm04YI
24. Replit — code and deploy from browser
https://t.co/sBjAq4aEzV
25. Leonardo AI — generate images for free
https://t.co/GVjRiLrNYs
26. Synthesia — AI avatar videos no camera needed
https://t.co/7TaVCXE0du
27. Fliki — turn text into videos with AI
https://t.co/b0bQhZgf96
28. Photoroom — AI product photography
https://t.co/7c8T6P0Sil
29. Invideo AI — turn prompts into full videos
https://t.co/8xbzjsU9il
30. Consensus — search what science agrees on
https://t.co/2nSQ6SSev8
31. SciSpace — understand any research paper
https://t.co/61vY5QRjUl
32. Tome — AI builds your pitch decks
https://t.co/5kpDkv3MFp
33. Beautiful AI — smart presentation design
https://t.co/d5H9kyhUBv
34. Meshy — turn text into 3D models
https://t.co/xSUe3G34J1
35. Vizcom — turn sketches into renders
https://t.co/BgHvCAjbUc
The AI revolution isn't coming.
It already happened and you missed half of it.
🚨 EXPLOITED IN THE WILD: CVE-2026-48842 — High-severity pre-authentication SQL injection in Roundcube Webmail (CVSS 8.1).
The flaw affects the virtuser_query plugin and can allow unauthenticated attackers to manipulate database queries through a backslash escaping bypass.
⚠️ Affects Roundcube 1.6.x before 1.6.16 and 1.7.x before 1.7.1.
🔴 Update to Roundcube 1.6.16 or 1.7.1.
PoC: https://t.co/EvXKu5DPQt
Source: https://t.co/amL4wBVByj
#CVE #CyberSecurity #Roundcube #SQLInjection #Infosec
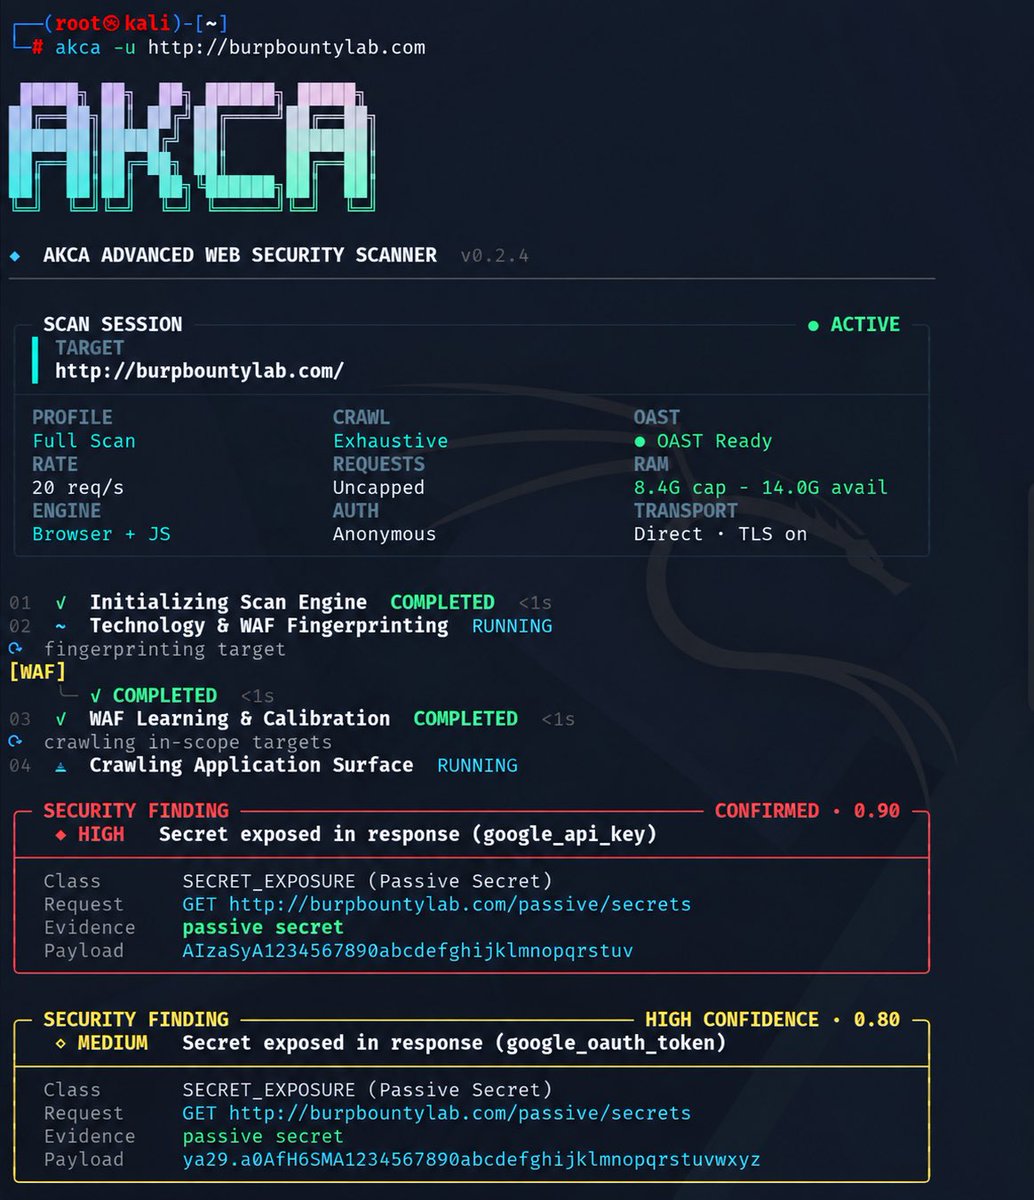
👾 AKCA - Advanced Web Security Scanner
AKCA is an open-source, evidence-oriented Dynamic Application Security Testing (DAST) scanner written in Go. It combines HTTP and browser-assisted crawling, JavaScript analysis, API imports, adaptive active testing, passive inspection, and replayable evidence in one command-line workflow.
https://t.co/R4HruJLn55
By - @caneraktas_
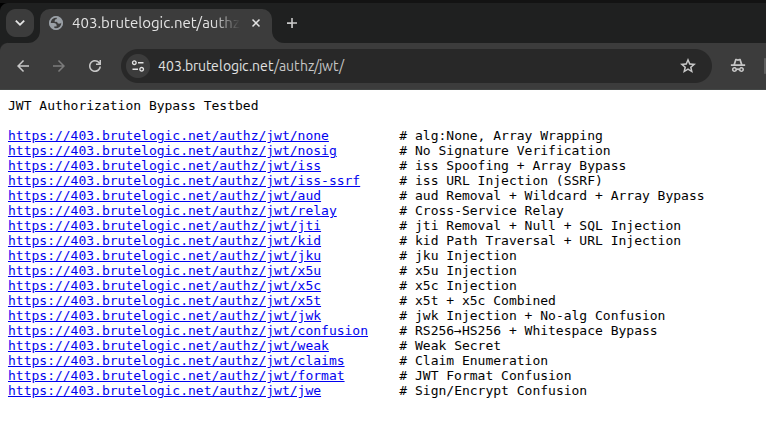
JBroken - JWT Authorization Bypass Tool
JBroken is our proprietary tool backed by our testbed in 23 cases that came from the ebook.
Be in touch if you are interested to use it via an API along with other tools.
Check all the info we provide below.
DORK: intext:@"yahoo|gmail|outlook|hotmail".com (filetype:xls OR filetype:csv OR ext:xlsx OR ext:txt OR ext:sql) site:*.gov
----------------------------------------------------------
Not gonna lie, this single google dork I made has given me SO much exposed PII from self-hosted programs and some .gov, .edu, .int and .mil domains.
Use it for BBP targets. If it helps you find something interesting, come back here on X and thank me.
Also, make sure you run this on Bing. Google has fixed/changed some search operators so it will not work.
When you encounter a 403 Forbidden page 🚫 ,try adding an "X-Client-IP" header in your request with the value "127.0.0.1"
X-Client-IP: 127.0.0.1
OR
curl -I https://target[.]com/.env -H "X-Client-IP: 127.0.0.1"
It doesn't always work, but worth trying. 🎯
#bugbountytips
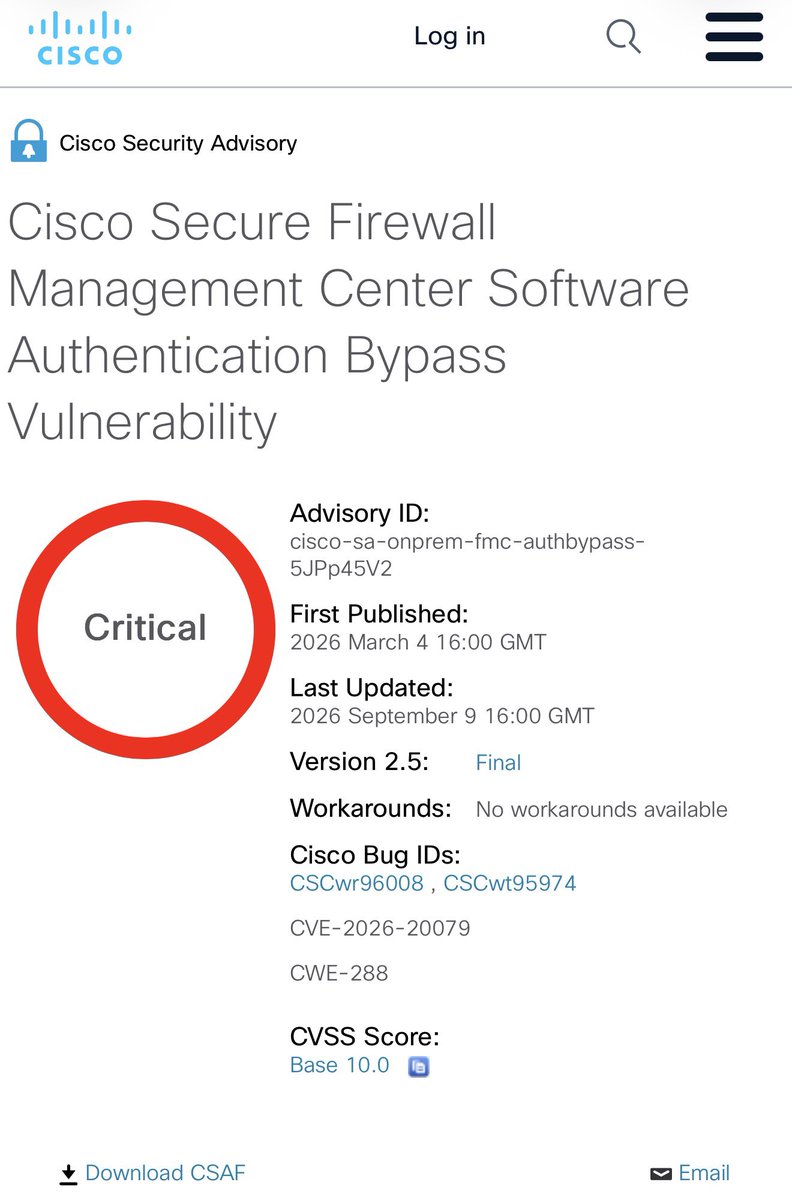
🚨 CISCO FIREWALL VULNERABILITIES ACTIVELY EXPLOITED — ROOT ACCESS, CYCLOPS BLINK AND QILIN RANSOMWARE OBSERVED
Cisco Talos has confirmed active exploitation of two vulnerabilities affecting Cisco Secure Firewall Management Center (FMC).
The most serious:
CVE-2026-20079
CVSS: 10.0 — CRITICAL
The vulnerability allows an unauthenticated remote attacker to bypass authentication and execute scripts and commands that can provide ROOT access to the underlying operating system.
Cisco says the vulnerability is being actively exploited in the wild.
A second vulnerability, CVE-2026-20316 (CVSS 5.3), exposes static credentials for a low-privileged account and has also been actively exploited.
But the post-exploitation activity is where this becomes particularly interesting.
Cisco Talos identified THREE distinct intrusion clusters.
🔴 Cluster #1 — UAT-12197
Attackers exploited CVE-2026-20079 and deployed:
* Web shells
* JAR-based command execution
* Credential harvesting
* Data exfiltration
🔴 Cluster #2 — UAT-11823
Attackers exploited the FMC vulnerabilities and ultimately deployed CYCLOPS BLINK.
Observed capabilities included:
* Reverse shells
* Credential harvesting
* Configuration theft
* Network reconnaissance
* Packet sniffing
* File upload/download
* Arbitrary command execution
Cyclops Blink has previously been attributed to Russia's Sandworm APT by U.S. and UK authorities.
Cisco says UAT-11823 overlaps in tooling with Sandworm, but does NOT directly attribute this cluster to Sandworm.
🔴 Cluster #3 — UAT-11988 / RANSOMWARE
Cisco assesses with HIGH CONFIDENCE that this actor is a ransomware operator.
After gaining access to FMC, the attacker:
* Conducted extensive internal reconnaissance
* Harvested Active Directory and MySQL credentials
* Enumerated domain infrastructure
* Established SOCKS5 and reverse-SSH tunnels
* Used Impacket and Invoke-TheHash
* Deployed custom AV killers
* Identified endpoints for encryption
The intrusion ultimately resulted in QILIN RANSOMWARE being deployed on selected endpoints.
Talos says the actor's TTPs were consistent with Qilin ransomware affiliates.
⚠️ Analyst Note:
Compromising security infrastructure creates a particularly dangerous situation.
The device intended to protect and manage the network becomes the attacker's foothold:
Internet-facing FMC
→ Root access
→ Credential harvesting
→ Internal reconnaissance
→ Network tunneling
→ Lateral movement
→ Ransomware deployment
Cisco has released hotfixes and strongly recommends applying them immediately.
There are NO workarounds for CVE-2026-20079.
Organizations running Cisco Secure FMC should treat this as an active-compromise scenario, not simply a patch-management exercise.
Patch immediately — and investigate whether exploitation occurred before remediation.
Official Cisco Talos research:
https://t.co/XBjP1YWc9H
Official Cisco Security Advisory:
https://t.co/RZHoXIDxyG
#DDW #Cisco #Qilin #Ransomware #CyberSecurity
url/?f=etc/passwd ==> 403
encode etc/passwd as base64
url/?f=L2V0Yy9wYXNzd2Q= ==> 200
#note
you can use this trick in SQL , SSTI , XSS , LFI , Etc...
Credit: @GodfatherOrwa#bugbountytips#bugbountytip
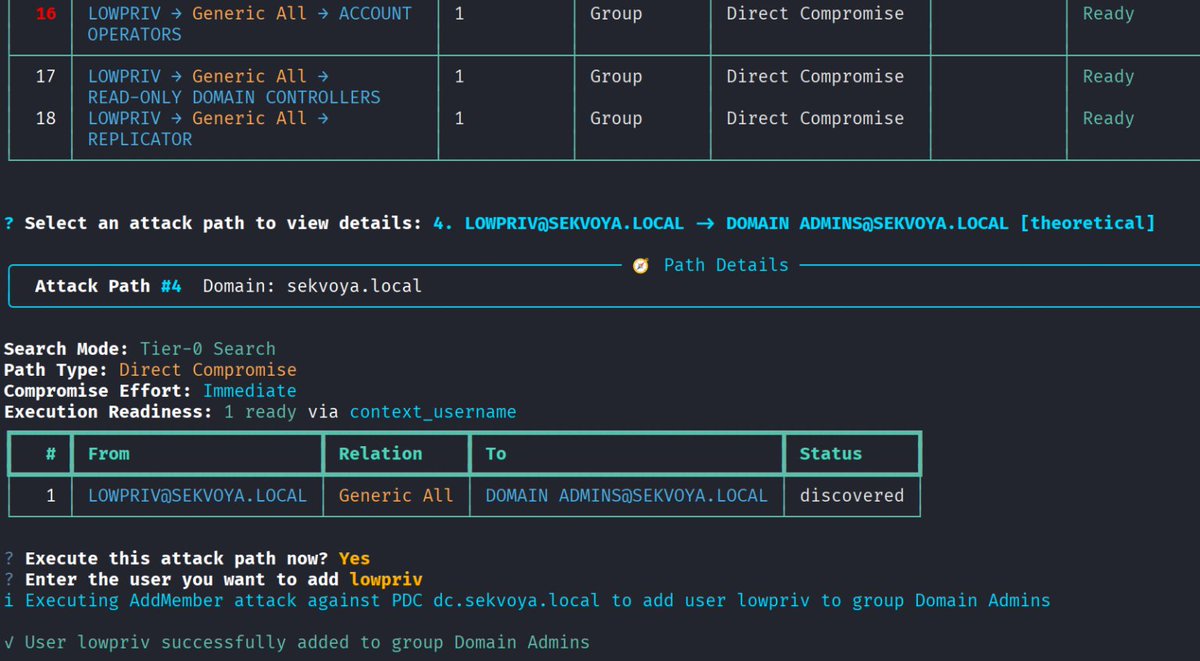
Active Directory Pentest with ADScan and ADPulse
Active Directory pentesting often starts with the same repetitive checks, but ADScan and ADPulse can help you automate them.
Unlike many other projects, ADScan doesn't need AI or any APIs. It can find privilege escalation paths and compromise the entire domain
https://t.co/r6qq1YRvOP
👾 DeepTeam - The LLM Red Teaming Framework
DeepTeam is a simple-to-use, open-source red teaming framework for LLM systems. Think of it as penetration testing, but for LLMs.
DeepTeam simulates attacks — jailbreaking, prompt injection, multi-turn exploitation, and more — to uncover vulnerabilities like bias, PII leakage, and SQL injection in your AI agents, RAG pipelines, and chatbots. It also offers guardrails to prevent these issues in production.
DeepTeam runs locally on your machine and is built on DeepEval, the open-source LLM evaluation framework.
WHOEVER BUILT THESE AI HACKING TOOLS WAS NOT PLAYING
And the crazy part?
They don’t just scan for vulnerabilities.
They can actually simulate attacks—> chain attack paths—> validate what they find.
Here are the 3 tools:
→ Decepticon runs 16 autonomous red team processes inside a hardened Kali Linux sandbox.
→ Pentest-Swarm-AI launches multiple attack paths across your network perimeter in parallel.
→ Strix performs real application pentests and validates vulnerabilities with working exploits.
AI powered security testing is getting seriously wild.
REPO BELOW